
Cobalt-Strike-CheatSheet
 s1ckb0y1337/cobalt-strike-cheatsheet
Some notes and examples for cobalt strike's functionality
command-and-controlcurated-resourcesdata-exfiltration+8
1.1k
s1ckb0y1337/cobalt-strike-cheatsheetSome notes and examples for cobalt strike's functionality
 abraxas/spark-connect-copy-local
Apache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal
 abraxas/spark-jdbc-serde-url
Apache Spark 4.2.0 - High - Remote - JDBC URL injection - ALTER TABLE SET SERDEPROPERTIES
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 abraxas/mysql-set-role-leftover
MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
 abraxas/phpmyadmin-config-set-2fa
phpMyAdmin 5.2.3 - High - Remote - 2FA - config/set clears two-factor
 moontea0416/webmirage
Adversarial image attacks on vision-language web agents, from visual grounding to browser execution
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 khush-613/cve-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…
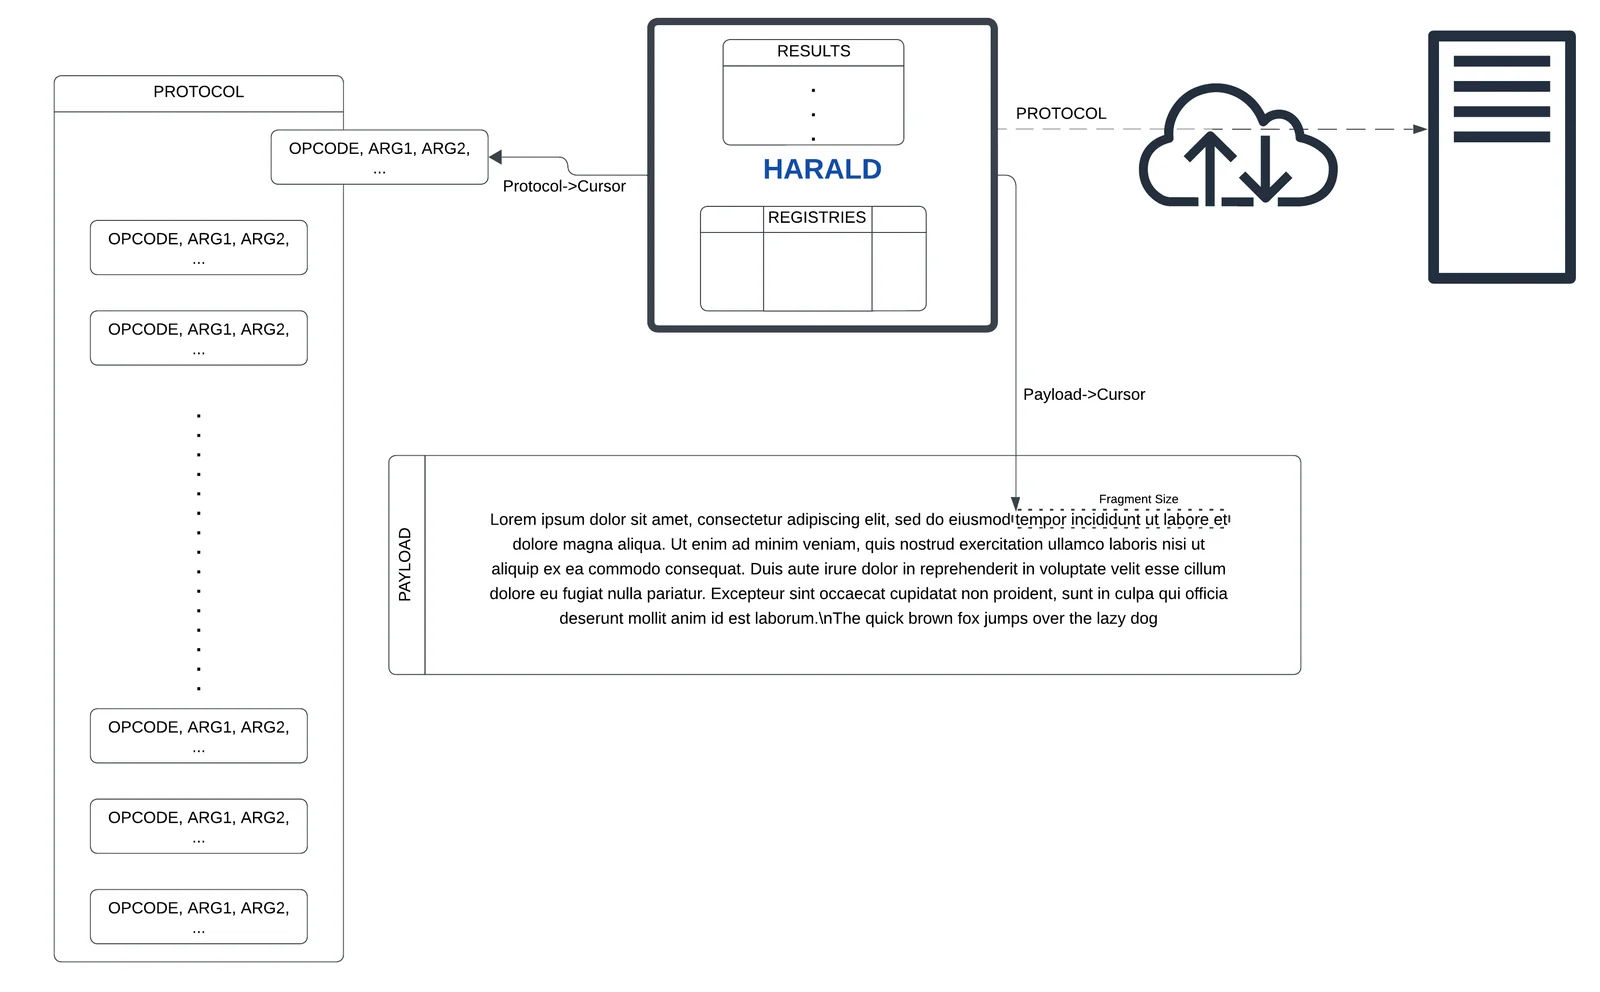 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 prasad-1808/tool-29489
This Tool is used to check for CVE-2023-29489 Vulnerability in the provided URL with the set of payloads available
 chosenonehacks/cve-2026-32746
Proof-of-concept exploit for a pre-authentication buffer overflow in GNU InetUtils telnetd (CVE-2026-32746), including a Docker lab environment and…
 yuhuamiao/cve-2026-36358
Proof-of-concept demonstrating a stored XSS vulnerability in Juzaweb CMS v5.0.0 via the banner ads HTML field, leading to arbitrary script execution…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.