IBM-Langflow-CVE-2026-48519-poc

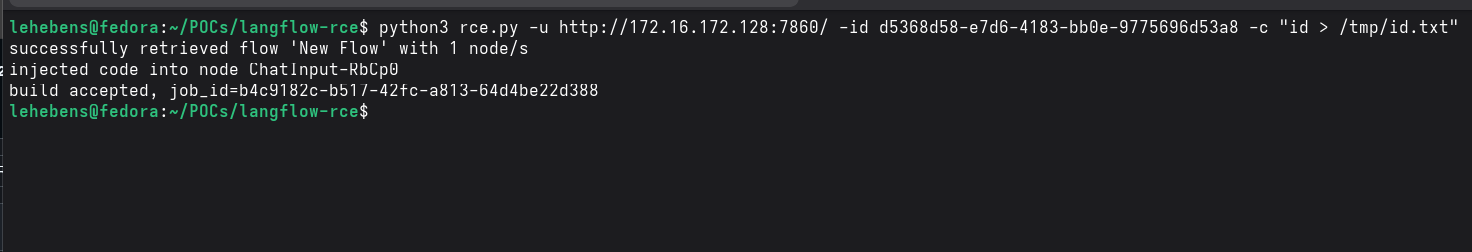
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…

Proof-of-concept exploit for CVE-2026-9198, an unauthenticated RCE in IBM Langflow OSS, chaining auto_login and validate/code endpoints. Includes a…

Exploit for CVE-2026-9198, containing proof-of-concept payloads and validation steps for assessing the vulnerability in target environments.

CVE-2026-9198利用代码

Exploit script for CVE-2026-9198 targeting IBM Langflow, providing proof-of-concept code to validate vulnerabilities and support authorized security…

Proof of Concept for CVE-2026-9198 - IBM Langflow Unauthenticated RCE via Auto-Login Bypass

Unauthenticated RCE exploit for Langflow OSS chaining auto_login JWT bypass with validate/code exec() to achieve remote command execution and reverse…

CVE-2020-4464 / CVE-2020-4450

Proof-of-concept exploit for CVE-2022-26377, an AJP smuggling vulnerability that poisons the HTTP response queue of IBM QRadar with a stored redirect.

CVE-2023-30990 exploits

IBM Maximo Asset Management is vulnerable to Information Disclosure via XXE Vulnerability (CVE-2020-4463)

CVE-2018-8021 Proof-Of-Concept and Exploit

🔍 Explore and test the CVE-2025-49844 (RediShell) vulnerability in Redis with this practical lab environment for secure education and research.

Exploit PoC for Buffer overflow vulnerability in the server in IBM Tivoli Storage Manager FastBack 5.5.x and 6.x before 6.1.12.2 (tested in version…

Proof-of-concept exploit for CVE-2017-1635, a use-after-free vulnerability in IBM Tivoli Monitoring's KDH web server component enabling remote code…

A POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)

IBM i Access Client Solutions < 1.1.9.4 - Remote code execution via insecure deserialisation