

Hexestra
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
ai-securitycommand-and-controlinformation-gathering+7
42
absllk/hexestraAI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 horkimhab/cve-2026-65660
Educational security research repository documenting CVE-2026-65660 with setup guidance for authorized lab testing and vulnerability awareness.
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 horkimhab/cve-2026-68121
Proof-of-concept for CVE-2026-68121 (PPPoEject), providing a Python exploit implementation for authorized security research and lab testing.
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 horkimhab/cve-2026-80844
Proof-of-concept and research repository for CVE-2026-80844 (DirtyAH6), providing educational material and lab setup guidance for authorized…
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
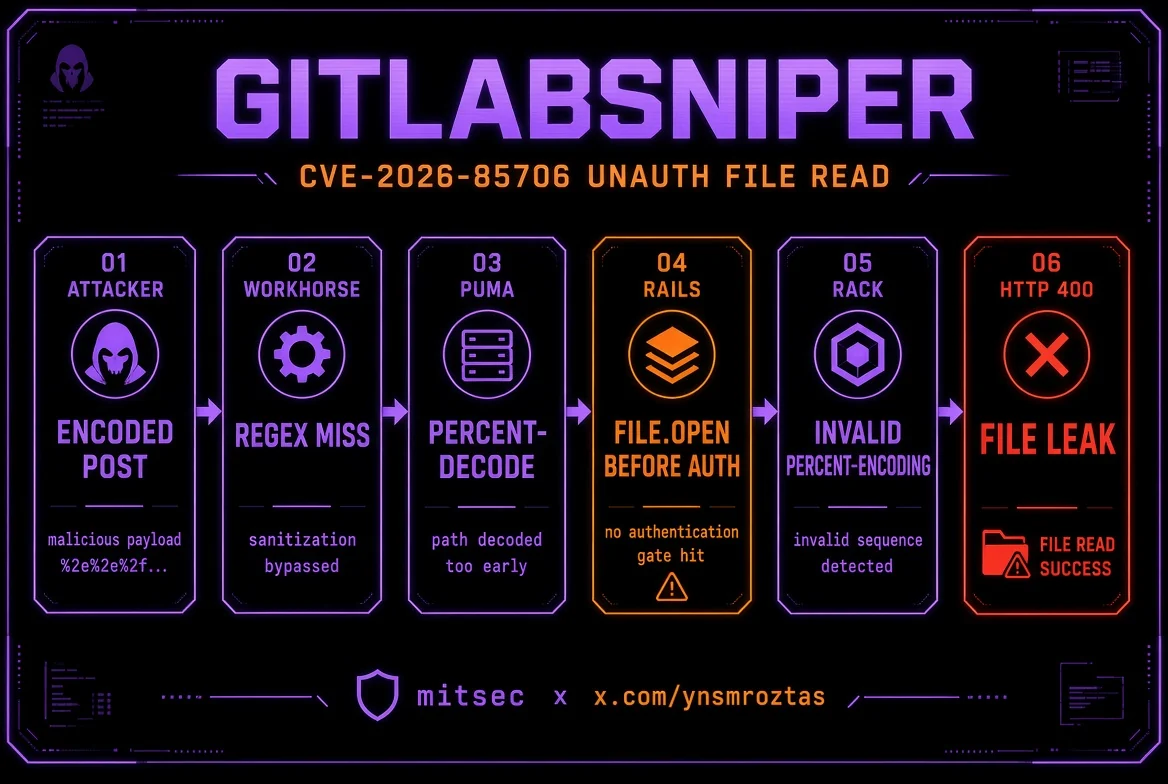 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…