
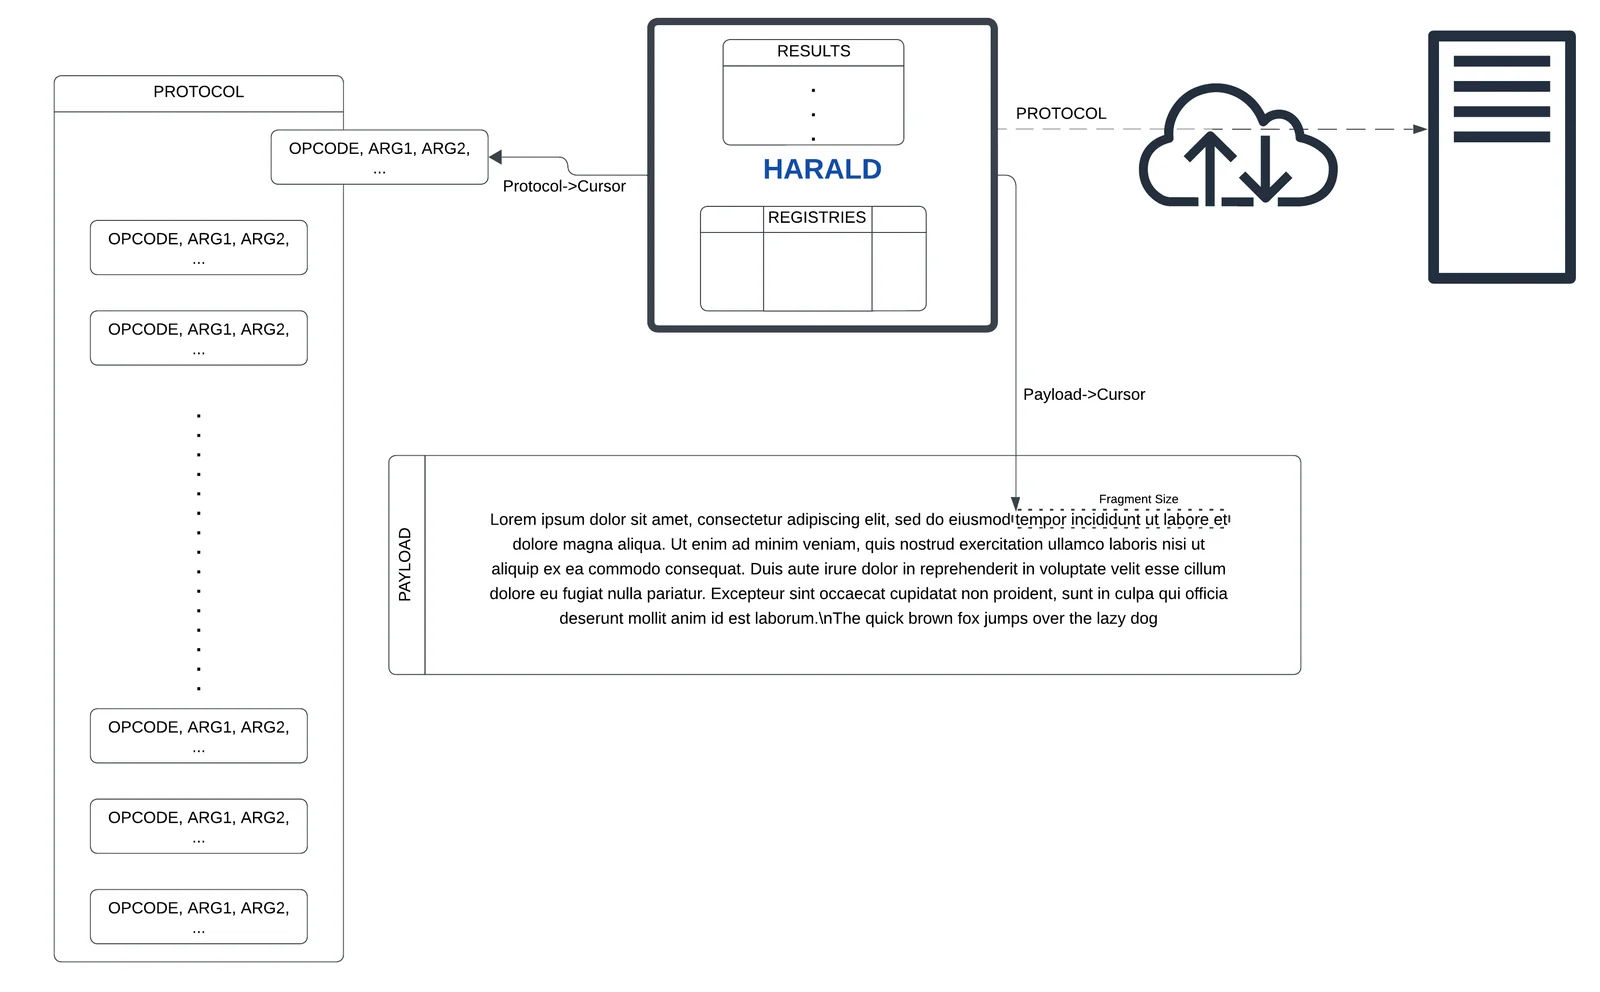
Harald
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
gmh5225/haraldAn in-memory minimal CPU for agnostic on-the-fly protocols creation
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
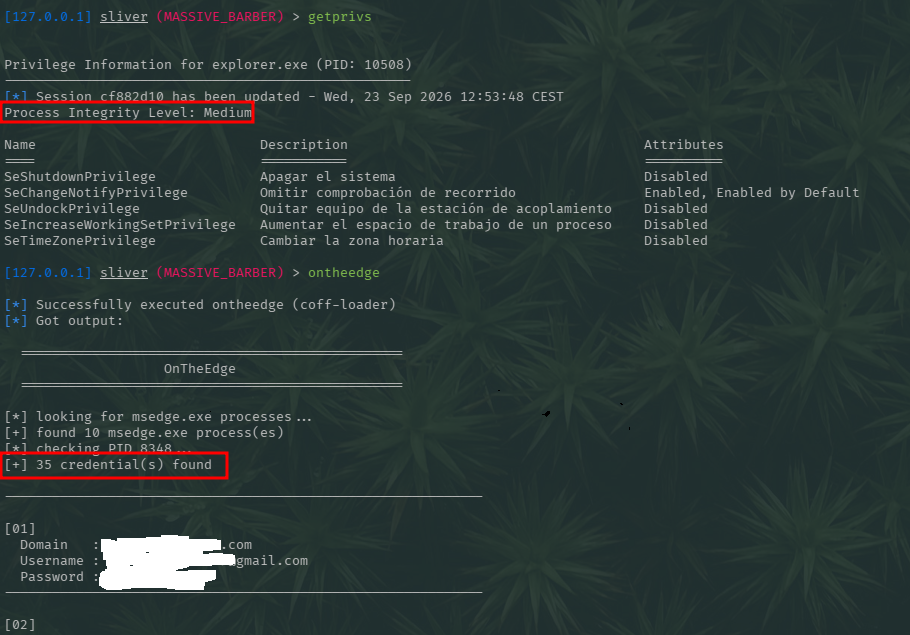 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 r3vpwnx/cve-2025-8110
Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…
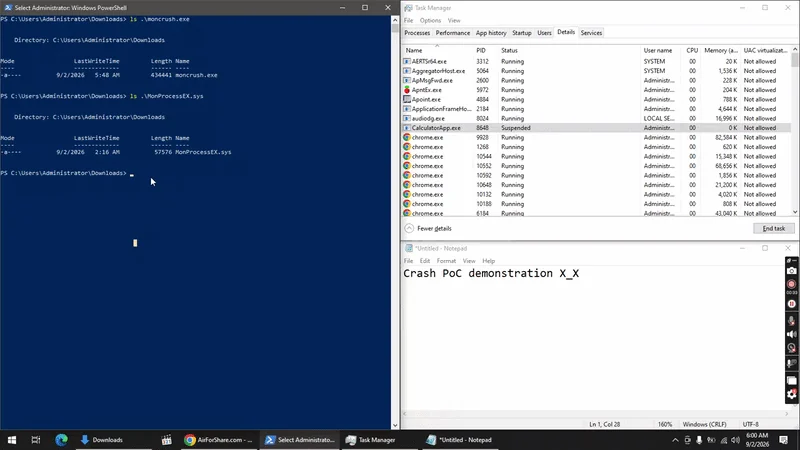 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 atiilla/cve-2026-27876
Grafana SQL Expressions Arbitrary File Write to RCE
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 abhinavagarwal07/nvidia-gpu-security-poc
PoCs and evidence for two NVIDIA Linux GPU driver findings closed by the vendor as expected/intended behavior: cross-UID GPU process telemetry via…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 johnossawy/cve-2023-42793_poc
Automated exploit script for CVE-2023-42793 targeting TeamCity, enabling token manipulation and admin user creation for penetration testing.
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
 realrodri/exploiteameesta
iOS app to check device compatibility with CVE-2021-30937 vulnerability, displaying alerts and popups during the process.
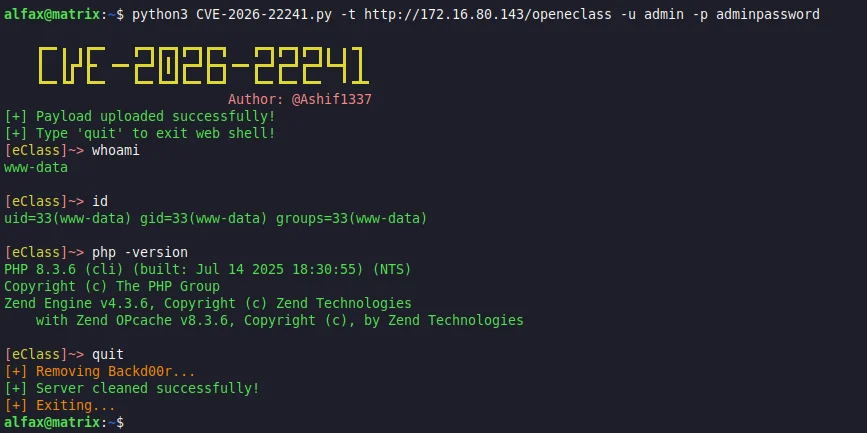 ashifcoder/cve-2026-22241
Automated exploit for CVE-2026-22241, an unrestricted file upload vulnerability in Open eClass, enabling remote code execution via a webshell with…
 hika-sec/terminator_killer
Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…