
PoC-CVE-2025-24071
 daemon-404/poc-cve-2025-24071
Python PoC for CVE-2025-24071 that crafts a .library-ms file to coerce Windows Explorer into leaking NetNTLMv2 hashes over SMB for capture and…
ctfexploitationlabs-practice+5
daemon-404/poc-cve-2025-24071Python PoC for CVE-2025-24071 that crafts a .library-ms file to coerce Windows Explorer into leaking NetNTLMv2 hashes over SMB for capture and…
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
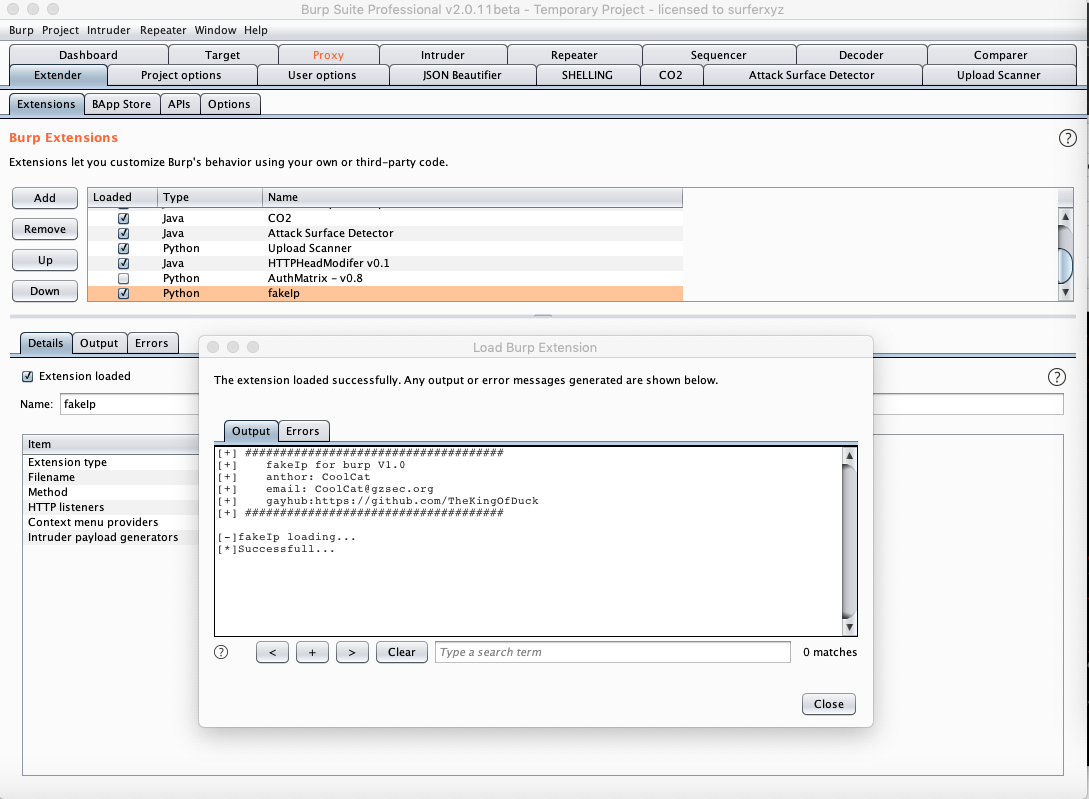 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
 mziqudhd92/honeypot-auditor
Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like a low-interaction honeypot — Shodan…
 amirrezamarzban/portscan-cve-2026-41940
IP CIDRs (presumably as input, maybe command line or file) and checks ports 2083 and 2087 for openness
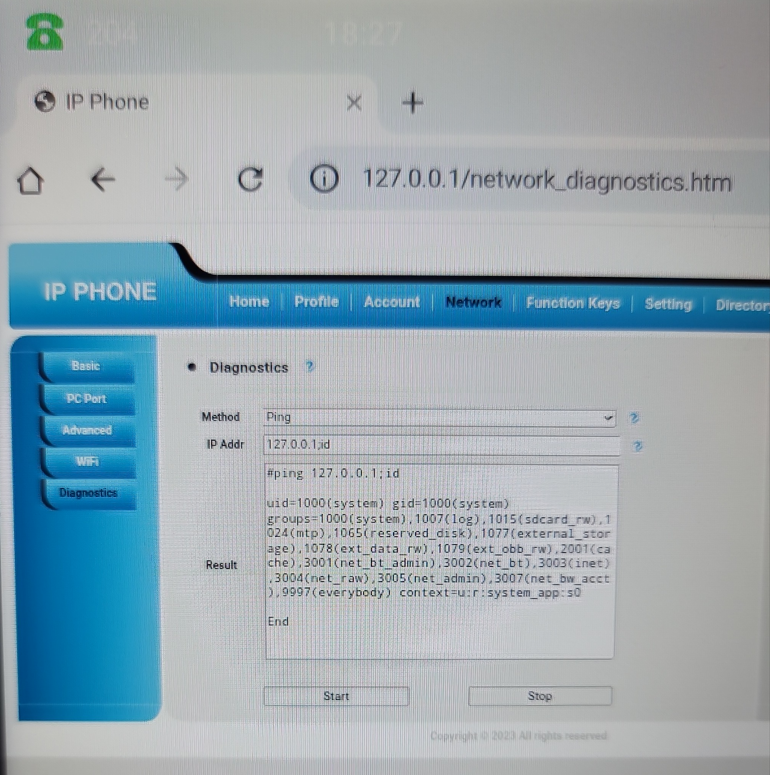 restdone/cve-2025-57457
Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.
 redyank/cve-2026-33752
Demonstrates a redirect-based SSRF vulnerability in curl_cffi allowing internal network access, with PoC code and analysis of TLS impersonation…
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
 woodenklaas/cve-2021-44521
Automated proof-of-concept exploit for CVE-2021-44521, enabling remote code execution on Apache Cassandra via user-defined functions. Executes…
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
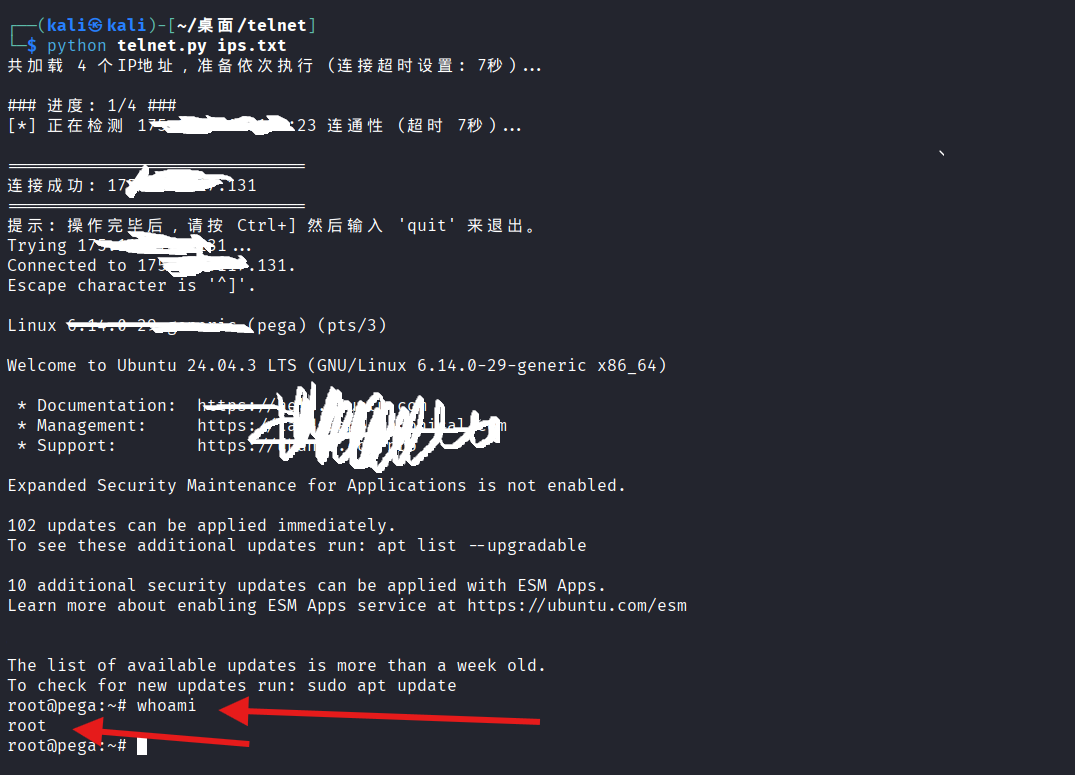 parameciumzhang/tell-me-root
Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration…
 bysinks/cve-2021-29441
Exploit for CVE-2021-29441 in Alibaba Nacos, enabling unauthorized addition of user accounts by sending crafted requests to the target IP.
 feng-huang-0520/dataease_postgresql_jdbc_bypass-cve-2025-49002
Proof-of-concept exploit for CVE-2025-49002, a remote code execution vulnerability in DataEase via PostgreSQL JDBC bypass, including a crafted HTTP…
 brainbob/cve-2026-24061
Python-based exploit for CVE-2026-24061, targeting a network service with customizable port and debug mode for security testing.
 0x656565/cve-2023-48022
Exploit for CVE-2023-48022, adapted from Bishop Fox research. Configure IP, port, and payload to execute against vulnerable Ray instances.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.