

JURIG
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
ai-assisted-reversingai-securityandroid-security+9
reverserid/juriga fully autonomous AI agent for reverse engineering
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 rootxran/cve-2026-29053
Proof-of-concept exploit for Ghost CMS remote code execution via prototype pollution in jsonpath and static-eval, with a vulnerable environment setup…
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 ac8999/cve-2026-29053
(RCE) vulnerability discovered in Ghost CMS (specifically affecting versions 0.7.2 through 6.19.0)
 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 ghost-otpbot/smsotpbot
OTP BOT Bypass SMS verifications from Paypal, Instagram, Snapchat, Google, 3D Secure, and many others...
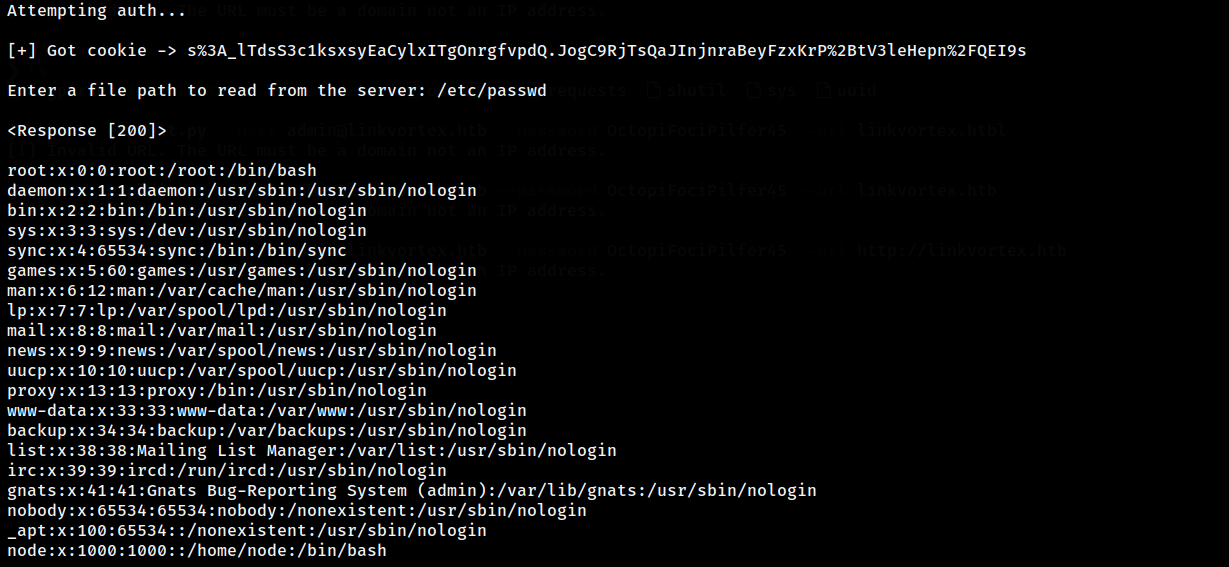 monke443/cve-2023-40028
Arbitrary file read in Ghost-CMS allows an attacker to upload a malicious ZIP file with a symlink.
 rvzsec/cve-2023-40028
CVE-2023-40028 PoC Exploit
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
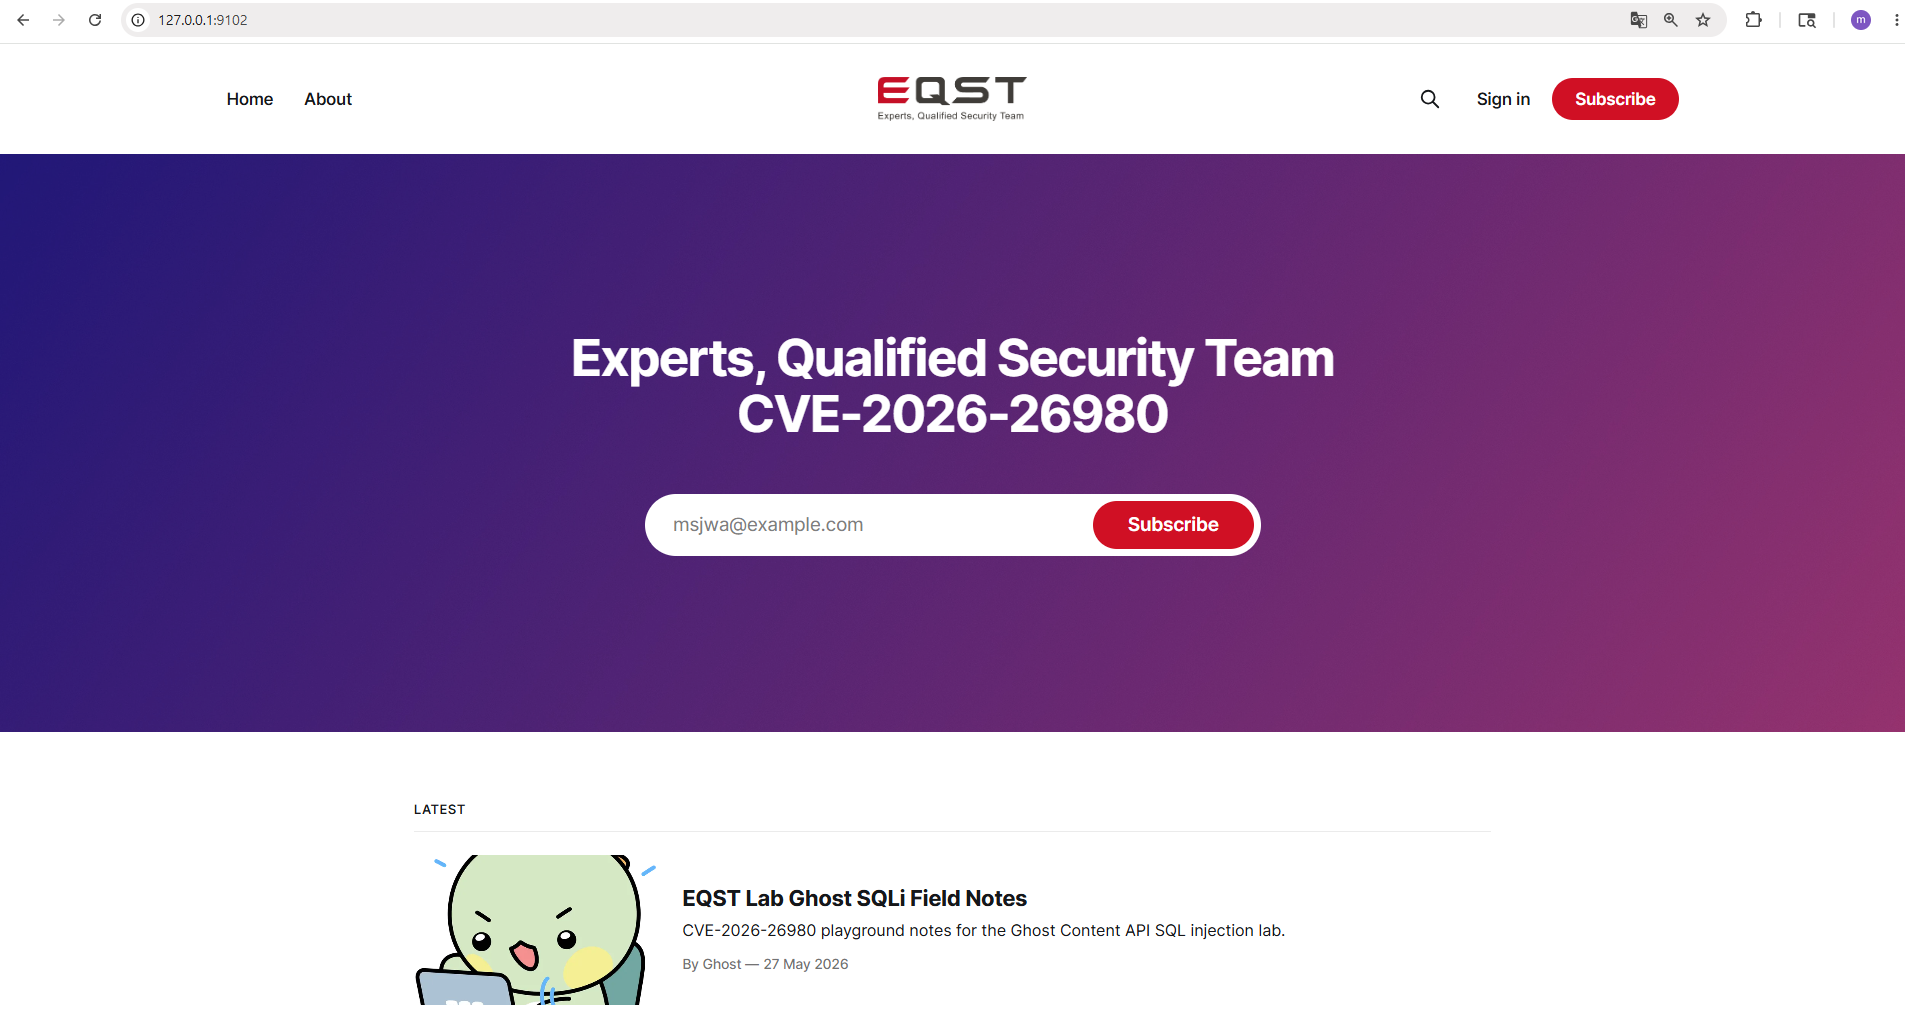 eqstlab/cve-2026-26980
Ghost Content API SQL Injection
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
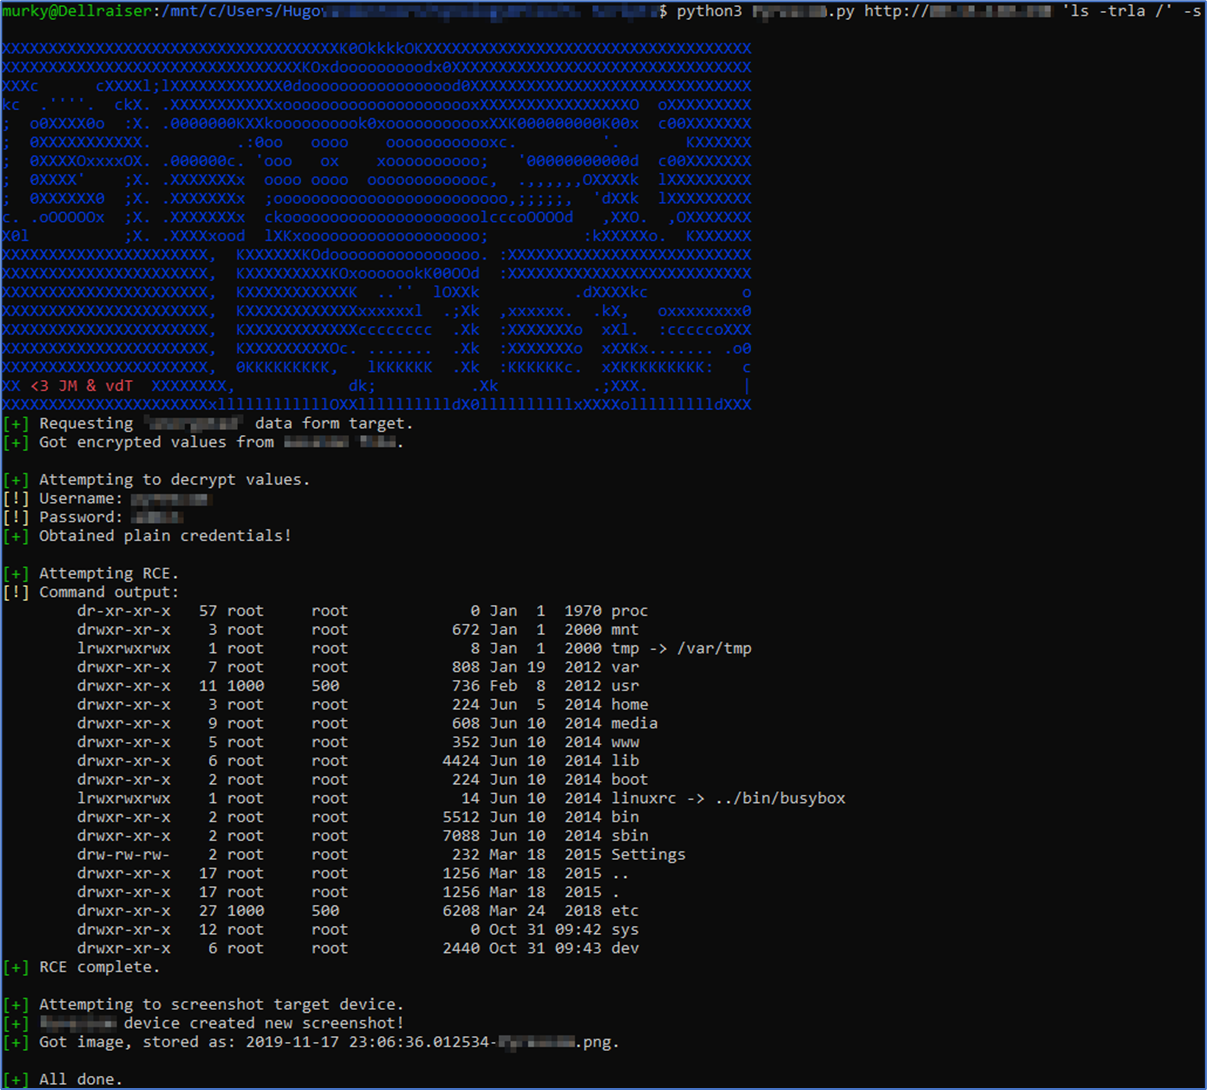 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 sudlit/cve-2023-40028
Proof-of-concept exploit for CVE-2023-40028, demonstrating arbitrary file read in Ghost CMS via improper file handling. For educational and…
 syogod/cve-2023-40028
CVE-2023-40028 is a security vulnerability affecting Ghost CMS versions prior to 5.59.1.
 rehan6658/cve-2023-40028
Python exploit for CVE-2023-40028 in Ghost CMS, enabling arbitrary file read via symlink abuse in ZIP uploads. Includes automated cleanup.
 subc0ol/cve-2015-0235
Ruby-based exploit for CVE-2015-0235 (Ghost) targeting glibc gethostbyname buffer overflow for remote code execution on vulnerable systems.