
fufu-sec
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
exploitationnetwork-securitypassword-attacks+4
kyllr-qwen/fufu-secFramework for Uninvited Frequency Usage
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 qkaiser/awind-research
This repository holds interesting bits and pieces related to research I performed on wireless presentation devices manufactured by Awindinc and…

 commonexploits/weape
Weape-Wireless-EAP-Extractor
 samyk/skyjack
A drone engineered to autonomously seek out, hack, and wirelessly take full control over any other Parrot or 3DR drones within wireless or flying…
 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
 plantdaddy/fuzzap
A python script for obfuscating wireless networks
 lixiang957/cve-2021-36630
Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.
 0n1con3/fluxer
FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
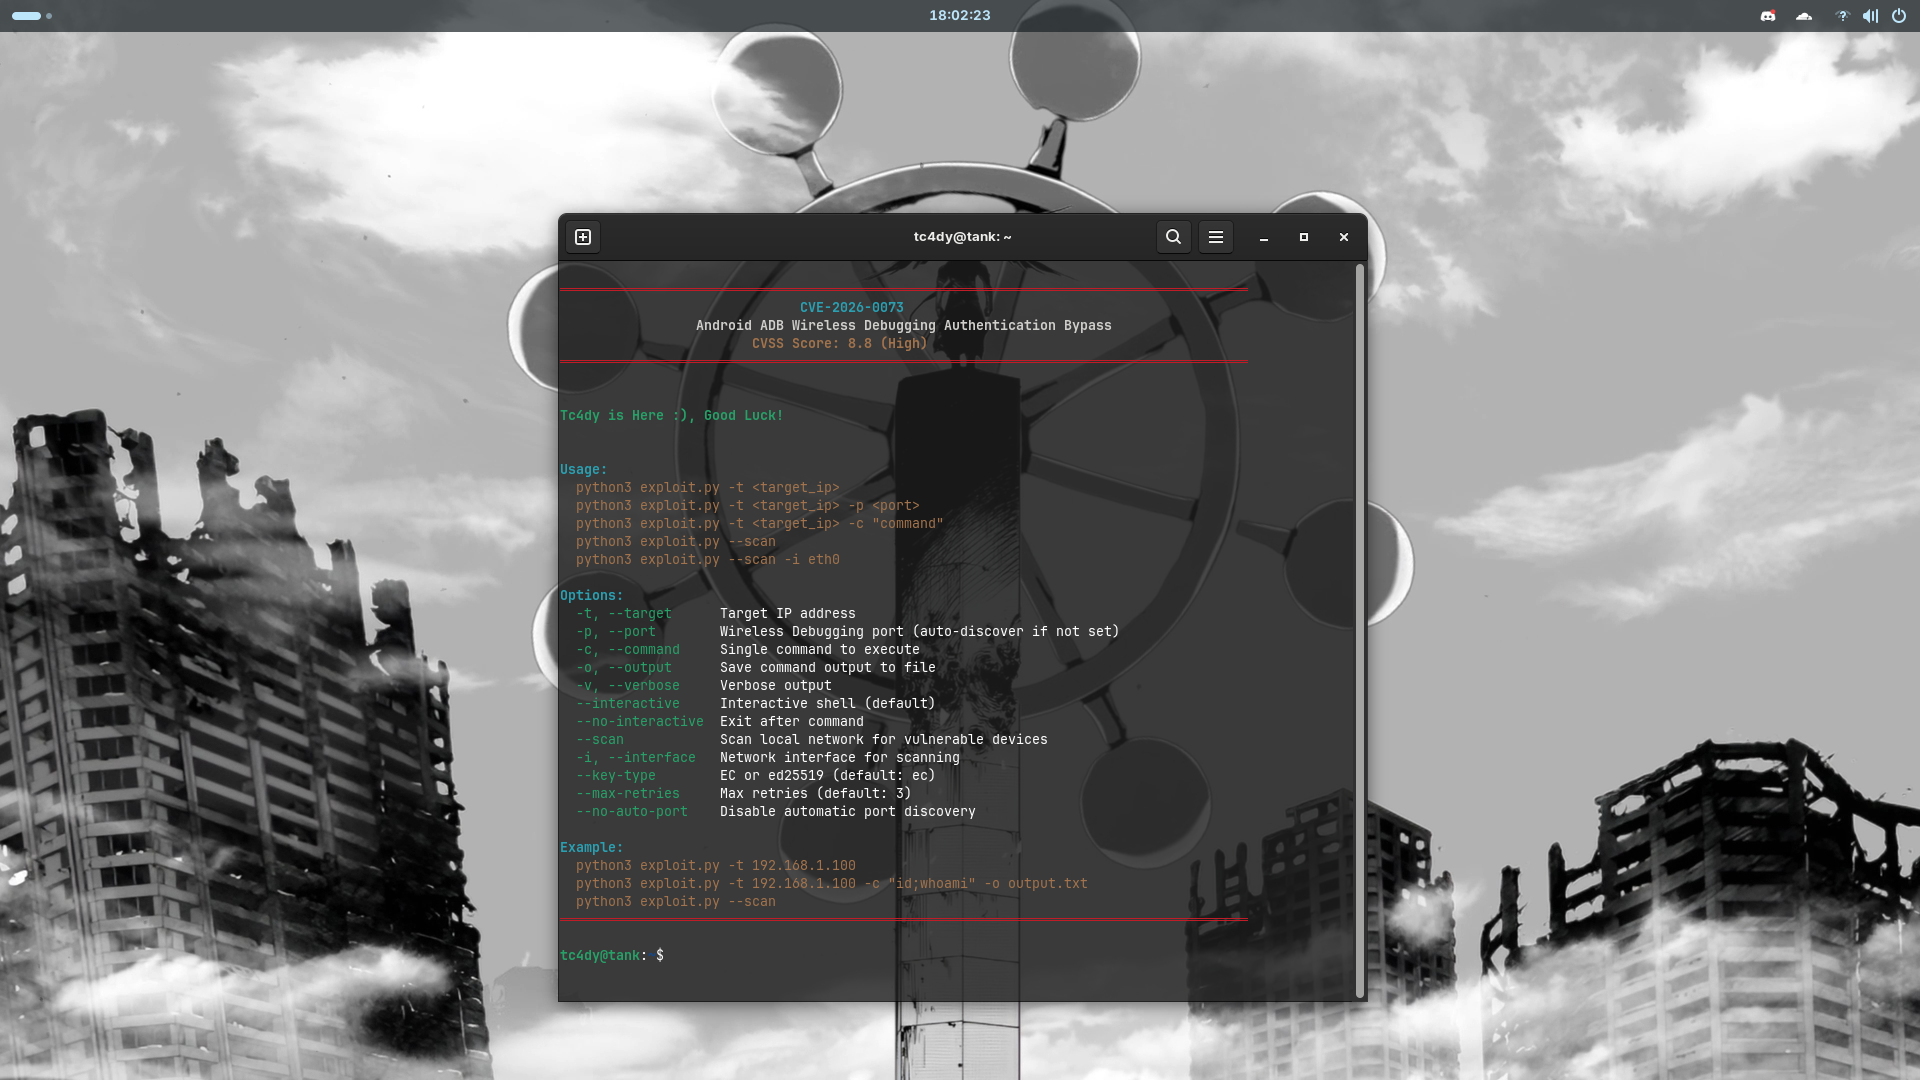 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 xchwarze/wifi-pineapple-cloner-builds
Build repo from Universal Wifi pineapple hardware cloner
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32