
CVE-2026-19658
 murrez/cve-2026-19658
Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
exploitationinformation-gatheringpayload-development+7
murrez/cve-2026-19658Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 ll104567/cve-2023-5966
Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…
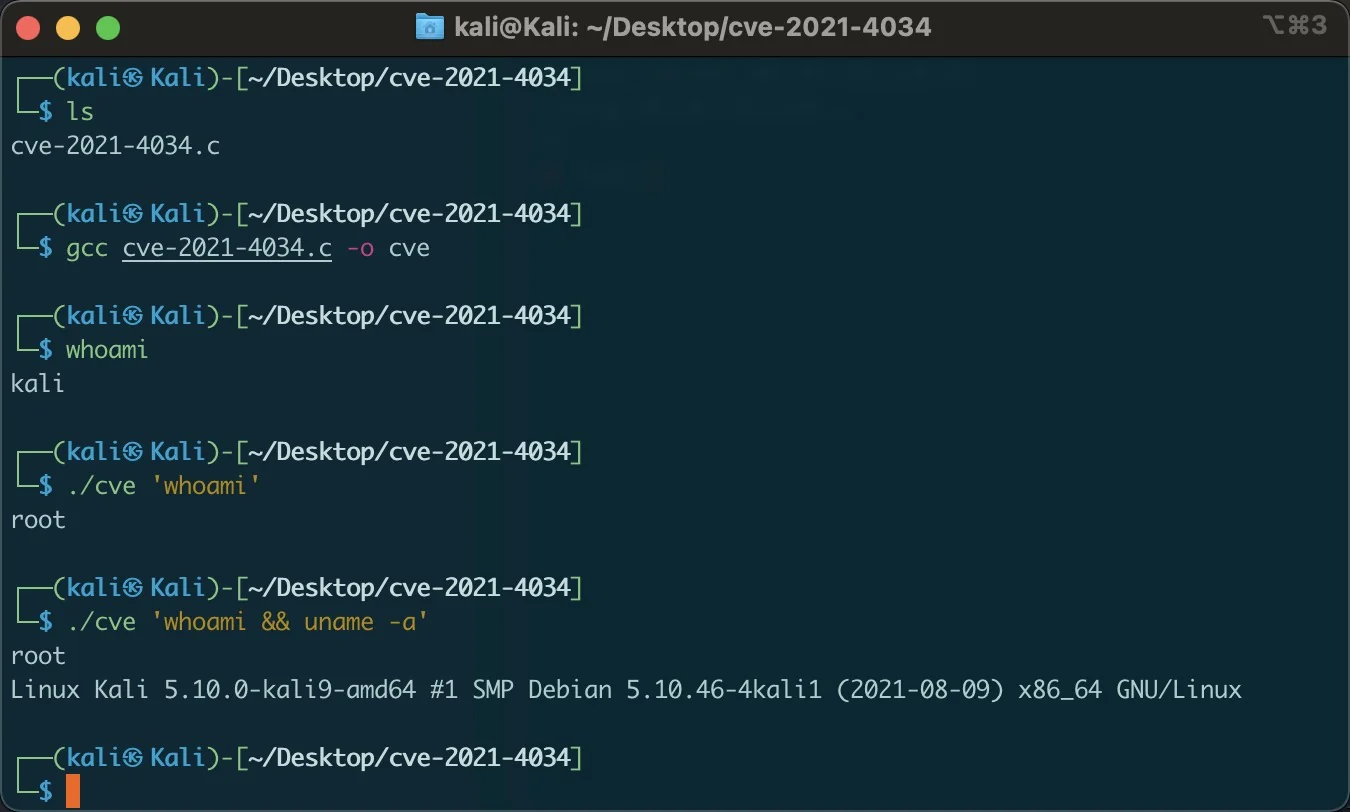 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands
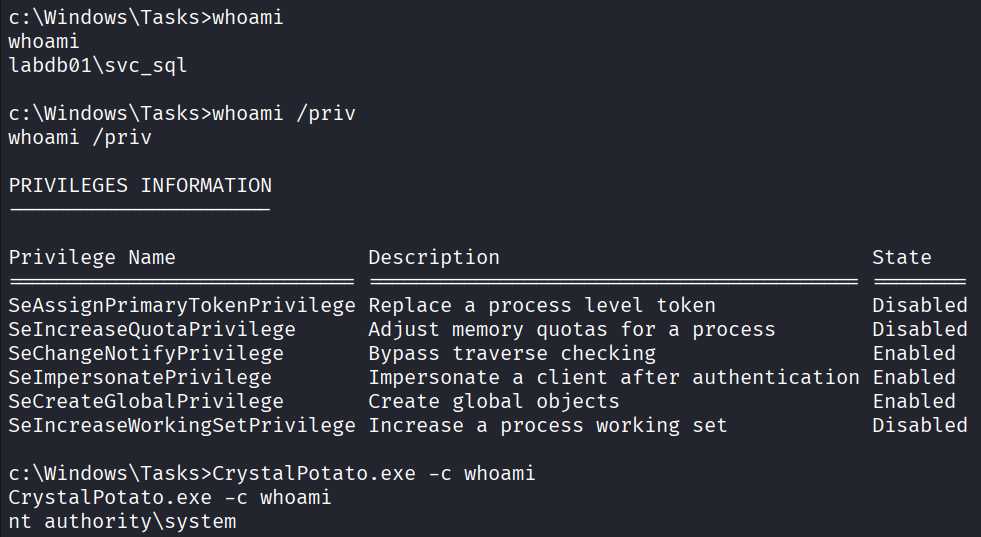 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 mdsecresearch/burpsuitesharpener
Enhances Burp Suite with tab management, customizable themes, keyboard shortcuts, title renaming, window position memory, and UI utilities for faster…
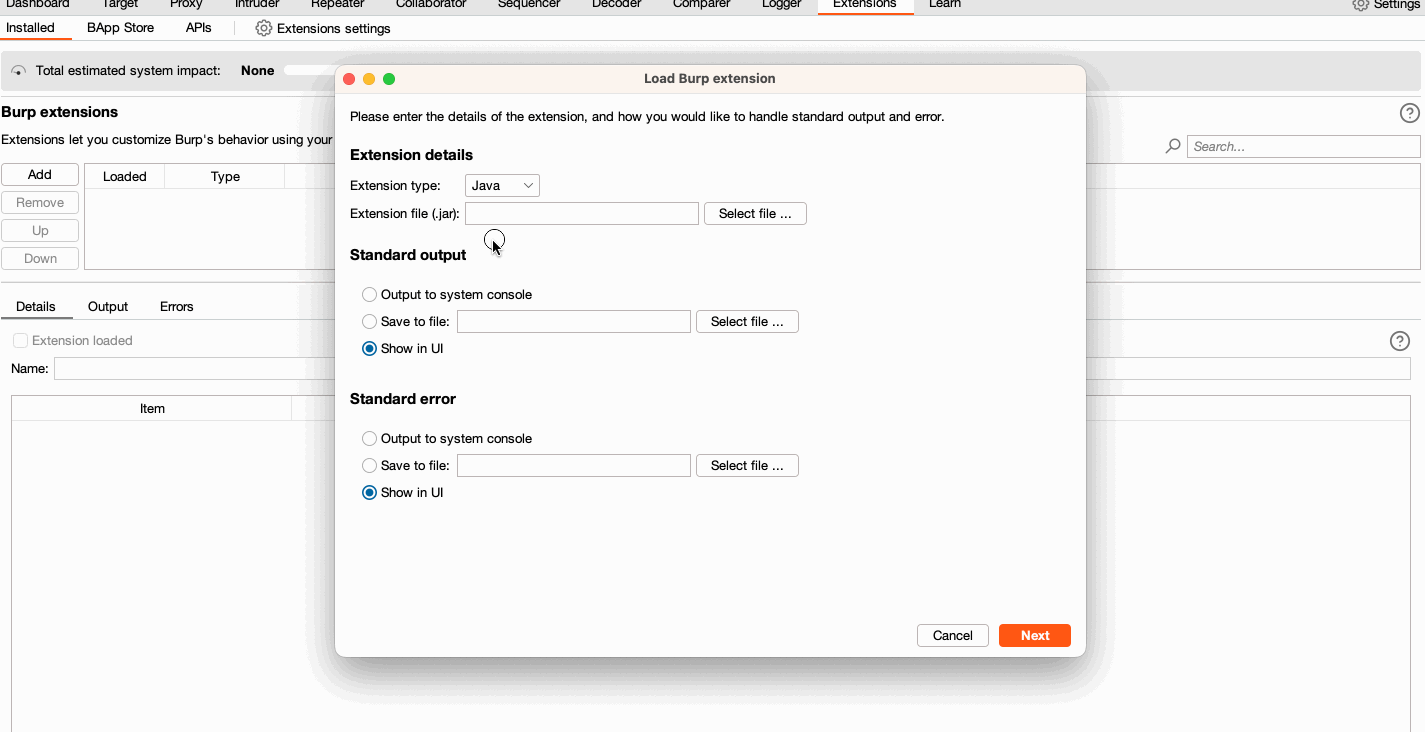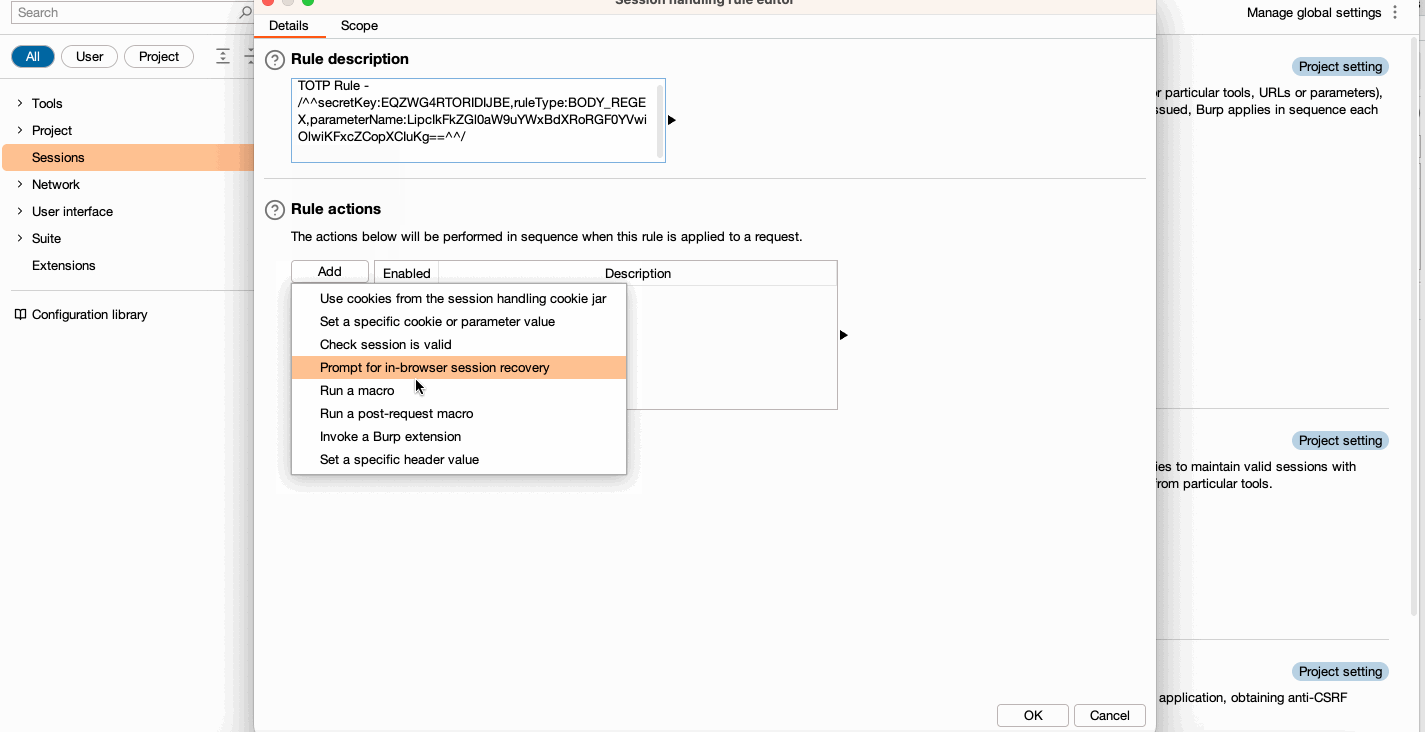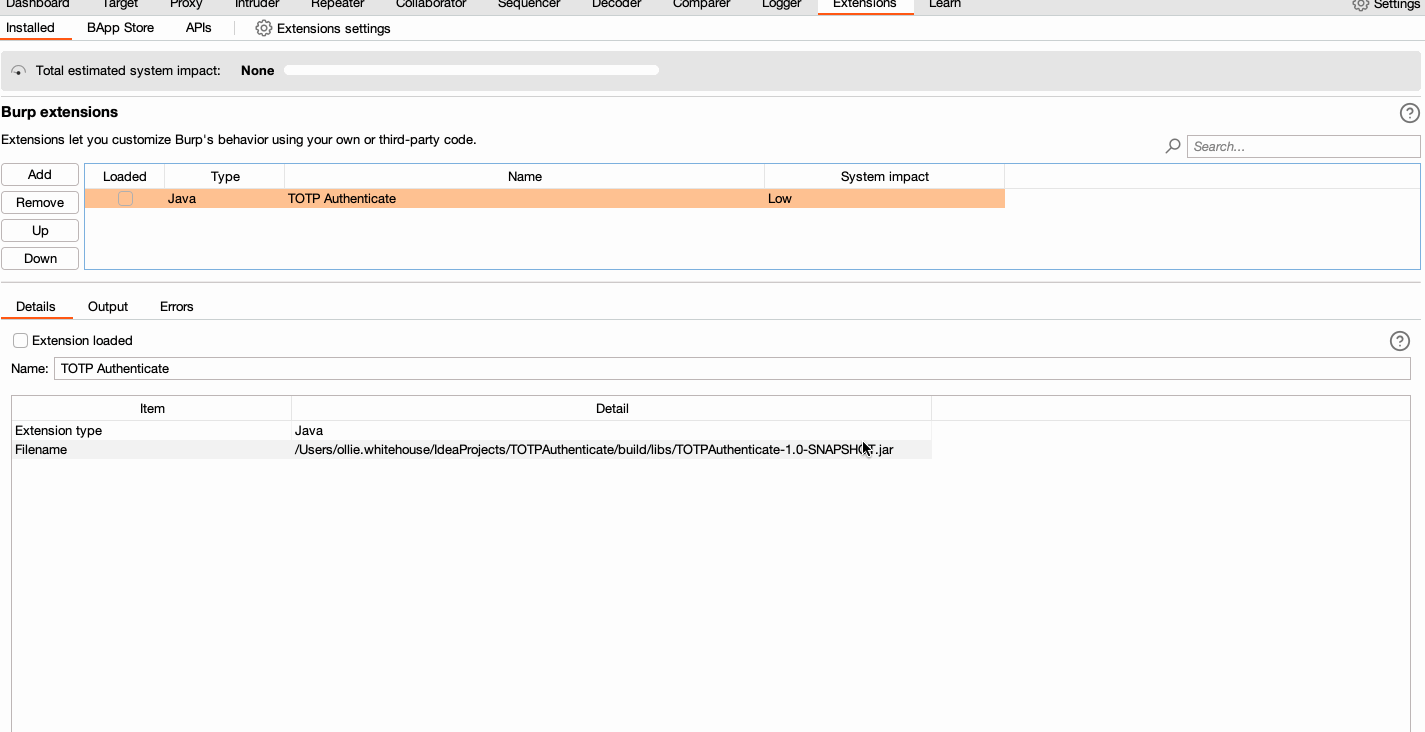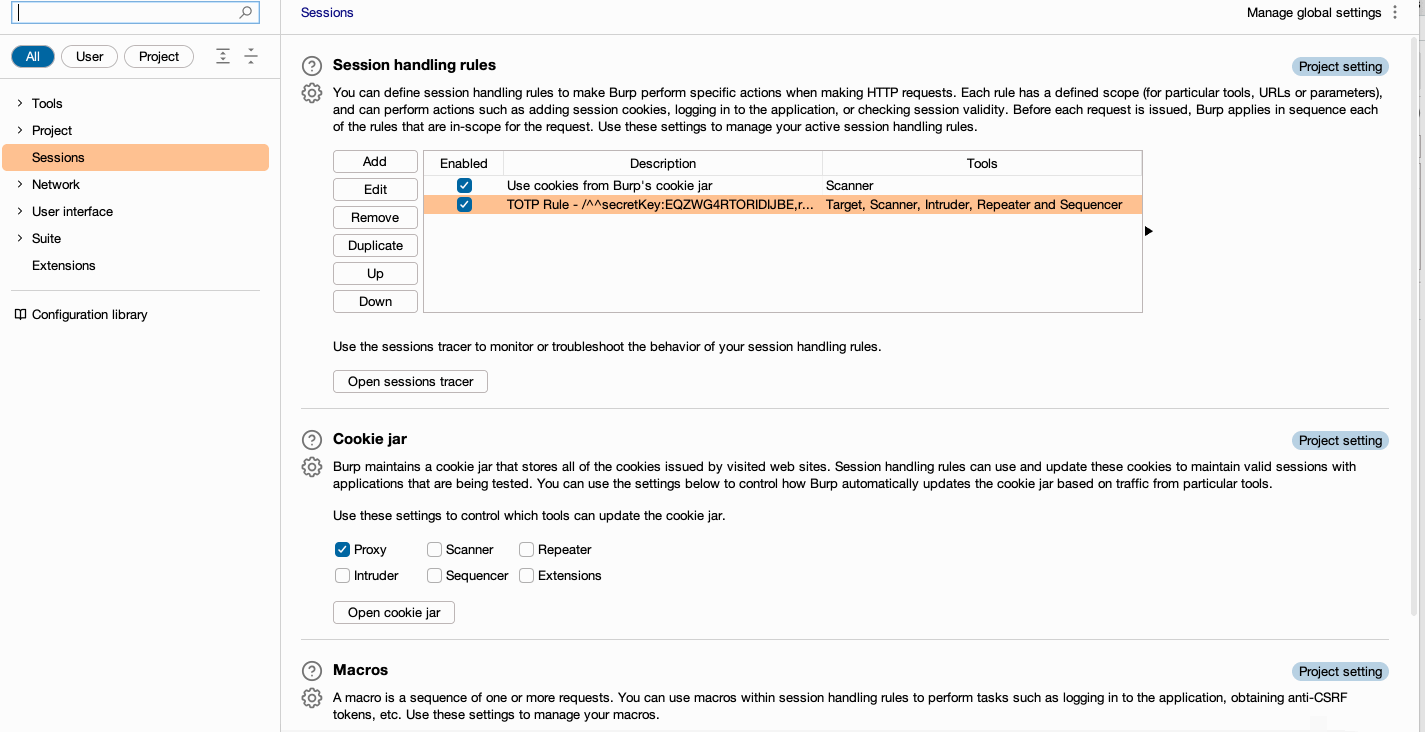 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 rasta-mouse/cswhispers
Source generator to add D/Invoke and indirect syscall methods to a C# project.
 mbadanoiu/mal-005
MAL-005: Zip Slip in Add Carbon Applications in WSO2 ESB
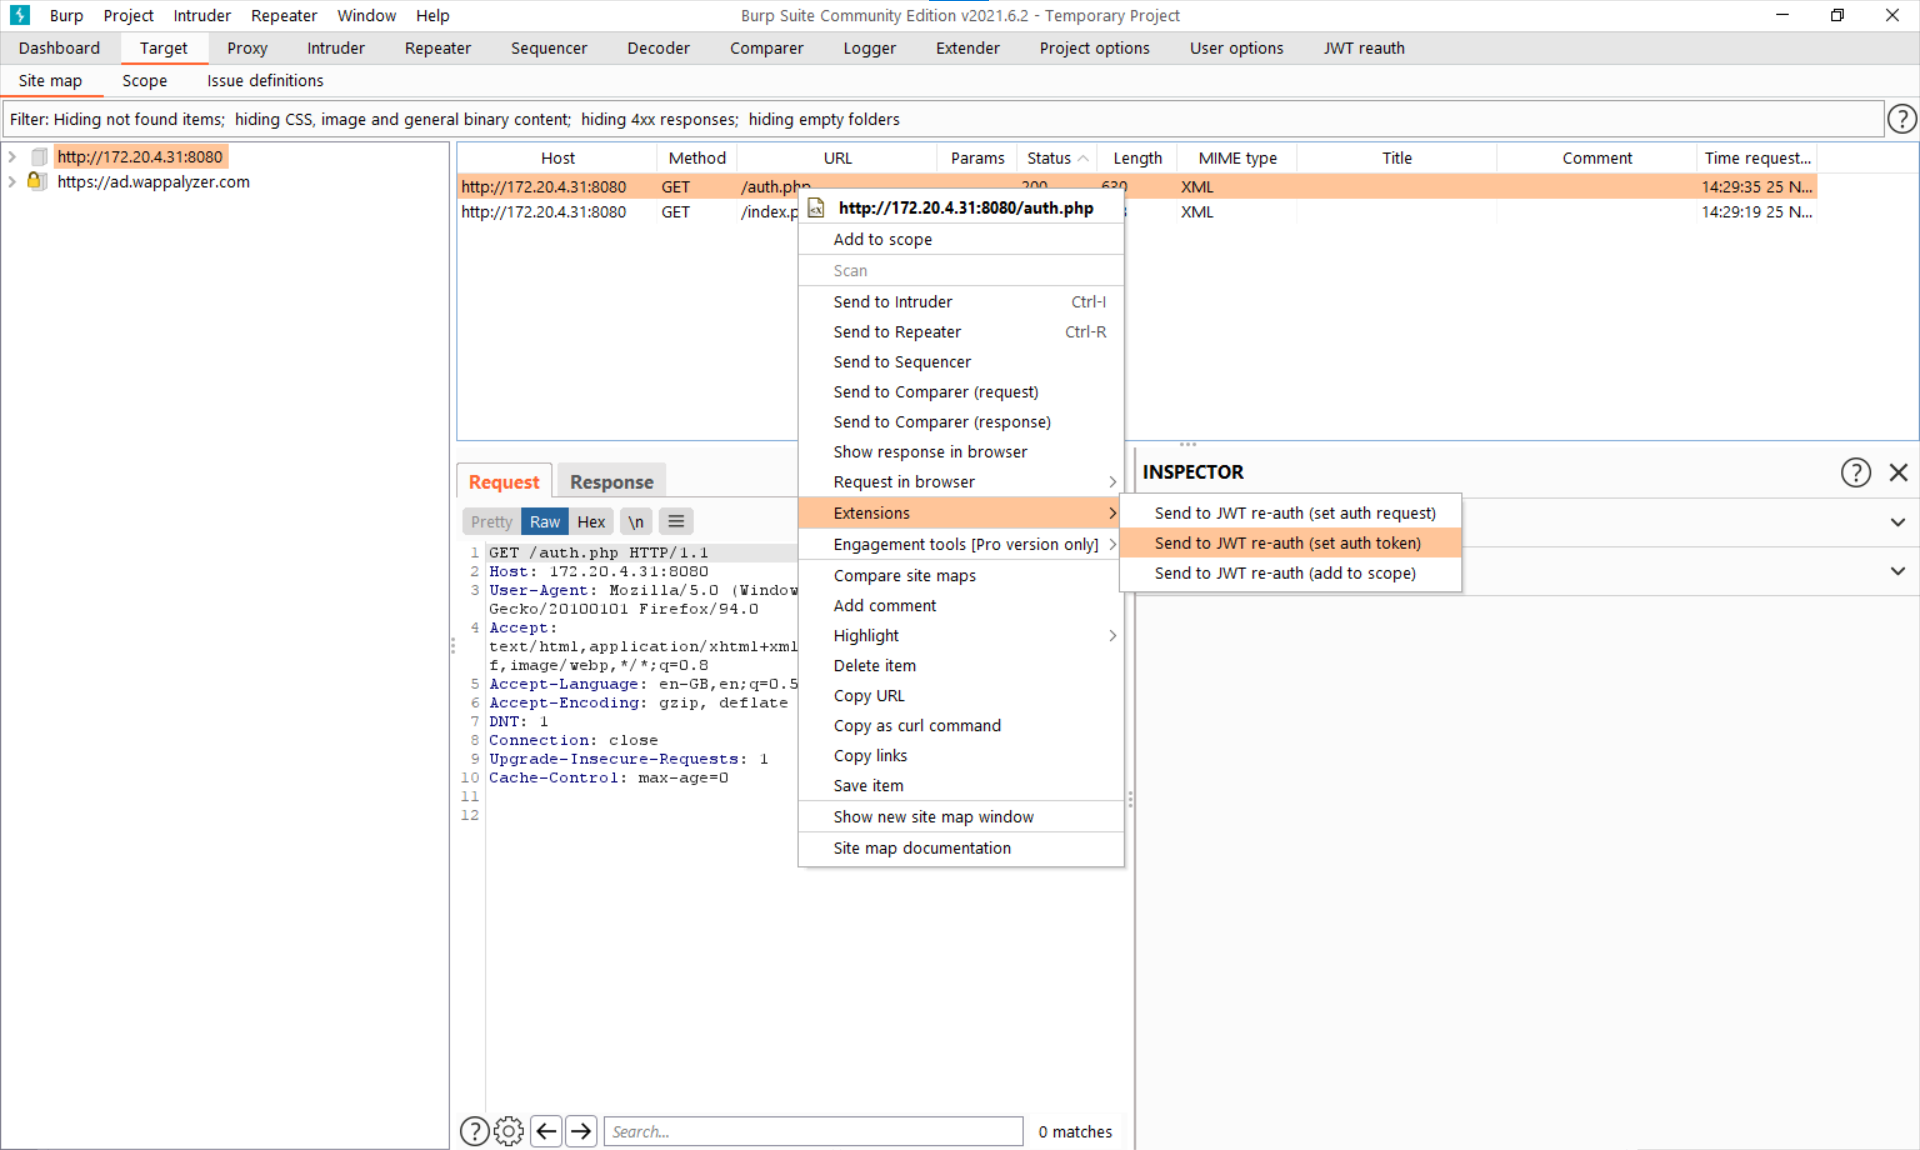 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.

 ctn-qvo/cve-2026-0073-android-adbd-bypass-poc_zh_cn
CVE-2026-0073-Android-ADBD-bypass-POC汉化版
 jtripper/sslnuke
Transparent proxy that decrypts SSL traffic and prints out IRC messages.
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
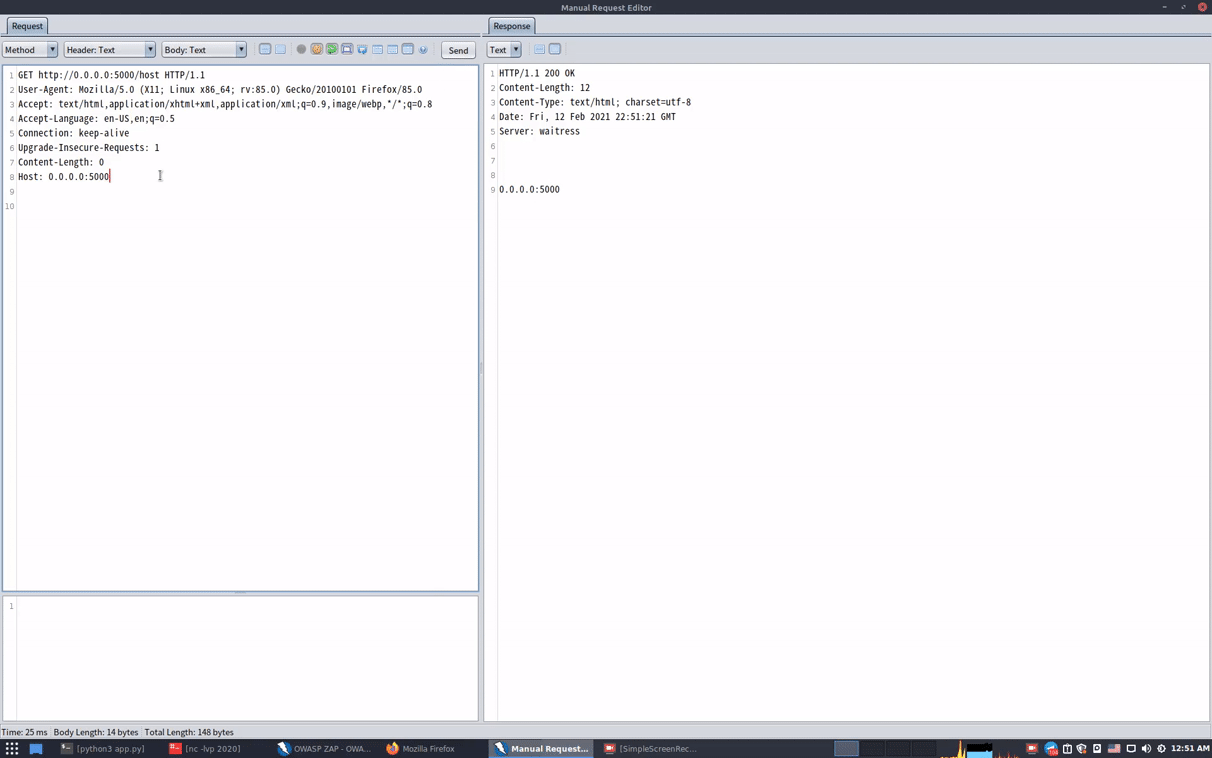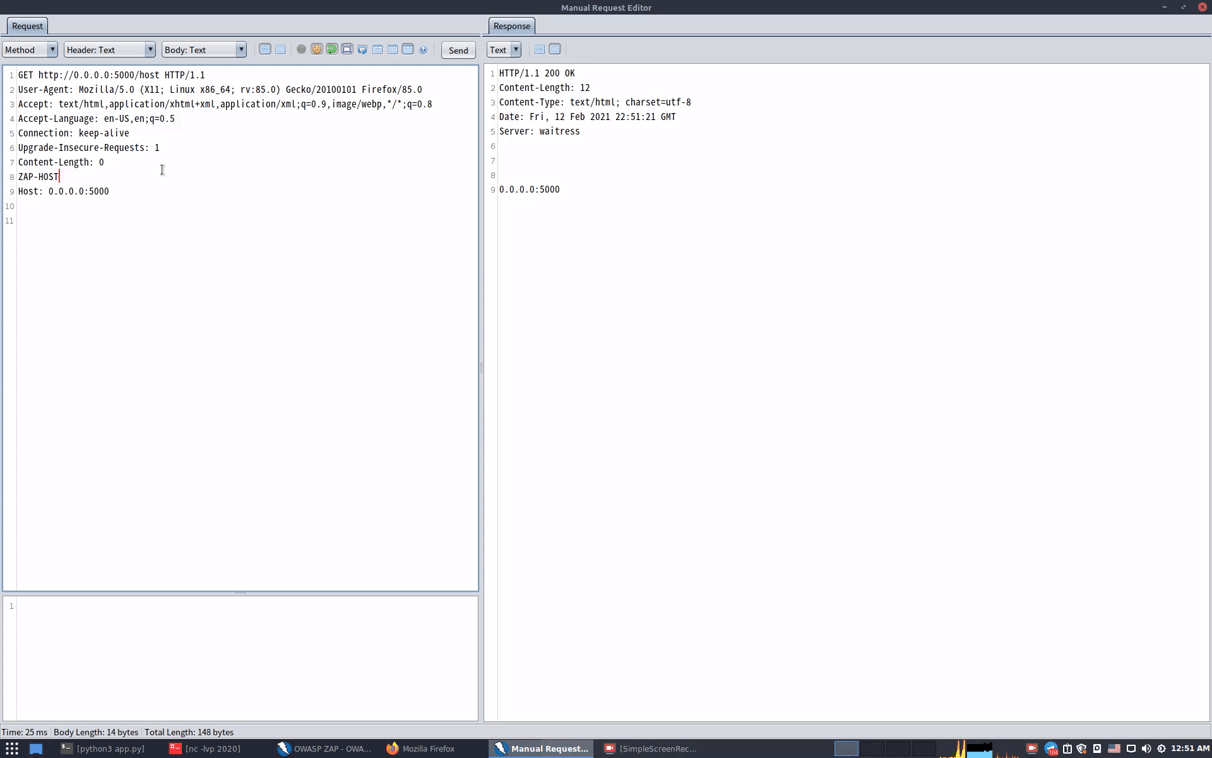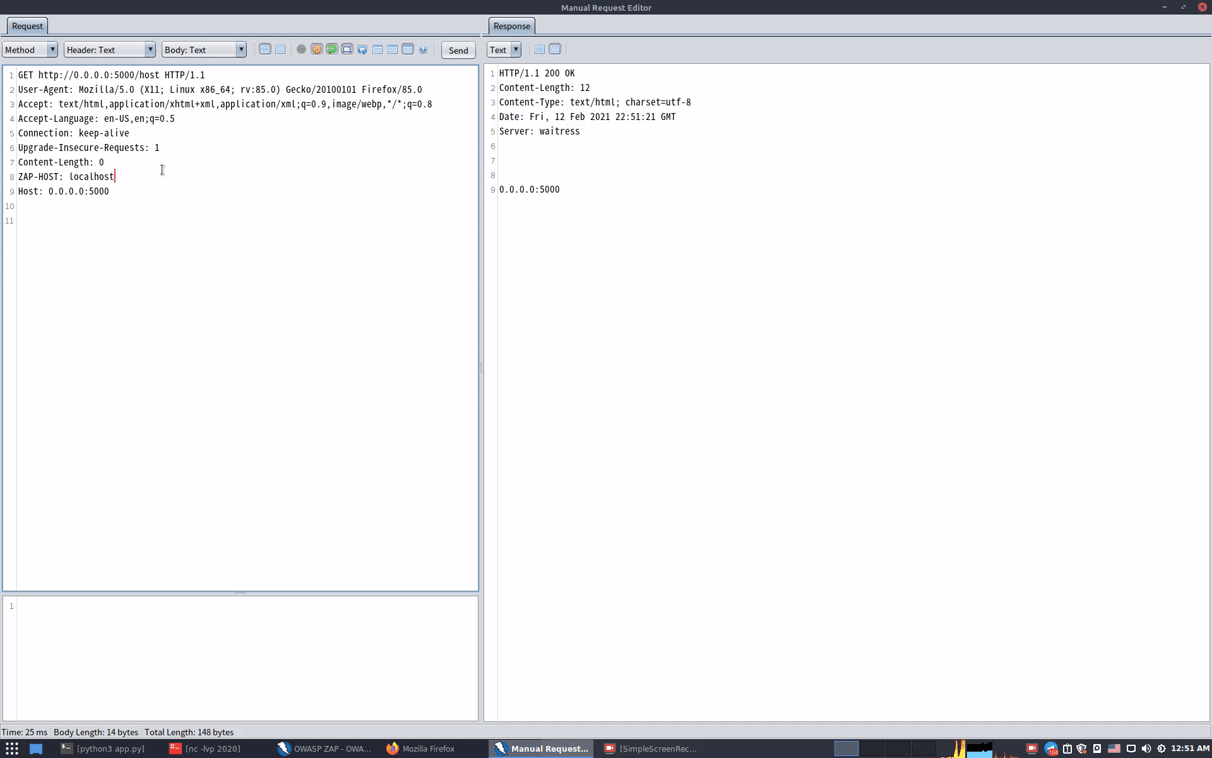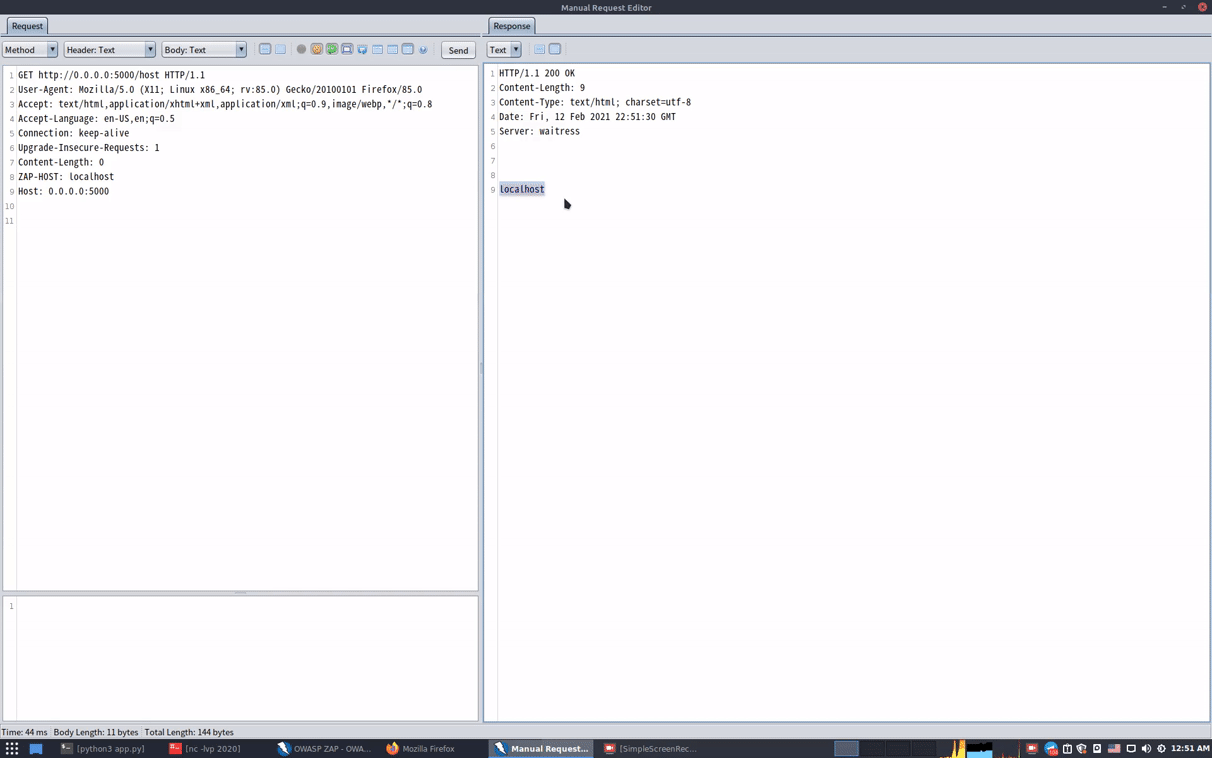 mindpatch/zaphoster
Fix host header error in zaproxy
 blacksnufkin/holygrail
BYOVD hunter to help prioritize windows drivers worth manual analysis