

JavaSecLab
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
code-analysisctfdevsecops+6
885
whgojp/javaseclabComprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 isuruwa/log4j
Scanner and proof-of-concept exploit for Log4j RCE (CVE-2021-44228). Creates a vulnerable application and runs the exploit with a netcat listener.
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 notkmhn/cve-2022-21449-tls-poc
CVE-2022-21449 Proof of Concept demonstrating its usage with a client running on a vulnerable Java version and a malicious TLS server
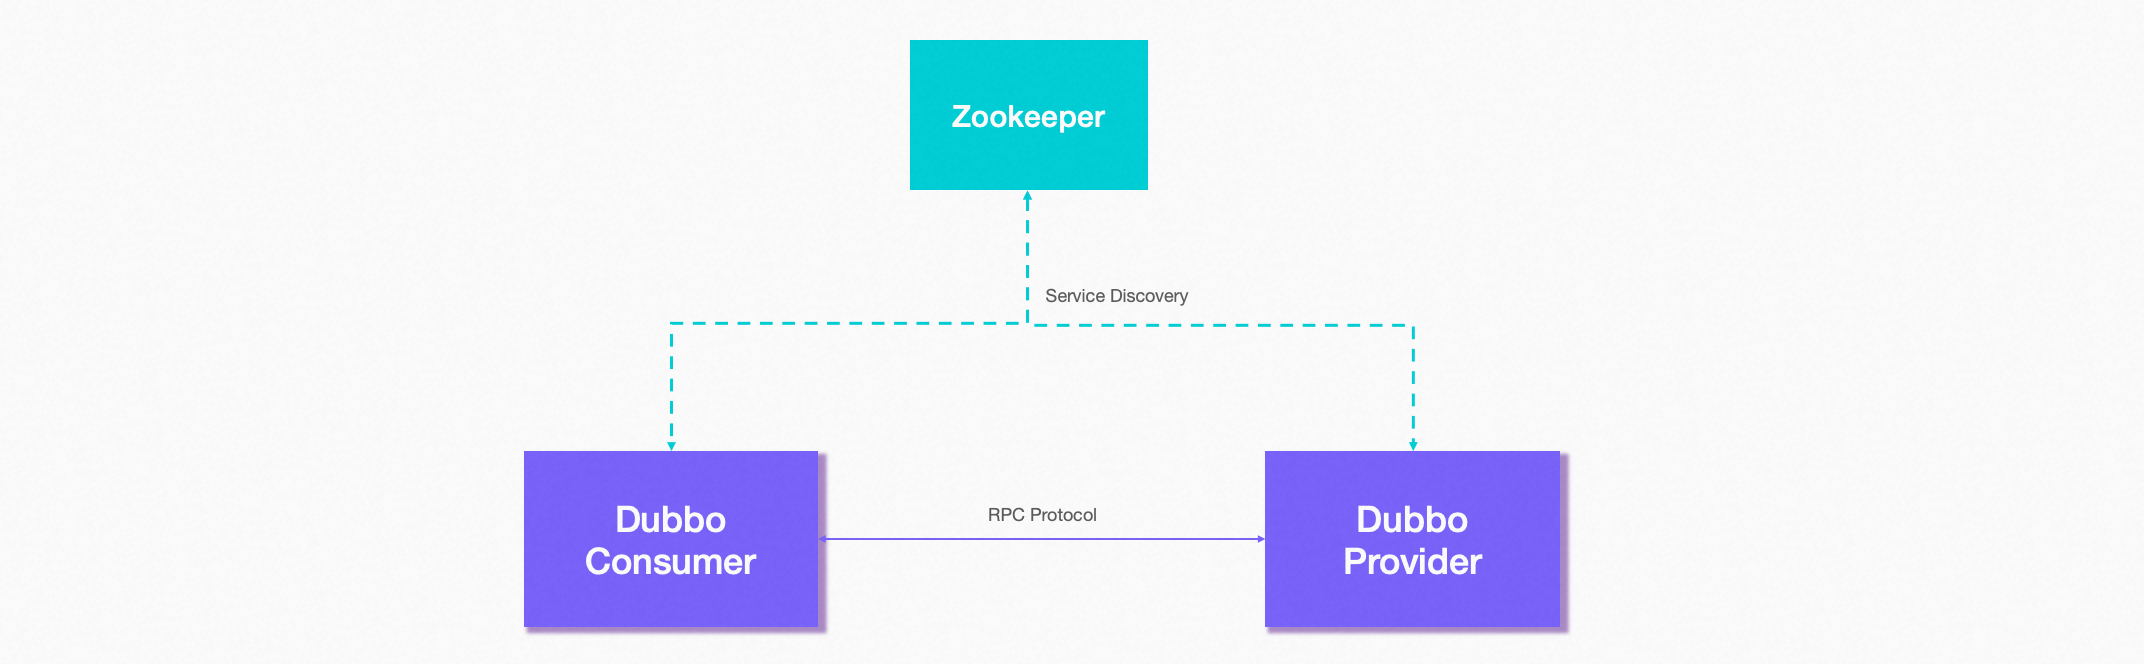 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 zeyad-azima/cve-2022-1388
F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
 cyber-niz/cve-2020-9496
Manual exploit for CVE-2020-9496, an unauthenticated Java deserialization RCE in Apache OFBiz XML-RPC, with step-by-step instructions for payload…
 snyk-labs/exploit-workshop
A step by step workshop to exploit various vulnerabilities in Node.js and Java applications
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 bishopfox/vulnerablegwtapp
An intentionally-vulnerable GWT-based web application to test tooling and techniques
 48484848484848/jmeter-cve-2018-1297-
Dockerized vulnerable Apache JMeter RMI environment for CVE-2018-1297 deserialization RCE, with ysoserial exploit commands, verification, and…
 nix-xin/vuln4japi
A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).
 aajuvonen/log4stdin
A Java application intentionally vulnerable to CVE-2021-44228
 willian-2-0-0-1/log4j-exploit-cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) that sets up a malicious LDAP server and delivers a Java payload to achieve remote code execution on…