
nmap-CVE-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…

Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…

Python exploit for CVE-2015-1635 (MS15-034) targeting HTTP.sys remote code execution vulnerability in IIS servers. Supports custom arguments for…

Exploit for CVE-2017-7269 targeting IIS 6.0 WebDAV remote code execution vulnerability. Enables buffer overflow exploitation on legacy Windows…

Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…

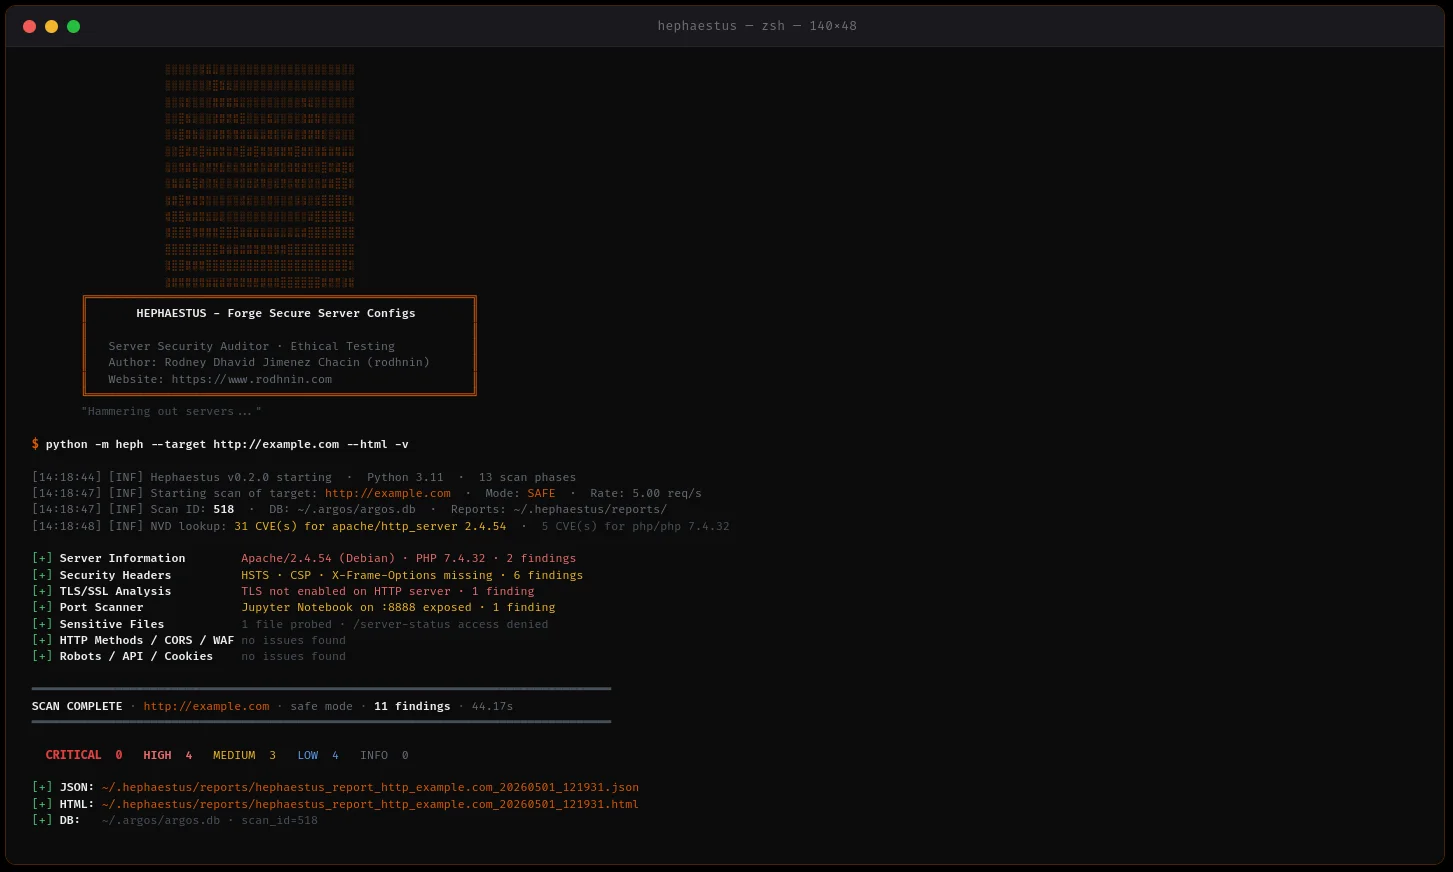
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.

Rusty Impersonate

Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…

Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…

Proof-of-concept exploit for CVE-2022-21907, a remote code execution vulnerability in the HTTP protocol stack (IIS). Includes a Python script and…

Bu laboratuvar ortamını sıfırdan kendim oluşturdum. Next.js uygulaması içerisinde giriş, ana sayfa ve admin sayfalarını hazırladım. Middleware ile…

Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…

CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。

CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…

A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.

Script fo testing CVE-2000-0649 for Apache and MS IIS servers

Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…

Authentication Bypass Vulnerability — CVE-2024–4358 — Telerik Report Server 2024

Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…