CVE-2018-8062
 oscarakaelvis/cve-2018-8062
Persistent XSS on Comtrend AR-5387un router
exploitationpenetration-testingphishing-tools+3
12 years ago
oscarakaelvis/cve-2018-8062Persistent XSS on Comtrend AR-5387un router
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
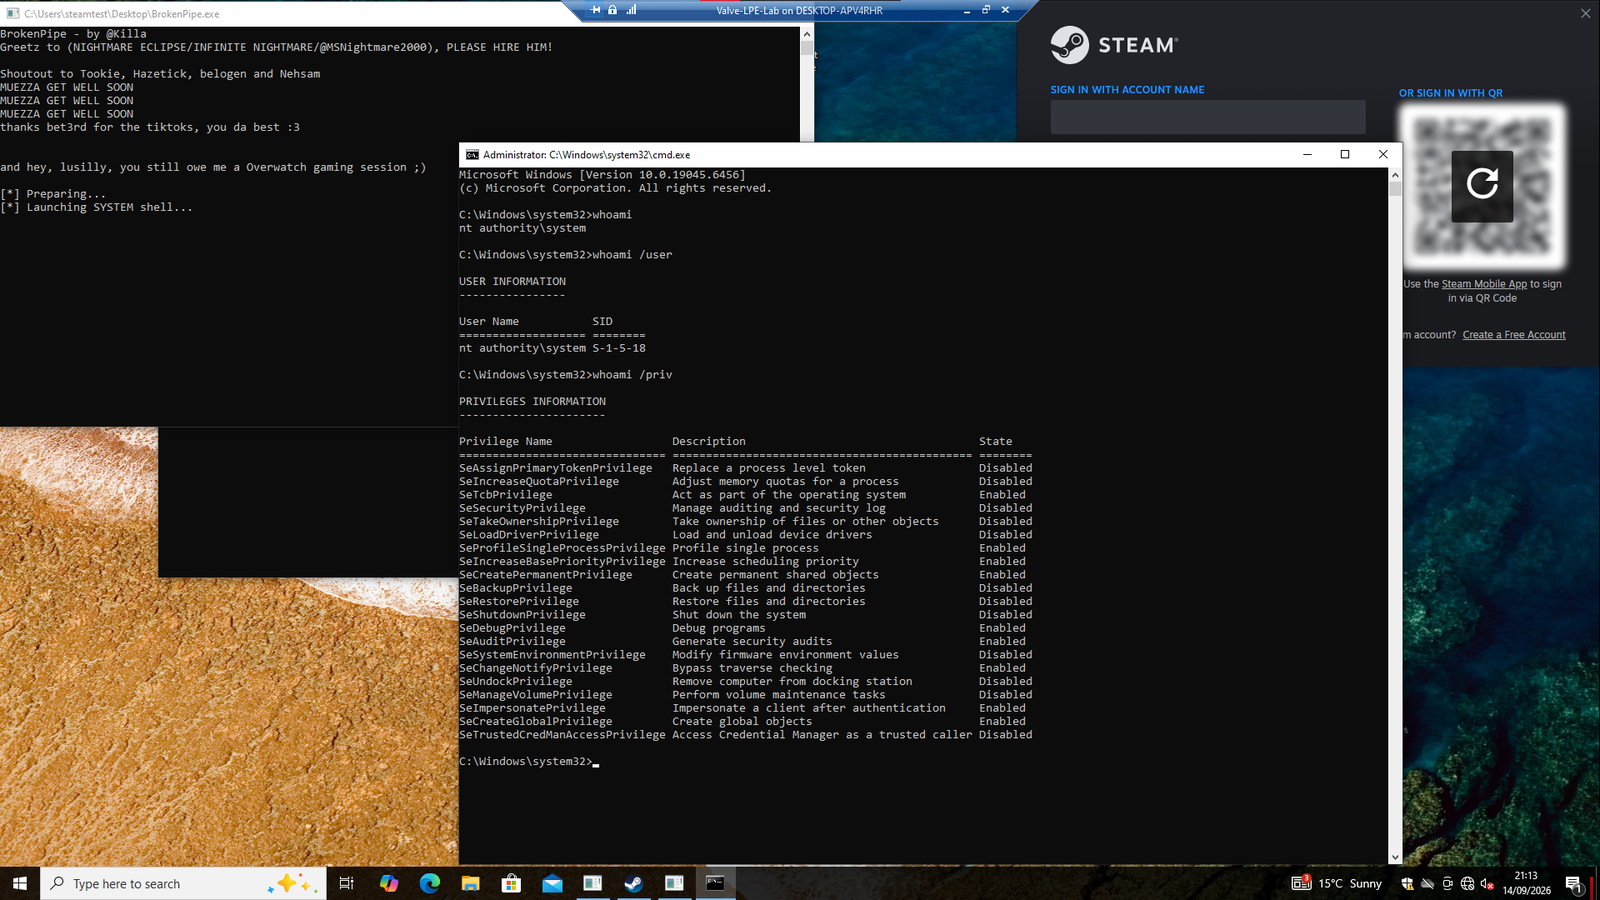 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
 motikan2010/cve-2021-34646
CVE-2021-34646 PoC
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 rxerium/cve-2024-39929
Detection method for Exim vulnerability CVE-2024-39929
 b0marek/cve-2023-4549
Repository for CVE-2023-4549 vulnerability.
 j0eyv/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, an Outlook/Exchange privilege escalation vulnerability that triggers NTLM credential theft via a…
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
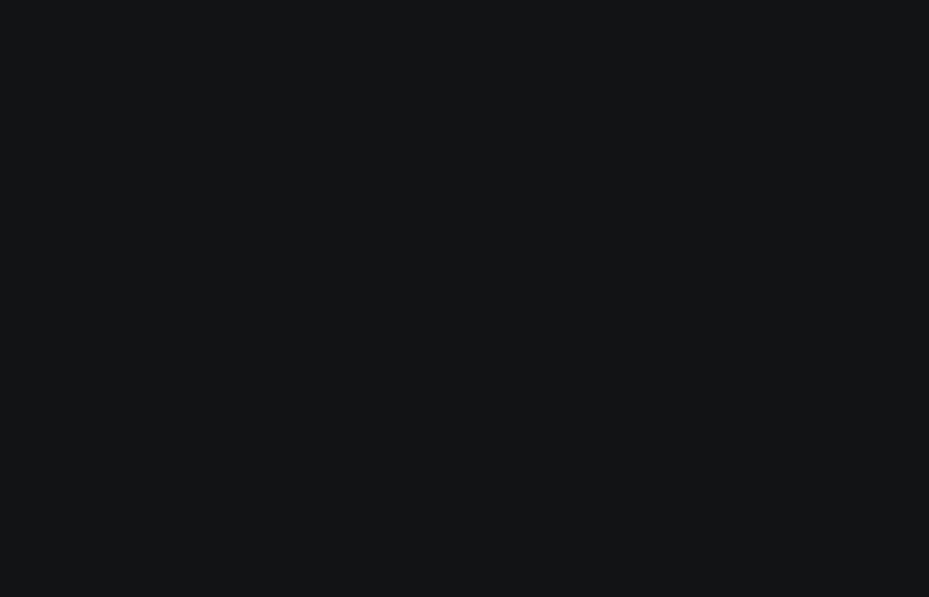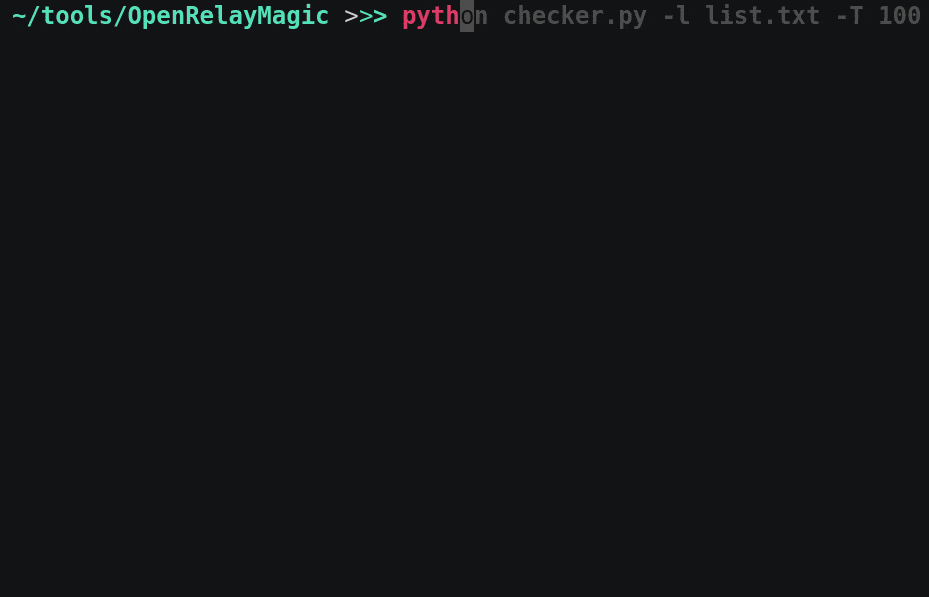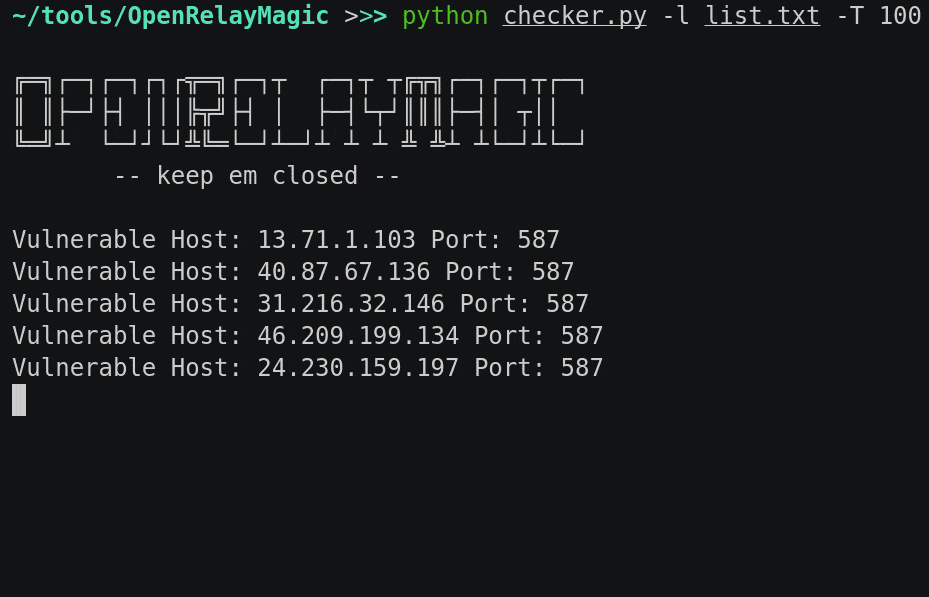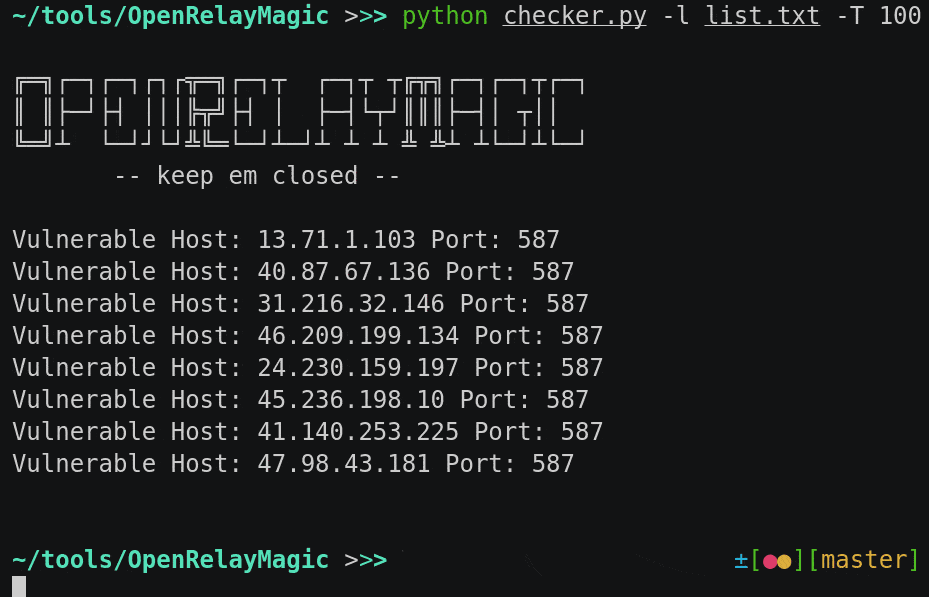 bl4ckmamb4/openrelaymagic
Tool to find SMTP servers vulnerable to open relay
 0xblackash/cve-2026-28289
CVE-2026-28289
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.