
hackingtool
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
cloud-securityexploitationforensics+9
79.5k
z4nzu/hackingtoolAll-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
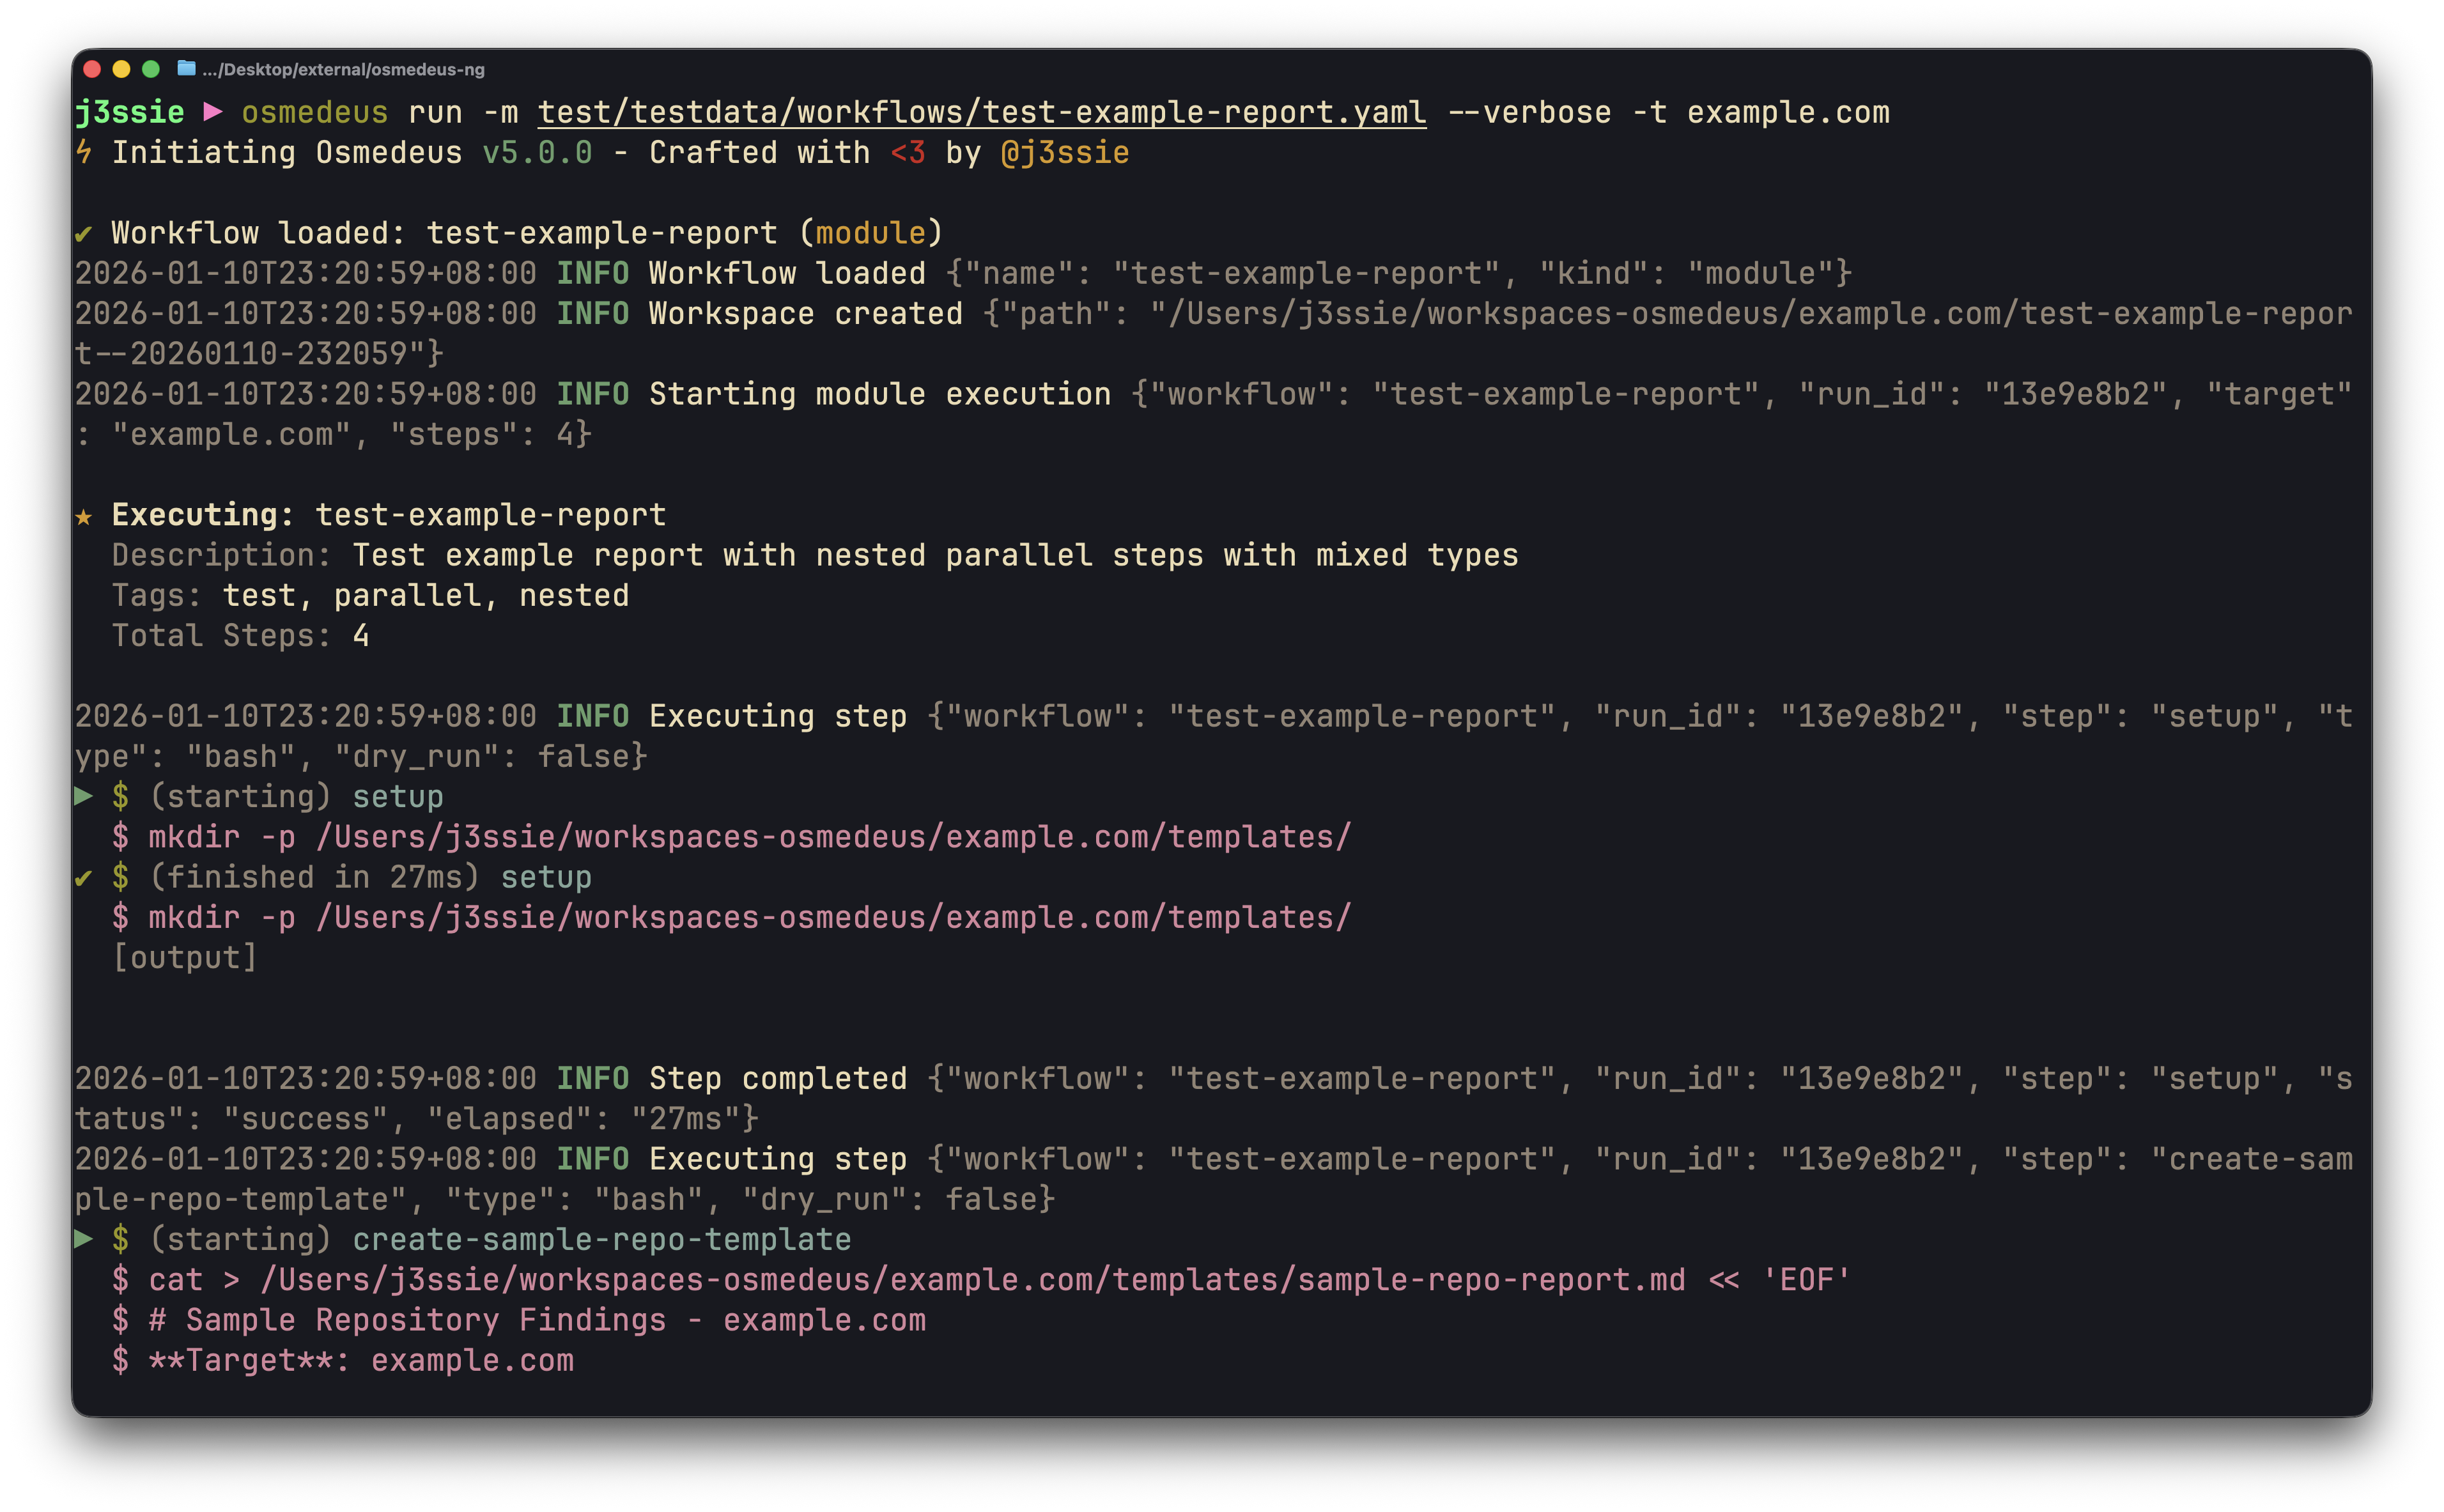 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 ixsly/cve-2022-41401
Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
 nccgroup/carnivore
Tool for assessing on-premises Microsoft servers authentication such as ADFS, Skype, Exchange, and RDWeb
 ivanacostarubio/libssh-scanner
A libssh CVE-2018-10933 scanner written in rust
 s4nshine/cve-2023-23169
Proof-of-concept demonstrating Local File Inclusion and Server-Side Request Forgery in PDFocus, with steps to reproduce and demo screenshots.
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 nullarray/intrec-pack
Intelligence and Reconnaissance Package/Bundle installer.
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
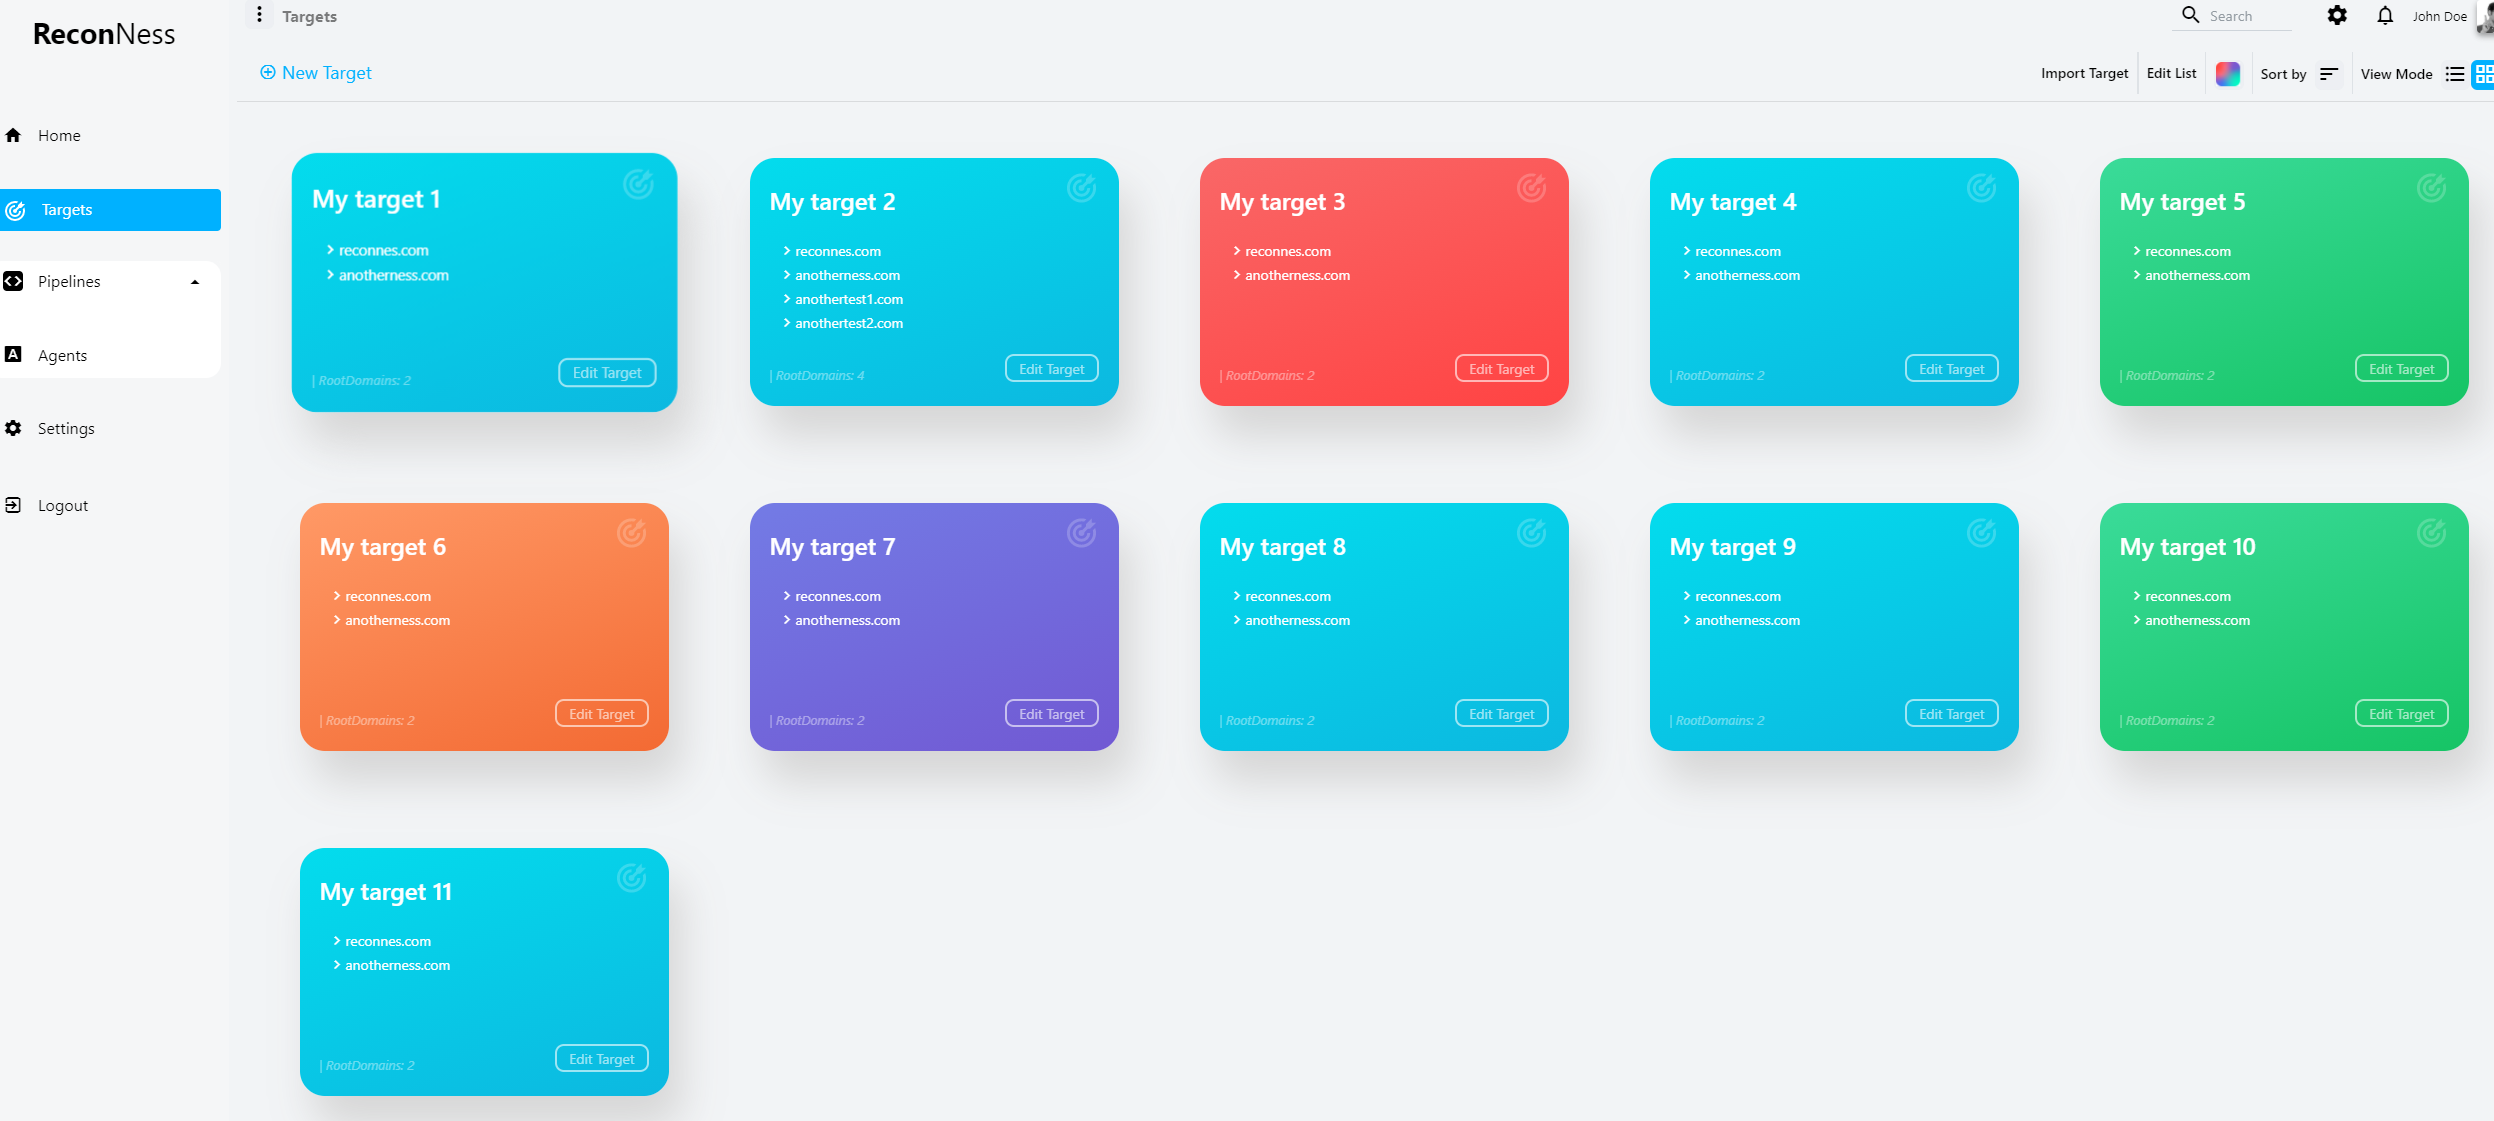 reconness/reconness
Automated continuous reconnaissance platform that orchestrates a pipeline of recon tools via scheduled or event-driven triggers, helping security…
 osyanina/westone-cve-2021-21980-scanner
A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.
 kernel-cyber/cve-2006-3392
Exploit for CVE-2006-3392: unauthenticated local file inclusion in Webmin before 1.290 and Usermin before 1.220, bypassing path traversal filters…
 sense-of-security/adrecon
ADRecon is a tool which gathers information about the Active Directory and generates a report which can provide a holistic picture of the current…