
cve-2017-5638
 bongbongco/cve-2017-5638
Proof-of-concept exploit for Apache Struts2 remote code execution vulnerability CVE-2017-5638, demonstrating exploitation via crafted Content-Type…
exploitationpayload-generationpenetration-testing+2
bongbongco/cve-2017-5638Proof-of-concept exploit for Apache Struts2 remote code execution vulnerability CVE-2017-5638, demonstrating exploitation via crafted Content-Type…
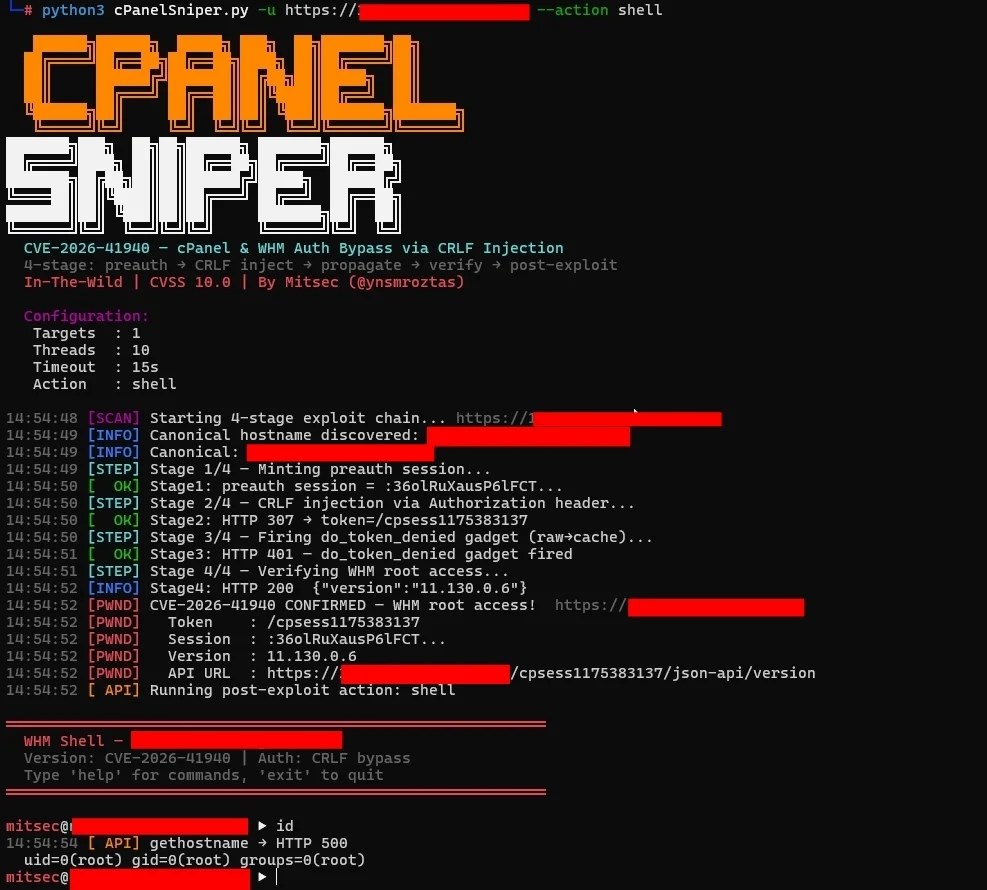 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 hash3lizer/wifibroot
A Wireless (WPA/WPA2) Pentest/Cracking tool. Captures & Crack 4-way handshake and PMKID key. Also, supports a deauthentication/jammer mode for stress…
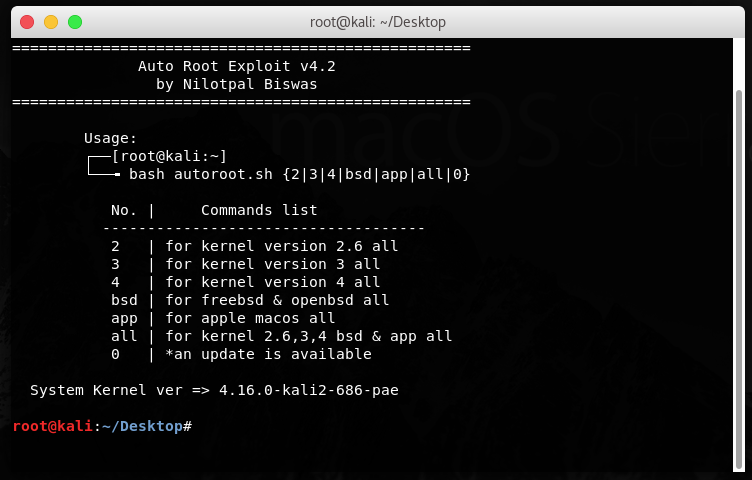 nilotpalbiswas/auto-root-exploit
Auto Root Exploit Tool
 gainsec/cve-2017-16744-and-cve-2017-16748-tridium-niagara
Proof of Concept (PoC) for CVE: 2017-16744 and 2017-16748
 polosss/by-poloss..-..cve-2026-15038-poc
POC 4 CVE-2026-15038
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
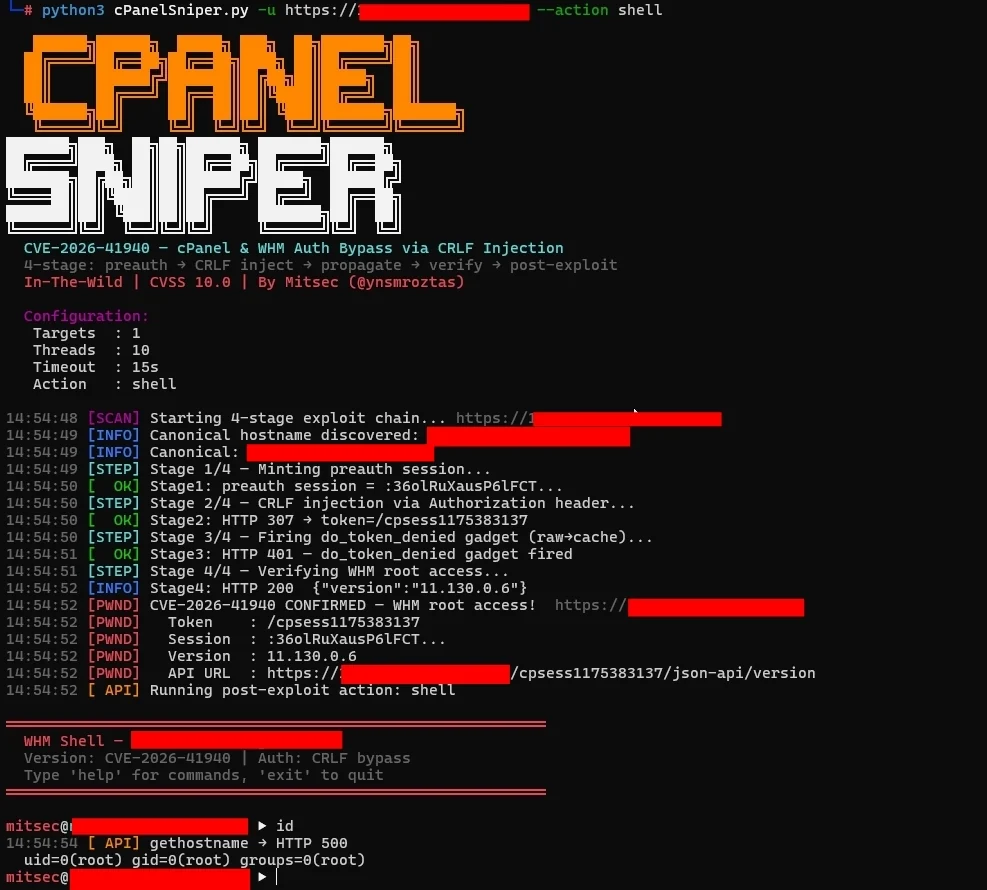 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 can/cve-2015-5374-dos-poc
DoS exploit for CVE-2015-5374 targeting Siemens SIPROTEC 4 and Compact EN100 Ethernet modules via a crafted UDP packet to port 50000, with an…
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 hunt-benito/pgadmin-ai-assistant-sql-injection-cve-2026-17351-lexer-differential-bypass
Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…
 javokhir-sec/cve-poc-hub
🛡️ CVE Proof-of-Concept Hub — 4 PUBLISHED CVEs · 5 under review (VulnCheck) · SuiteCRM batch withdrawn
 khashayarnzk/cve-2025-2945-pgadmin-rce
PoC for CVE-2025-2945 — pgAdmin 4 authenticated eval() injection RCE, CVSS 9.9
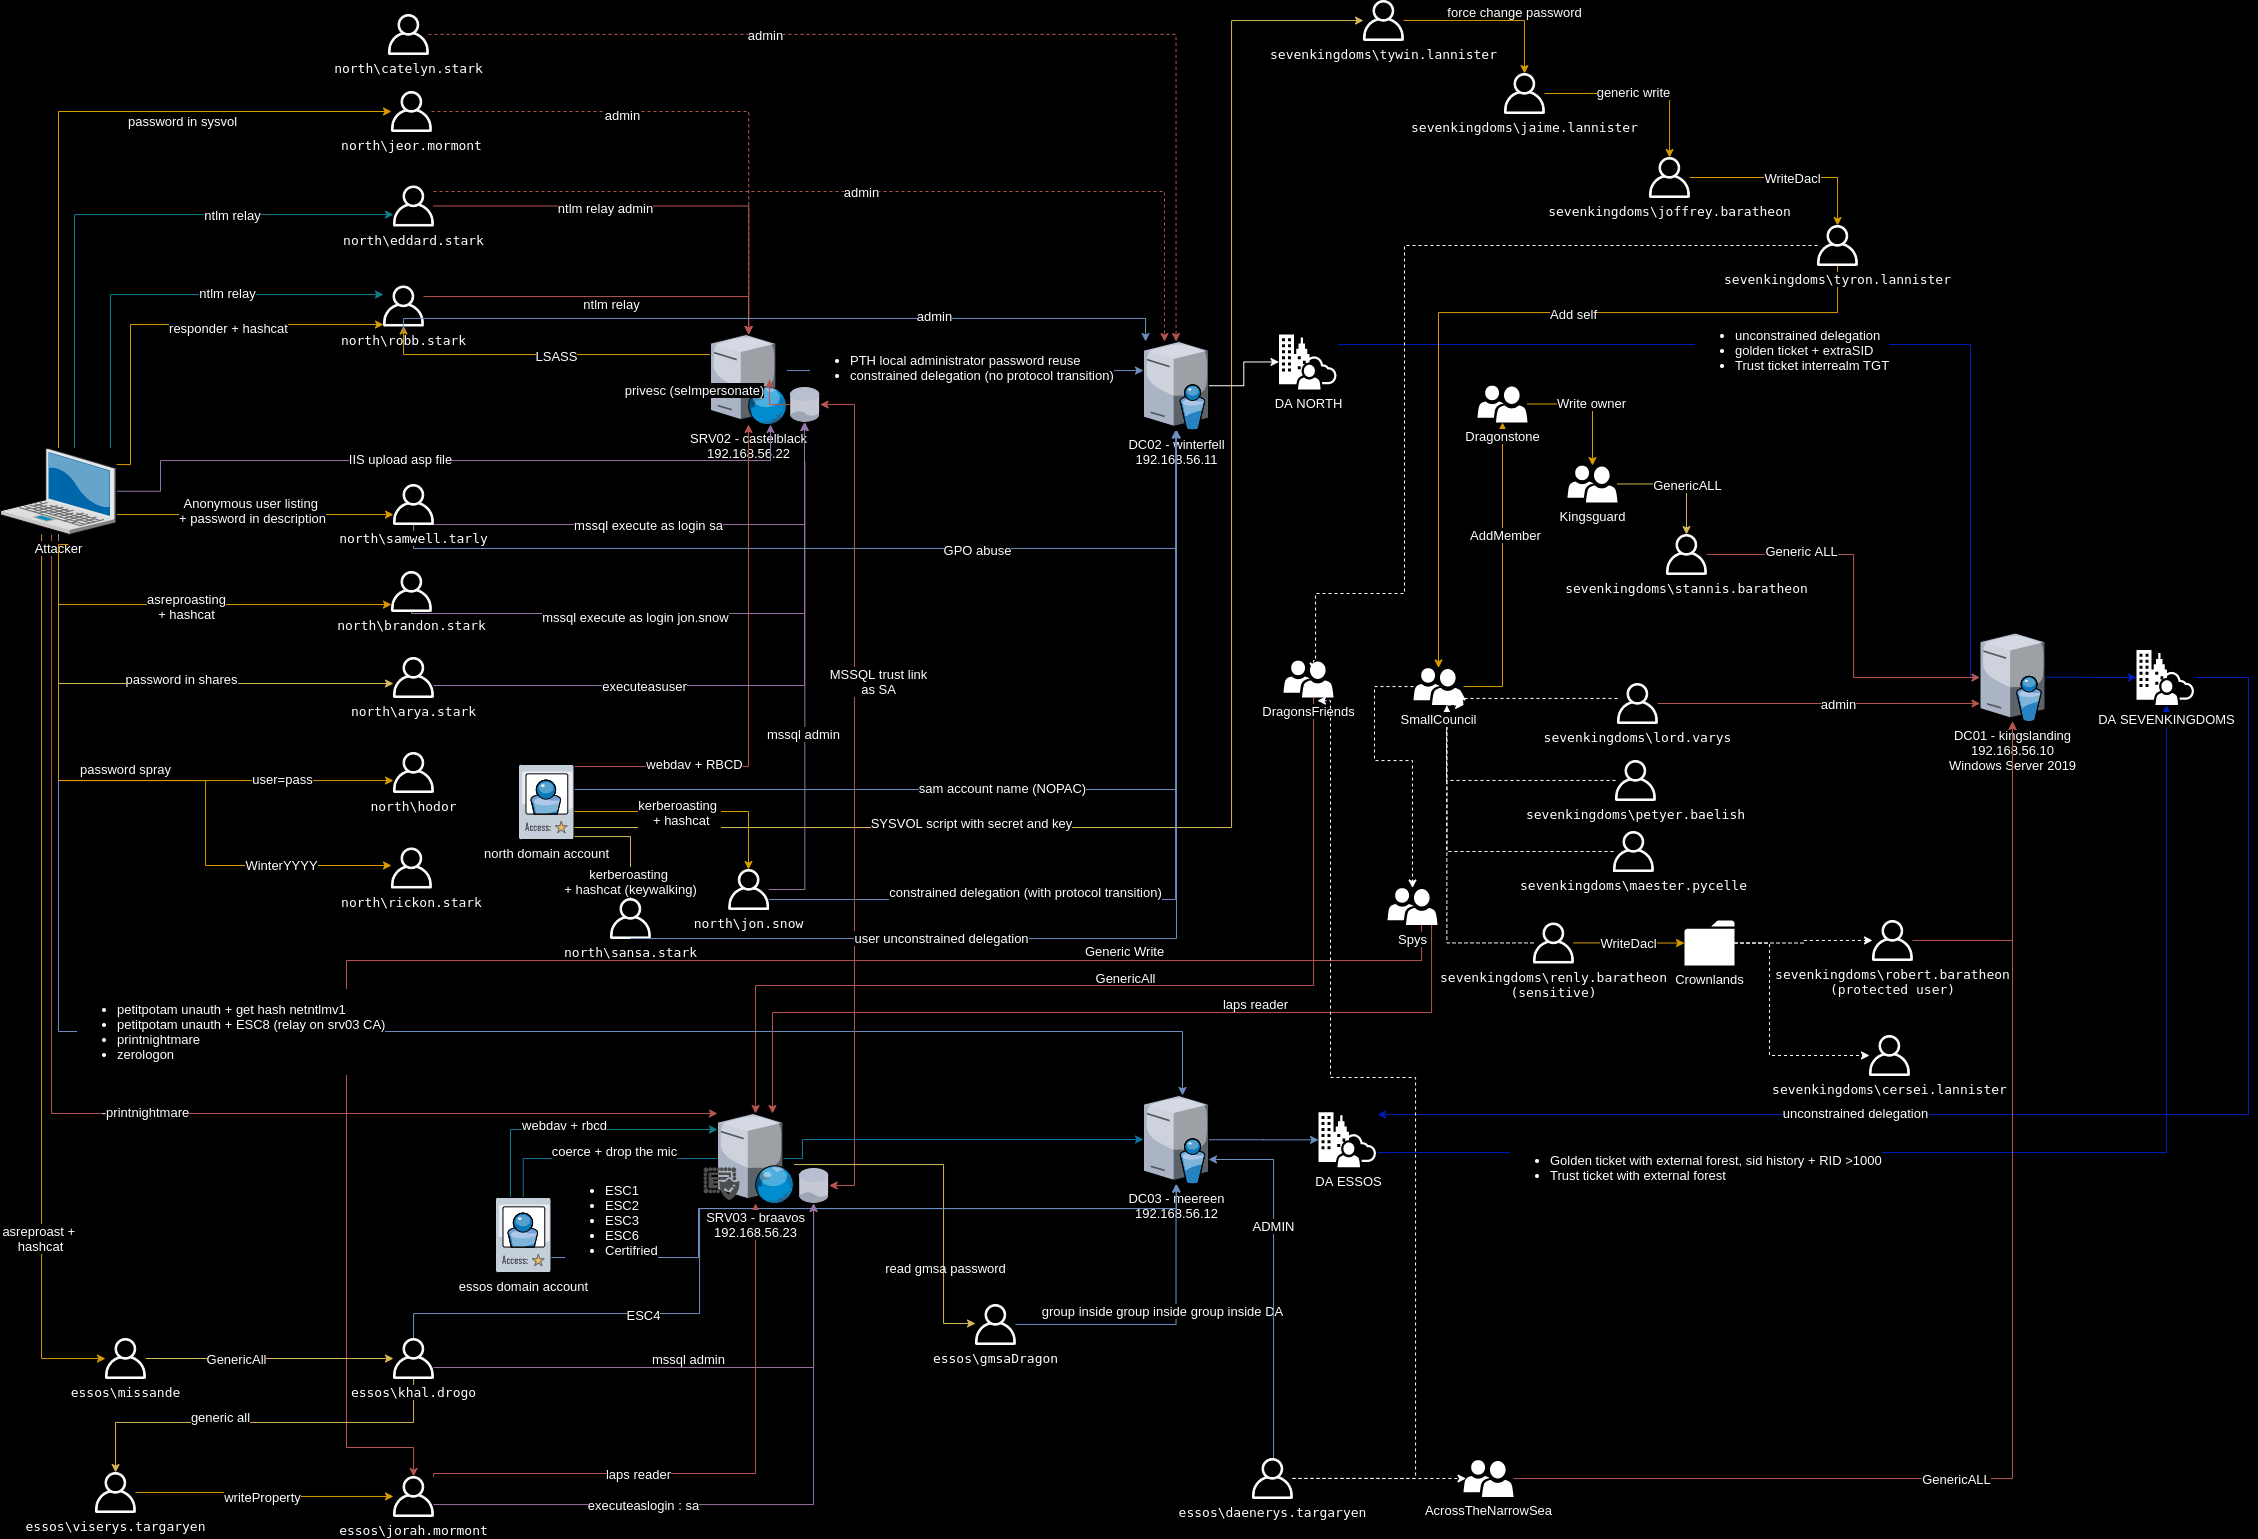 lkarlslund/deploy-goad
Script to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
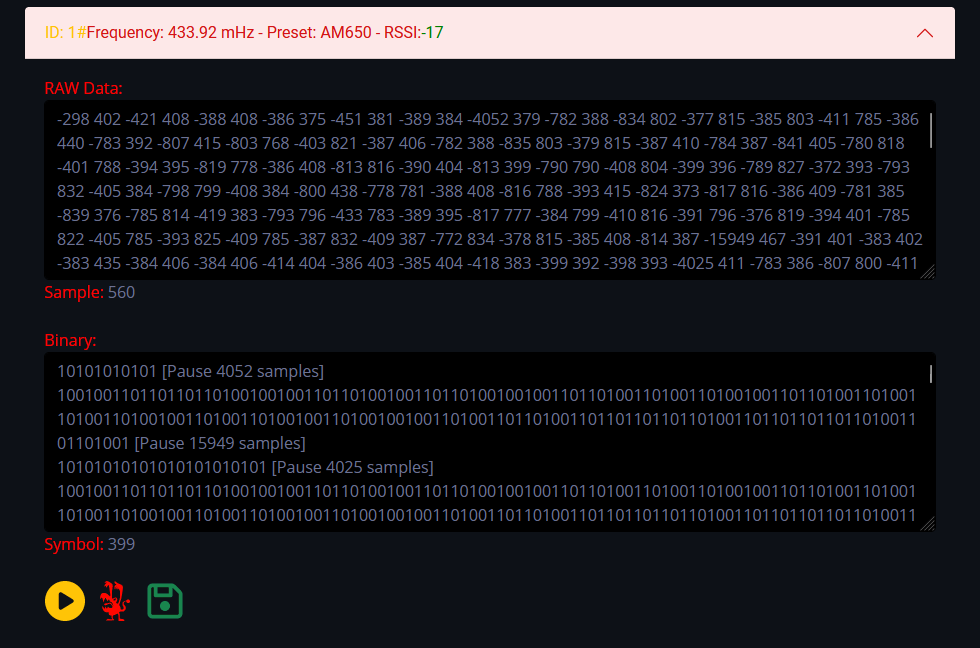 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 analyticeth/tesla-security-research
Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…