
Octopus
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
command-and-controlencryption-decryption-toolsinformation-gathering+3
7695 years ago
mhaskar/octopusOpen source pre-operation C2 server based on python and powershell
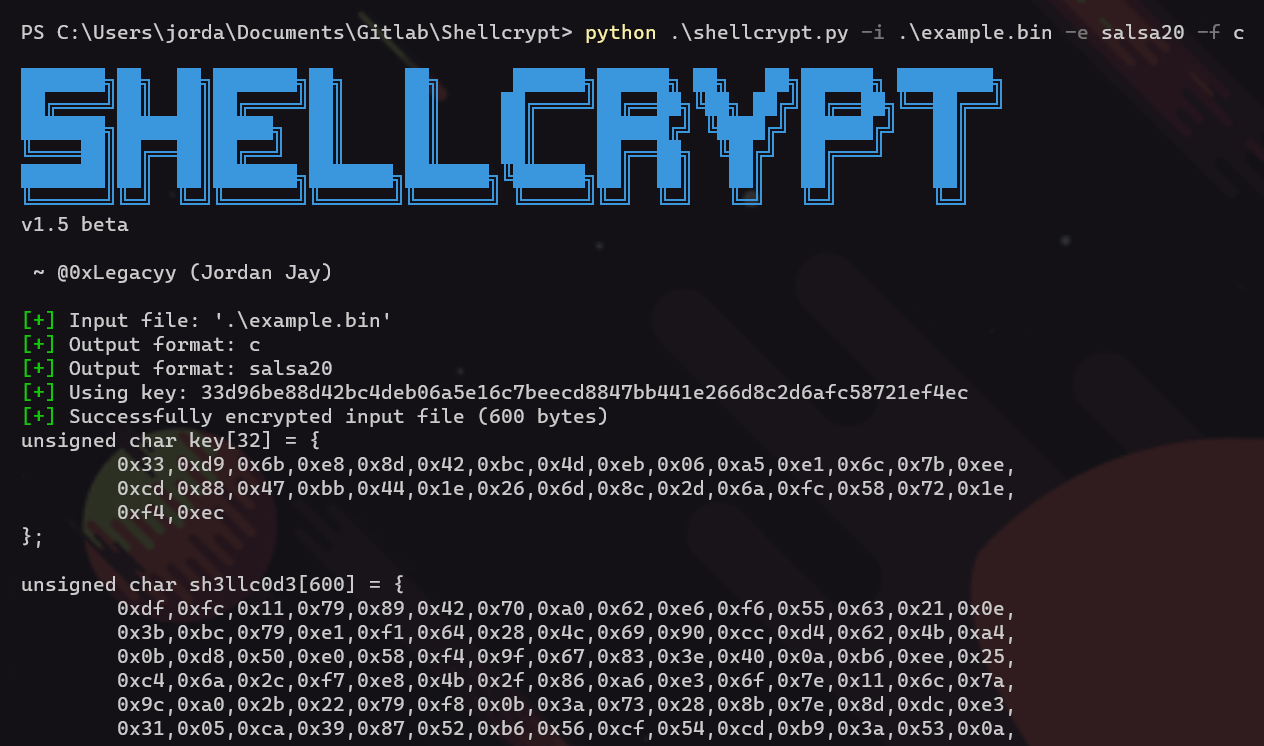 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
 r00t-3xp10it/backdoorppt
transform your payload.exe into one fake word doc (.ppt)
 tsuyoken/imgbackdoor
Hide your payload into .jpg file

 0x00-0x00/cve-2014-6271
Shellshock exploitation script that is able to upload and RCE using any vector due to its versatility.
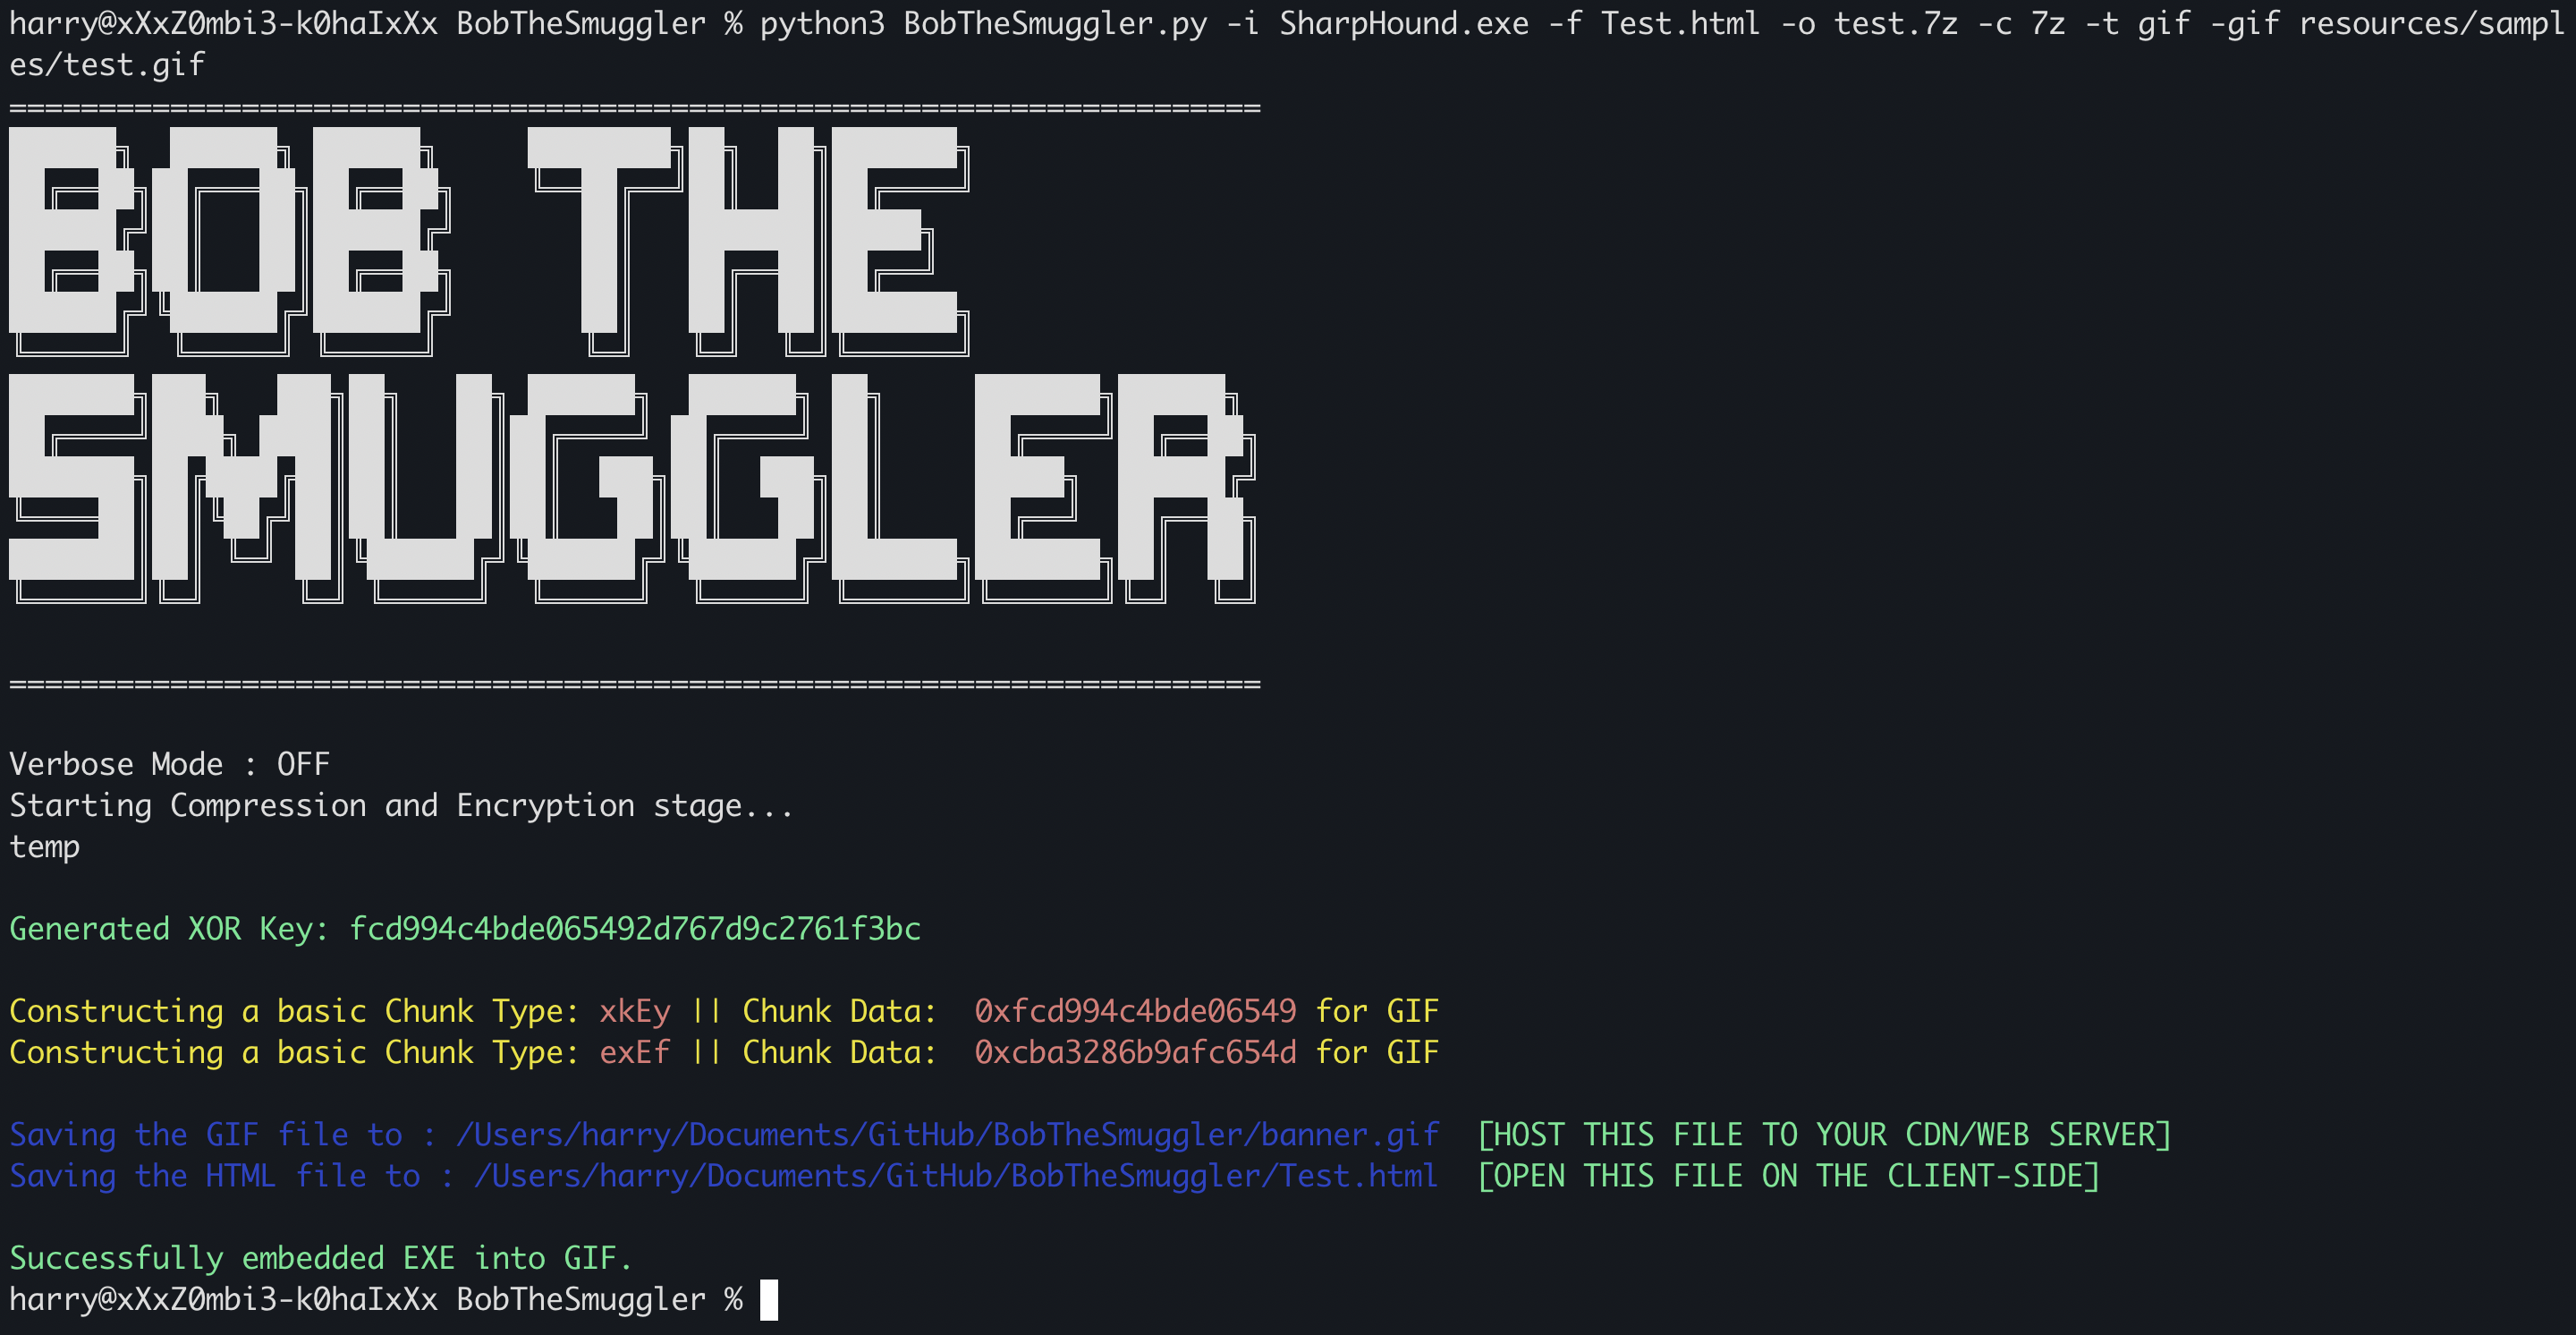 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 scumdestroy/cve-2019-5420.rb
POC Exploit written in Ruby
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
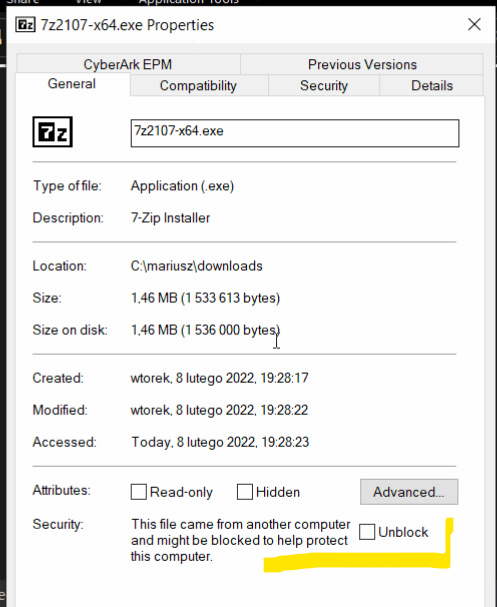 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 hasherezade/exe_to_dll
Converts a EXE into DLL
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 dlegs/php-jpeg-injector
Injects PHP payloads into JPEG images for web application exploitation, bypassing GD library image processing to achieve remote code execution.