

weaponised-XSS-payloads
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
exploitationpayload-developmentpayload-generation+3
1.4k
hakluke/weaponised-xss-payloadsXSS payloads designed to turn alert(1) into P1
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 synacktiv/laravel-crypto-killer
A tool designed to exploit bad implementations of decryption mechanisms in Laravel applications.
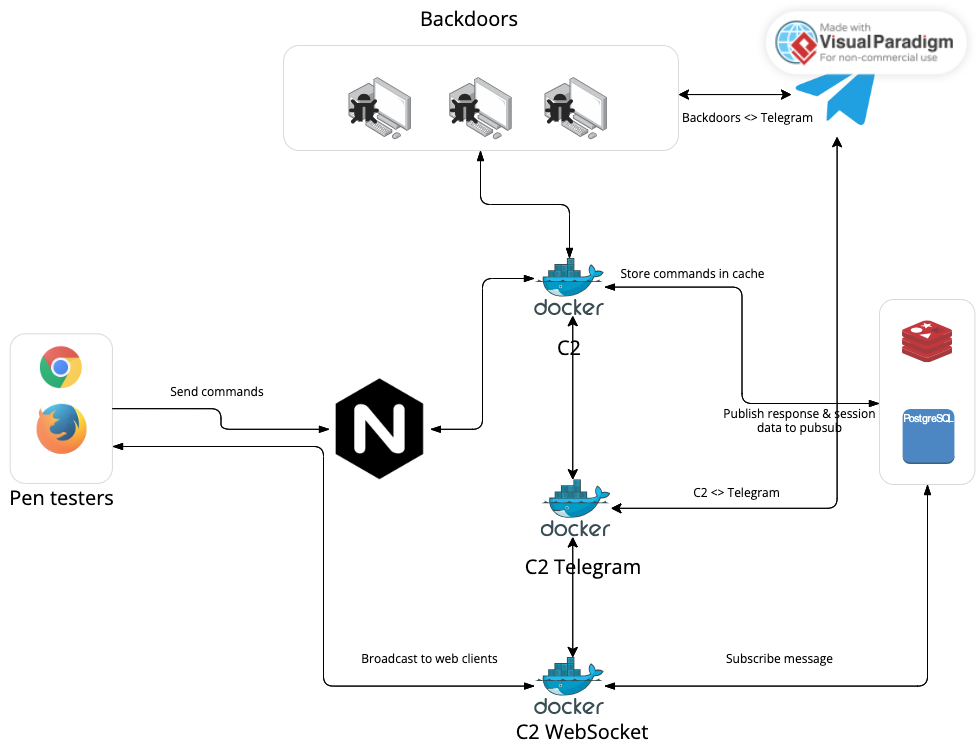 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 shyambhanushali/react2shell
React2Shell is a Python-based proof-of-concept tool designed to exploit CVE-2025-55182 and CVE-2025-66478, both impacting Next.js applications using…
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
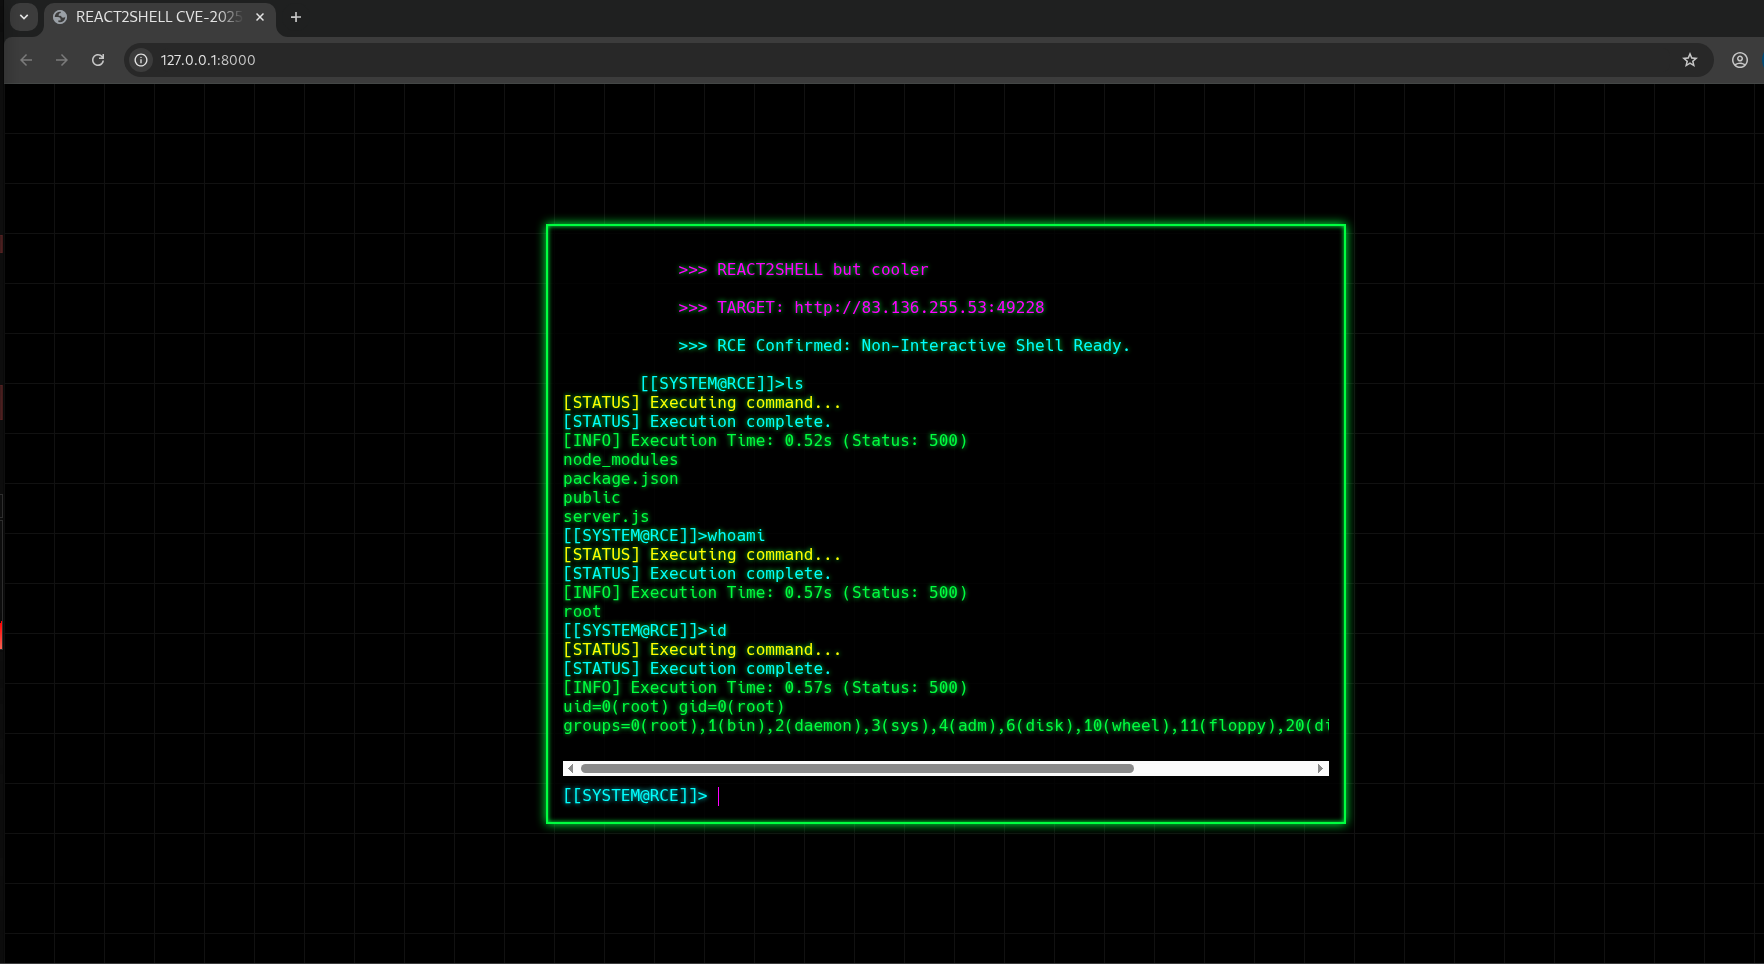 raivenlockdown/web-cli_rce_react2shell
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…
 dragonked2/cve-2024-50379-poc
This repository contains a Python script designed to exploit CVE-2024-50379, a vulnerability that allows attackers to upload a JSP shell to a…
 haxorstars/cve-2025-54068
A tool designed to exploit CVE-2025-54068 and Remote Command Execution of the Livewire project.
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 d0rb/cve-2024-27130
This Python script is designed as a proof-of-concept (PoC) for the CVE-2024-27130 vulnerability in QNAP QTS
 jcaz2378/comfyuirce
Proof-of-concept exploit payload for CVE-2025-67303 targeting Git repositories. Designed for security testing and vulnerability validation.
 redteamblueteam/cve-2024-5084-red-team
Proof-of-concept exploit for CVE-2024-5084 (Hash Form WordPress plugin) demonstrating unauthenticated file upload to RCE. Designed for educational…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 cdedmondson/modified-cve-2019-15107
Modified exploit for CVE-2019-15107 with a Perl reverse shell payload. Designed for penetration testing of the targeted web application vulnerability.
 soch4n/cve-2018-7600
Python exploit for CVE-2018-7600 (Drupalgeddon2) targeting remote code execution in Drupal CMS. Designed for penetration testing and vulnerability…