CVE-2025-22457-vulnserver-lab

Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…

Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…

Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

A list of useful payloads and bypass for Web Application Security and Pentest/CTF

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…

A list of interesting payloads, tips and tricks for bug bounty hunters.

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

All about bug bounty (bypasses, payloads, and etc)

Nishang - Offensive PowerShell for red team, penetration testing and offensive security.

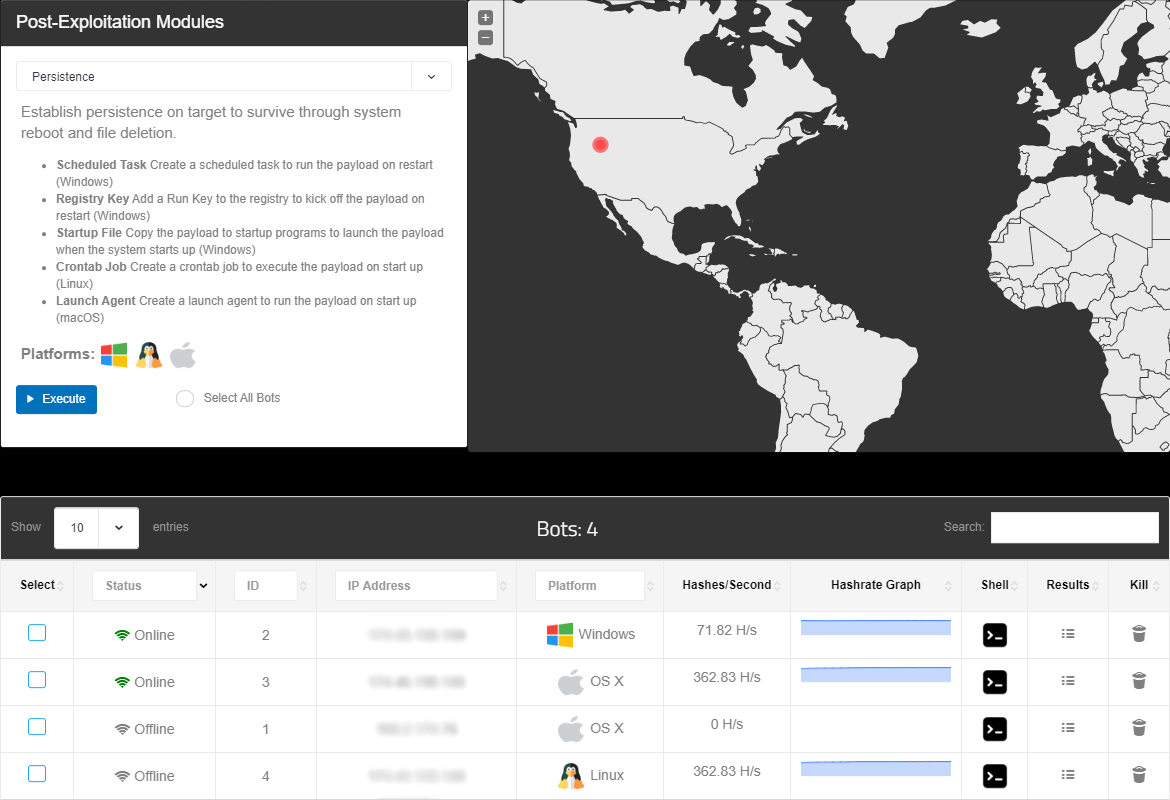
An open-source post-exploitation framework for students, researchers and developers.

Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.

Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…

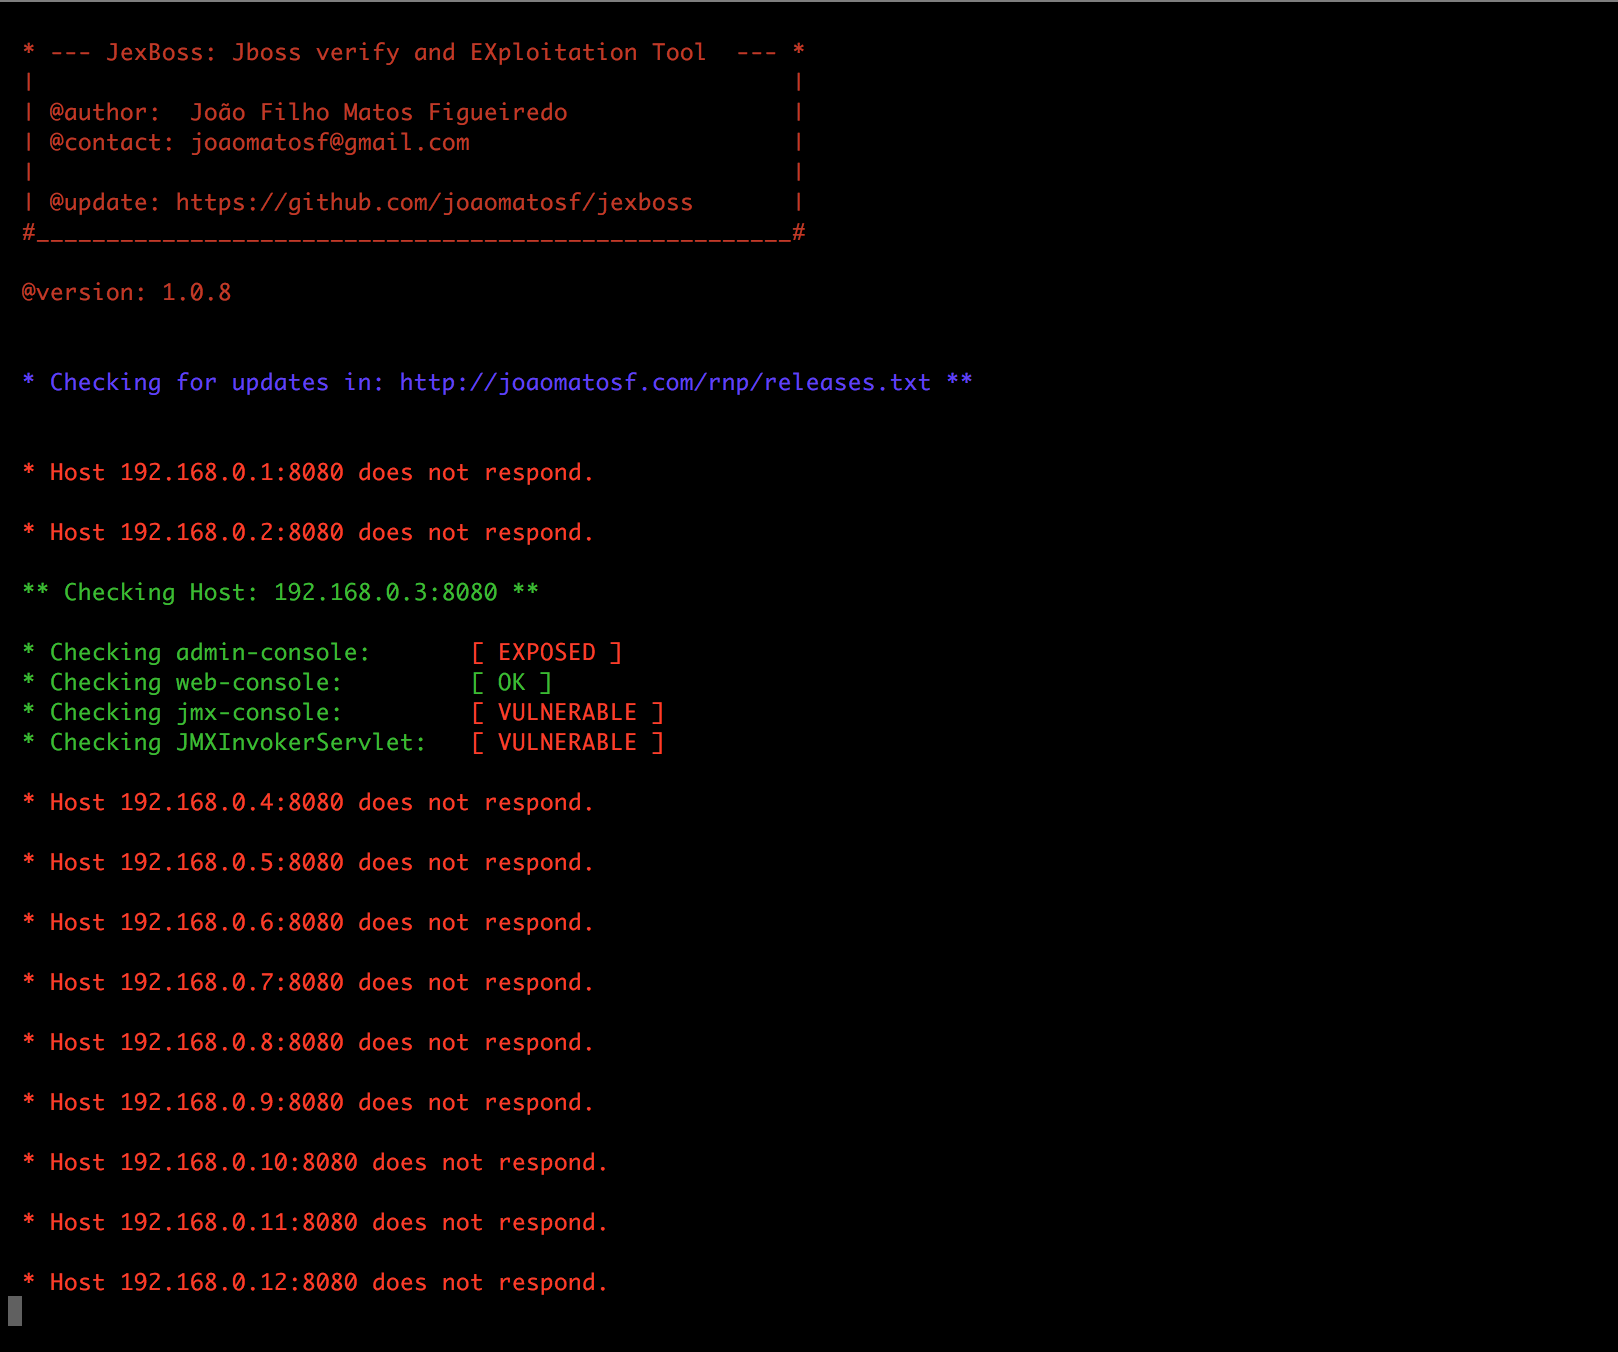
JexBoss: Jboss (and Java Deserialization Vulnerabilities) verify and EXploitation Tool