

shredder-rs
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
binary-analysiseducationexploitation+4
112
zx0cf1/shredder-rsA high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 egebalci/sgn
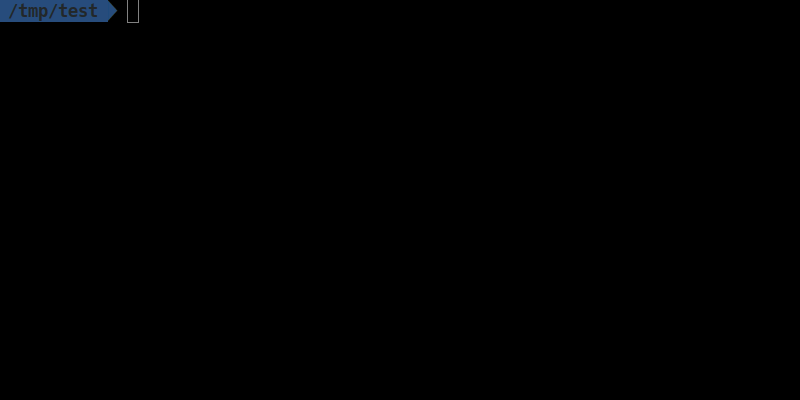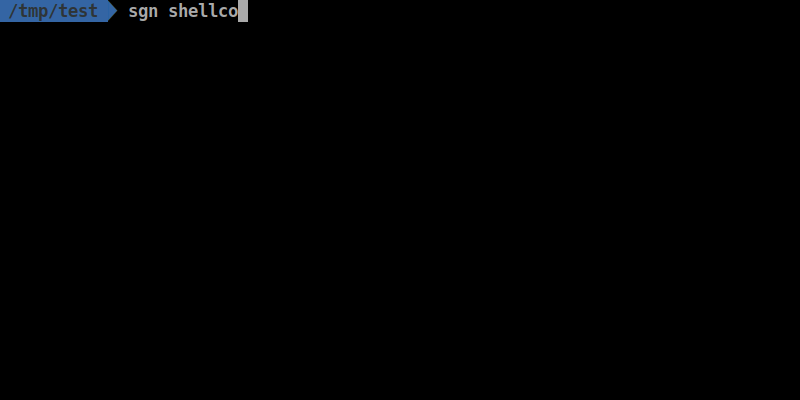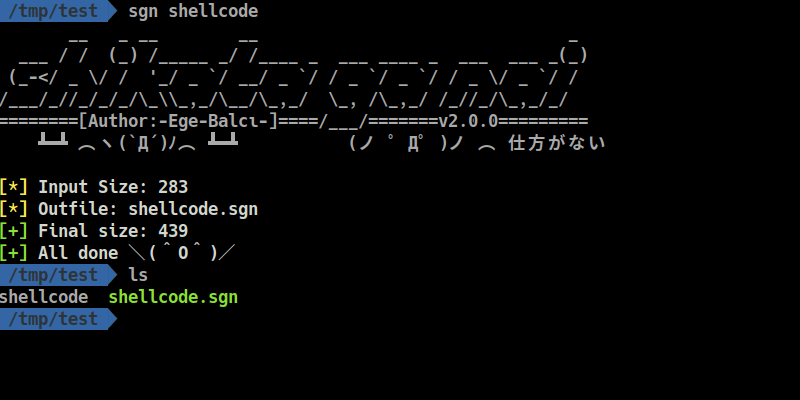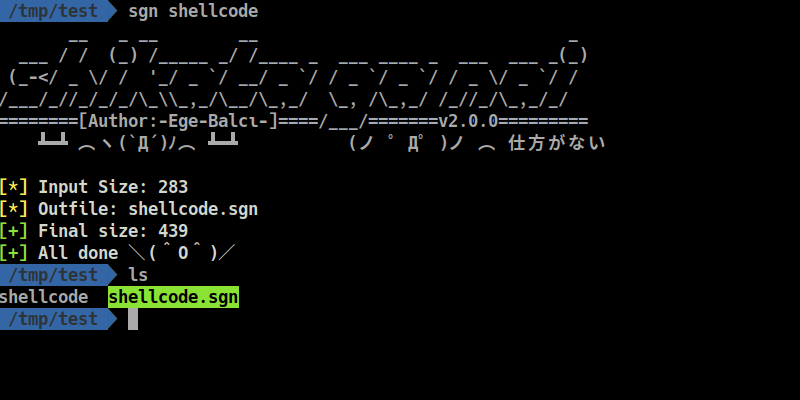
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 abstractengine/pentest-muse-cli
AI-powered assistant for penetration testers that generates payloads, analyzes code, performs reconnaissance, and executes command-line actions to…
 ab1gale/phpcms-2008-cve-2018-19127
Proof-of-concept exploit for CVE-2018-19127 in phpcms 2008, demonstrating remote code execution via crafted template parameter leading to webshell…
 aelmokhtar/cve-2024-34716
Proof-of-concept exploit for CVE-2024-34716, a PNG-driven XSS to RCE chain in PrestaShop 8.1.5, enabling remote code execution via crafted image…
 redteampentesting/moodle-rce-calculatedquestions
Scripts for Analysis of a RCE in Moodle Calculated Questions (CVE-2024-43425)
 dor-tumarkin/cve-2019-17564-fastjson-gadget
Basic code for creating the Alibaba FastJson + Spring gadget chain, as used to exploit Apache Dubbo in CVE-2019-17564 - more information available at…
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 cyberh3als/cve-2023-36845-poc
Automated PoC script for CVE-2023-36845, exploiting a PHP flaw in Juniper Junos OS J-Web to remotely modify PHPRC and achieve code injection on…
 v3cn4x00/poc-cve-2025-66034
Automated exploit for CVE-2025-66034, chaining path traversal and XML injection in fontTools varLib to achieve unauthenticated remote code execution…
 xxconi/cve-2026-5718
CVE-2026-5718: Unauthenticated File Upload To RCE in DnD Upload CF7 Plugin
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
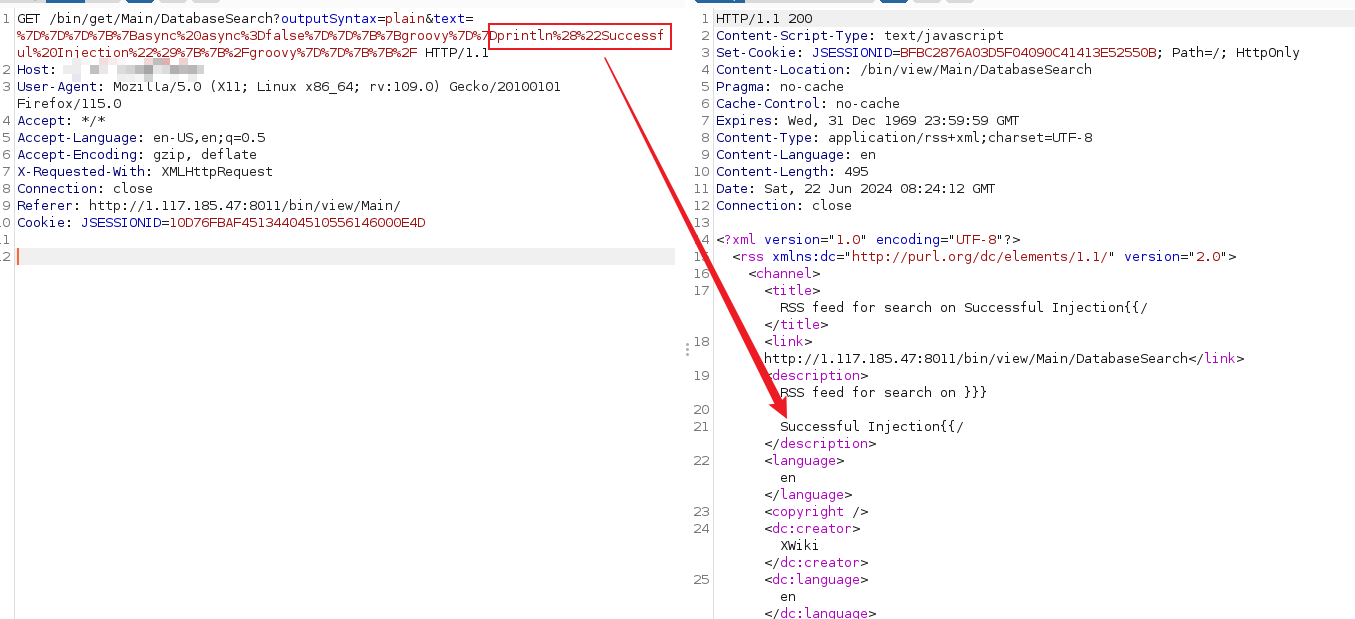 nanowraith/cve-2024-31982
Proof-of-concept exploit for CVE-2024-31982: Java Server-Side Template Injection (SSTI) leading to remote code execution via Groovy payload injection.
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…