
CVE-2025-2005
 h4ckxel/cve-2025-2005
Proof-of-concept exploit for CVE-2025-2005, an arbitrary file upload vulnerability in the WordPress Front-End Users Plugin (<=3.2.32). Includes…
educationexploitationpayload-generation+3
1
h4ckxel/cve-2025-2005Proof-of-concept exploit for CVE-2025-2005, an arbitrary file upload vulnerability in the WordPress Front-End Users Plugin (<=3.2.32). Includes…
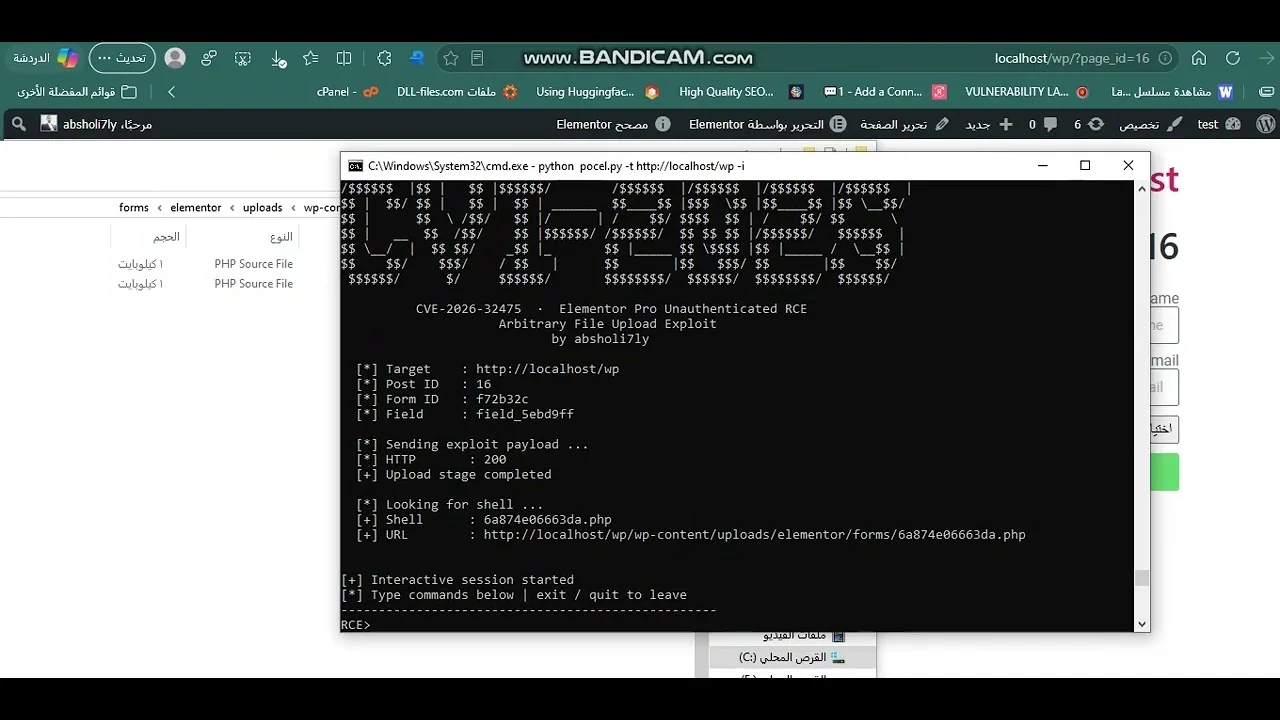 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 randomrobbiebf/cve-2023-2877
Formidable Forms < 6.3.1 - Subscriber+ Remote Code Execution
 shinthink/cve-2026-56291
Balbooa Forms (com_baforms) < 2.4.1 — Unauthenticated File Upload to RCE via form.uploadAttachmentFile | CVSS 9.8 | CISA KEV
 exdev994/cve-2026-0740-mass
PoC untuk CVE-2026-0740: Ninja Forms File Uploads <= 3.3.26 — Unauthenticated Arbitrary File Upload yang dapat mengarah ke RCE.
 xshadow-here/cve-2026-4883
Piotnet Forms Pro <= 2.1.40 - Unauthenticated Arbitrary File Upload → RCE
 1beelze/cve-2026-14894
Exploit for CVE-2026-14894, an unauthenticated file upload to RCE in WordPress Super Forms ≤ 6.3.313. Uploads PHP webshell and supports single-target…
 0xabcd01/cve-2026-48866
CVE-2026-48866 — Gravity Forms <= 2.10.0.1 Arbitrary File Deletion via Path Traversal (CVSS 9.6)
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…