CVE-2019-5475-Nexus-Repository-Manager-

Exploit payload for CVE-2019-5475 in Nexus Repository Manager, enabling remote code execution via crafted Yum capability configuration.

Exploit payload for CVE-2019-5475 in Nexus Repository Manager, enabling remote code execution via crafted Yum capability configuration.

Tiny File Manager <= 2.4.6 - Remote Code Execution (RCE)

ManageEngine PAM360, Password Manager Pro, and Access Manager Plus unauthenticated remote code execution vulnerability PoC-exploit

Authenticated exploit for Moodle 3.9 that escalates teacher privileges to manager role and achieves remote code execution via malicious plugin upload.

CVE-2025-56399 – Remote Code Execution in laravel-file-manager v3.3.1. Exploits misconfigured config in Laravel File Manager to upload and verify a…

A file upload restriction bypass vulnerability in Pluck CMS before 4.7.13 allows an admin privileged user to gain access in the host through the…

Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…

Proof-of-concept exploit for CVE-2022-47966, a pre-authentication remote code execution vulnerability in multiple ManageEngine products via SAML…

Python exploit for RCE in Wordpress

Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…

A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.

Post-authentication reverse shell exploit for Webmin <=1.984 leveraging CVE-2022-0824 File Manager privilege escalation. Downloads and executes a CGI…

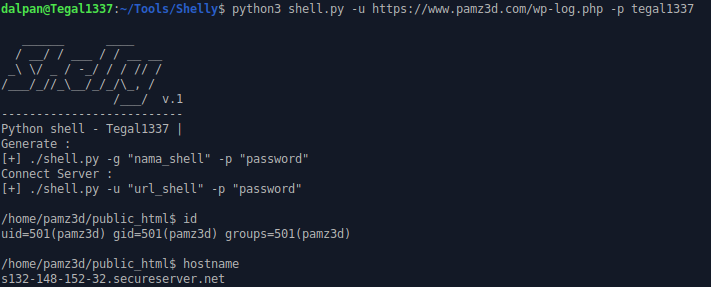
Simple Backdoor Manager with Python (based on weevely)

Apache Tomcat Manager API WAR Shell Upload

Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…

Exploitation of a vulnerability in Cisco's node-jose, a JavaScript library created to manage JWT.

Proof-of-Concept script for WordPress plugin Bit File Manager version <= 6.5.7 Authenticated (Subscriber+) Limited JavaScript File Upload…

Proof-of-concept exploit for CVE-2024-21542 demonstrating arbitrary file write via Zip Slip in Luigi pipeline manager. Generates malicious archives…