


 zeng9t/cve-2018-4407-ios-exploit
CVE-2018-4407,iOS exploit

 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 ax/apk.sh
Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
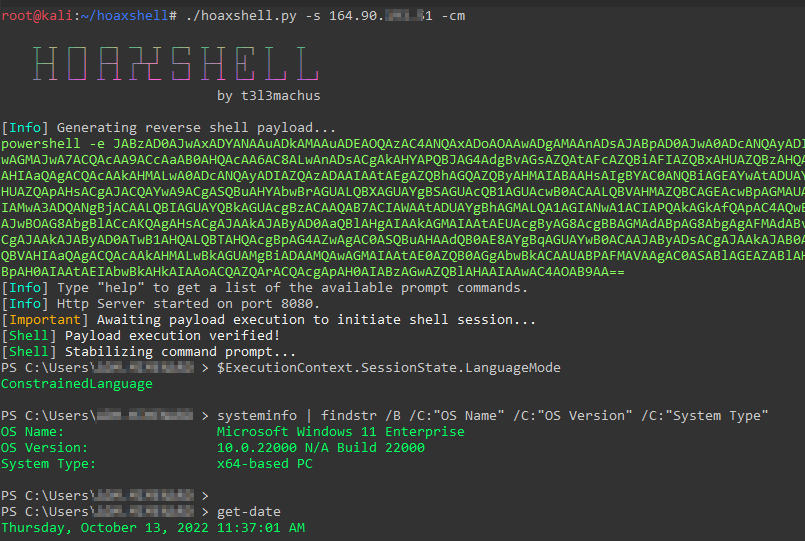 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
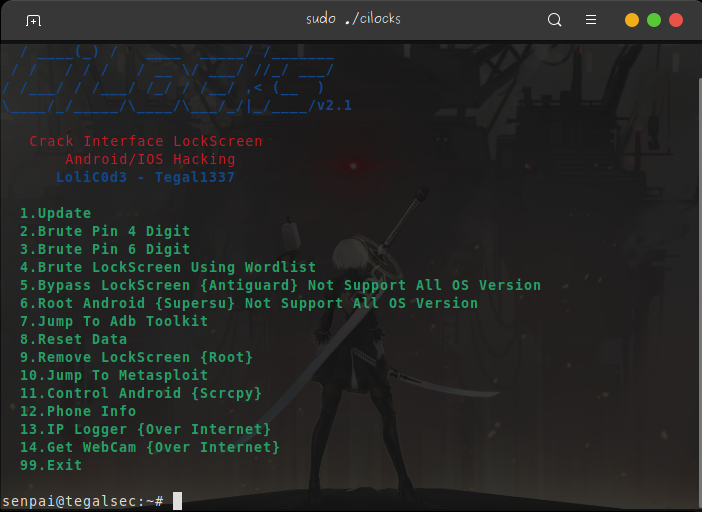 tegal1337/cilocks
Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
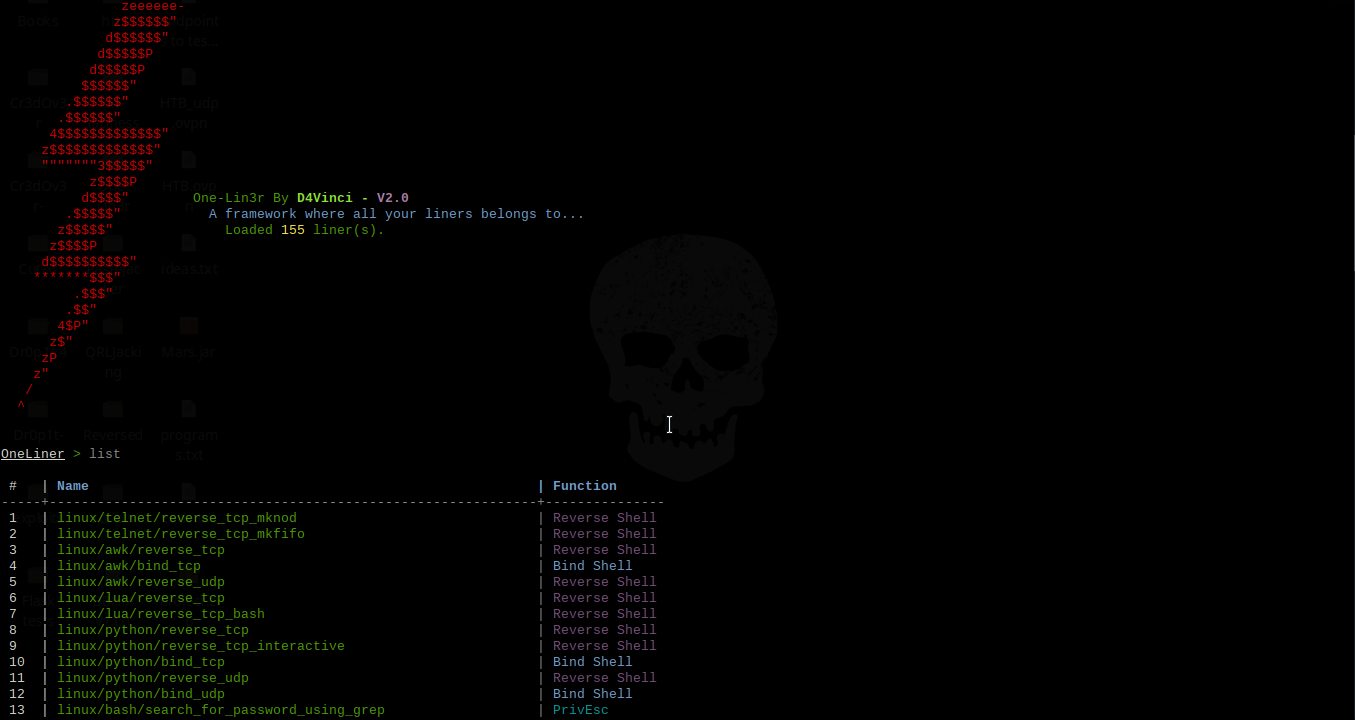 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
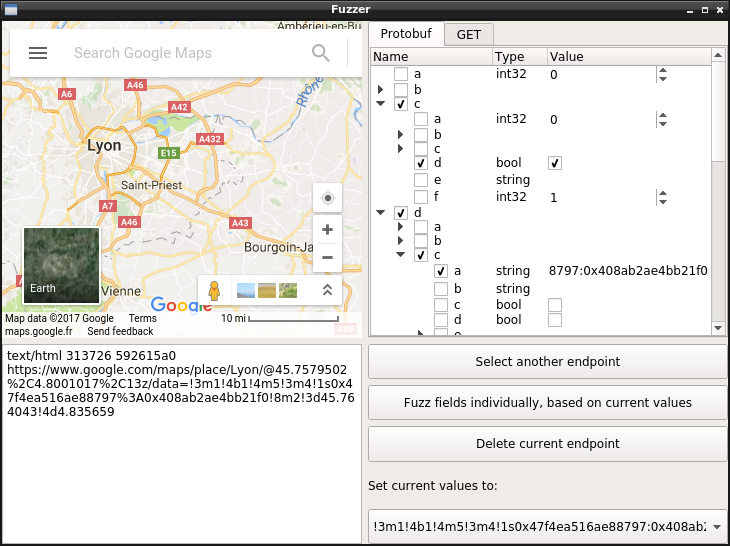 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…