

Cybersec
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
command-and-controlctfeducation+9
11
amitr12/cybersecSingle-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 asaotomo/cve-2021-42013-apache-rce-poc-exp
Apache 远程代码执行 (CVE-2021-42013)批量检测工具:Apache HTTP Server是美国阿帕奇(Apache)基金会的一款开源网页服务器。该服务器具有快速、可靠且可通过简单的API进行扩充的特点,发现 Apache HTTP Server 2.4.50 中针对…
 jas502n/drivelife-pstrojan
TrojanDropper/PS.Maloader.d
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
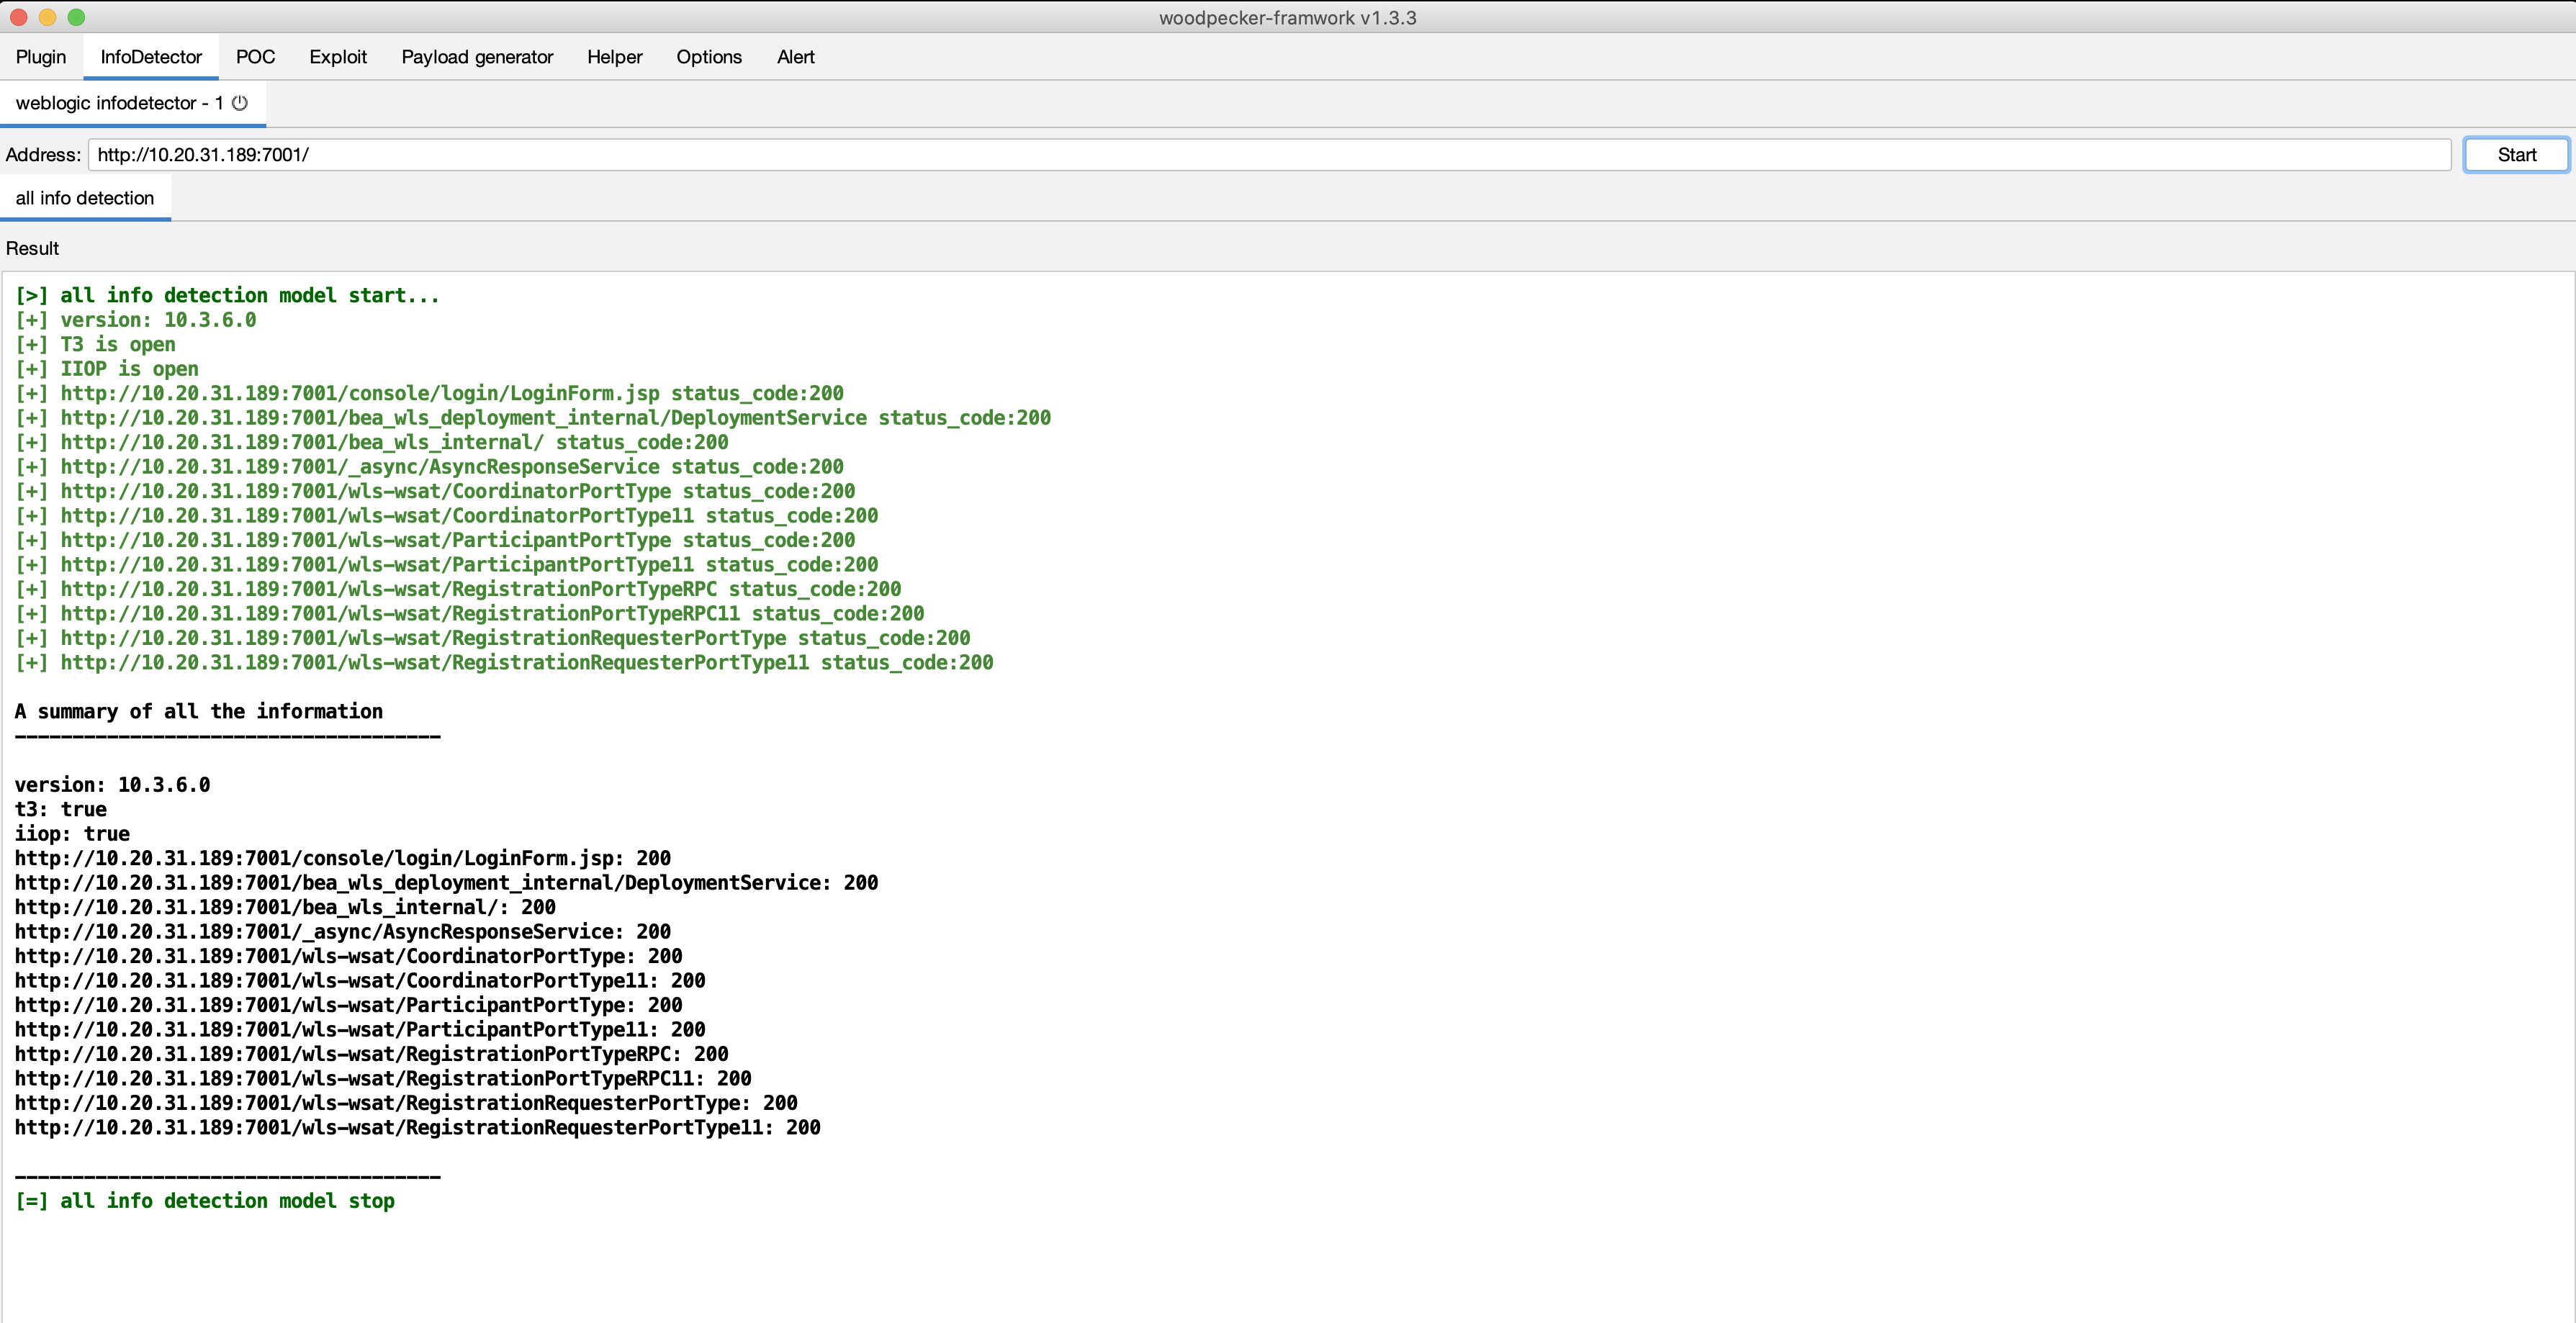 jas502n/woodpecker-plugins
woodpecker-plugins
 thatformat/hvv2023
HW2023@POC@EXP@CVE-2023-2023
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 mr-exo/cve-2021-41773
Remote Code Execution exploit for Apache servers. Affected versions: Apache 2.4.49, Apache 2.4.50
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 nxploited/cve-2026-10818
WPForms Pro <= 1.10.1.1 - Unauthenticated Arbitrary File Write via Chunked Upload Init/Finalize Ordering
 themehackers/cve-2025-30208
CVE‑2025‑30208 is a medium-severity arbitrary file read vulnerability in the Vite development server (a popular frontend build tool)
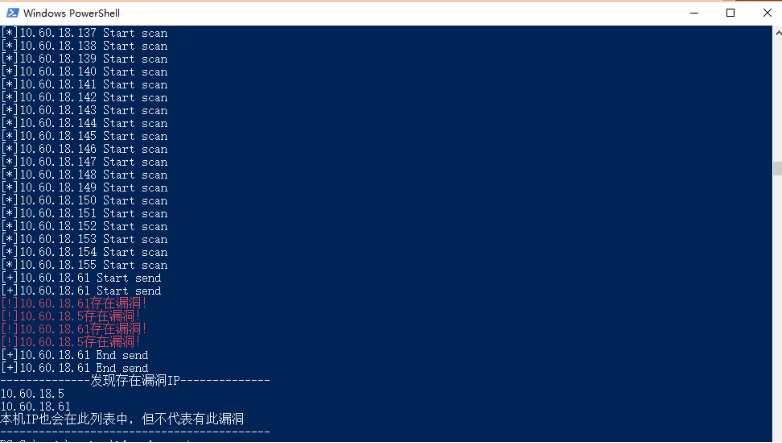 etocheney/javadeserialization
针对类似CVE-2017-10271漏洞的一个java反序列化漏洞扫描器
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 9lyph/cve-2019-12836
CVE-2019-12836
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 cirqueiradev/massexploit-cve-2024-4577
CVE-2024-4577 Mass Scanner & Exploit Tool