
CVE-2024-23692-RCE-in-Rejetto-HFS
 jakabakos/cve-2024-23692-rce-in-rejetto-hfs
Unauthenticated RCE Flaw in Rejetto HTTP File Server (CVE-2024-23692)
exploitationpayload-generationpenetration-testing+3
17
jakabakos/cve-2024-23692-rce-in-rejetto-hfsUnauthenticated RCE Flaw in Rejetto HTTP File Server (CVE-2024-23692)
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 pankass/cve-2024-37032_cve-2024-45436
CVE-2024-45436
 abrewer251/cve-2024-21762_fortinet_poc
Proof-of-concept scanner targeting CVE-2024-21762 in FortiOS SSL VPN’s /remote/hostcheck_validate endpoint with reverse shell payload delivery.
 gh-ost00/cve-2024-0195-spiderflow
CVE-2024-0195 Improper Control of Generation of Code ('Code Injection')
 0x20c/cve-2024-4577-nuclei
CVE-2024-4577 nuclei-templates
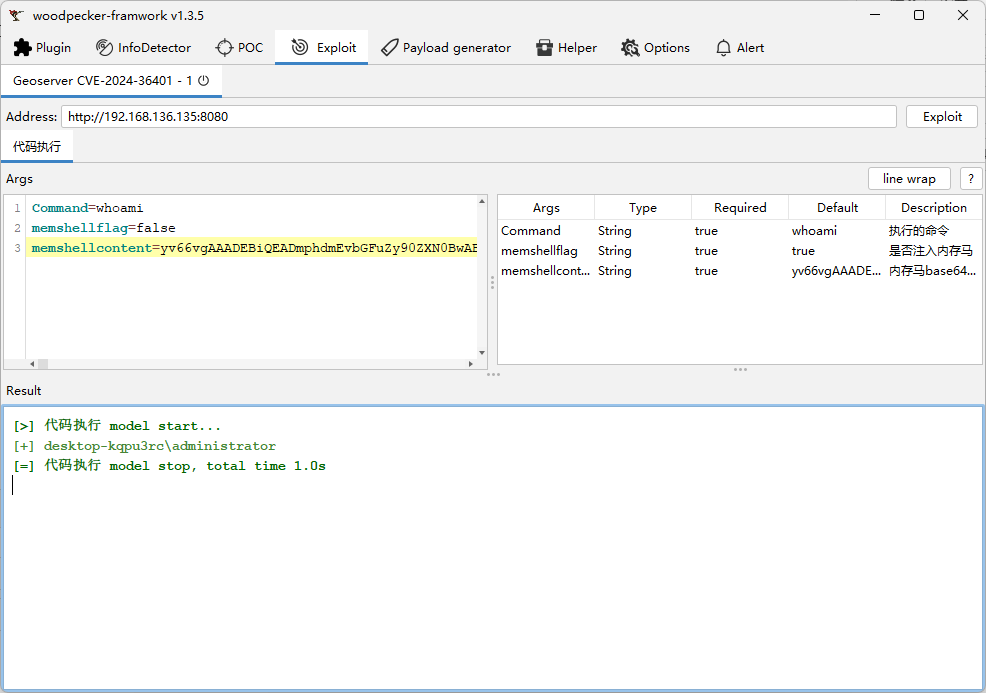 h1ng007/cve-2024-3640_wafbypass
CVE-2024-3640绕过Waf进行漏洞利用
 ktn1990/cve-2024-42640
Unauthenticated Remote Code Execution via Angular-Base64-Upload Library (npm:bower)
 gl1tch0x1/php_8.1.x_exploit
Automated detection & exploitation of critical PHP vulnerabilities (CVE-2024-4577 bypass, CVE-2025-14177, CVE-2025-14180, CVE-2025-14178)
 foxer131/cve-2024-42008-9-exploit
The scripts in this repository are made to abuse CVE-2024-42008 and CVE-2024-42009. Both of these CVEs are vulnerabilities found on Roundcube 1.6.7
 vitaciminipi/cve-2024-28397-rce
CVE-2024-28397 - Remote Code Execution From Vulnerable JS2PY
 funnydog896/cve-2024-36401-woodpeckerplugin
CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件
 ktn1990/cve-2024-31351_wordpress_exploit
Wordpress - Copymatic – AI Content Writer & Generator <= 1.6 - Unauthenticated Arbitrary File Upload
 0xilis/cve-2024-27876
libAppleArchive exploit maker, read the writeup here https://snoolie.gay/blog/CVE-2024-27876
 nxploited/cve-2024-52375
WordPress Datasets Manager by Arttia Creative plugin <= 1.5 - Arbitrary File Upload vulnerability
 shinspace92/cve-2024-26229
Nim touch up of CVE 2024 26229
 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 hackerronin/cve-2024-0044
a vulnerability affecting Android version 12 & 13