
CVE-2024-32002
 spyciokon/cve-2024-32002
Just small script to exploit CVE-2024-32002
exploitationpayload-generationpenetration-testing+3
spyciokon/cve-2024-32002Just small script to exploit CVE-2024-32002
 michredteam/cve-2024-4761
High CVE-2024-4761 Exploit
 night-have-dreams/php-cgi-injector
一個測試CVE-2024-4577和CVE-2024-8926的安全滲透工具
 daemon-reconfig/cve-2024-32002
Generates reverse shell payloads targeting the GitLab-shell vulnerability CVE-2024-32002 for exploitation testing.
 nxploited/cve-2024-52380-exploit
Picsmize plugin for WordPress is vulnerable to arbitrary file uploads.
 akabe1/graver
Proof of Concept script to exploit the authenticated SSTI+RCE in Grav CMS (CVE-2024-28116)
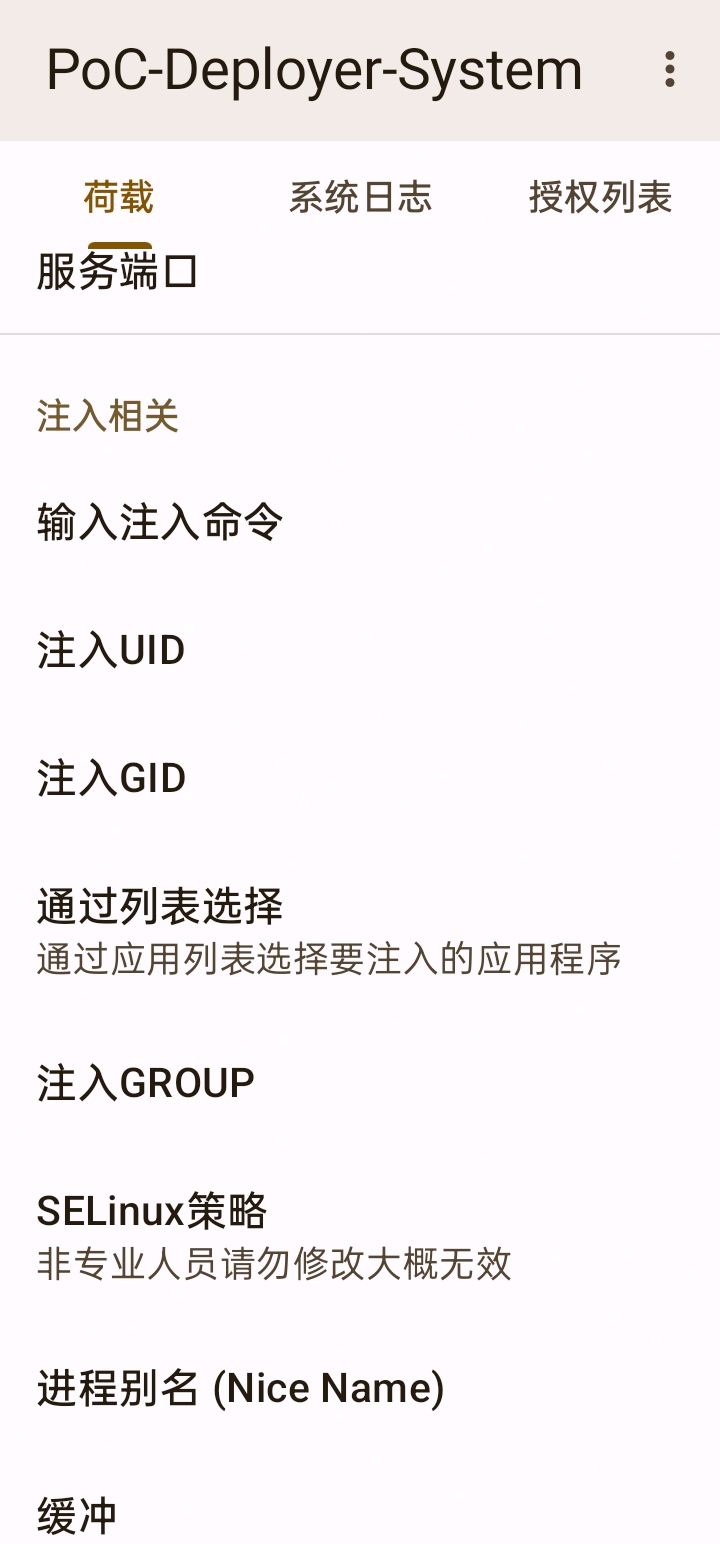 wqry085/poc-deployer-system
Quick tool for utilizing CVE-2024-31317 on Android
 ynwarcs/cve-2024-30052
Materials for CVE-2024-30052.
 ktn1990/cve-2024-8425
The WooCommerce Ultimate Gift Card plugin for WordPress is vulnerable to arbitrary file uploads.
 ktn1990/cve-2024-43160
The BerqWP – Automated All-In-One PageSpeed Optimization Plugin for Core Web Vitals, Cache, CDN, Images, CSS, and JavaScript plugin for WordPress is…
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 gill-singh-a/cve-2024-4577-exploit
PHP CGI Parameter Injection Vulnerability (RCE: Remote Code Execution)
 ap0dexme0/cve-2024-27956
Perform with massive Wordpress SQLI 2 RCE
 cipherspy/cve-2026-42945-poc
exploit for CVE-2026-42945
 aelmokhtar/cve-2024-34716
Proof-of-concept exploit for CVE-2024-34716, a PNG-driven XSS to RCE chain in PrestaShop 8.1.5, enabling remote code execution via crafted image…
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
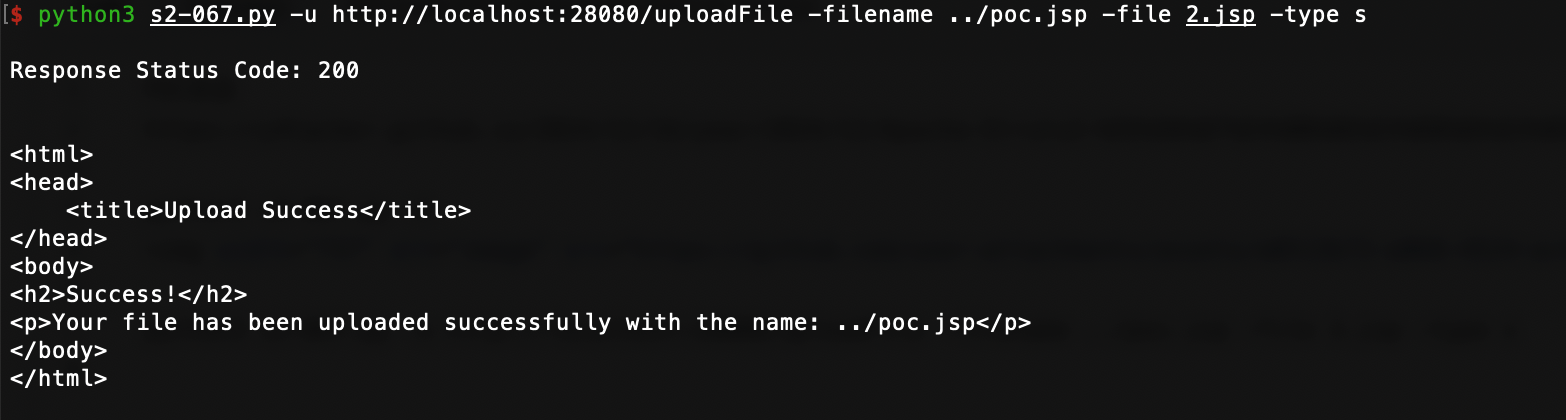 yangyanglo/cve-2024-53677
Proof-of-concept exploit for CVE-2024-53677 (S2-067), an Apache Struts2 file upload logic bypass enabling remote code execution via crafted filename…
 phirojshah/cve-2024-4577
Proof-of-concept exploit for PHP CGI argument injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers with scanning…