
QuickResponseC2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…

Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…

Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…

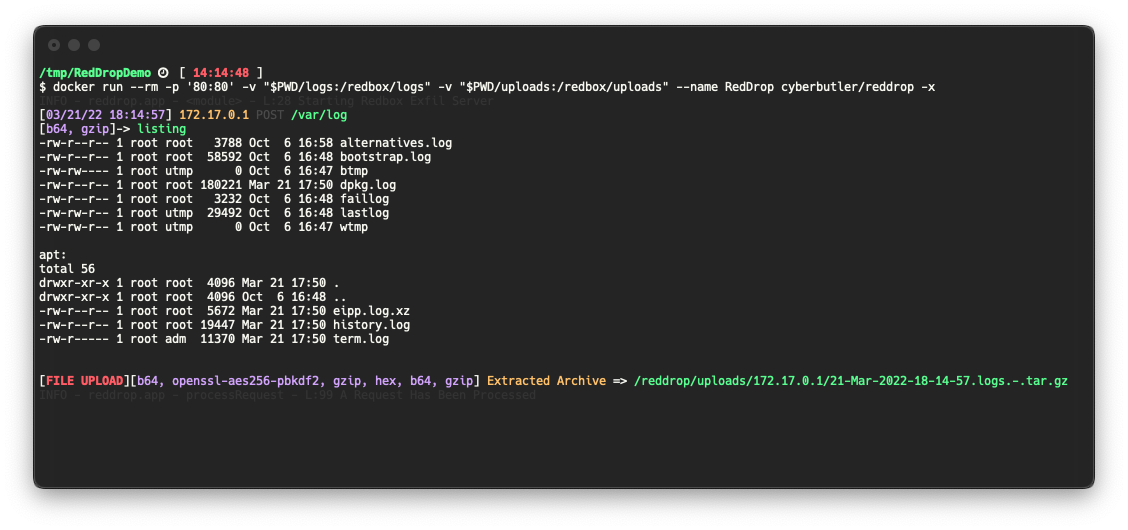
Python Flask web server for capturing, processing, and logging encoded/encrypted payloads and tar archives, designed for penetration testers and red…

Python-based proof-of-concept exploit for CVE-2017-9791 (Apache Struts2 S2-048) with check and command execution modes for penetration testing.

Exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP vulnerabilities in XP and 7, enabling remote code execution for penetration testing.

Proof-of-concept exploit scripts for CVE-2016-3714 (ImageTragick) using MVG/SVG files to deliver reverse shells via bash, nc, and PHP for ethical…

Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…

An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…

a CLI for ephemeral penetration testing

Python exploit script for CVE-2021-22205 (GitLab RCE) with command execution and reverse shell capabilities. Supports one-click getshell for…

Automated remote code execution exploit for Apache Struts2 (CVE-2017-5638) with auto-exploitation capabilities for penetration testing and…

Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…

Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…

Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.

Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…

Proof-of-concept exploit for CVE-2024-37054, a critical deserialization vulnerability in MLflow. Includes a full exploit script and a malicious model…

AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…

Collection of payloads for exploiting the Log4j remote code execution vulnerability (CVE-2021-44228), including JNDI injection strings and bypass…