

CVE-2023-23397_EXPLOIT
 billskico/cve-2023-23397_exploit
Generates meeting requests taking advantage of CVE-2023-23397. This requires the outlook thick client to send.
educationexploitationlateral-movement+3
7
billskico/cve-2023-23397_exploitGenerates meeting requests taking advantage of CVE-2023-23397. This requires the outlook thick client to send.
 aeroot/wp-gdpr-compliance-plugin-exploit
Exploit of the privilege escalation vulnerability of the WordPress plugin "WP GDPR Compliance" by "Van Ons"…
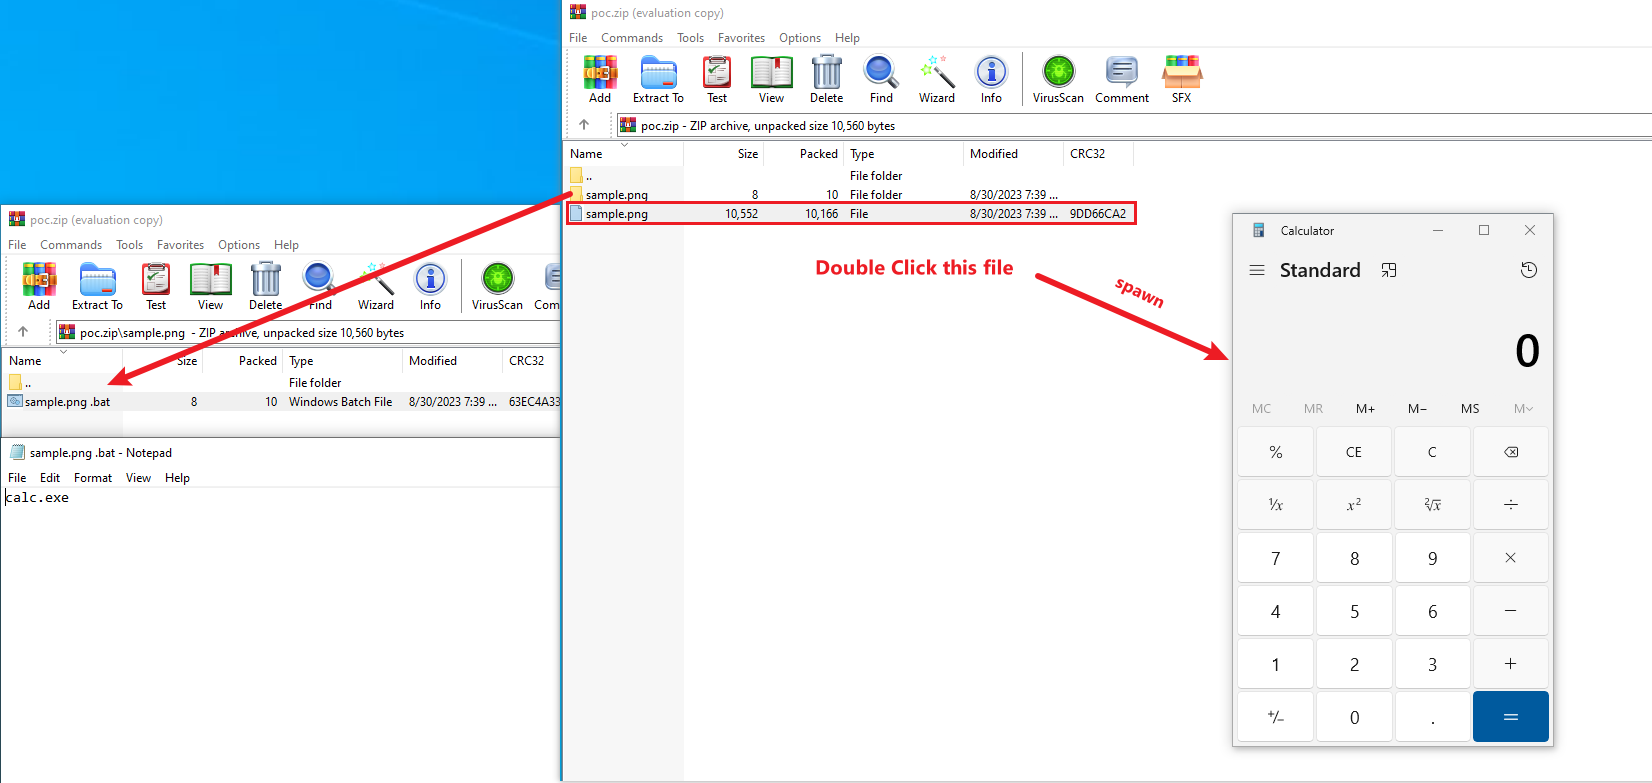 malvika-thakur/cve-2023-38831
Proof-of-Concept (POC) of CVE-2023-38831 Zero-Day vulnerability in WinRAR
 glen-pearson/proxylogon-cve-2021-26855
Exploit for CVE-2021-26855 (ProxyLogon) targeting Microsoft Exchange. Creates a new admin user and establishes a reverse shell for post-exploitation…
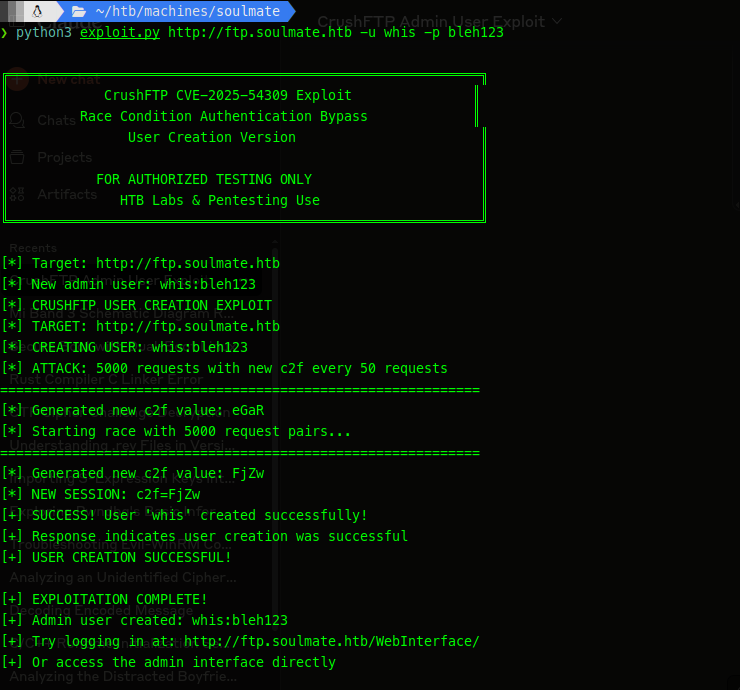 whisperer1290/cve-2025-54309__enhanced_exploit
Multi-threaded exploit for CrushFTP authentication bypass (CVE-2025-54309) with race condition implementation, XML payload generation, and admin user…
 monzaviman/cve-2025-9816
Proof of Concept for Stored-XSS on Vulnerable WP-Statistics Plugin known as CVE-2025-9816
 arno0x/embedinhtml
Embed and hide any file in an HTML file

 tounsi007/cve-2023-20198
CVE-2023-20198 PoC (!)
 z3r0sw0rd/cve-2023-38831-poc
Proof-of-Concept for CVE-2023-38831 Zero-Day vulnerability in WinRAR
 kuyrathdaro/cve-2023-38831
CVE-2023-38831 (PoC) - WinRAR Exploit
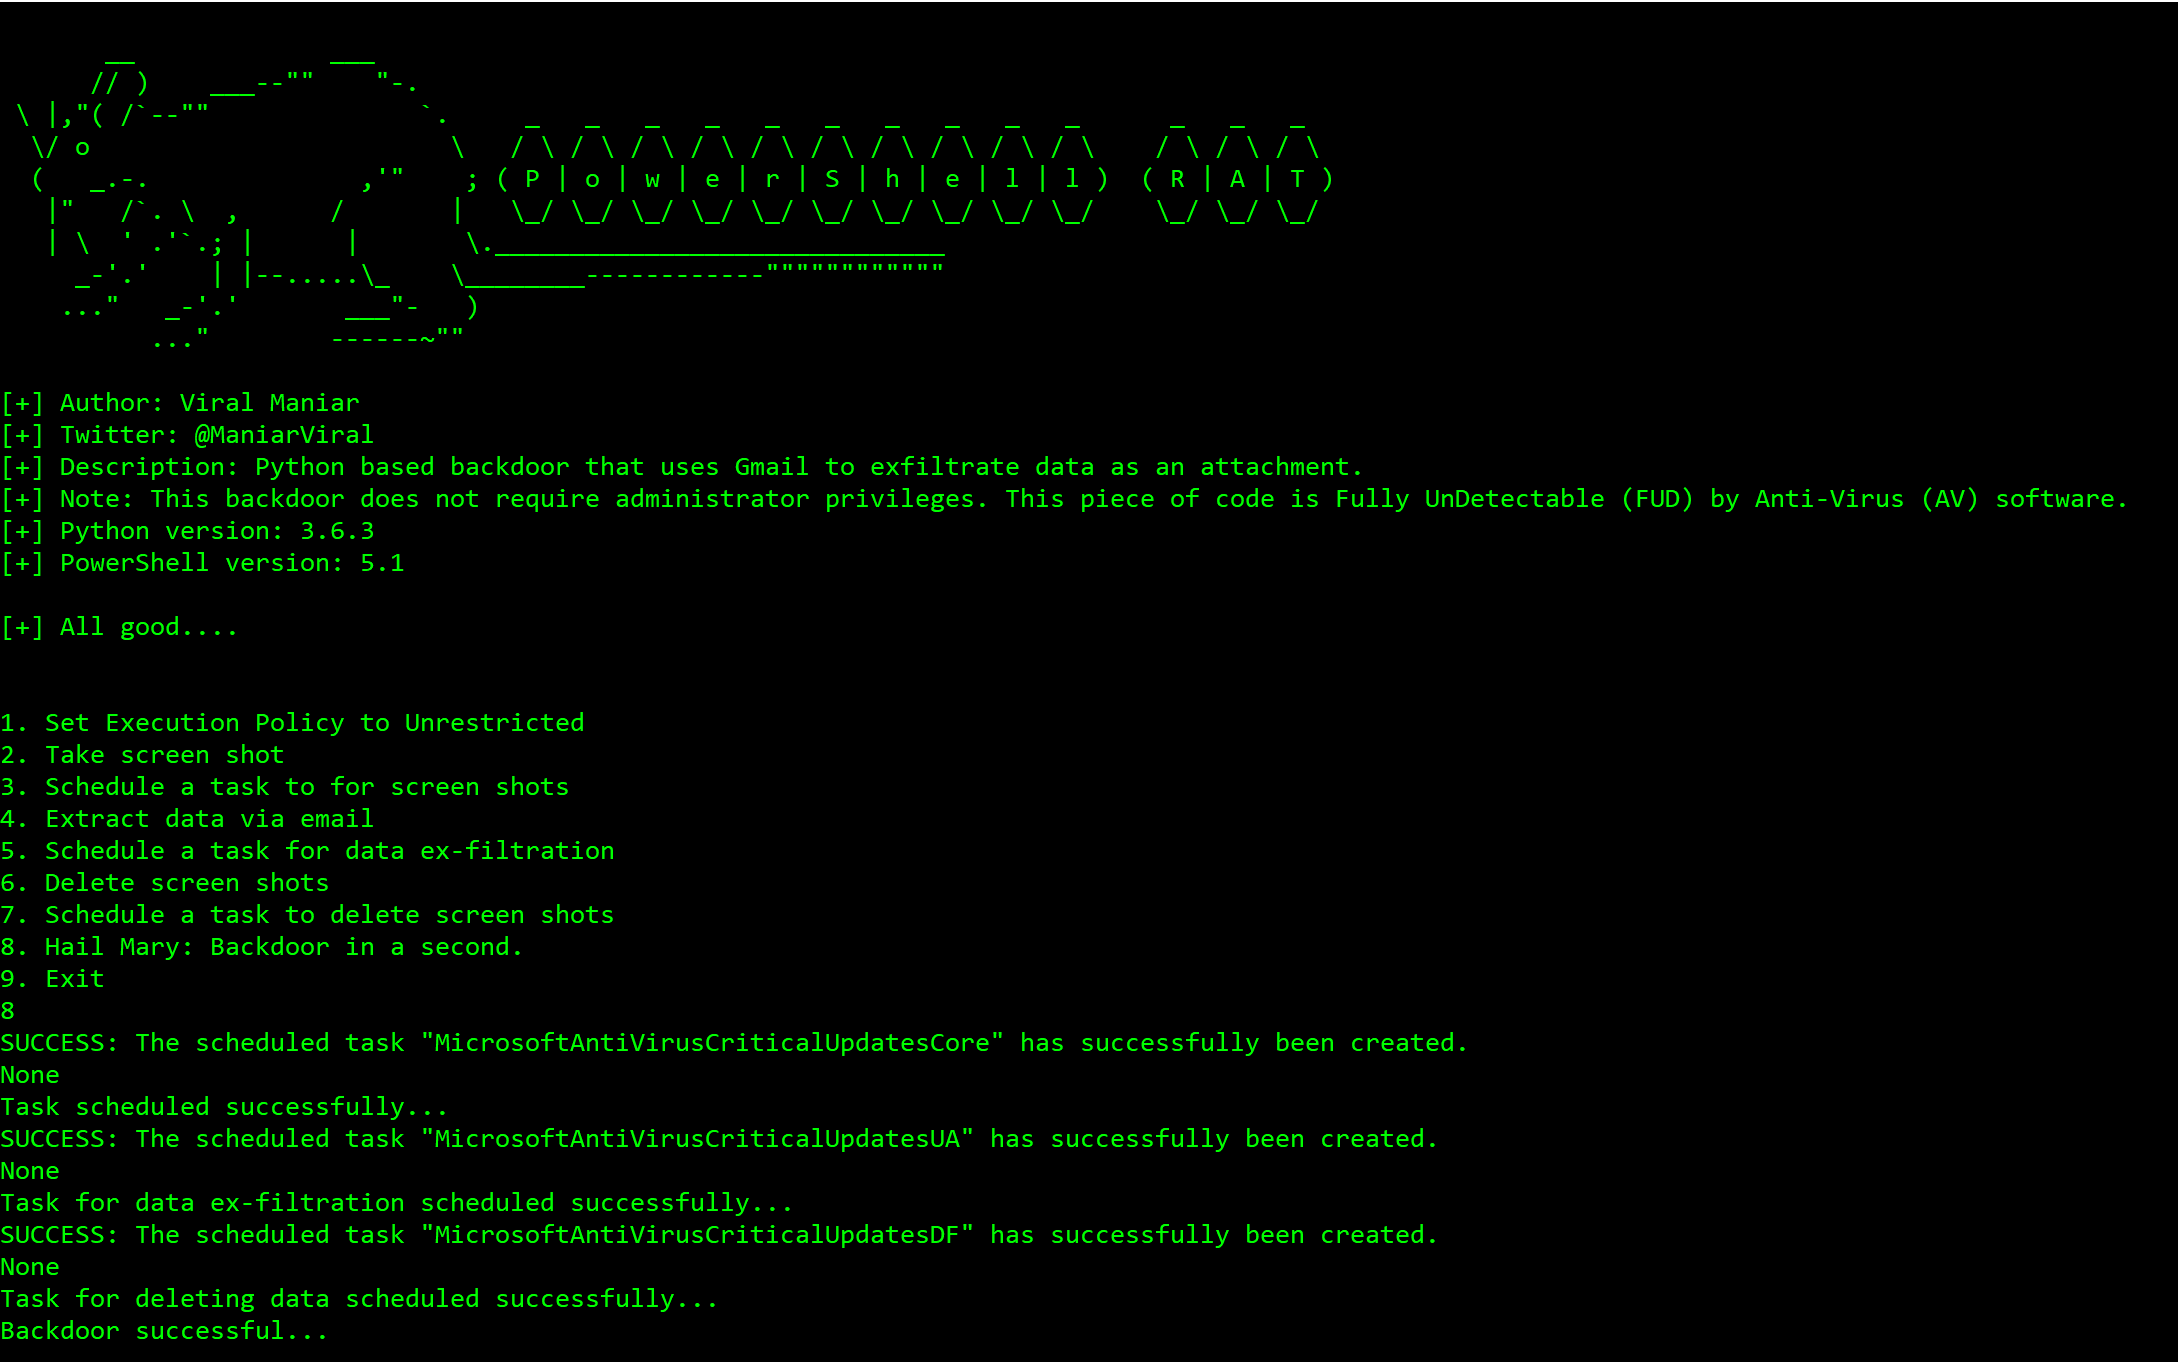 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
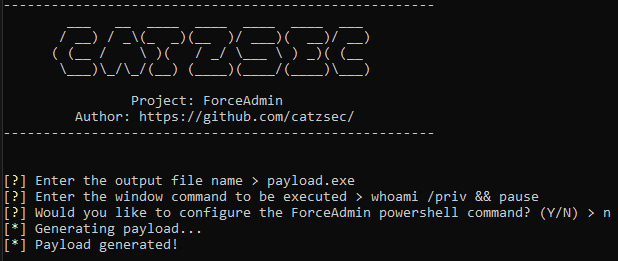 catzsec/forceadmin
⚡ Create infinite UAC prompts forcing a user to run as admin ⚡
 iveresk/cve-2022-26134
Just simple PoC for the Atlassian Jira exploit. Provides code execution for unauthorised user on a server.
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 abbarhissarh/cve-2020-29607
A file upload restriction bypass vulnerability in Pluck CMS before 4.7.13 allows an admin privileged user to gain access in the host through the…