

wordlistgen
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
fuzzinginformation-gatheringpayload-generation+1
113
ethicalhackingplayground/wordlistgenGenerates target specific word lists for Fuzzing with fuff
 kleiton0x00/xsscope
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.
 imbas007/cve-2026-64638-poc
CVE-2026-64638: WordPress Pre-auth XSS → RCE (XSS2Shell) PoC
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 ch3m1cl/cve-2025-31161
Python exploit script for CVE-2025-31161 targeting CrushFTP. Enumerates users and creates malicious accounts with elevated permissions via HTTP…
 watchtowrlabs/watchtowr-vs-junosevolved-cve-2026-21902
Generates detection artifacts for CVE-2026-21902 on Juniper Junos Evolved, enabling verification of unauthenticated remote code execution via command…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 kljunowsky/cve-2022-42889-text4shell
Proof-of-concept exploit for CVE-2022-42889 (Text4Shell) in Apache Commons Text, with manual and mass exploitation scripts using script, URL, and DNS…
 charlesgargasson/cve-2023-41425
XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
 kljunowsky/cve-2022-44268
Proof-of-concept exploit for CVE-2022-44268 enabling arbitrary file read via poisoned PNG images uploaded to vulnerable ImageMagick instances.…
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 rwxrwxs/cve-2026-87902
Python exploit for CVE-2026-87902, an unauthenticated LFI in WordPress Core ≤7.1.1: fingerprints OPML, detects webroot, abuses the PEAR gadget to…
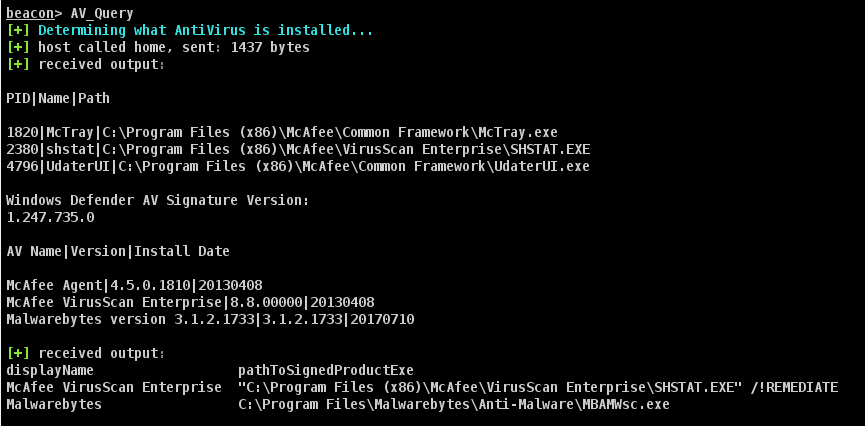 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
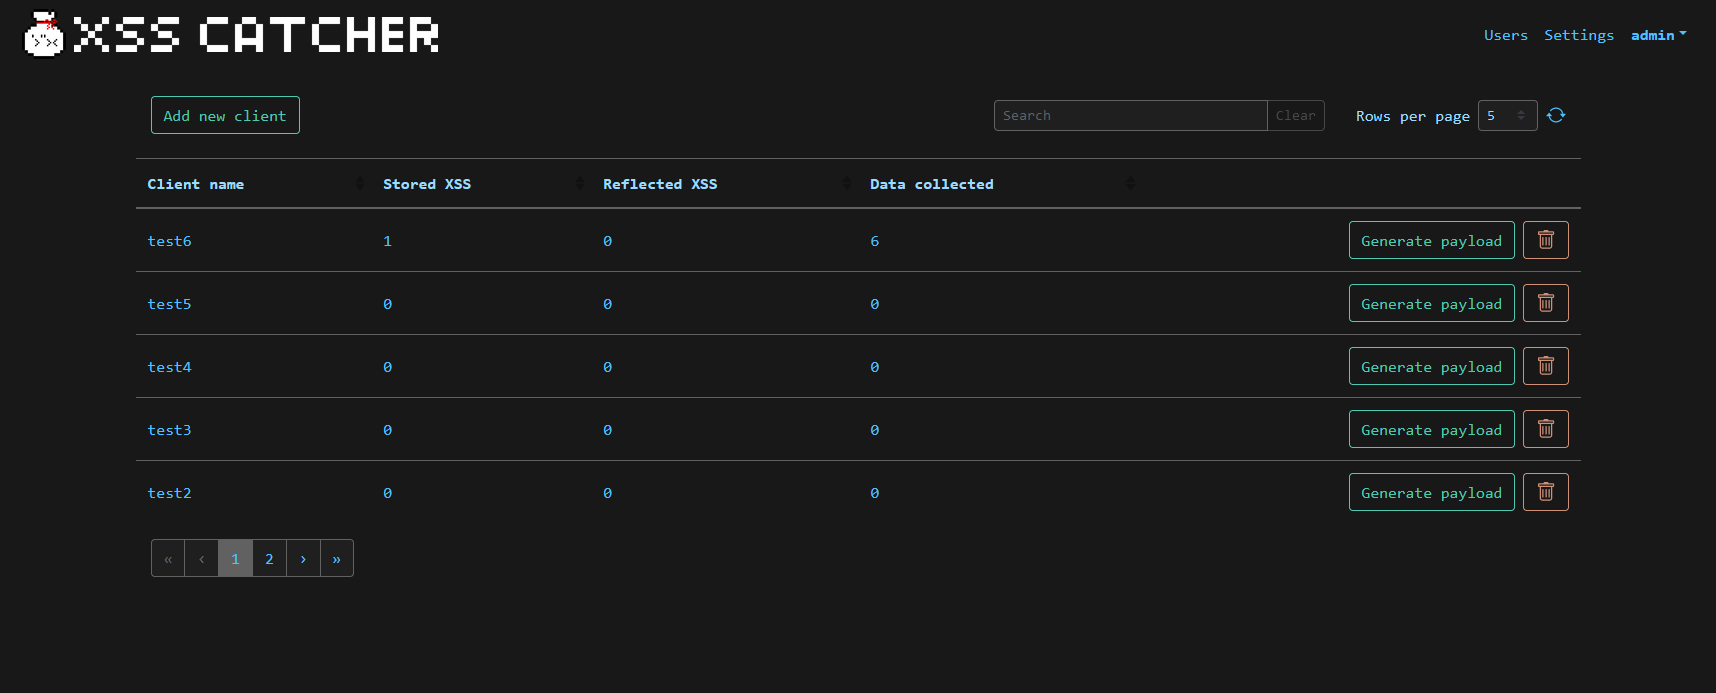 daxakahackerman/xss-catcher
A blind XSS detection and XSS data capture framework
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…