

XSSYA-V-2.0
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
information-gatheringpayload-generationpenetration-testing+5
83
yehia-mamdouh/xssya-v-2.0Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 kljunowsky/cve-2022-42889-text4shell
Proof-of-concept exploit for CVE-2022-42889 (Text4Shell) in Apache Commons Text, with manual and mass exploitation scripts using script, URL, and DNS…
 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 kljunowsky/cve-2022-44268
Proof-of-concept exploit for CVE-2022-44268 enabling arbitrary file read via poisoned PNG images uploaded to vulnerable ImageMagick instances.…
 redtimmy/enumjavalibs
Remote Java classpath enumeration via deserialization
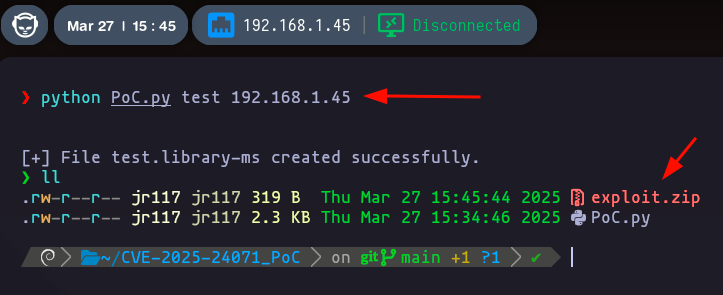 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
 imbas007/cve-2026-64638-poc
CVE-2026-64638: WordPress Pre-auth XSS → RCE (XSS2Shell) PoC
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
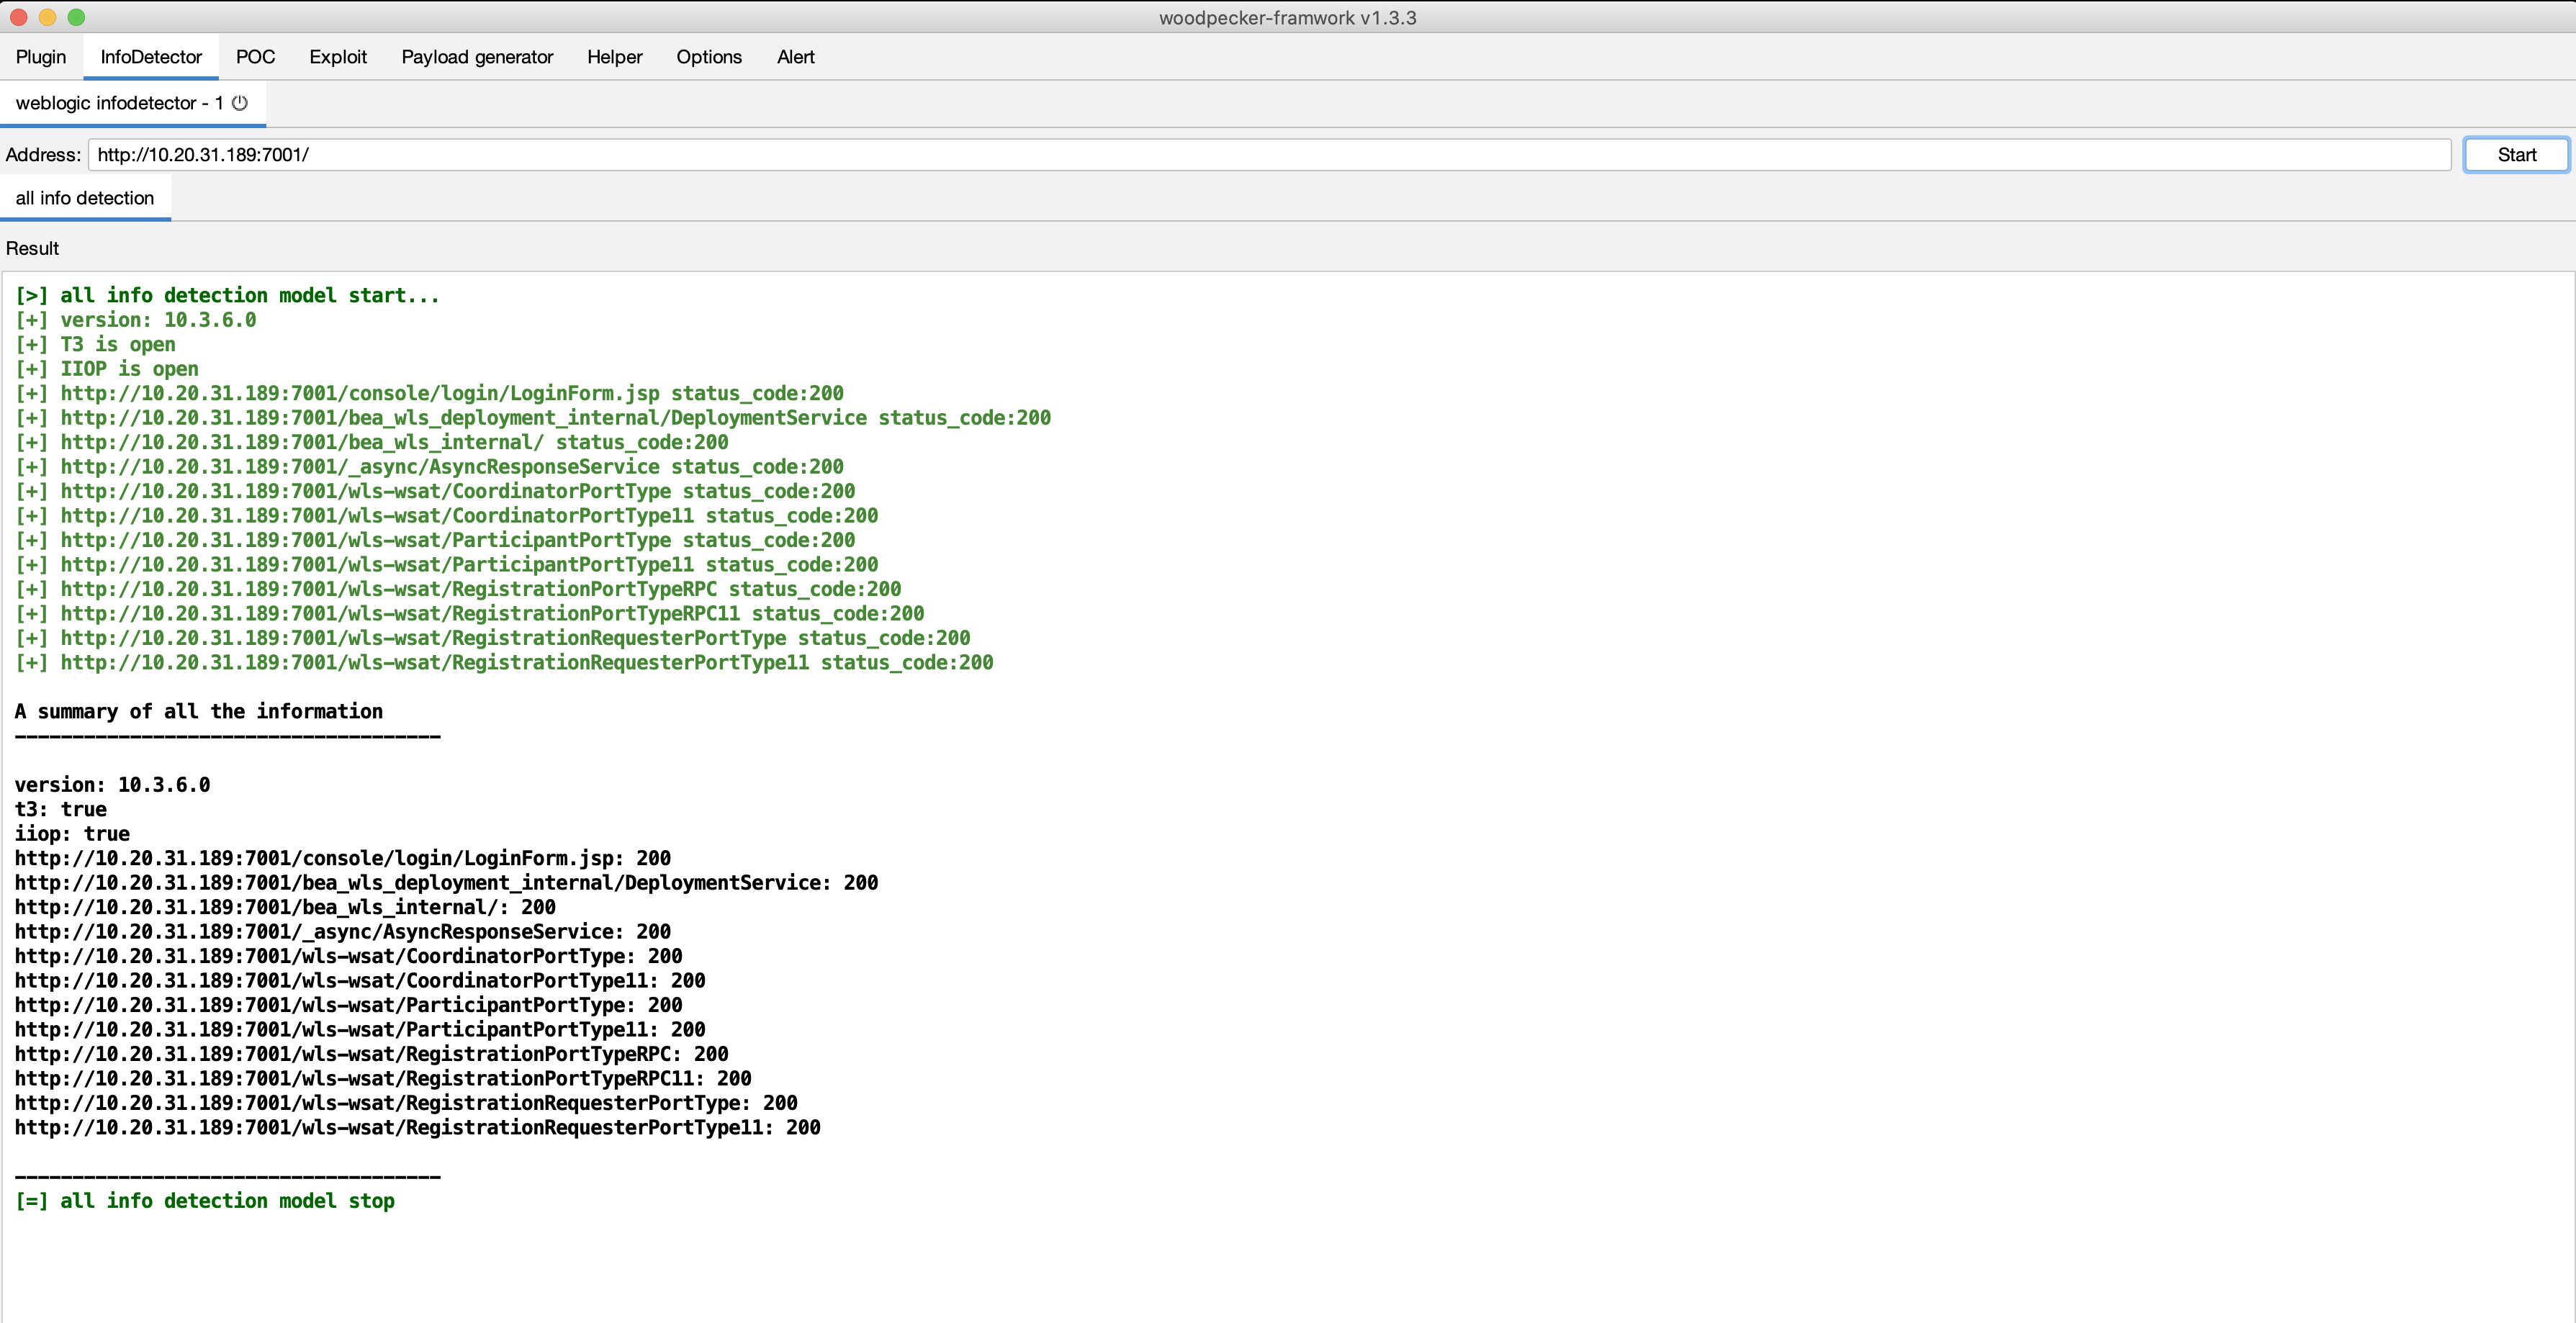 jas502n/woodpecker-plugins
woodpecker-plugins
 thatformat/hvv2023
HW2023@POC@EXP@CVE-2023-2023
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 nxploited/cve-2026-10818
WPForms Pro <= 1.10.1.1 - Unauthenticated Arbitrary File Write via Chunked Upload Init/Finalize Ordering
 themehackers/cve-2025-30208
CVE‑2025‑30208 is a medium-severity arbitrary file read vulnerability in the Vite development server (a popular frontend build tool)
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 9lyph/cve-2019-12836
CVE-2019-12836
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.