
backdoorppt
 r00t-3xp10it/backdoorppt
transform your payload.exe into one fake word doc (.ppt)
impersonation-toolspayload-generationphishing-tools+2
4706 years ago
r00t-3xp10it/backdoorppttransform your payload.exe into one fake word doc (.ppt)
 aslitsecurity/cve-2021-40444_builders
This repo contain builders of cab file, html file, and docx file for CVE-2021-40444 exploit
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
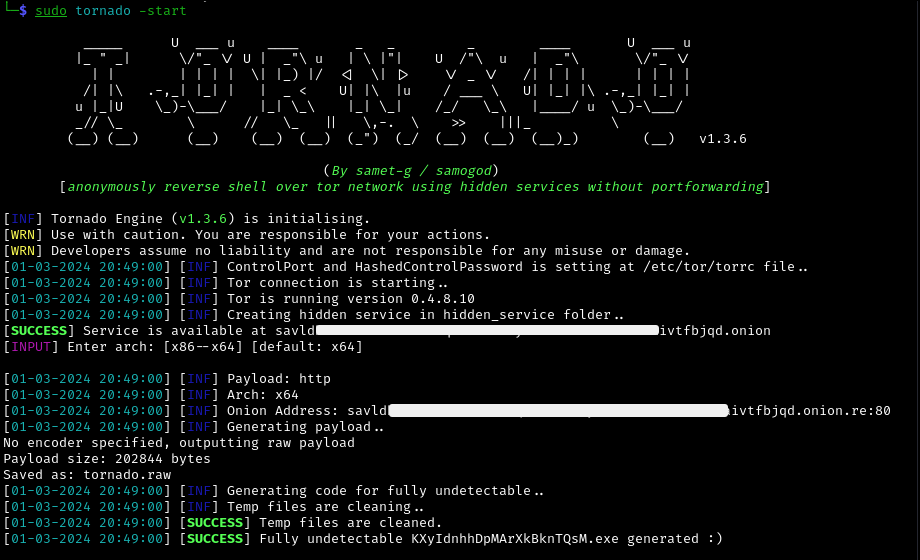 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 doocop/cve-2022-30190
Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…
 yrkuo/cve-2022-30190
Step-by-step reproduction guide for CVE-2022-30190 (Follina) MSDT remote code execution vulnerability, including malicious document creation and C2…