
static_asm
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
binary-analysiscode-analysiseducation+6
3118h 1m ago
mahmoudimus/static_asmHeader-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
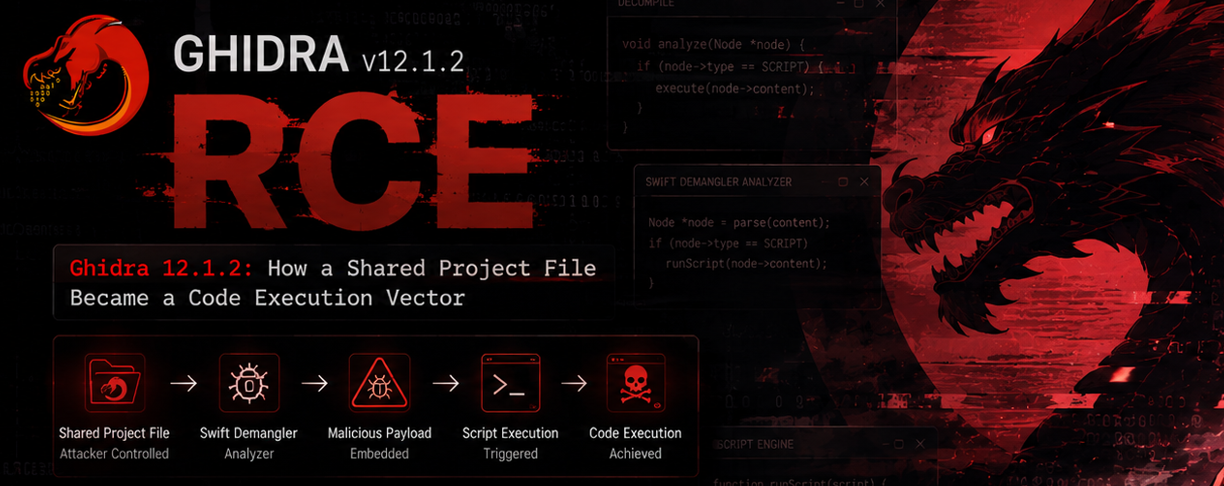 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
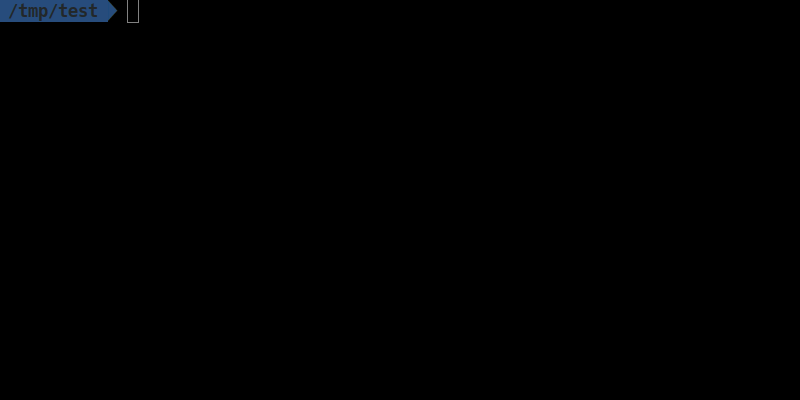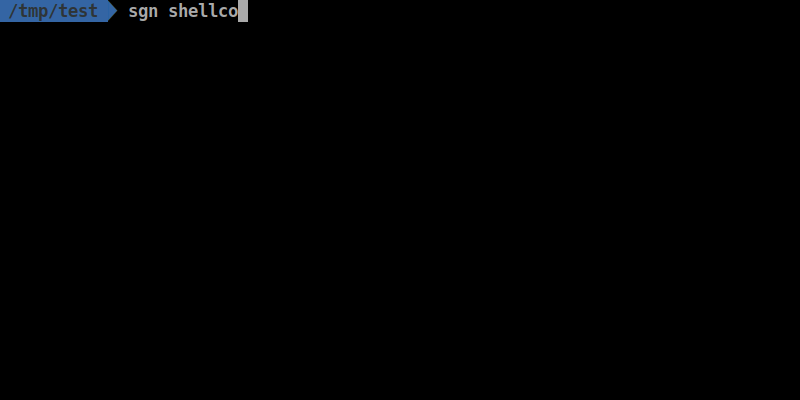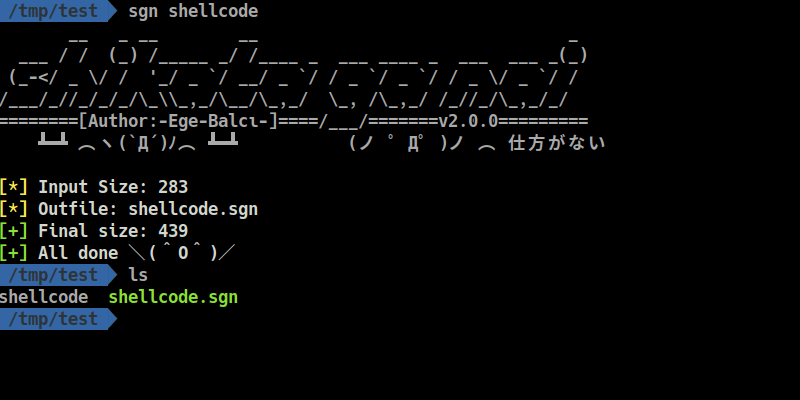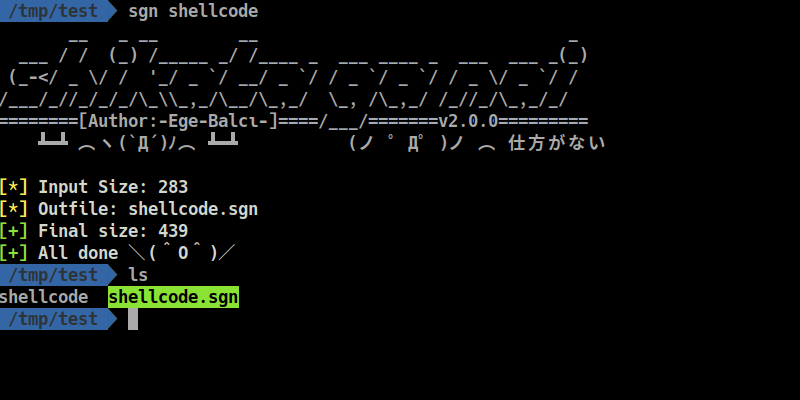 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 mehdichyhab/cve-2025-64512-exploit
CVE-2025-64512 - pdfminer.six Remote Code Execution Exploit
 matesz44/cve-2025-64512
CVE-2025-64512: pdfminer.six pickle deserialization rce; .pickle.gz + pdf generator w/ custom payloads
 m2sousa/cve-2025-69212
CVE-2025-69212 Proof-of-concept.
 papageo75/cve-2026-48908-poc
Unauthenticated RCE PoC for CVE-2026-48908 — SP Page Builder for Joomla (≤ 6.6.1): arbitrary file upload via asset.uploadCustomIcon. Self-cleaning,…
 whattheslime/cve-2026-0740
Ninja Forms File Uploads <= 3.3.26 - Unauthenticated Arbitrary File Upload to RCE (CVE-2026-0740)
 t1ckprivate/cve-2026-43284-dirty-frag
Pre-compiled exploit for CVE-2026-43284 (Dirty Frag) with multi-architecture support (x86_64, i386, aarch64, armv7, riscv64, ppc64le, s390x).…
 xxconi/cve-2026-27384
Automated scanner and exploit for CVE-2026-27384, an unauthenticated RCE in W3 Total Cache via mfunc/eval() injection. Features auto-detection, 48…
 xxconi/cve-2026-5718
CVE-2026-5718: Unauthenticated File Upload To RCE in DnD Upload CF7 Plugin
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…