
DLLHijackHunter
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
ghostvectoracademy/dllhijackhunterAutomated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 nikitapark/cve-2023-50164-poc
CVE-2023-50164 PoC Application & Exploit script
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
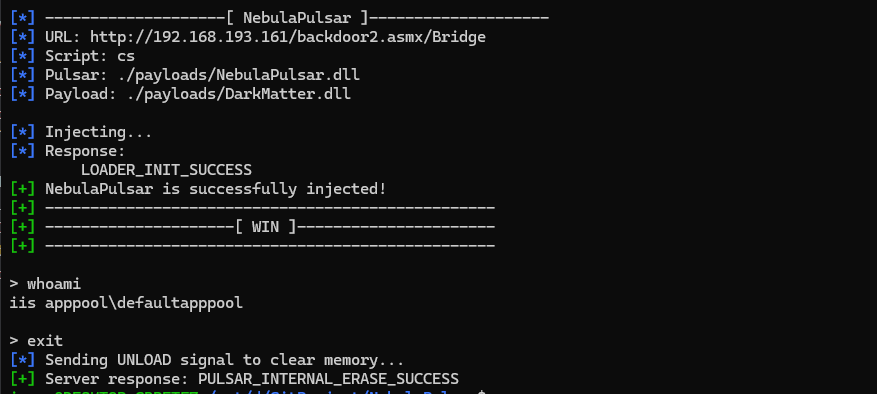 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 ahmedshamsddin/cve-2025-55182
Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…
 derziad/cve-2022-30190
This project demonstrates a proof-of-concept exploit for CVE-2022-30190, also known as "Follina"—a critical remote code execution vulnerability…
 bytereaper77/cve-2025-7840
Proof‑of‑concept exploit for CVE‑2025‑7840 that injects malicious payloads into the Firstname parameter of a reservation form to trigger XSS
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
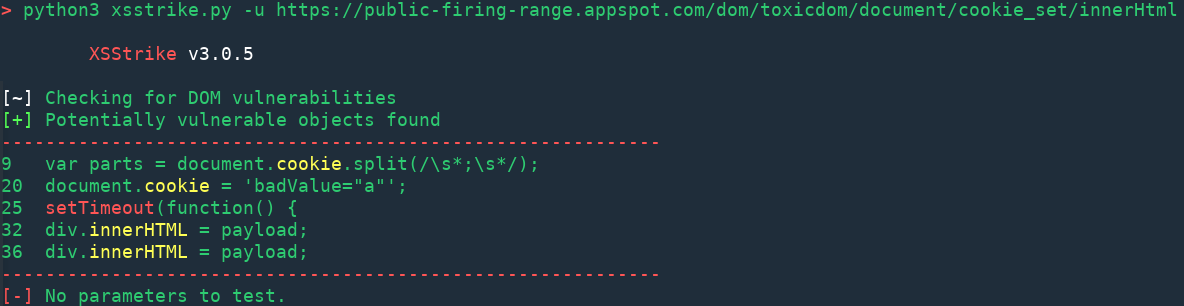
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 qw3rtyou/cve-2021-44228_dockernize
Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
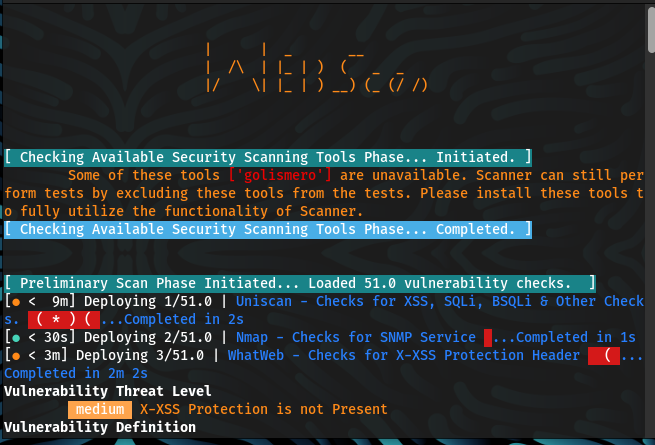 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
 projectforsix/cve-2021-45428-defacer
Python-based exploit for CVE-2021-45428, targeting a specific web application vulnerability for penetration testing and security assessment.