

joro
 bishopfox/joro
A collaborative web exploitation framework.
command-and-controlexploit-frameworksfuzzing+5
bishopfox/joroA collaborative web exploitation framework.
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 keelanbrady1011/cve-2024-36401
CVE-2024-36401 exploit with webshell-like functionality for limited environments, supporting self-signed TLS sessions and remote command execution…
 roodhelios/cve-2022-26134-ognl-injection
Exploit for CVE-2022-26134, an OGNL injection vulnerability in Atlassian Confluence Server and Data Center, enabling unauthenticated remote code…
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 noraj/vbsmin
VBScript minifier
 0xblackash/cve-2026-111497
Advisory and proof-of-concept toolkit for CVE-2026-111497 (Node2Shell), a Brotli heap overflow in Node.js, with trigger scripts, version checker, and…
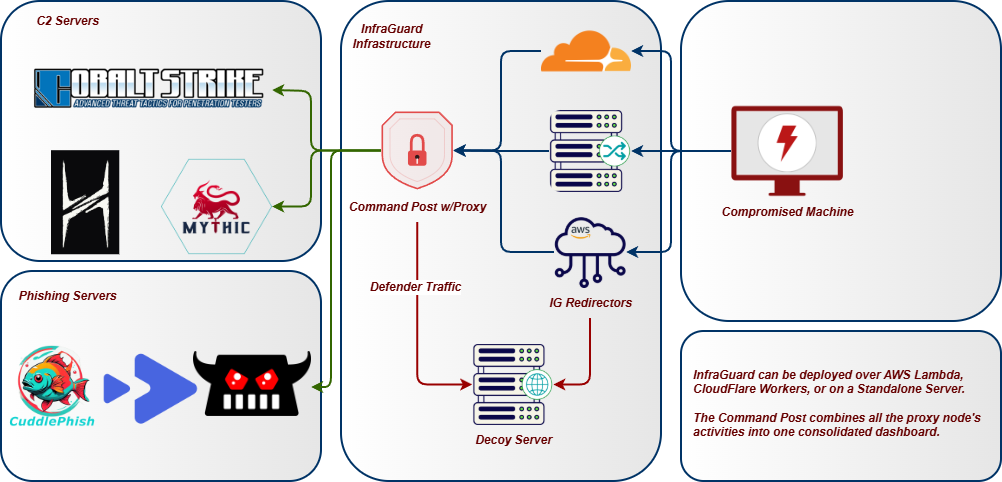 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 ghxstsec/php2shell-poc
Python exploit for CVE-2026-109618: abuses PHP session.upload_progress heap corruption to overwrite zend_call_function and achieve remote command…
 0xabcd01/cve-2026-48866
CVE-2026-48866 — Gravity Forms <= 2.10.0.1 Arbitrary File Deletion via Path Traversal (CVSS 9.6)