

http-terminator
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
ai-securityexploitationfuzzing+8
120
portswigger/http-terminatorAI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
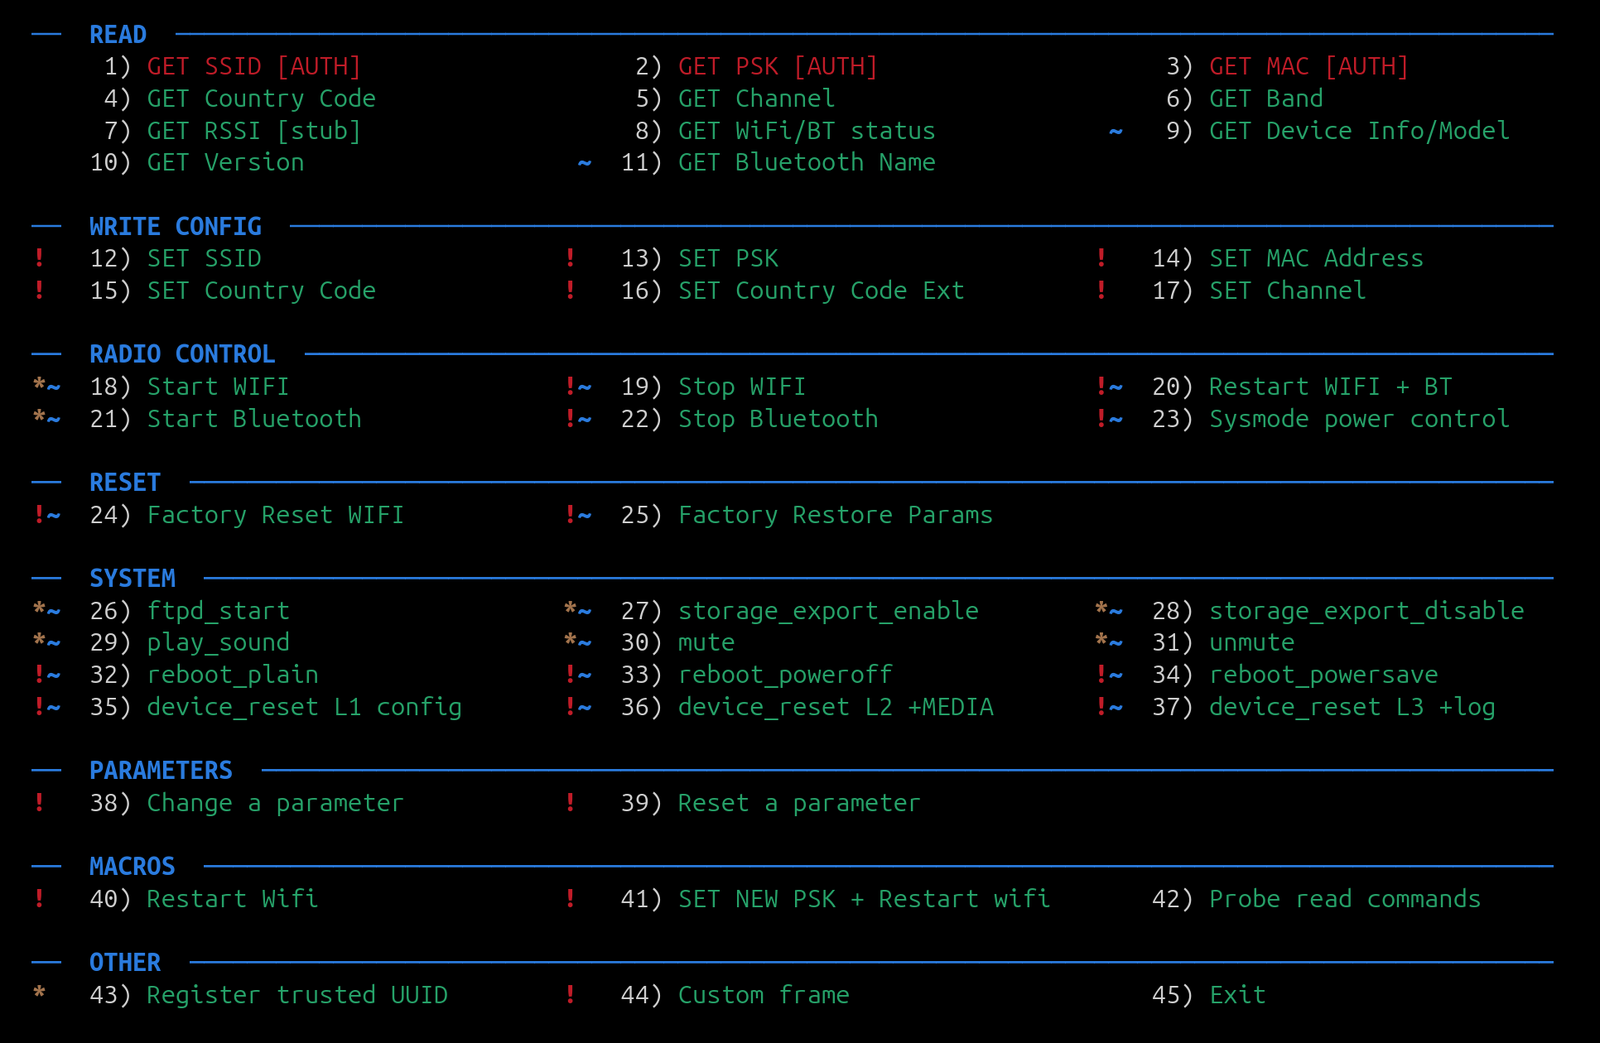 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 moi404/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit and payload generator for CVE-2026-22686, a sandbox escape in enclave-vm <2.7.0 enabling arbitrary code execution and…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…